A signed, patched, CIP-013-compliant relay can still fall within EO 14421. The test is who owns the company behind its firmware, and it reaches assets down to 69 kV. Doc McConnell on what to build before DOE’s December rules: https://t.co/aenRRNZzuh #EnergySecurity#OTSecurity
OT security spending is projected to roughly quadruple by 2035. Doc McConnell tells Manufacturing Business Technology the scarcest resource is people who can secure control systems without causing downtime. #OTSecurity#CriticalInfrastructure
https://t.co/Oaery9KTvZ
Product security is on the agenda this October. 🔍
Meet Finite State at:
🩺 Oct. 15 to 17 | U.S. Medical Device Cybersecurity Conference
🏭 Oct. 21 to 22 | ManuSec
🔐 Oct. 26 to 27 | Cybersecurity Summit, Minneapolis
Schedule a demo: https://t.co/l9nDhM9gD3
#ProductSecurity
The strongest measure of a product security platform? What customers say after putting it to work.
G2 reviews highlight Finite State’s binary scanning, vulnerability analysis, flexible SAST/SCA/SBOM scans, & advanced AI capabilities. Learn more:
https://t.co/l9nDhM9gD3
Explore What’s Next in Connected Vehicle Product Security.
Following #SAECOMVEC, Finite State’s Cade Jackson is continuing the conversation around securing increasingly connected, software-defined vehicles.
Schedule time with Cade: https://t.co/l9nDhM9gD3.
#ProductSecurity
🚗 Heading to #AutoISAC in Novi?
Meet with Finite State to discuss gaining deeper software visibility, prioritizing real risk, and accelerating vulnerability response.
Schedule time with our team:
https://t.co/BpwnIlUAh4
#AutomotiveCybersecurity#ProductSecurity
For connected medical devices, product security starts below the surface. 🩺 Join Finite State at #USCyber2026. Meet with our team to discuss deeper product visibility, vulnerability prioritization, SBOMs, and regulatory evidence.
https://t.co/l9nDhM9gD3
#MedicalDeviceSecurity
Live from #AutoISAC 2026! 🚗 Visit Finite State at Booth #10, Oct. 7 to 8, to see how we help connected-device manufacturers secure every release and prove compliance continuously. Schedule a personalized demo: https://t.co/l9nDhM9gD3
#AutomotiveCybersecurity#ProductSecurity
🚀 Finite State is growing!
We’re looking for talented people ready to tackle important challenges in product security and help secure the connected products and systems we rely on every day. Explore our open roles and help spread the word: https://t.co/iCsPdLwbEG
#Hiring
🚗 Does this vulnerability actually affect our products, and where?
At #AutoISAC 2026, Finite State will show how automotive teams can prioritize real exposure, accelerate PSIRT response, & strengthen security across the software supply chain. 📍 Booth 10 https://t.co/BpwnIlUAh4
Finite State has been named a finalist in the Security Operations & Response category of the SiliconANGLE TechForward Buyer’s Guide.
🔎 Deeper product visibility
🎯 Risk-based prioritization
📋 Defensible security evidence
View the guide: https://t.co/xTONVzbShK #ProductSecurity
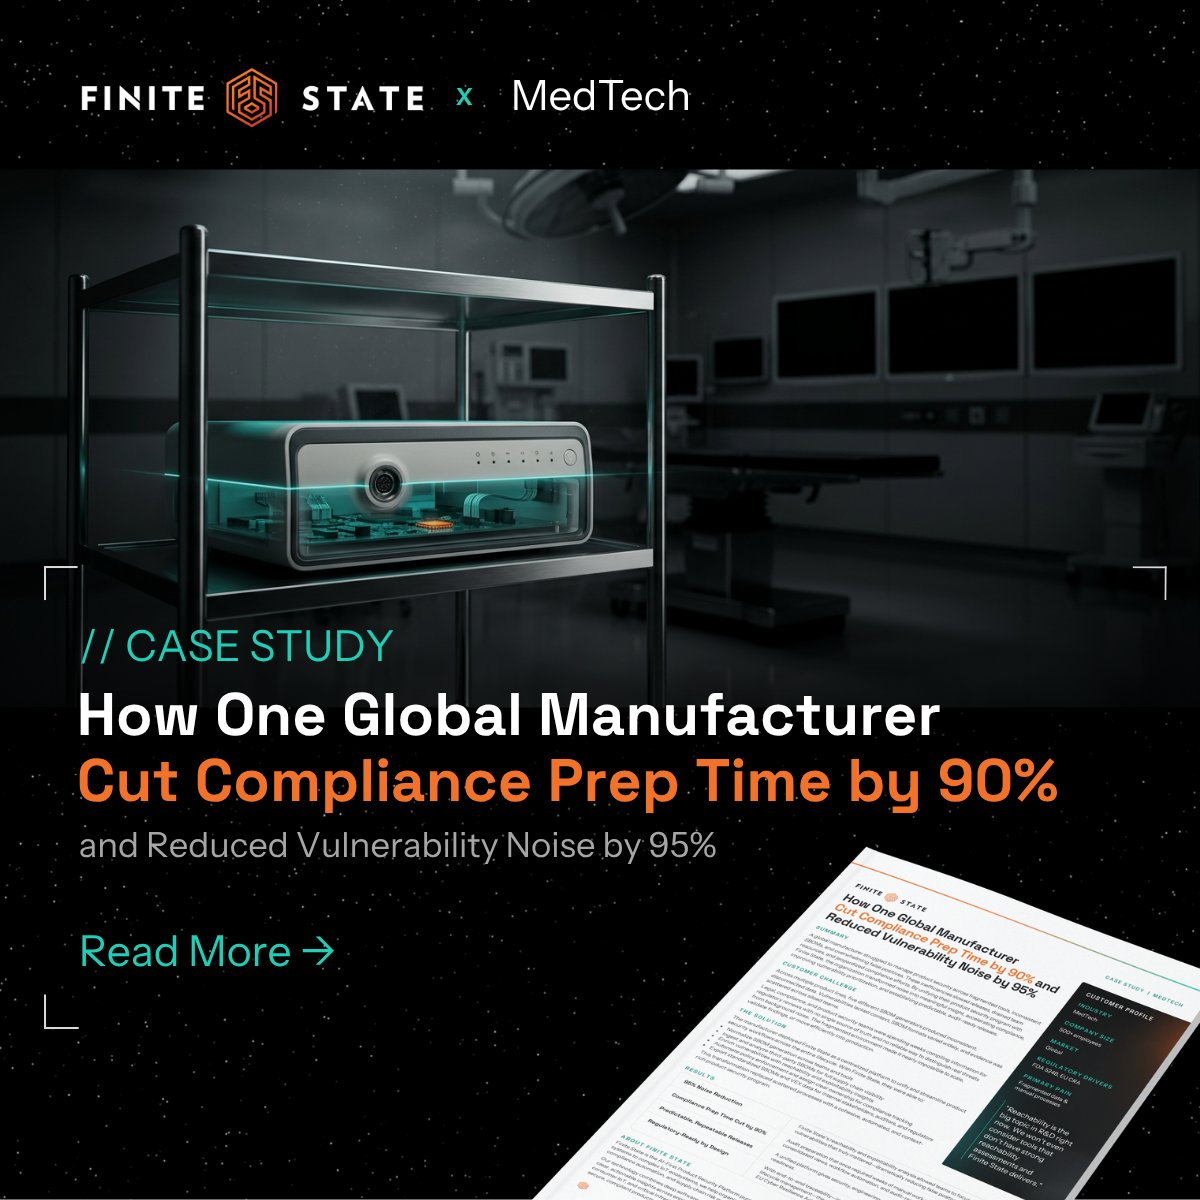
What if your product security team could cut vulnerability noise by 95% and turn weeks of compliance prep into days? One global MedTech manufacturer did it:
🔎 95% less vulnerability noise
⏱️ 90% less compliance prep time
📋 Audit-ready SBOMs + VEX
https://t.co/p9cIJMe8lv
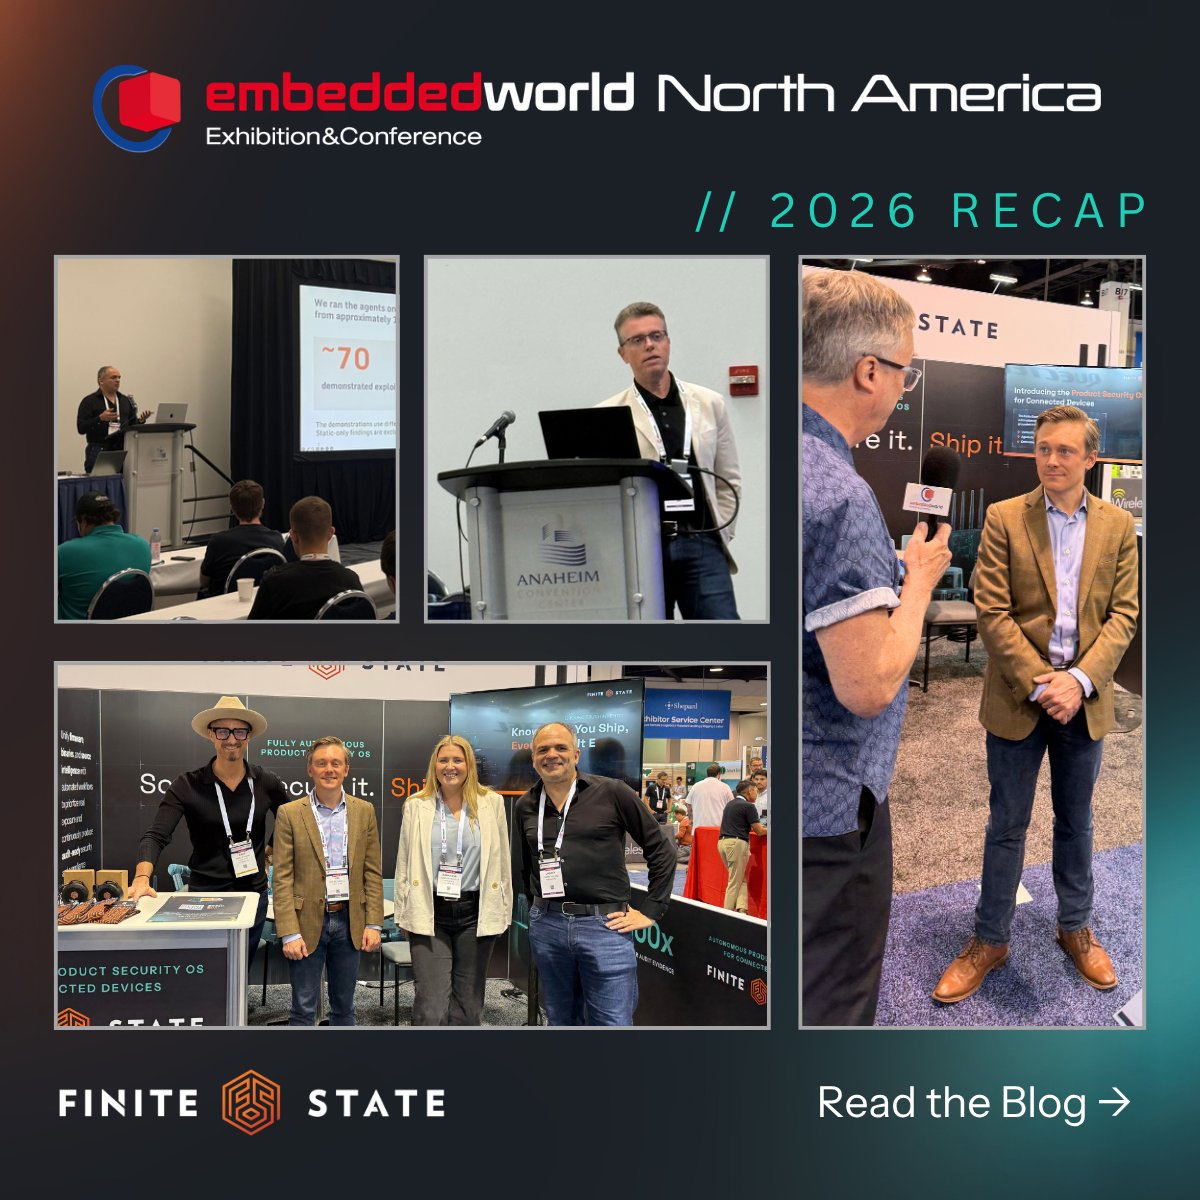
What did #EW26 tell us about product security?
More software, AI & connected products mean more pressure to prove what actually shipped. Our recap explores binary-grounded evidence, CVE impact analysis and AI-assisted firmware testing. https://t.co/VqaOZ4m7BM
#ProductSecurity
🔍 Open source is everywhere in connected products. Understanding its risk has to be continuous.
From #EmbeddedWorldNA: see why ongoing visibility into open source components and vulnerabilities matters for product security.
Request a demo: https://t.co/4neClhI1ze
🔎 What does product security success look like at enterprise scale?
One verified Finite State user put it simply:
💬 “Finite State gives us everything I need... [so] we focus on clearing vulnerabilities.”
Better visibility. More focus on reducing risk.
#ProductSecurity
What does it take to turn product security into defensible regulatory proof?
At #THREATCON1, Finite State’s Doc McConnell will share how teams can build credible security evidence into their programs.
📅 Oct. 6 | 10:30 AM ET
Meet with Doc: https://t.co/4neClhI1ze
Every vehicle software release changes the evidence security teams need to stand behind.
At #AutoISAC, we’re talking about continuously generating audit-ready SBOM, VEX, vulnerability, and product security evidence.
Attending? Meet with Finite State: https://t.co/BpwnIlUAh4
✨ Employee Spotlight: Moiz Shafi
Moiz brings Leverage to life by using AI and automation to streamline workflows, build scalable solutions, and save valuable time across the engineering team. Thanks, Moiz, for continuing to improve how we work!
#EmployeeSpotlight#FiniteState
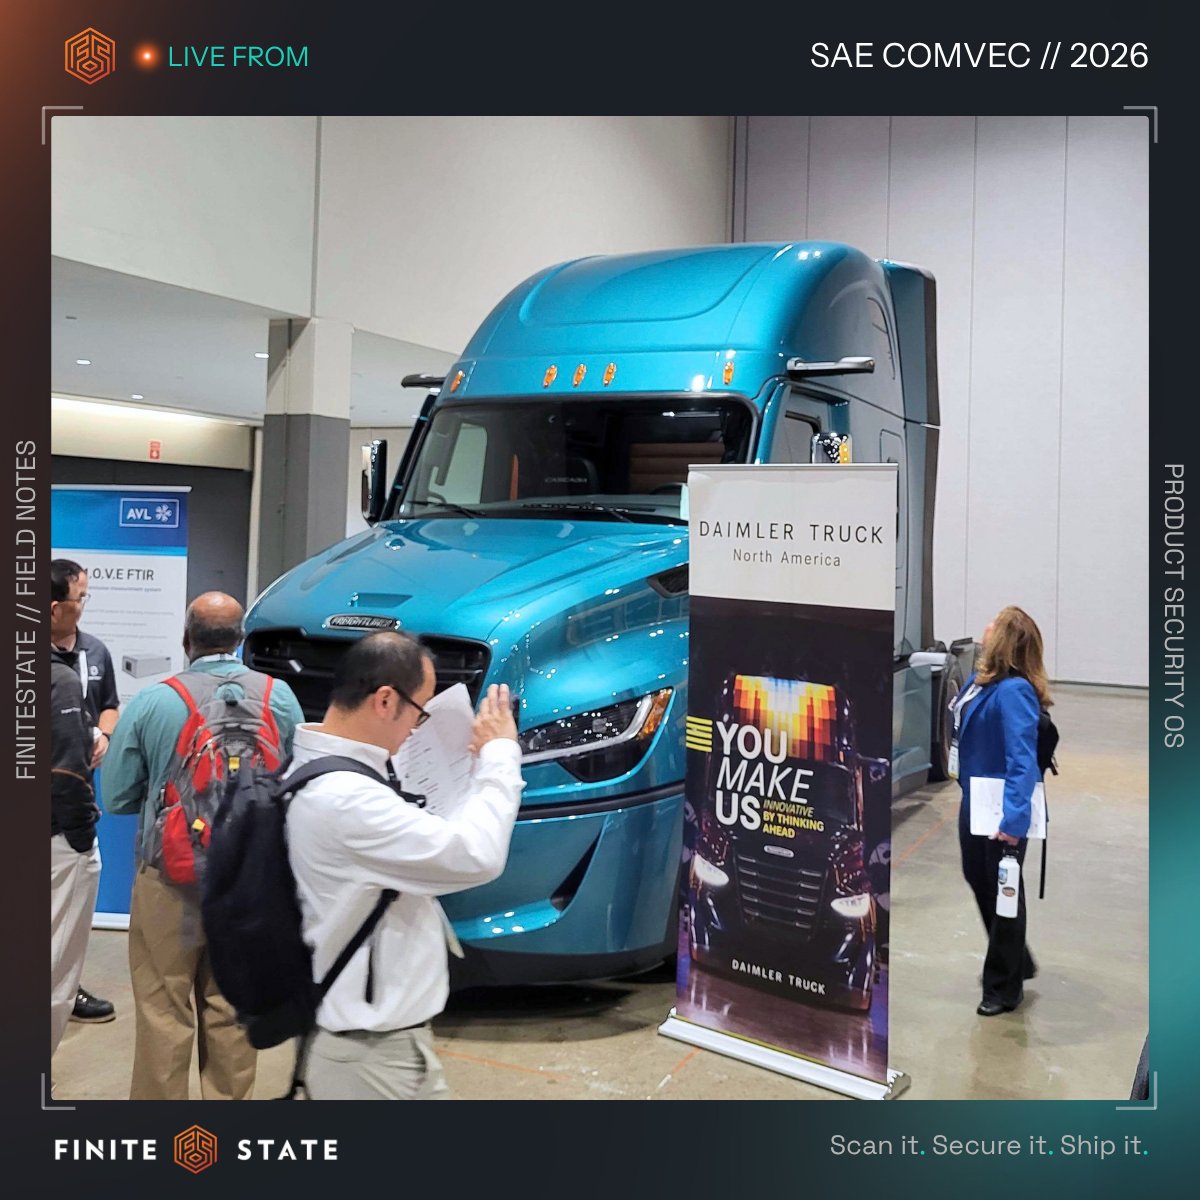
LIVE from SAE COMVEC 2026! 📸
Connect with Cade Jackson, Regional Sales Director at Finite State, to talk continuous product security for software-defined vehicles, from software visibility and real exposure to faster PSIRT response. https://t.co/l9nDhM9gD3 #Cybersecurity
At SAE COMVEC this week? 👋
Connect with Finite State’s Cade Jackson to talk firmware and software supply chain security, SBOMs, vulnerability risk, and vehicle cybersecurity.
📍 Sept. 29 to Oct. 1
📩 [email protected]#SAECOMVEC#VehicleSecurity