Question for security leaders:
How many accounts in your company don't belong to a person?
Service accounts. API keys. Bots. Scripts.
Who owns each one? When was its secret last rotated? Does it have more access than its job needs?
No answer means no control.
#CISO
A backup you've never restored is a hope, not a plan.
Ransomware crews often hit backups first. Keep one copy offline or immutable. Use separate admin logins for it. Run a full restore test every quarter and time it.
#CISO
CISA this week added an auth bypass in GPUStack, a tool for running AI models, to its exploited-flaws list. No login needed to get admin.
AI servers are servers. Inventory them. Keep them off the open internet. Patch them like your VPN.
#CISO
You can't patch what you don't know you own.
This week: list everything internet-facing. Give each system a named owner. Hunt for apps bought on a company card. Repeat monthly.
When did you last find a box nobody knew about?
#cybersecurity#CISO
Logs nobody checks won't save you.
Quick check:
- Sign-in logs kept 90+ days?
- VPN, email and cloud logs in one place?
- Alert when a new admin account appears?
- Can you pull last month's logins in 10 minutes?
Any "no" is your next fix.
#CISO
Researchers keep flagging fake download sites and rigged GitHub repos pushing malware, some posing as security tools.
Your admins are the prize. They hold the keys.
Rule: admin tools come from one approved source. Check signatures. Test before production.
#CISO
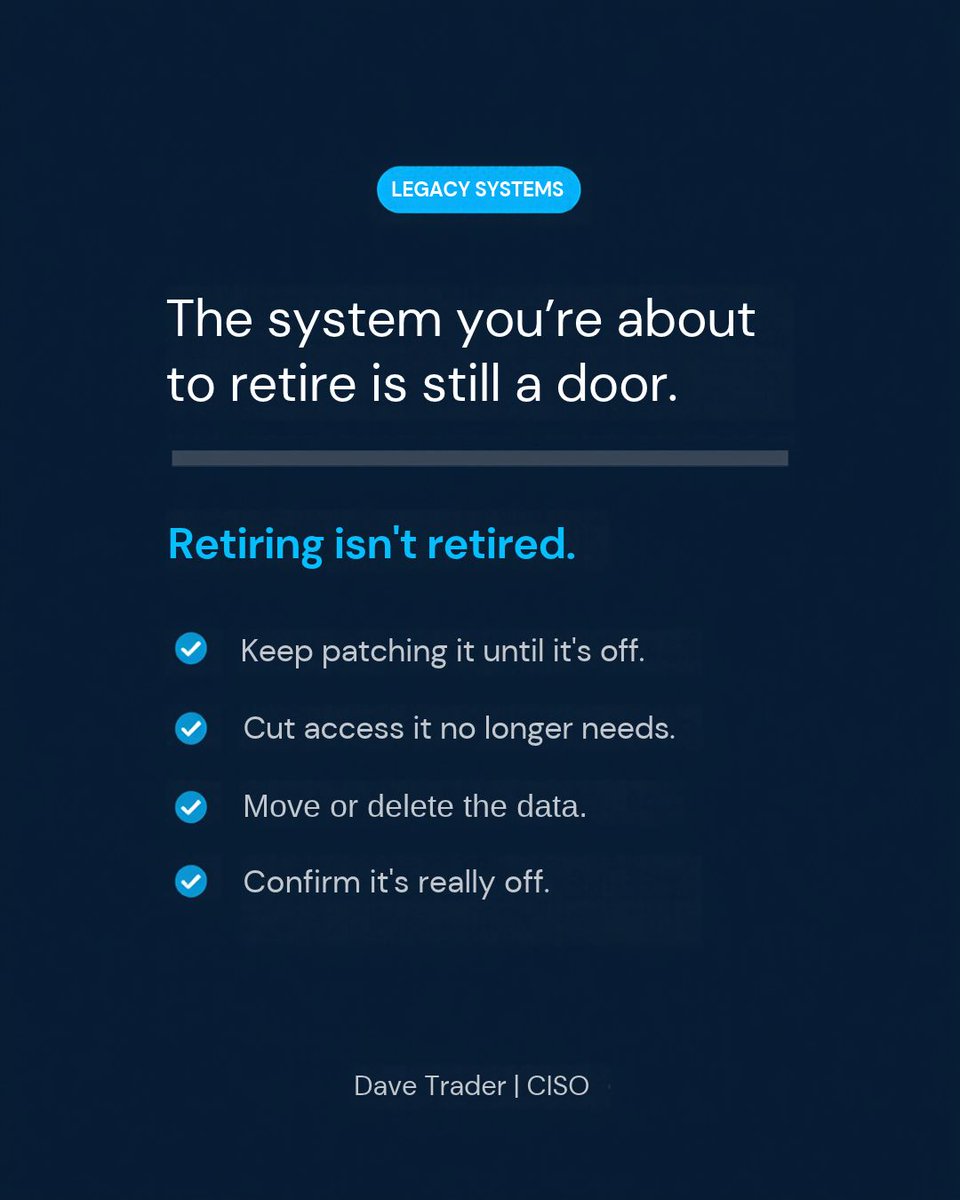
A system with a shutdown date is still a door.
Keep patching it. Cut access it doesn't need. Move or delete the data. Then prove it's really off.
What's the oldest system still running in your shop?
#CISO#cybersecurity
Microsoft's Patch Tuesday landed today.
Question for security leaders: how many days until today's critical fixes are live on your internet-facing systems?
If you don't know the number, you can't defend it. Measure it this month.
#CISO
CISA lists an exploited OpenSSH flaw on musl-based Linux like Alpine and OpenWrt. With PAM off, an overlong password can get into accounts that should be locked.
The boxes you forgot still run SSH.
Find them. Patch. Get SSH off the internet.
#CISO
Holiday scam season is here. Some of your people will click.
The click isn't the failure. Silence is.
Make reporting one button. Answer every report fast. When someone says "I clicked," start with "thank you."
Do your people report it, or hide it?
#cybersecurity#CISO
Thanksgiving is 17 days out. Attackers like long weekends.
Before you leave:
- Name who watches alerts all four days
- Put on-call numbers on paper
- Finish critical patches before the freeze
- Confirm backups restore
- Save your IR and insurer hotlines
#cybersecurity
CISA lists a SonicWall SSL VPN flaw as exploited. With valid credentials for another login method, an attacker may get past SAML and its MFA.
MFA only guards the doors that enforce it.
Patch. Test every login path. Check logs. A patch won't tell you who's already in.
#CISO
Next year's security budget is getting locked in now.
Don't bring a tool list. Name the 3 events that would stop the business. Price them. Fund the basics first.
Then say: "Cut this, and here's the risk you accept."
What would you defend to the end?
#CISO#cybersecurity
Admin rights on every laptop are a gift to attackers.
One click on the wrong file and the malware runs with full control.
Remove standing admin. Grant it per task, time-limited and logged. Your users will adjust. Your attackers won't like it.
#CISO
Google patched a critical Android flaw this month. Code execution, no tap from the user needed. No reported attacks yet.
That quiet is your window.
Look for patch level 2026-11-01 or later. Phone makers ship on their own clock. Check company phones. Don't assume.
#CISO
Attackers research your executives. Do it first.
Search your leaders like an attacker would. Lock down personal email and phones. Require a callback for any urgent ask.
If your CEO's voice called finance today, what would stop the wire? #cybersecurity#CISO
Question for security leaders:
Your top-priority alert fires at 2 a.m. on a Saturday.
Who sees it? Who has authority to isolate a machine or kill an account without waiting for approval?
If you had to think about it, run the test this month.
#CISO
CISA just listed an Apple flaw as actively exploited. Apple patched it in May 2024.
Old bugs don't expire. They wait on devices nobody updated.
Can you name every iPhone and Mac touching your data, and its OS version? If not, start there.
#CISO
Nobody hacked it. It was left open.
One report counted 19.6B files in 535K publicly listable cloud buckets.
Block public storage account-wide. Name an owner for every bucket. Alert on any change to public.
Who owns your cloud settings?
#cybersecurity#cloudsecurity
Phishing kits are stealing Microsoft 365 access with device codes.
The user enters a code on the real Microsoft page and approves MFA. The attacker gets the tokens.
Block device code flow unless you need it. Teach one rule: never enter a code you didn't request. #CISO