@tryhackme I made the payment for the subscription twice. The funds were deducted from my account, but I am still unable to access the services I have subscribed to.
I tried to contact the support however the wait time is around a week 😞
I recently got a dupe on a complex, 35k crit.
It feels like taking a punch to the gut.
Duplicates can be one of the most challenging parts of bug bounty, especially for beginners.
Here is my system for dealing with dupes:
1. Avoid them
Its best to not get a dupe in the first place. In order to do so you either need to be fast to report a bug or report weird shit. To be fast, you'll need to invest in building some automation to alert you when new endpoints have been pushed into a JS file or when a new subdomain pops up. If you're reacting within an hour or so, its unlikely you'll get a dupe.
The alternative to being fast, and my preferred technique, is to report weird shit (ie, go deep and find bugs no one else is finding). You need to think of attack vectors that others have not come up with which means you need to have a deeper understanding of the application than most people. Read the code. Read the docs. Spend time ideating. When you go deep, you will rarely have bug collisions (though they do occasionally happen, like the 35k bug above).
2. If you suspect a report may be a dupe, report quickly and keep the report bare bones
After a little while you kind of get a 6th sense on whether someone has already reported a bug or not. If they have, any time you spend writing a report is wasted time. Instead of building out a full PoC for XSS -> ATO, simply report the alert with a couple lines of text explaining the bug. Spend less than 5 minutes on the report until you've confirmed whether its a dupe or not. Feel free to put in the report that you can fill in more details once the dupe status is sured up.
3. Confirm the dupe
When you dupe, make sure you get the report number of the original report. I've had triagers go back to get the report number and realize it wasn't a dupe. Once you've got the number (and confirmed it is before yours) then ask to confirm that the details of your bug are the same. Just because its the same endpoint doesn't mean that its the same bug. Did you do something differently than others might in this situation? Then your report might be different.
4. When you dupe, breath.
At the end of the day, most of the time a triager dupes your report, its gonna be a dupe. If this is a particular gutting dupe, step away and breath it out. I normally go get a hug from my wife. I also try to look at the bigger picture and accept that dupes are a part of the bigger game of bug bounty. Avoid the internal narrative that all that work was for nothing, because everyone will get dupes sometimes. Its unavoidable.
GLHF, find bugs!
🚨 New GIVEAWAY 🚨
It's been a year since the announcement of our first certification, #CBBH, and we're celebrating!
Want to be the one to win a Silver Annual subscription?
1️⃣ Follow HTB and @Hacker0x01
2️⃣ Like & RT this post
Good luck 🍀
#BugBountyHunting#HTB#Hacking
As much as I hate that @LinusTech got hacked. How he responded is pretty amazing, and shows how anyone can become the victim of social engineering/phishing. And kudos to him for taking responsibility himself, not easy for anyone to do especially publicly. https://t.co/b2BUsYMh8L
We're back with another week of the #burpchallenge
For a chance to win Burp swag:
1. Complete all 6 practitioner-level XXE labs this week.
2. Then Tweet your progress using #burpchallenge.
Complete by Sunday to be eligible. https://t.co/P0BxAFhyzw
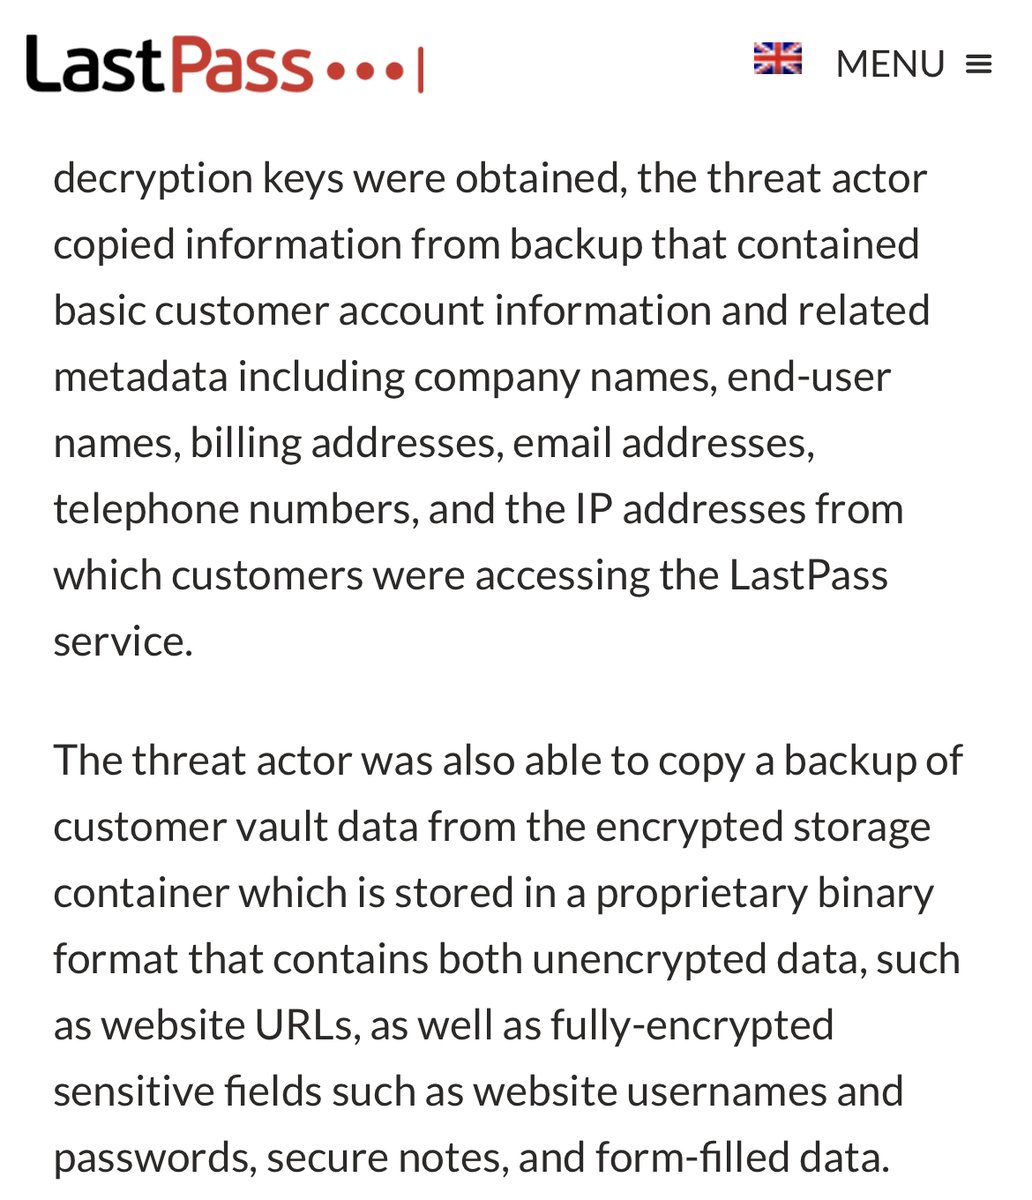
Bardzo, bardzo, bardzo grubo. LastPass przyznał, że wykradziono bazy haseł klientów. Teraz ich bezpieczeństwo zależy już tylko od tego, jak silne było wasze hasło i ile mocy obliczeniowej ma sprawca ataku. Chyba najciekawszy incydent 2022. https://t.co/hsk5HEiSa7
Ho ho hackety ho! 🎅
To celebrate the launch of #AdventOfCyber, we’re giving away a limited edition #TryHackMe Yeti t-shirt. All you have to do is like and retweet!
The winner will be chosen at random on Sunday and announced on Monday 12th December. Good luck! 🤞
Final Giveaway! This time for #Cyber Monday
Make sure you check our deals: https://t.co/FuZ7cX2kTd
We are going to send a t-shirt and a few goodies to one person who retweets this tweet!!
And we are going to give a 12-month voucher to someone who likes this tweet!!
GIVEAWAY!🚨
Advent of Cyber is 9 sleeps away, but we're feeling festive now!
Like and share this post, and join the Advent of Cyber room ready for December to win:
🎁 Christmas t-shirts
🎁 TryHackMe vouchers
🎁 Extra raffle tickets for $40,000 of prizes
https://t.co/goV4HratBh
Time for another giveaway!
We are going to send a t-shirt and a few goodies to one person who follows
@PentesterLab and retweets this tweet!!
And we are going to give a 12-month voucher to someone who follows
@PentesterLab and likes this tweet!!
1,000,000 people use TryHackMe!🔥
🎉 We're giving away a bunch of year-long subscriptions to TryHackMe, plus limited edition t-shirts! Share this post and leave us a comment to enter👇
Here's our journey, the launch of new training labs, and a thank you!
https://t.co/N5Pz2DyBDi