اگر هنوز نمیدونی Dots چیه، این مطلبو بخون 🚨
اول از همه باید ببینی فرق Dots با اجنتسازهایی مثل OpenClaw چیه.
دات یه کامپیوتر و مرورگر ابری مخصوص خودش داره. به اپهات وصل میشه و همزمان چندتا پروژه رو جلو میبره، دقیقاً مثل Muse و Grok Bot. یعنی لازم نیست هی بشینی قدمبهقدم بهش بگی بعدش چیکار کنه.
قسمت دیوونهکنندهش اینه که دات منتظر دستور تو نمیمونه. یه قابلیت داره به اسم Proactive Research. یعنی حتی وقتی باهاش کار نمیکنی، میره توی اپهایی که بهش دسترسی دادی میچرخه دنبال چیزایی که احتمالاً نیاز به توجه تو دارن.
مثال خود OpenAI خیلی جالبه: دات یه کاربر فهمیده بود یادش رفته برای یه نشریه فاکتور بفرسته. خودش فاکتور رو آماده کرده و فقط برای ارسالش تأیید گرفته.
کانتکست هم همهجا باهاش میمونه. تو ChatGPT شروع میکنی، تو Slack یا Teams ادامه میدی، حتی میتونی باهاش وویسکال داشته باشی.
برای شرکتها هم Specialist Dot میسازن. هر کدوم یه هویت و دسترسی مشخص و یه مسئولیت مشخص دارن؛ مثل Procurement Dot و Support Dot و Invoice Processing Dot و Marketing Dot. فعلاً هر کاربر یه دات اصلی داره ولی OpenAI میگه آپدیت بعدی یه تیم از داتها همزمان برات کار میکنن.
سهتا نکته هم از اطلاعات دیشب: با GPT-6 Astra کار میکنه که قویترین مدلشونه، میگن به ۴۰۰۰+ اپ وصل میشه، و فعلاً فقط Pro و Business دارنش، اگه Plus داری فعلاً خبری از داتس نیست.
بهعنوان شهروند ایرانی به شدت مراقب باشید. تو گزارش سناتور بلومنتال اومده که تتر خیلی کمکاری کرده و هنوز هم پیشگیرانه همه کیف پولهای آشکارا غیرقانونی رو بلاک نمیکنه و از وزارت خزانهداری خواسته فوراً تتر رو از نظر نقض احتمالی تحریمها و قوانین بانکی بررسی کنن.
The dataset is still in its raw form and needs some cleaning/normalization before it’s ready for ML training.
Also available on GitHub — a ⭐️ would be appreciated!
https://t.co/0Qzyt1YEAV
23 625 smart contract vulnerabilities — open sourced
I collected these findings over the past year from private audit reports and contest platforms
Hopefully, it’ll be useful for security researchers and people working on AI for smart contract security
https://t.co/SgY7J1crlr
🤯 Someone has released a dataset with over 23,000 smart contract security audit findings, free to download
Severity, proof of concepts, recommended fixes, everything is inside - it's a GOLDEN MINE. Thank you @RightNowIn - amazing contribution🔥
https://t.co/ejmuCuCkRK
@pashov Not fully today. But I think it's absolutely possible to build. The real challenge is giving the model both deep protocol-level understanding and the ability to reason through complex code and attack surfaces.
how to get rich in web3 (without scamming):
learn to find Critical & High Severity vulnerabilities in web3 projects' code
this space's been printing millionaires for years now, easy - all guys who've truly put in the work daily have made it - be the next one🫡
`solidity-auditor` v3 from pashov/skills has found countless Critical/High vulnerabilities for Solidity devs & security researchers
v4 is coming this week. Better recall than ever. Fully Open Source, MIT License, built to serve everyone in the Solidity community. Get ready🫡
اگر تو حوزه #رمزارز کار میکنید و میخواهید تحریم نشید باید مراقب باشید. ممکنه شما هیچ اقدامی نکنید اما کسی که باهاش یا براش کار میکنید کاری بکنه.
در نظر داشته باشید که تمام تتری که تو ایران در اختیار مردم هست فقط تو بازار ایران اعتبار داره و عملا برای بقیه دنیا سیاهه.
Since many people are learning about effective altruism, it's worth learning about Mozi, the ancient Chinese philosopher who was surprisingly close to being a proto-effective-altruist (particularly the global-health-focused variety, not the AI-risk-focused variety).
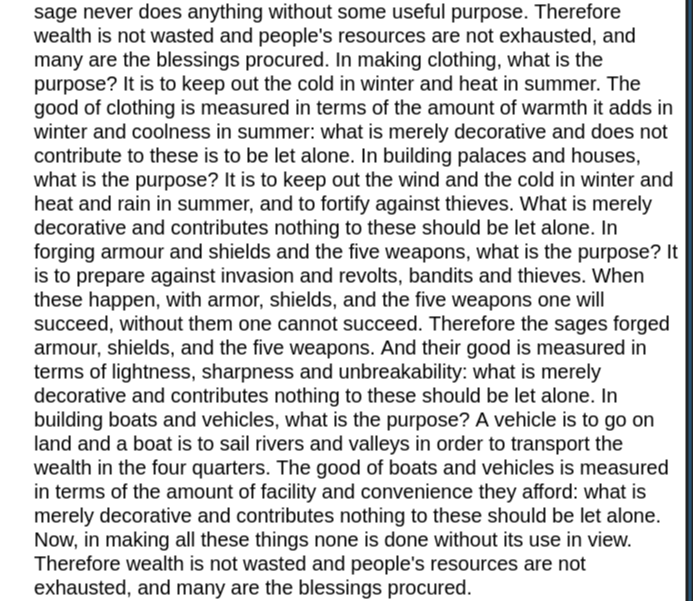
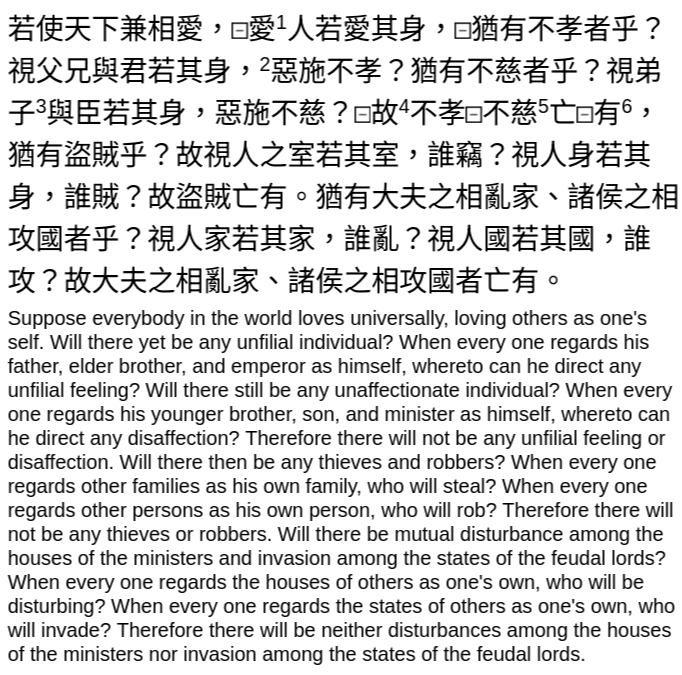
He valued the twin goals of (i) universal love, loving everyone and not just yourself and people similar or close to you, and (ii) being efficient about how you use your limited resources to most effectively help people.
https://t.co/eYLH7Inzl9