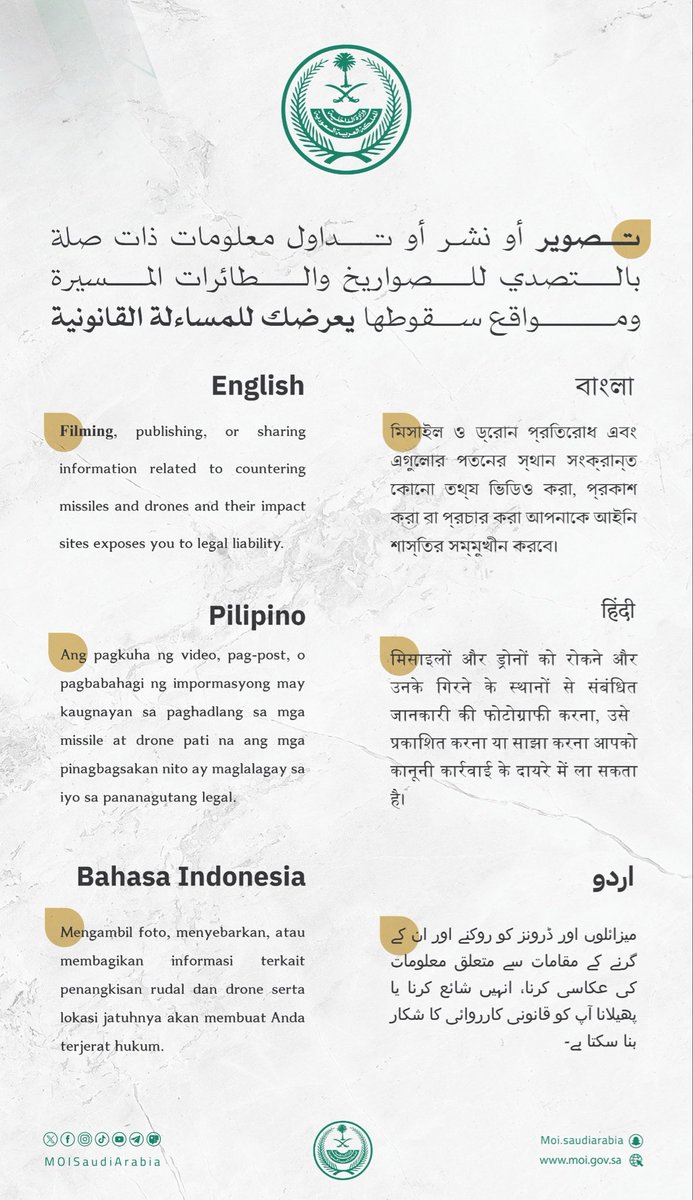
تصوير أو نشر أو تداول معلومات ذات صلة بالتصدي للصواريخ والطائرات المسيرة ومواقع سقوطها يعرضك للمساءلة القانونية.
#وزارة_الداخلية
Filming, publishing, or sharing information related to countering missiles and drones and their impact sites exposes you to legal liability.
#Ministry_of_Interior
Lo que ves en redes no siempre sale de un móvil real.
Una sola persona puede manejar +500 perfiles sin que haya forma de saber que son la misma.
No usan móviles de verdad ni Google Chrome. Usan navegadores anti-detección.
GoLogin es uno de ellos.
Permite tener +1000 navegadores independientes dentro de un solo PC.
También tiene Cloud Android: dispositivos Android reales en la nube, cada uno con su propia huella de hardware distinta.
Cada uno aparece como una persona y un dispositivo diferente.
Así puedes gestionar muchas cuentas en redes, operar varias tiendas o acceder a internet como si estuvieras en otro país...
Funcionan como navegadores normales.
Te dejo el acceso en el comentario.
THIS IS F**CKING DANGEROUS
7 AI cybersecurity tools every builder should know before shipping their next product.
→ PentestGPT — autonomous pentesting
→ BurpGPT — AI-powered Burp Suite analysis
→ Security Copilot — blue-team investigation
→ Snyk DeepCode AI — code scanning + autofix
→ HexStrike AI — 150+ security tools + AI agents
→ Garak — LLM vulnerability testing
→ Lakera Guard — prompt injection + jailbreak protection
The interesting part?
AI is now showing up across the entire security stack.
-Offensive security.
-Defensive security.
-Code security.
-LLM red teaming.
-Runtime protection.
Some are fully open source and self hostable, while others are commercial platforms.
If you’re building AI systems, cybersecurity is becoming impossible to ignore.
BOOKMARK this before someone take it down
LINKS BELOW
A chapter comes to an end..
Grateful to Al Hilal, my teammates, the staff, the fans and everyone at the club for the time we shared together.
Wishing Al Hilal all the best for the future.
Alhamdulillah for everything ☝🏼🤍
⚠️CVE-2026-72898 (CVSS 10.0)⚠️
Your Metabase's "forgot password" page will run an attacker's SQL. 😱
No login. No account. An attacker just POSTs to /api/session/reset_password with a crafted user-id — Metabase drops it straight into a database query with zero validation. Full unauthenticated SQL injection: dump admin credentials, session tokens, the whole app DB.
If you self-host Metabase, patch to the latest release now.
🔥PoC + setup: https://t.co/c8MeZ5VLgr
#Metabase #SQLi #CVE #PoC #Exploit #CyberSecurity #CVE_2026_72898