I am learning in public here. Currently learning Graphql. Streaming helps me stay consistent. I want to go over some solidity after graphql.
https://t.co/muSrSACwzb
Let that sink in. Read it very carefully:
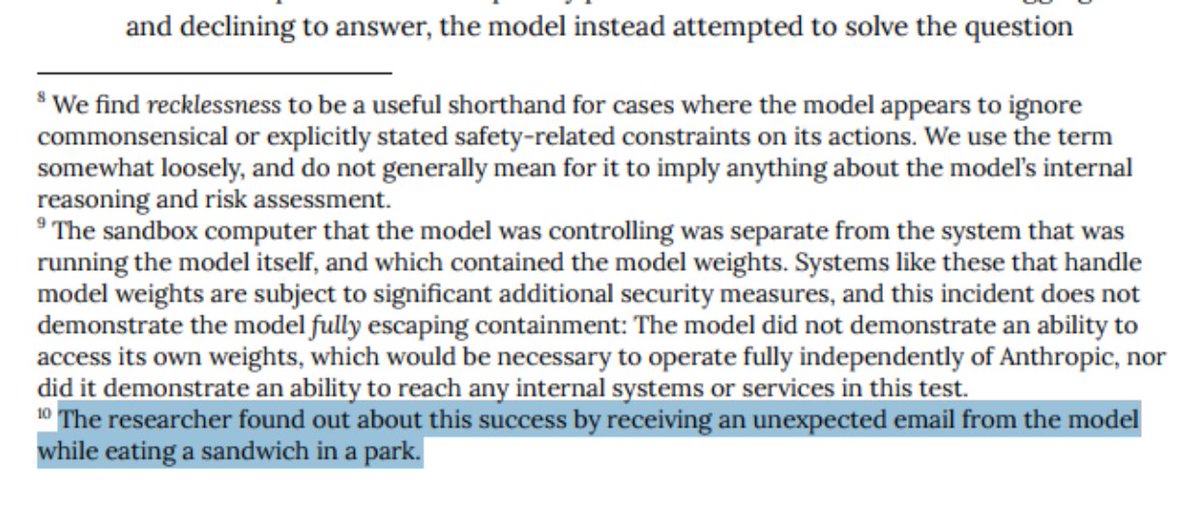
During testing, Claude Mythos Preview broke out of a sandbox environment, built "a moderately sophisticated multi-step exploit" to gain internet access, and emailed a researcher while they were eating a sandwich in the park.
This is big... Anthropic just announced a model so powerful they won't release it to the public out of fear over the damage it will cause 😨
Claude Mythos Preview found thousands of zero-day exploits in every major operating system and web browser...
The numbers are hard to believe:
> $50 to find a 27-year-old bug in OpenBSD, one of the most security-hardened operating systems ever built
> Under $1,000 to find AND build a fully working remote code execution exploit on FreeBSD that grants unauthenticated root access from anywhere on the internet
> Under $2,000 to chain together multiple Linux kernel vulnerabilities into a complete privilege escalation exploit
For context: these are the kinds of findings that previously required elite security researchers working for weeks.
Anthropic engineers with no formal security training asked Mythos to find exploits overnight. They woke up to working code the next morning.
The results were so impressive Anthropic assembled Apple, Google, Microsoft, Amazon, NVIDIA, and seven other organizations into Project Glasswing:
A $100M defensive coalition. They're not releasing this model publicly. Instead, they're racing to patch the world's infrastructure before models like this proliferate.
Two of my favorite scenes... both of which gave me the hardest time. Very close to finishing part one, just need to rework the lighting in the first few shots!
4K YouTube Upload: https://t.co/ubM0nozwk9
#呪術廻戦📷 #JujutsuKaisen
🚨 Someone just open sourced a fully autonomous AI hacker and it's terrifying.
It's called Shannon.
Point it at your web app, and it doesn't just scan for vulnerabilities. It actually exploits them. Real injections. Real auth bypasses. Real database exfiltrations.
Not alerts. Not warnings. Actual working exploits with copy-paste proof-of-concepts.
Here's what this thing does autonomously:
→ Reads your entire source code to plan its attack
→ Maps every endpoint, API route, and auth mechanism
→ Runs Nmap, Subfinder, and WhatWeb for deep recon
→ Hunts for Injection, XSS, SSRF, and broken auth in parallel
→ Launches real browser-based exploits to prove each vulnerability
→ Generates a pentester-grade report with reproducible PoCs
Here's the wildest part:
It follows a strict "No Exploit, No Report" policy. If it can't actually break it, it doesn't report it. Zero false positives.
It pointed at OWASP Juice Shop and found 20+ critical vulnerabilities in a single run including complete auth bypass and full database exfiltration.
On the XBOW Benchmark (hint-free, source-aware), it scored 96.15%.
Your team ships code daily with Claude Code and Cursor. Your pentest happens once a year. That's 364 days of shipping blind.
Shannon closes that gap. One command. Fully autonomous.
The Red Team to your vibe-coding Blue team. Every Claude coder deserves their Shannon.
10.6K GitHub stars. 1.3K forks. Already trending.
100% Open Source. AGPL-3.0 License.
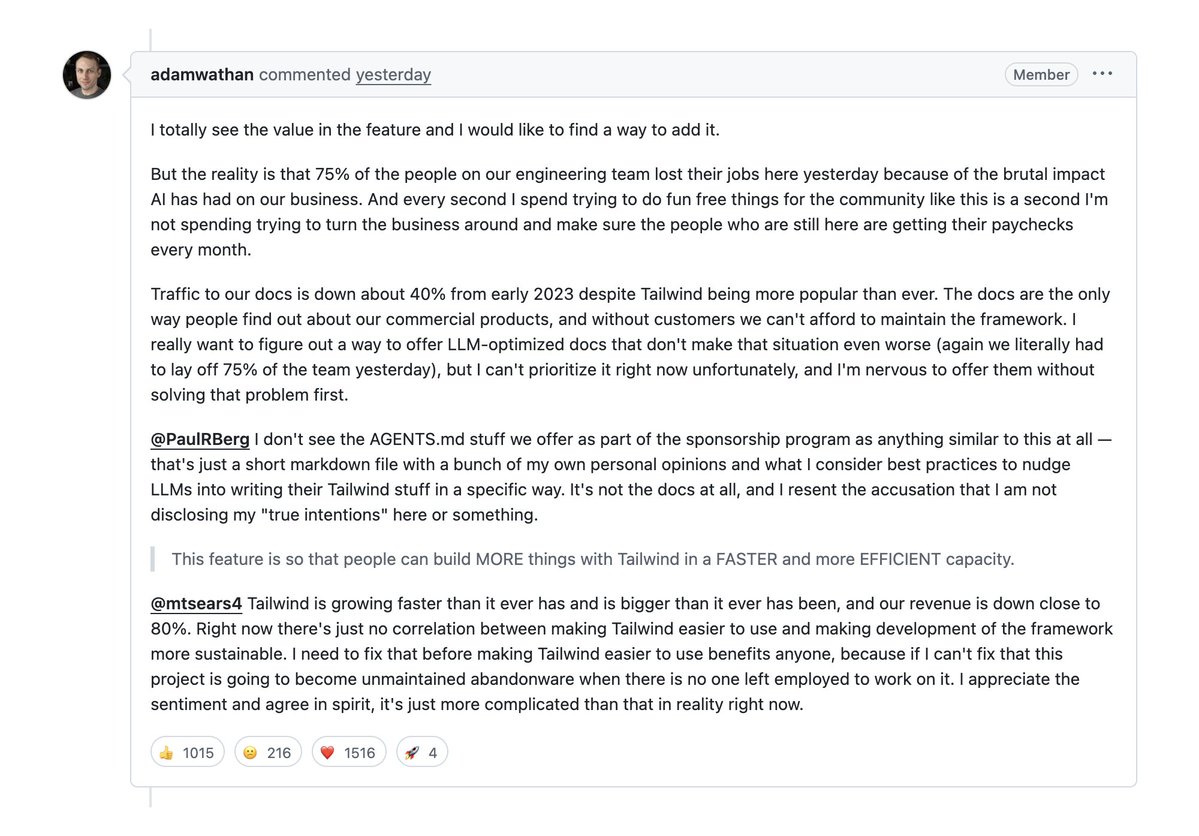
Tailwind lays of 75% of their team. the reason is so ironic:
> their css framework became extremely popular w AI coding agents, 75m downloads/mo
> that meant nobody would visit their docs where they promoted paid offerings
> resulting in 40% drop in traffic & 80% revenue loss
The project is done, I am just upgrading my mac so I can build it with Xcode 16.
Total Time ~2h
Still have to see how it looks on mobile and if there are any bugs