Email verification infrastructure for developers and AI agents.
Verify OTPs and magic links from code — no Docker, no regex, no signup.
Built on @Cloudflare's edge.
https://t.co/ZmBeS7woI7
ZeroDrop — disposable inboxes for CI and AI agents. Your test triggers a real signup, we catch the email at Cloudflare's edge and hand back the OTP/magic link as a field. No Docker, no regex, no signup.
Just shipped a deep-dive on why fake SMTP servers pass builds that are actually broken: https://t.co/tep3YshxMs
Mailtrap catches your email before it ever leaves the building. That's the feature — and it's exactly why your CI never tests the thing that actually breaks.
The two tests people conflate: does the mail render, and did the provider accept it.
https://t.co/HYeUGoqOP1
Both are the live questions. Deliverability is the sharper one — a shared disposable domain gets flagged, which is exactly why the paid tier is custom domains rather than volume limits. On abuse: monitoring pattern shape now (sender domains, inbox prefixes), policy published, enforcement deliberately held until signal warrants it. Appreciate the specificity.
New post: RSpec email testing without MailCatcher.
ActionMailer's deliveries array only proves you *called* the mailer. It won't catch a broken template, a bad SMTP key, or an OTP that doesn't match the DB.
Real email verification in CI — no daemon, no regex.
https://t.co/osqvhsvXOy
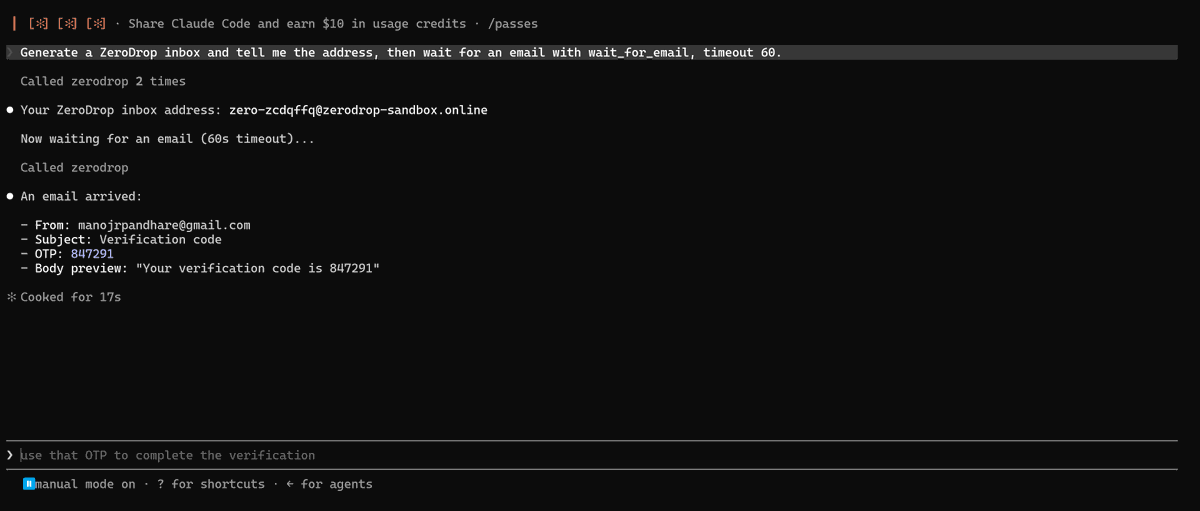
Your AI agent can now verify email signups.
zerodrop-mcp gives Claude, Cursor, and any MCP client three tools: generate a disposable inbox, wait for the email, read the OTP — pre-extracted, no parsing.
claude mcp add zerodrop -- npx -y zerodrop-mcp
Free. No signup. Listed in the official MCP Registry.
A lot of authentication bugs aren't authentication bugs.
They're email reliability bugs.
If verification emails arrive late, password resets fail, or magic links expire before users receive them, the login experience breaks.
Email is part of your auth infrastructure.
Every authentication flow has an invisible dependency.
Email.
If verification emails are delayed, users think your app is broken.
Reliable email isn't just about deliverability.
It's part of your application's uptime.
People think about email when they're sending newsletters.
Users think about email when they're trying to sign in.
Password resets. Magic links. OTP codes. Verification emails.
If email isn't reliable, neither is your authentication flow.
That's why email infrastructure deserves as much attention as your API or database.
A surprising number of developers spend weeks building features, then treat email as an afterthought.
Until password resets fail.
Receipts don't arrive.
Verification emails land in spam.
Email isn't just another feature.
It's infrastructure.
Just published two guides on testing auth email flows in Playwright:
→ Testing Clerk email verification without hitting the 100 email limit
→ Testing NextAuth magic links without smtp-tester or Cheerio
email.otp and email.magicLink auto-extracted — no regex, no Docker, no fake addresses.
@chaosengineerr@Anubhavhing you can't, coding/building is the easy part.. even a solid product without proper marketing and distribution would fail. like @Anubhavhing said, you cant vibe your way through it..
Just published: How to test Better Auth email verification, magic links, OTP and password reset with Playwright.
email.otp and email.magicLink auto-extracted — no regex, no Docker, no shared inboxes.
Includes working example repo.
https://t.co/k8TDsuLfGN
@better_auth@bekacru
Resend solved sending.
We built the missing verification step.
An end-to-end example for testing email verification, magic links, OTPs, and password resets with Playwright:
📤 Resend → 📥 ZeroDrop → ✅ Assertions
https://t.co/301P5ypzm3
@resend
Built an example repo for testing Better Auth email flows with Playwright.
Covers all 4 flows:
→ Email verification
→ Magic links
→ Email OTP
→ Password reset
email.otp and email.magicLink auto-extracted — no regex, no Docker.
https://t.co/IqLaoAwrVK
@better_auth@bekacru