@maomao000211 worktree per agent. that's the thing
lol worktrees kept them from overwriting each other, but 29 still crossed lanes when it all merged back. that's the gap staked's hook covers
just shipped two open-source tools.
both came from running claude code, codex and cursor on one repo: 4 agents, 24 days, ~1,600 commits.
29 of those commits touched two agents' work at once. nothing caught them.
@mmisbbahh both layers. worktrees per agent so they don't overwrite each other while working. staked on top so what comes back stays in each agent's paths. there's also staked lock for shared stuff like the db schema, with a ttl
@kylekane a check. one roles.yml says which paths each agent owns, and a pre-commit hook refuses commits outside that. repo stays one repo. the hook is the whole point of staked
@carlomakes not always. each one touched paths owned by two different agents in one commit. sometimes the same file, mostly the same area from two sides. that's the part nobody reviews.
honest limits: the hook is a check, not a sandbox. --no-verify skips it. free models after a switch are weaker, so review what they do.
both free, MIT. windows reports welcome.
Security tools have a bad habit:
once they scream, they keep screaming.
I asked Sentrail to explain a Postgres finding.
It checked fresh DB evidence and basically said:
this alert is probably stale.
Finding bugs matters.
Knowing when not to scare you matters too.
Security tools have a bad habit:
once they scream, they keep screaming.
I asked Sentrail to explain a Postgres finding.
It checked fresh DB evidence and basically said:
this alert is probably stale.
Finding bugs matters.
Knowing when not to scare you matters too.
Building Sentrail to run that second check… code, auth, secrets, before you ship.
If you build with Replit, Cursor, Lovable or v0 I want 5 minutes. Voice, no signup. https://t.co/5AraRzUijR
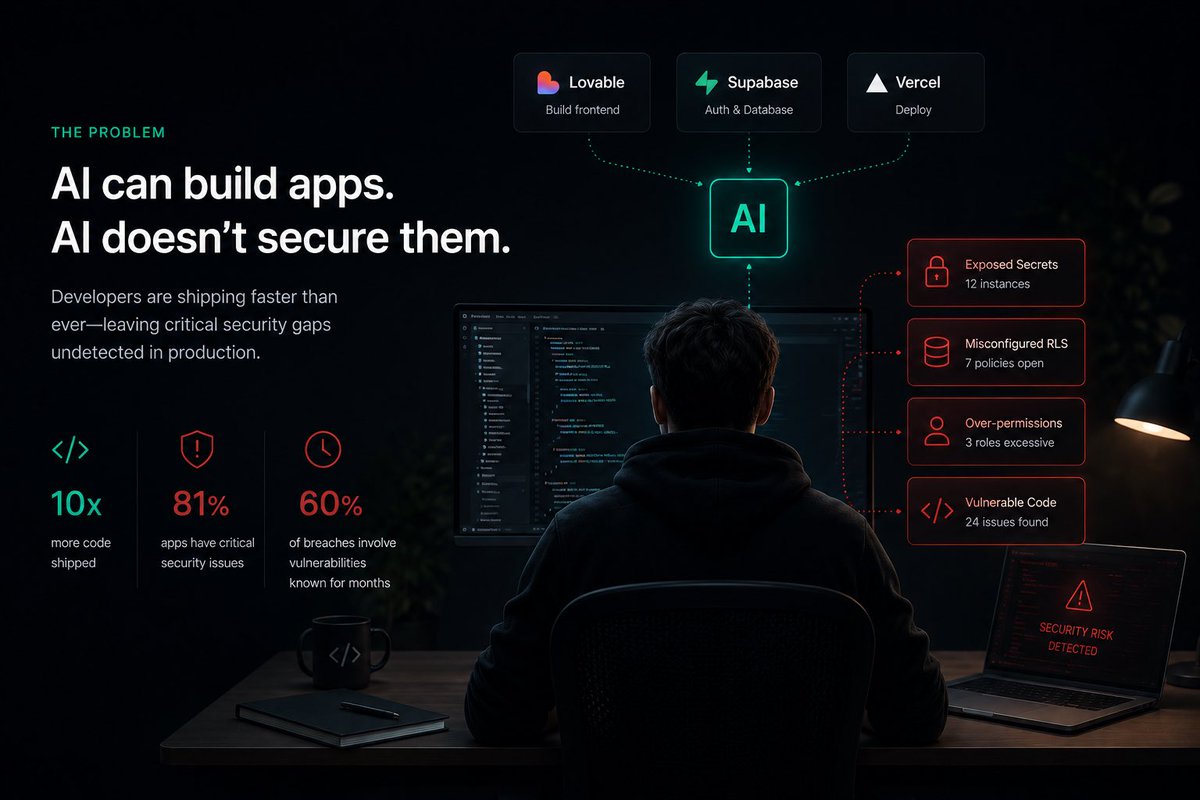
AI writes the code and AI reviews the code.
Same model, same blind spots. It doesn’t catch the leaked key in the frontend because it’s the thing that put it there.
Working and safe to ship are not the same check. Almost nobody is running the second one.
Building with Cursor, Lovable, or v0?
AI writes code that works. Not code that's secure.
No auth middleware. No errors. Just ships.
I'm building Sentrail to fix this. First I want to hear how you handle it — 5 min, voice, no signup.
https://t.co/5AraRzUijR
This app was working perfectly.
Sentrail found 13 critical security issues.
That’s the part of AI coding I think we’re underestimating.
AI can build incredibly fast.
But working ≠ safe to ship.
Who’s verifying what the agents build?
@saikatx I’m building Sentrail — it checks your Supabase, GitHub, and Vercel setup to find what could put your app at risk before you launch.
https://t.co/4bjK7R9Ev6
@JonBuildsHQ I’m building Sentrail — it checks your Supabase, GitHub, and Vercel setup to find what could put your app at risk before you launch.
https://t.co/4bjK7R9Ev6