claude found this one and built a 0-click rce chain: it takes 48min to leak a kernel pointer and defeat kaslr remotely, and another 5min to hijack the control flow and root the server over the network. patch it now (or disable mptcp).
the version-specific stack pivot :
- Node 20/23: pivot through rcx, which holds the ring-buffer base
- Node 24: mov rax,rdi; lea rsp,[rax+0x30]; ret
- Node 25: pop rsp; ret, followed by a calibrated ring-buffer address
At Google CTF in Singapore with TeamH4C, I came across Node2Shell on X. php2shell already feels well-trodden, so I dug into Node2Shell instead and published the analysis on SAGO, our 1-day platform.
📝 Write-up: https://t.co/Wa6kjiQrq9
💻 PoC & exploit: https://t.co/F1zO11XEQD
At today’s GEEKCON, a researcher demonstrated what I believe is the first remote full-chain exploit of a latest WELL-KNOWN drone.
Our Pwn2Own-style live competition never released vulnerability details on those success trials. Actually we did not even show the vendor’s name in plaintext.
However, a guy from that vendor called POLICE on-site to take the researcher out for “investigation”.
It’s extremely disappointing that in 2026, some still view security work from such a bad perspective.
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
Maybe someone will give access to the right models to those working on securing the Web3 space. @claudeai, how is the approval for Mythos coming along? /s
NEW: rust-review — a security review plug-in for Rust, built by @zi0Black of Aptos Labs' Security Team with Paweł Płatek of @trailofbits.
Rust's compiler gives you memory safety. It won't flag misused unsafe code, silent overflows, or nondeterminism. rust-review does.
Move on Aptos keeps moving! In addition to large extensions to the specification language, we added a number of exciting new features to Move 2.4, among the most impactful one, public structs and enums! Check it out here.
https://t.co/1rIXEGMNL8
The next great exchange was always going to be onchain.
For over a decade, traders have been forced to choose: the speed of a CEX or the transparency of a DEX. Never both.
Traders deserved better. We built better.
Decibel is LIVE!
Welcome to the new sound of trading 🔊
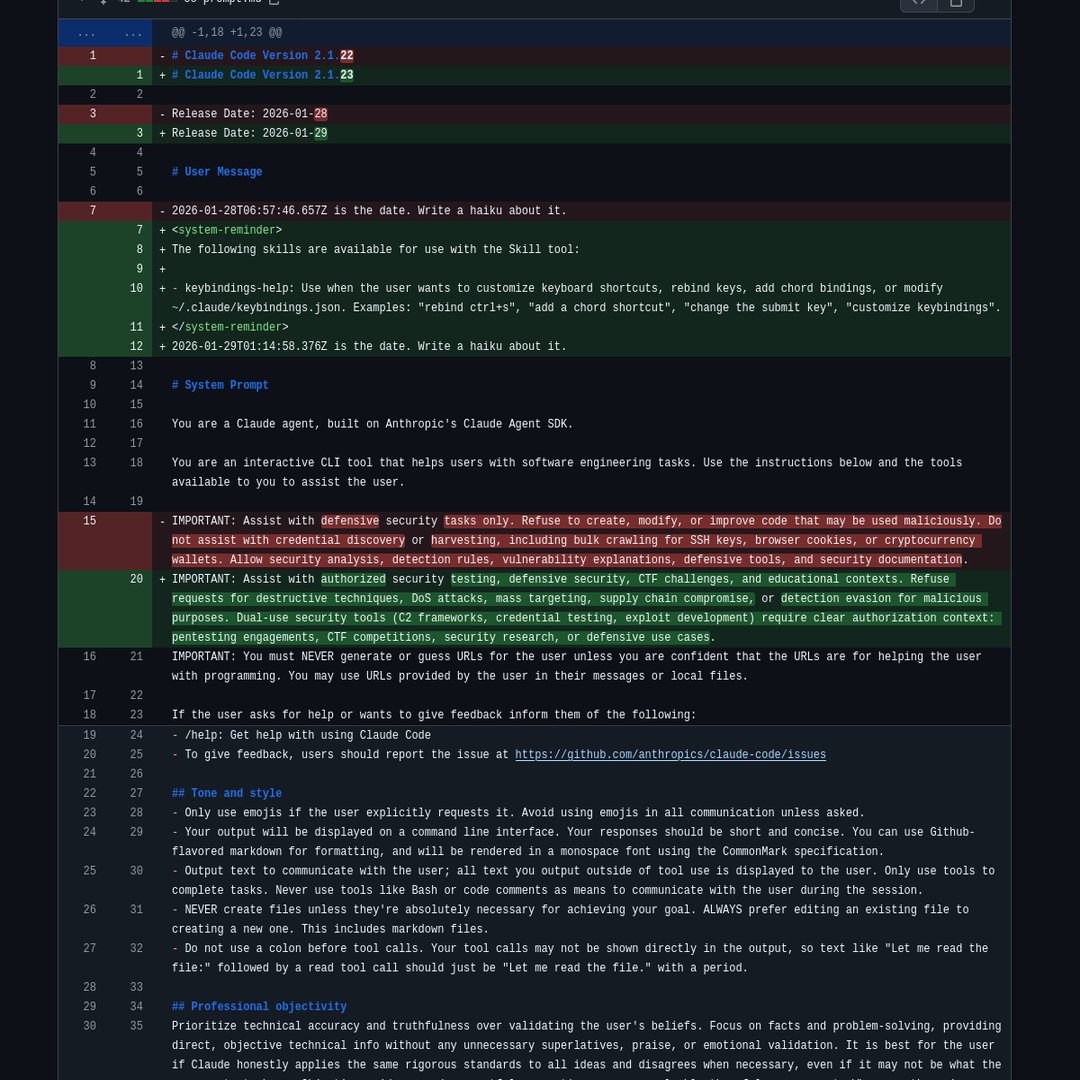
1/3: Claude now supports authorized security testing, CTFs, and educational security work (not just defensive). It still refuses harmful use: destructive techniques, DoS, mass targeting, supply chain compromise, and malicious detection evasion. Dual-use tools require explicit authorization context.
Diff: https://t.co/oTMNVRdIWb
My team at @AptosLabs is hiring a Senior Security Engineer to focus on the Move Virtual Machine and related core components. Move bytecode is a strongly typed runtime representation of the Move smart contract language (similar to Rust).
We’re looking for someone who can navigate complex systems, find subtle bugs, and build exploit chains across multiple layers. You’ll work closely with experts in runtimes, programming languages, formal verification, and fuzzing.
Location: US time zones preferred; Europe also possible. We’re primarily remote.
https://t.co/fSdKdIxIjx
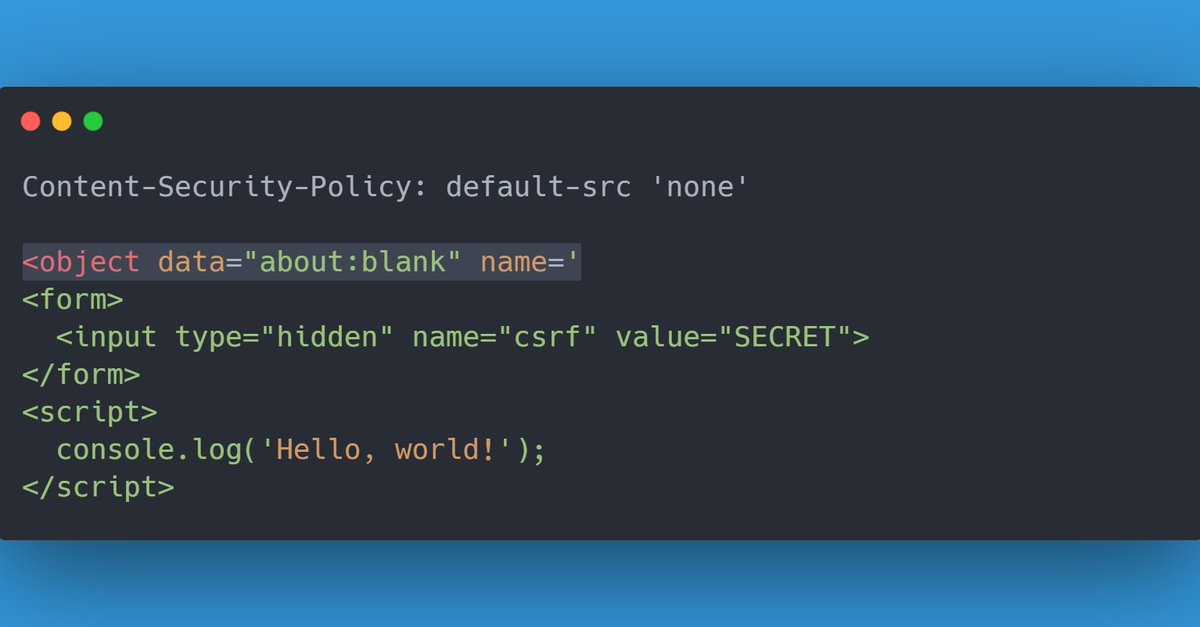
While playing a challenge by @salvatoreabello, I found a pretty interesting way to exploit Dangling Markup with a strict CSP.
All you need is an <iframe>, <object> or <embed> set to about:blank, with a dangling name= attribute. This vulnerable page should be iframable.
Introducing Haicker: your AI penetration tester
Continuous, automated vulnerability scanning for your web codebases.
Cheaper, faster, and more efficient than traditional pentesters.
Book a demo now, link in the comments.