I just created a repository of awesome resources for CTF competitions. It contains tools, platforms and other useful information for every CTF player.
https://t.co/nUav9875lV
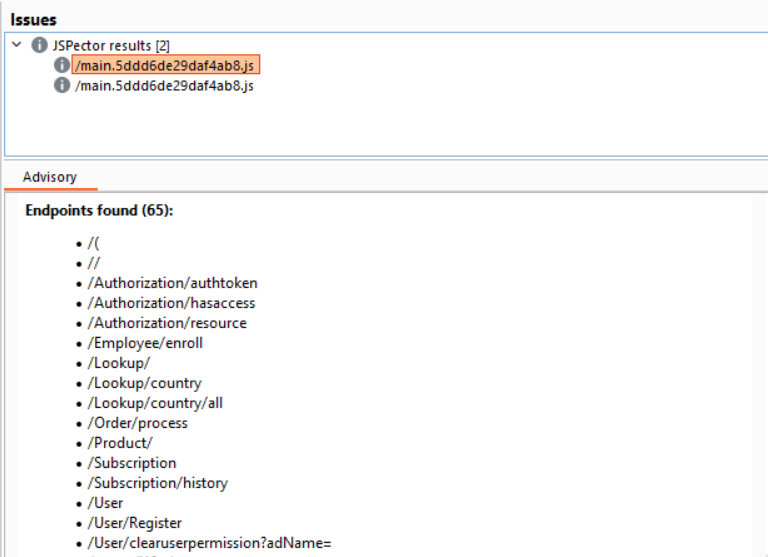
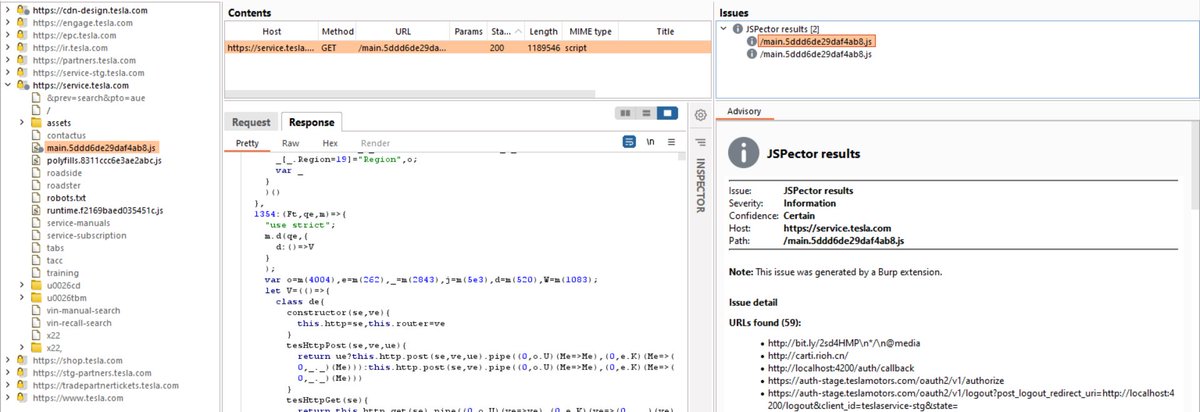
👋 I just released "JSpector" : a simple Burp Suite extension to passively crawl JS files and display the results (URLs & endpoints) in the "Issues" tab of each target.
I needed something simple to do this, and now that it's done, I'm sharing i!🤗
➡ You can download it here: https://t.co/K8Bn6Btb2e
#BugBounty
Hi Guys, Again I'm here to review another of my finding on the Sony program, This write-up is about how to automate process helps you find High or even critical vulnerability easier.
https://t.co/WpcDggNr01
#infosec#BugBounty#bugbountytips#bugbountytip
One common use-case to leak this kind of information is to exploit "Web Cache Deception" across the server, I've managed to find it several times already in Live Hacking Events, and It's also well documented across various blogs, such as:
https://t.co/vygv6ELKdH
OSINT TIP #145🧐
I came across this insane reverse face check website! Tested few images, showed unexpectedly amazing results.
It discovers their social media profiles, appearances in blogs, video, and news websites.
Maintain OPSEC!
https://t.co/ncvW3LQRcc
#OSINT#SOCMINT
Found another SQLi on @Bugcrowd 's private program
#ItTakesACrowd#BugBounty#bugbountytips#bugbountytip
Tip: Use this payload 0'XOR(if(now()=sysdate(),sleep(15),0))XOR'Z
In the value of every parameter and check if response delays according to the provided time in payload
A Simple Tip for #bugbounty, But a Money Maker 🧐💸🫰
Before you finish your day of hunting:
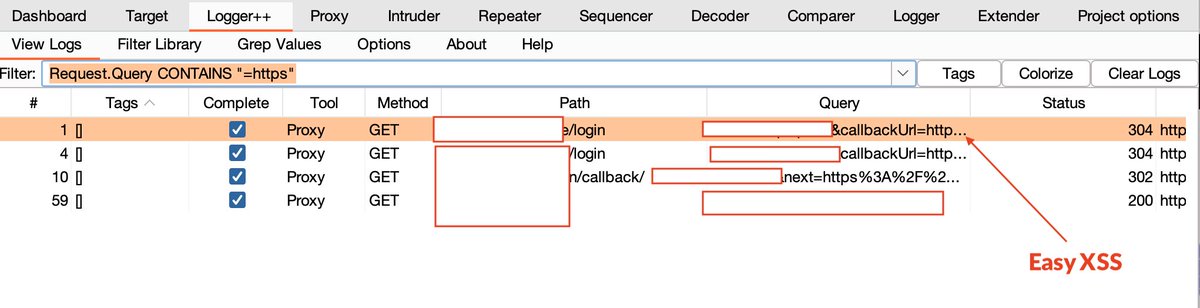
search in all requests and check if the value is equal to `=https`.
-----------------------------------------
Request.Query CONTAINS "=https"
-----------------------------------------
By doing this, you can modify the URL after the parameter to find potential SSRF, XSS, Open Redirects, etc.
#BugBounty #bugbountytips
Burp Suite > Proxy > Options > TLS Pass Through.
Add these:
.*\.google\.com
.*\.gstatic\.com
.*\.mozilla\.com
.*\.googleapis\.com
.*\.pki\.goog
No more noise in your logs!
credit:@sw33tLie#bugbountytips
" This is how i got my first bounty "
1. Tools :
- Naabu, Httpx, Katana , Nuclei from @pdiscoveryio
- Waymore , xnLinkfinder from @xnl_h4ck3r
2. How to exploit :
- https://t.co/TcRpQVy55t
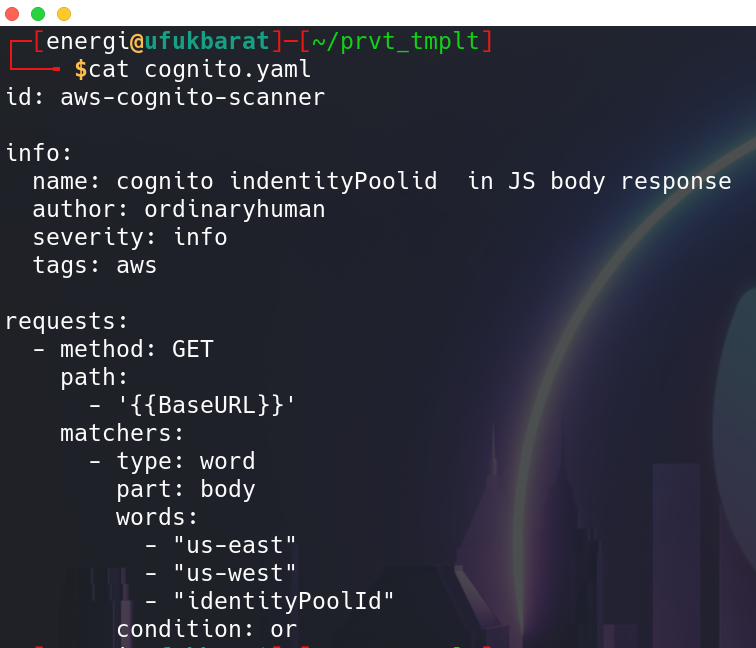
Nahamcon 2022 AWS Cognito
ScanAndroidXML
This tool analyzes #Android app to find vulnerabilities in
AndroidManifest.xml
network_security_config.xml
Firebase URLs from strings.xml.
https://t.co/Xw0imCoiUF
#cybersecurity#infosec https://t.co/vsyfXwvJ4s