Security news is endless. Your morning isn't.
Today we're launching The Transilience Brief, a daily newsletter: 3 threats, 3 breaches, 3 product flaws. Each in 3 parts, 2 lines each.
Five minutes and you're current.
Subscribe for free: https://t.co/HBpR7FHLLM
Apple has patched CVE-2026-65400, a CVSS 9.8 authentication bypass in macOS Screen Sharing.
The vulnerability is actively exploited and can allow unauthenticated remote access with root-level privileges when Screen Sharing is enabled.
Patch to:
• Sonoma 14.8.9
• Sequoia 15.7.9
• Tahoe 26.6.1
Also restrict or disable TCP/5900 where Screen Sharing is not needed.
Full Advisory: https://t.co/1OOiIviMQT
TheHatman is allegedly selling employee-directory data from 9+ enterprises, covering more than 3.6M records.
The data reportedly includes emails, phone numbers, reporting lines, group memberships, service accounts and privileged account names.
Access was reportedly obtained through compromised Azure/Entra ID credentials.
For defenders, the main concern now is follow-on phishing, BEC and account targeting using real internal company data.
Full Advisory: https://t.co/1OOiIviMQT
IBM i ACS users: check your exposure.
CVE-2026-17083 is a CVSS 8.8 RCE affecting IBM i Access Client Solutions 1.1.5.0–1.1.9.12.
• Network exploitable
• Low privileges required
• No user interaction
• Exposure depends on the IBM i Navigator listener configuration
Prioritize affected deployments.
Full Advisory: https://t.co/DtOtAeNLsN
#BHUSA Briefing "Secure Boot, Insecure Reality: Peeling Back Layers of False Security" is a deep dive into the systemic weaknesses which undermine the security of your boot environment. Register now>> https://t.co/c3H1v7rkil
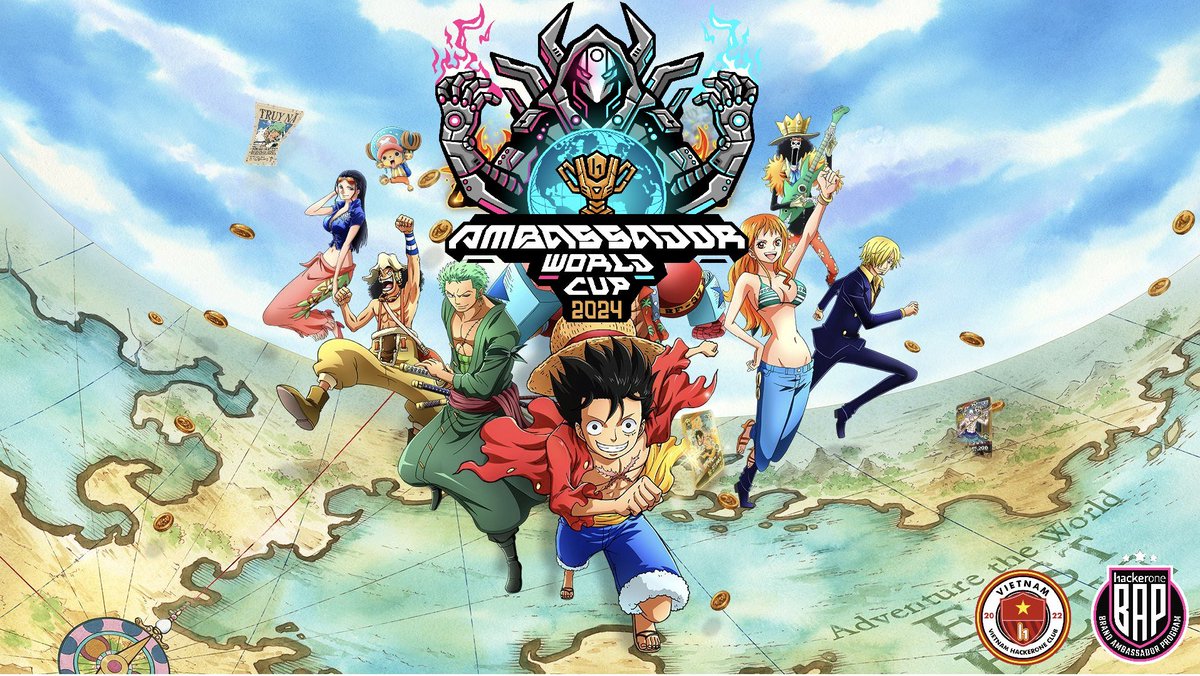
Calling bug bounty hunters 🥷 in Hanoi and Ho Chi Minh areas to participate in HackerOne's biggest Ambassador Worldcup 2024 event of the year 🔥
If you want to try your hand at difficult targets and collaborate in a strong, experienced community. Please join us 🇻🇳 🤝💰💪
@LamScun
Chandrayaan-3 Mission:
'India🇮🇳,
I reached my destination
and you too!'
: Chandrayaan-3
Chandrayaan-3 has successfully
soft-landed on the moon 🌖!.
Congratulations, India🇮🇳!
#Chandrayaan_3#Ch3
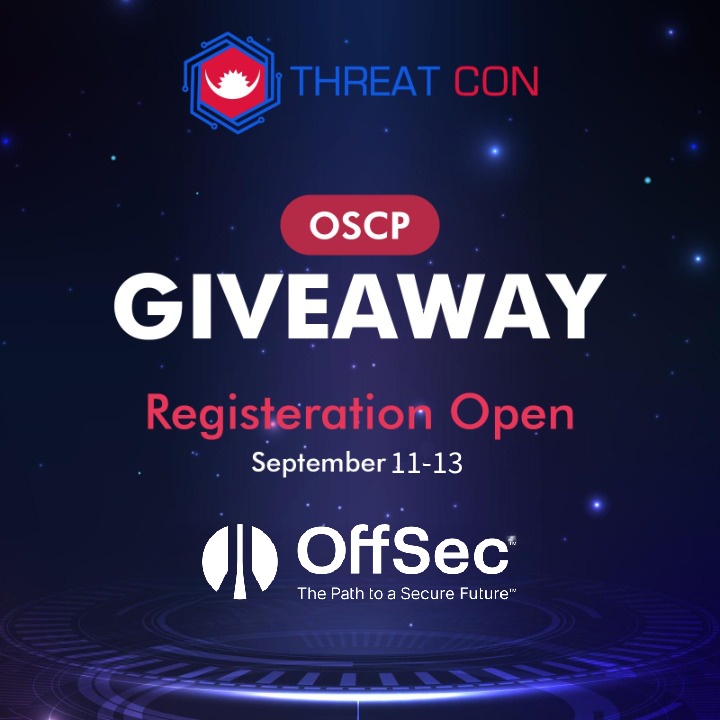
We're giving away an OSCP voucher to our community.🎉
To participate :
1. Follow us on Twitter.
2. Retweet this post.
3. Like this tweet.
It's that simple! By completing these steps, you'll be eligible to win.
Also, register now at https://t.co/iXhLYJRA1j.
#offsec#giveaway
Time for another giveaway!
We are going to send a t-shirt and a few goodies to one person who follows @PentesterLab and retweets this tweet!!
And we are going to give a 12-month voucher to someone who follows @PentesterLab and likes this tweet!!