🕵️ Investigated PrintNightmare (CVE-2021-34527) on @LetsDefendIO
correlating PCAP and endpoint evidence to reconstruct the attack chain — from SMB and malicious DLL delivery to persistence and Meterpreter post-exploitation.
#CyberSecurity#SOC#DFIR
🔗 https://t.co/tTzHOZsczD
Completed another @LetsDefendIO lab — Adobe ColdFusion RCE 🔍
Decoded the payloads, traced the web shell and PowerShell activity, and mapped out the full attack chain.
📷 Full investigation & IOCs: [https://t.co/tTzHOZsczD]
#CyberSecurity#SOC#LetsDefend#BlueTeam
Another one from @LetsDefendIO 🔍
Took apart Phantom Loader in Ghidra — C2, anti-debugging, sandbox checks, process hunting & fingerprinting.
Found some interesting stuff along the way.
🔗 Full write-up: [https://t.co/vjgW97vUwr]
#LetsDefend#MalwareAnalysis#Ghidra
Another malware analysis done.
This time: Odyssey Stealer — obfuscated AppleScript,
fake password prompt, LaunchDaemon persistence and a Base64 second stage.
The script was ugly. The analysis was worse. 😭
GitHub ↓
https://t.co/tTzHOZsczD
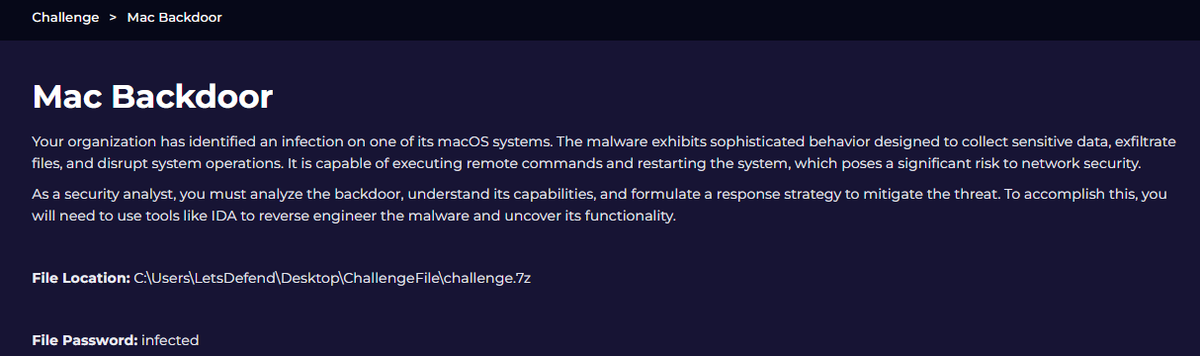
Took apart a macOS backdoor in Ghidra.
Found its C2, traced POST traffic, followed Base64 → XOR, and mapped command & payload execution.
Turns out param_1 wasn't the real enemy. 😶🌫️
@LetsDefendIO#MalwareAnalysis#ReverseEngineering
https://t.co/tTzHOZsczD
@Bolutalksgospel Tbh i never used any yt links for my journey i just gathered info about platforms which provide content for learning that's what i have done, doing
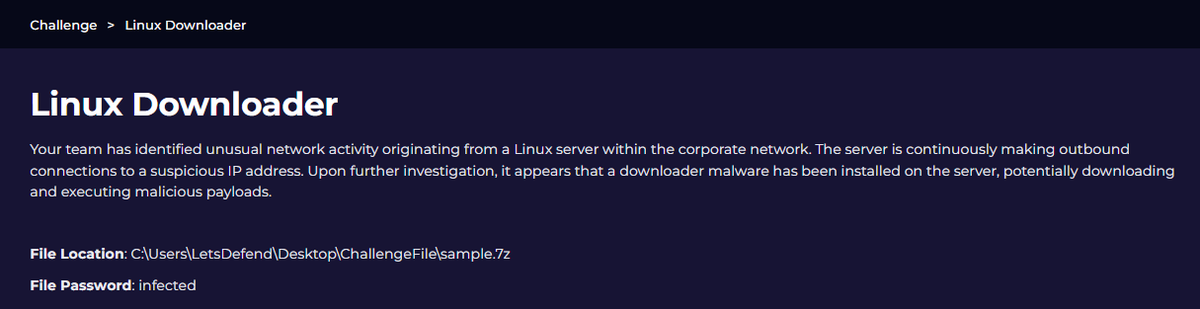
A 9 KB ELF with a simple job: connect, download, XOR, execute.
Reverse-engineered a Linux downloader in Let’sDefend using DIE + Ghidra. Found the C2 IP, syscall, XOR key, execution flow, and a suspicious [kworker/0:2] disguise.
Tiny binary. Big problem.
https://t.co/tTzHOZsczD
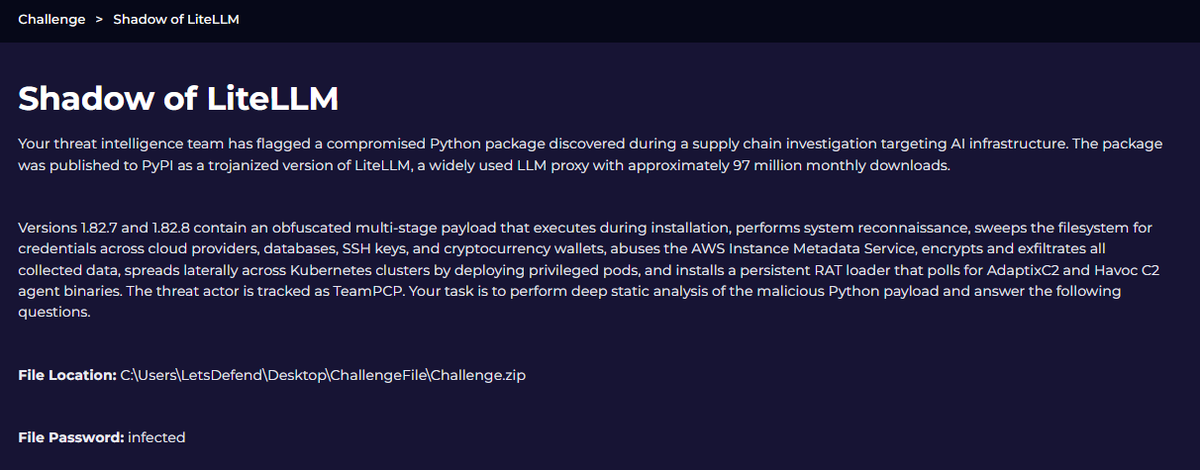
One Python package. Multiple stages.
Credentials → Cloud → Kubernetes → Persistence → C2.
Just finished my static analysis of Shadow of LiteLLM, decoding its hidden Python payloads with CyberChef.
📄 Write-up & IOCs: [https://t.co/rw3NyTvBYZ]
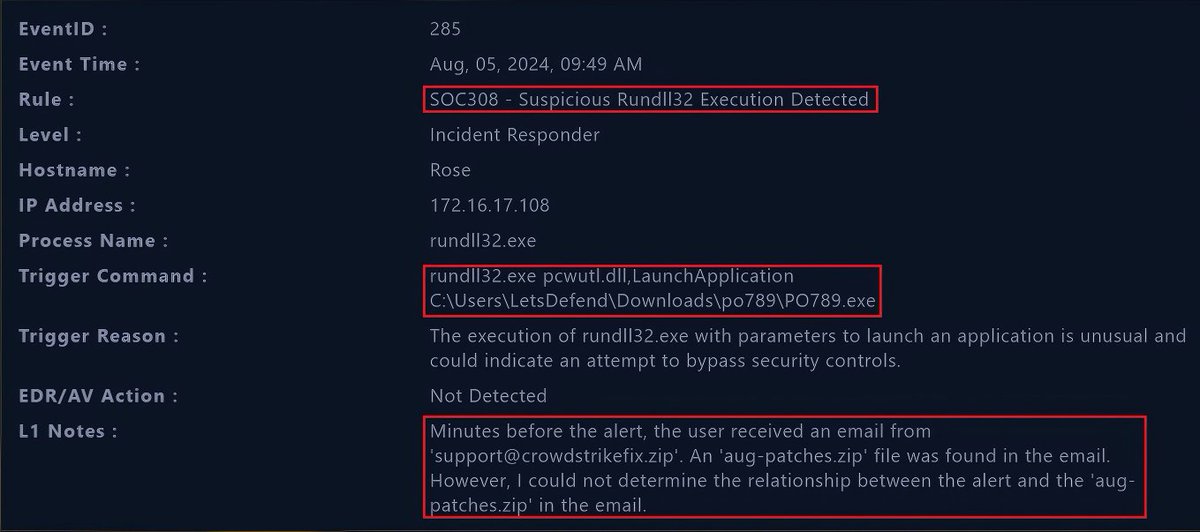
Investigated a suspicious rundll32.exe execution and traced it from phishing → BITSAdmin payload delivery → malware execution → Defender evasion → scheduled-task persistence.
#CyberSecurity#SOC#DFIR#ThreatHunting
Full investigation & IOCs ↓
[https://t.co/tTzHOZrEK5]
The suspicious file was the clue. The timeline was the proof.
SOC312 investigation: traced an RDP brute-force attack from initial access to a weaponized Normal.dotm template and VBA-based C2.
https://t.co/rw3NyTvBYZ
#SOC#CyberSecurity#DFIR
I want to connect with gys who are interested in SOC - Cybersecurity
Drop hii
let's connect & grow together
Especially from India
#cybersecurity#india#SOC
A malware sample isn’t just a file to identify — it’s a story to investigate. 🦠🔍
Completed the Malware Analysis Skill Path on @LetsDefendIO .
One path completed. The analysis continues.
#CyberSecurity#MalwareAnalysis#LetsDefend
Kindly let me know what should i do next ?
@WilliamInCyber It would be very good if u provide some insights on platforms where we can take our first step towards cybersecurity in terms of learning