As promised... this is Loki Command & Control! 🧙♂️🔮🪄
Thanks to @d_tranman for his work done on the project and everyone else on the team for making this release happen!
https://t.co/fR44ukK1Y2
Had a lot of fun digging into COM stuff with @bohops recently! We ended up finding a way to laterally move without dropping a file.
https://t.co/F6NahVpuHP
Big brother is watching you 👁️
A new #HTB Seasons Machine is coming up! DarkCorp created by 0xEr3bus will go live on 8 February 2025 at 19:00 UTC. MagicGardens will be retired!
✓ Insane
✓ Windows
→ Join the competition & start #hacking: https://t.co/4h7fj5XlsV
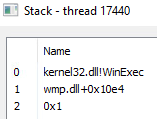
Need a sanity check on module stomping. I've always thought that it backs the first return address, but the rest of the call stack isn't guaranteed due to our payload making `calls` from the stomped DLL from points of the code which may or may not have a suitable stack size (1/?)
I have created a project called “RdpStrike.” The goal is to extract clear text creds from mstsc. The aim is to dive into the Positional Independent Code, a blog post by @C5pider and the original implementation by @0x09AL.
https://t.co/YnBezzHy6n
#cybersecurity#redteam#infosec
I'm happy to announce that I've (finally) started a blog: https://t.co/SknC0pegYe. Check out the first posts about doing ROP on 2.34+ without "pop rdi", and more will be coming soon™ :)
Just crafted a beacon object file for the 8th variant of the powerful process injection technique by @_0xDeku. An exciting journey into the Windows Thread Pool! https://t.co/7OJmrT1prF
#cybersecurity#redteam#infosec#cobaltstrike