Dumping LSASS is old school. If an admin is connected on a server you are local admin on, just create a scheduled task asking for a certificate on his behalf, get the cert, get its privs. All automatized in the schtask_as module for NetExec 🥳🥳🥳
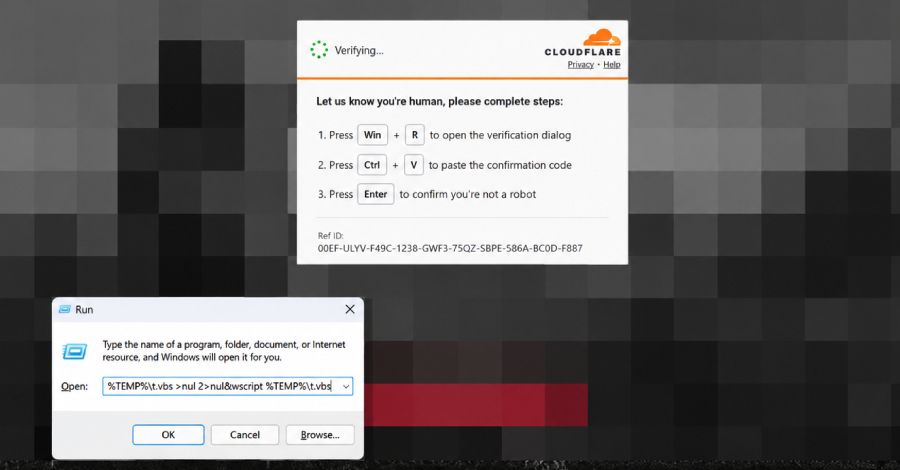
I see a lot of activiy going around browser cache smuggling which I presented back in 2023 there https://t.co/kI5P9Dqw32. Remember, the detection part is trivial: monitor any process that is not a browser, that is reading cache files. Also, disable Win+R shortcut! :)
🚨 ClickFix has a new trick... the malicious payload is already sitting in your browser cache before you paste the command.
Compromised sites preload scripts disguised as PNGs, letting pasted commands bypass Windows Run's ~260-character limit and launch a multi-stage malware chain.
Read: https://t.co/T28KHjsB5T
@dotimus_@MsftSecIntel Mostly watching for processes that are not browsers reading the cache folder. Originally I described that technique using a powershell oneliner but this could be a proper binary, a batch script or anything else. So yeah, matching processes reading the cache folder is the best
@MsftSecIntel More information about that technique here https://t.co/kI5P9DpYdu, detection is pretty simple! Monitore for processes that are not browsers, accessing the Cache folder of any browser :)!
3 months of work later, MS-NEGOEX is merged into Impacket 🚀
First big step toward bringing Impacket on Entra ID-joined & hybrid machines.
Next stop is PKU2U, after #2260 gets merged and soon after you will have SMB, LDAP & MSSQL on Azure with the tools you already know 👀
Be sure to check it out, research or/and build on it! Cant wait to see the sort of Azure offsec opportunities that may come out of this : )
https://t.co/pFmjQT8H2b
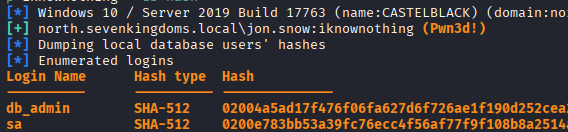
Yesterday we merged two new functionnalities on NXC for MSSQL. The ability to dump local database users' hashes. The new function lists both the login name, the algorithme used to hash the password and the hash allowing cracking them via hashcat/john:
This is part of a much bigger project that I started a year ago in order to provide better offensive capabilities to NXC and there is much more to come! 🥳👀
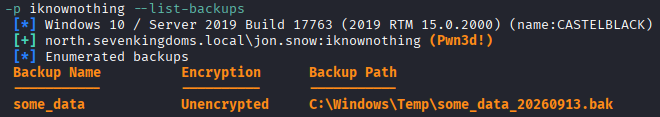
As well as a function that allows listing databases' backups as well as their backup path and whether the backup is encrypted or not (which may help finding password, sensitive data and so on).
Are you (like me) constantly running into your own Responder? The days are finally over!🚀
@Defte_ and I finally finished up a PR by bdrogja that let's you define exclusions such as "yourself". You can also exclude entire ranges or IPv6 addresses (if anyone uses those lol).
Be aware that your photos can be accessed without unlocking your phone when you receive a WhatsApp video call on Android.
This is in plain sight. It's not hidden, not a secret feature. Not a hack.
This has already been reported to Meta and Google.
#Privacy#Security#Android17
Cet episode des "rires du Medef" est un tournant.
Il vient adouber JLM en tant que seul défenseur des travailleurs/classe populaire
Il vient le déclarer comme seul opposant au système eco/politique actuel
Et il vient de souder toute une classe sociale derrière lui
Game changer!
I've published UniBLEed, a fully wormable proximity Bluetooth RCE affecting Unitree's G1 humanoids. Blog spans cloud, mobile, firmware, Bluetooth & hardware. Two multi-bug RCE chains. 3 months into ~80 minutes, $6,700 in bounties. Go jailbreak your G1s!!
https://t.co/GYopBgDtTO
He copied a value out of the Windows Event Log.
Pasted it into his special browser.
And he was signed into Microsoft Entra as the user who had just authenticated.
No password. No phishing link. No stolen private key.
@MGrafnetter's Black Hat USA 2026 research...
@mrzshyey2@seblatombe Mon point est juste de dire que c'est une tâche complexe et que tous les services de l'état où je suis passé, bah c'était calamiteux. Y'a juste pas assez de moyen pour recruter les profils et lancer les bons projets
@mrzshyey2@seblatombe Ouais je confirme, tu pèses pas tes mots et te rend pas compte de la charge de travail que c'est de gérer un SI qui plus est quand chaque ministère a le sien. Quant aux admins expérimentés, ça paie pas assez le public :)
This past week I’ve been asked several times by people of different ages “how do you research and publish so much?”. It’s awesome to be asked. I love sharing tips and I try to give my techniques for maintaining a research pipeline. But I also want to be honest about my reality. At times, it’s an unhealthy coping technique. I’m getting much better at it, but in the past I’ve not been so good. I’ve skirted psych wards on multiple occasions, been given a “multiple weeks off work with several therapy sessions” order, been on various psych meds, torpedoed family events and holidays etc... Social media highlights the wins, but I try and be honest about the lows too where I can.
This industry is awesome, for many of us it gives us the chance to pursue our hobbies and passions. But it does encourage unhealthy routines. There is a reason that alcohol, drugs and mental health issues are embedded in infosec culture. And while sharing a new blog post or cool vuln can inspire people to want to be doing more, it shouldn’t come at the expense of a healthy mind.
An old boss once said “we want you doing this for a long time, not doing a lot in a short time”.. I still think about this now. Stay healthy h4xx0rz!