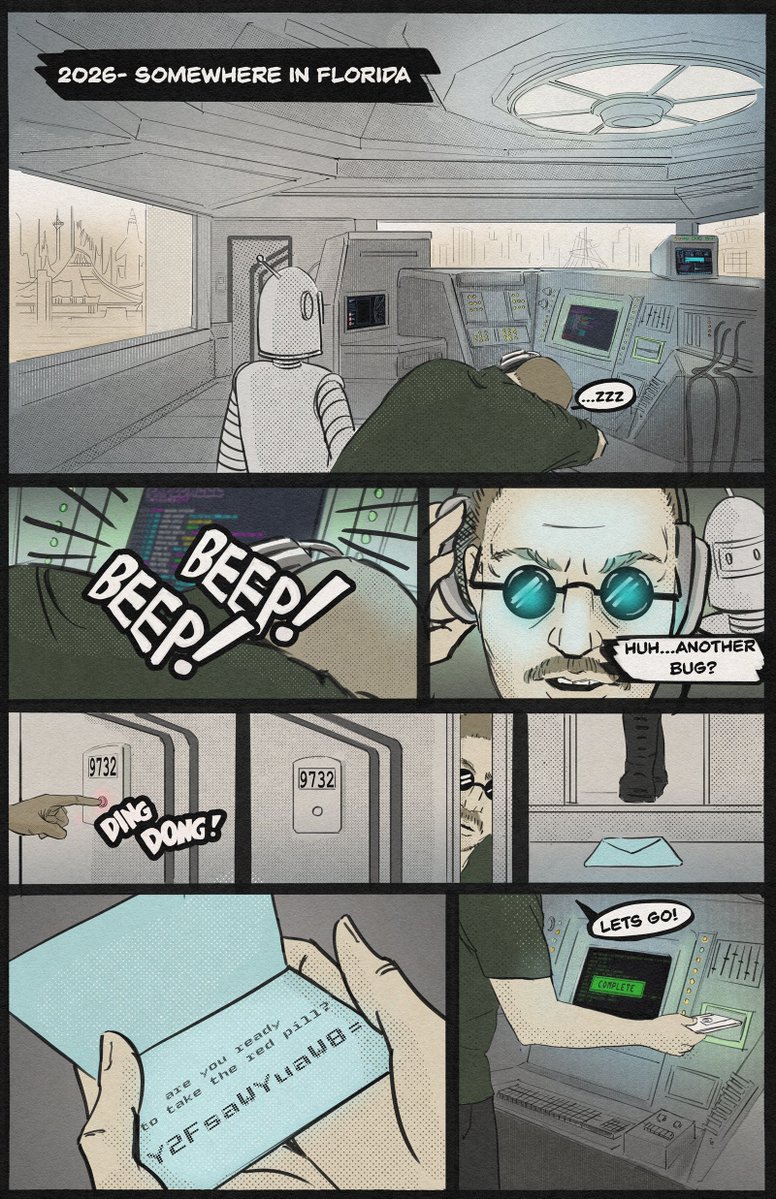
Team work makes the dream work <3
We wanted to do something a bit different than using LLM's to generate all the pieces from exploit, writeup and art. We decided on a human created comic to offset the LLM usage in our release, that tells the tale with some exaggerated scenarios inspired from a few movies.
If you liked the art (or want your own exploit story/comic..) check out her work at https://t.co/CyhBOcAqdF
The details of the long awaited KVM Escape are published. PwnEscape leads to VM escapes across multiple hypervisors due to a super cool Linux networking bug.
CVE-2026-99999 is a 9.3 CVSS critical rated KVM escape ⛓️
https://t.co/CXLvvjLxyF
We're releasing a small project today called Labyrinth
https://t.co/06VZHpZOqZ
It is a full offensive pipeline automation combining a few tools which takes place in your very own Ludus range, optimised for your development pleasures.
Hope it benefits you, PRs are always welcome.
Second part of my adventures with Eufy in @Adeptsof0xCC!
A story of wifi secrets, UART lockdowns and a damaged flash memory chip
https://t.co/ixO1MBh7ct
Thank you to @UnpromptedAU & @BSidesCbr for inviting me to speak. Being back down under was lovely! You can find the slides for my n-day automated pipeline talk here. I’m at OAIC this week if you want to chat about exploit dev in 2026 and beyond. https://t.co/LVpRd34i33
@viperbjk@0xSero Or actually, no-one would be needed for that job. The "AGI" would find all bugs itself with no human interaction needed, except sign off at the beginning and end. A non-technical job basically.
I'm not worried, if it happens, happens 😆
But I find it unlikely.
While I was gone I spent some time writing. Here is one that's been in my drafts for a while. It explains where we've been and where we might be going
https://t.co/LVyU8EEER4
@LiveOverflow not only because your own understanding of subject matter grows, but also to get a grip of your model's capabilities and pitfalls it encountered along the way. not to mention potential things it missed because a certain approach seemed more promising, etc.
Check out this fascinating story of two macOS Screen Sharing exploits we built over the weekend:
https://t.co/hotSQCVJds
Shoutout to @osxreverser for such a cool bug!