🎉 Proud to share my 2024 #HackerOne journey! 242 vulnerabilities reported, including 8 critical findings! Special thanks to @Hacker0x01 for providing the platform to make the internet safer. Here's to more discoveries in 2025! 🚀 #InfoSec#BugBounty#CyberSecurity
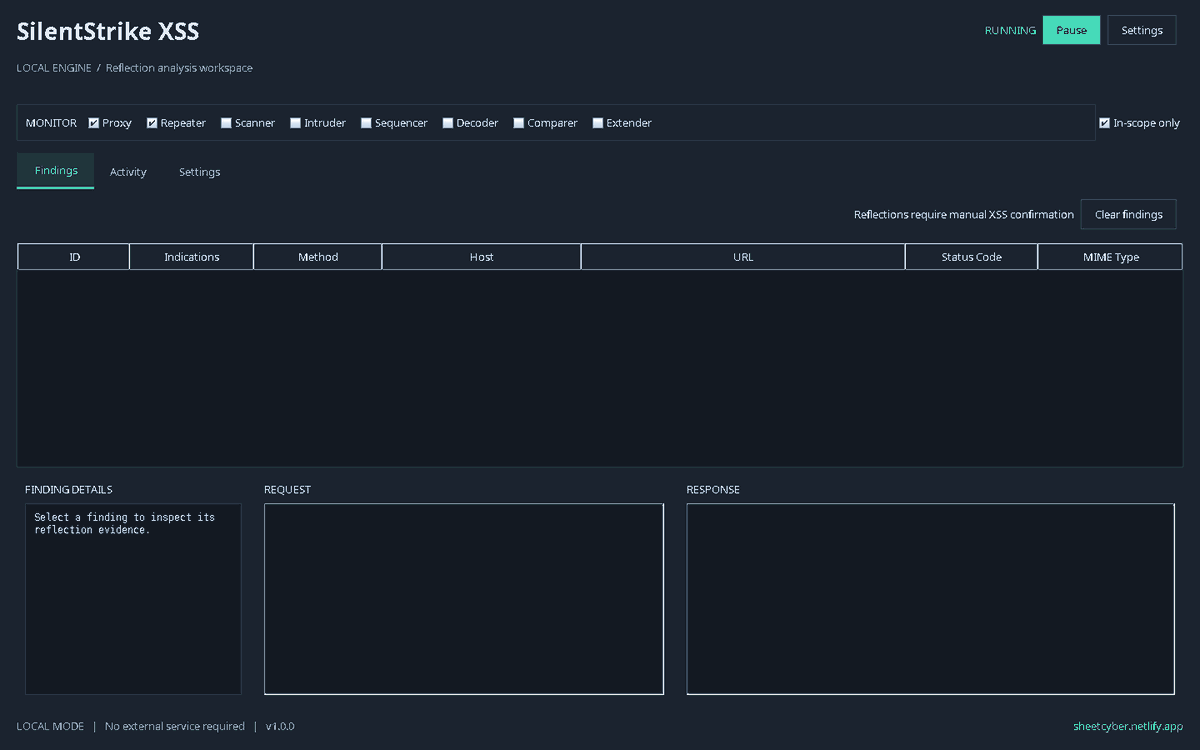
@V0iD_0daY Thanks! It currently uses literal marker/pattern matching, without decoding or cross-tool normalization, so re-encoded reflections can be missed. JSON probes test existing values; header probes cover User-Agent/Referer. New-parameter discovery is query-string only.
I’m pleased to share recent progress in my vulnerability research through HackerOne, involving two security findings across different Vulnerability Disclosure Programs (VDPs).
#hackerone#bugs#BugBounty
I’ve published Punycode Pro Tool for Burp Suite 🔧
• Explore Unicode homoglyphs
• Generate IDNA/Punycode results
• Copy characters with one click
• 421 entries across a–z
Code & setup:
https://t.co/2ROmAlz42B
#BurpSuite#AppSec
اتمني يكون فية psychologist يتكلم عن الصحة النفسية للمبرمجين بعد موجة layoffs العالمية و الاجهاد النفسي لكل اللي شغالين في الصناعة في الوقت الحالي عالميا
If we are not seeing mass exploitation of php2shell, it's not because the exploit is not easy. It's because threat actors are apparently absolute dumbasses, or don't make enough money to afford a Codex subscription.