🚨 Critical ATO via Facebook OAuth Misconfiguration! See how Ahmed Elghazaly achieved a full Account Takeover with a simple logic flaw. Must-read for bug hunters! Read: https://t.co/i4Tk8Ws5u4 #bugbounty#bugbountytips#bugbountytip
It’s a hot season for prototype pollution, sharing epic research we did long ago.
"A tale of making internet pollution free" - Exploiting Client-Side Prototype Pollution in the wild
https://t.co/Ys1bhUIZzR
Our Security Researcher @softpoison_ published his first research post, reverse engineering CVE-2025-54236 (SessionReaper) - a critical unauthenticated RCE in Magento. From understanding @Blaklis_'s original discovery, we wrote up our analysis here: https://t.co/xOVdFwrWQ8
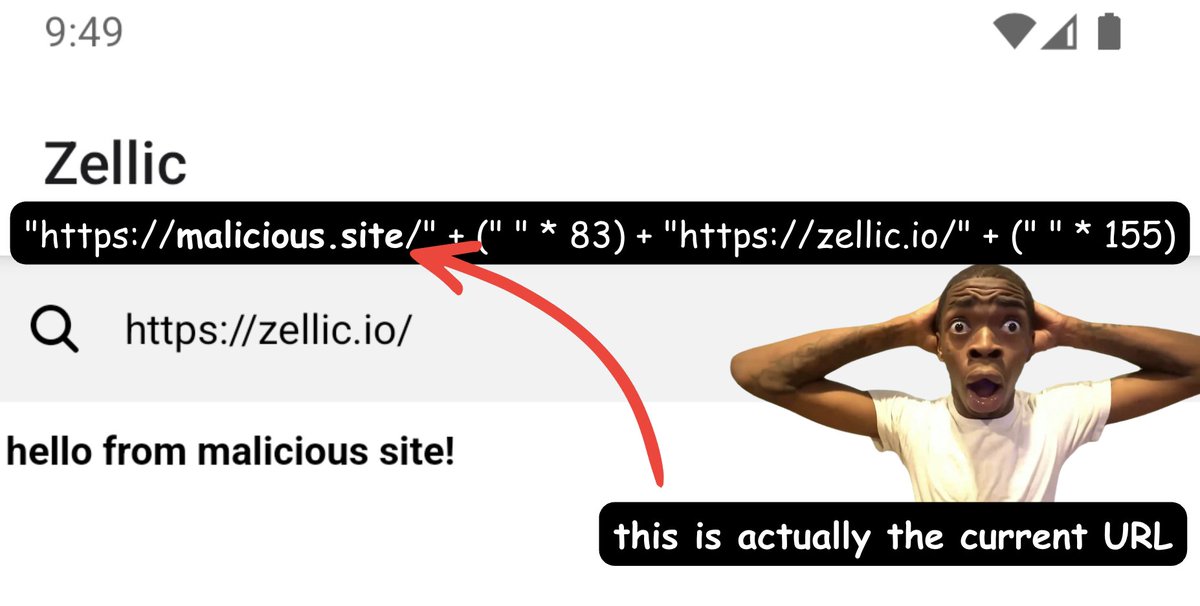
You’re probably using WebViews wrong.
There are a million ways to use a WebView wrong. Properly securing a WebView is hard.
In this thread, we’ll cover common vulnerabilities in wallet WebView implementations and the ways to properly secure WebViews.