Woohoo! @AMD openSIL Achieves Its Production Goal With 6th Gen @AMDServer EPYC "Venice"
After no openSIL messaging this week for SP7 shipping, I was able to now confirm that all is well with openSIL being used on all Venice platforms.
https://t.co/pEfzLGbduz
BSMConf 2026 talk now on YouTube!
"Firmware in Systems Research at KIT" by Yussuf Khalil.
Explore CXL-based hybrid SSDs with byte access, firmware/OS co-design for system suspend, and the role of open-source firmware in boot chain transparency.
Watch: https://t.co/gzujPsjCIH
BSMConf 2026 talk now on YouTube!
"Extending the Chain of Trust into the KV Cache" by Arthur Rasmusson.
Discover how hardware-rooted confidential computing, GPU TEEs, and remote attestation can help secure shared LLM KV caches in multi-tenant AI.
Watch: https://t.co/QbxCIKGpj9
BSMConf 2026 talk now on YouTube!
"Where the Chain of Trust Goes Dark" by Kamil Wcisło explores how WANTED extends the chain of trust beyond boot to signed Wasm workloads on Raspberry Pi RP2350 (ARM & RISC-V).
Watch: https://t.co/1mRMiw0TeE
BSMConf 2026 talk now on YouTube!
Will expiring UEFI Secure Boot certificates affect booting? Daniel Kiper explains the 2026 changes, their impact, and the future of PQC in Secure Boot.
Watch: https://t.co/HAwP72vfN9
BSMConf 2026 talk now on YouTube!
Flashkeeper: Manage and Protect your SPI Flash by Dodoid.
Explore SPI flash adapters, bus breakout, write protection, and FPGA-based authenticated flashing and runtime verification.
Watch: https://t.co/IRDYZ2y7OE
BSMConf 2026 talk now on YouTube!
Verifiable Computing: Connecting trust from bootstrap to runtime by Lance R. Vick.
Explore reproducible firmware, multi-hardware attestation, and how to verify code running on remote machines.
Watch: https://t.co/qw1lQpF5Fa
The third Dasharo FSP integration status community call is happening tomorrow, 13 October 2026, at 8:00 PM CEST.
We will share the latest progress on FSP integration in Dasharo, covering implementation status, platform enablement, challenges, validation work, and next steps.
BSMC 2026 talk now available!
NOVA: A Hardware-Anchored Microhypervisor with a Minimal TCB by Udo Steinberg
How does NOVA build trust from hardware up? The talk covers measured launch, TPM attestation, isolation, and formal verification in a minimal TCB.
https://t.co/wHmnWRWw4N
BSMConf 2026 talk now on YouTube!
TrustedServer: From a Verified Image to an Attested Machine by Francesco Castellana.
Root of trust, system measurements, rollback protection and remote attestation.
Watch: https://t.co/DqKytUDwZM
LPC 2026, Prague: System Boot and Security MC, Monday from 15:00, Small Theatre. My slot at 18:10: Arm DRTM beyond the reference model, on real hardware and in Linux. If you own the guarantees a platform has to make, find me on Monday or Tuesday. #LPC2026
This year, 3mdeb founder Piotr Król will also present our latest work on bringing Arm DRTM to real hardware and Linux, building on our Qualcomm and @TrenchBoot experience. Join us on Monday at LPC 2026.
Talk:
https://t.co/ZNGUY49n5y
Blog:
https://t.co/izNZ66cdc1
The System Boot and Security MC is returning to @linuxplumbers .
Since 2020, 3mdeb has been involved in organizing the microconference together with Daniel Kiper from Oracle, helping create a space for engineers working on critical areas of the Linux ecosystem, incl. firmware,
bootloaders, trusted computing, attestation, and platform security.
We are grateful to the LPC organizers for once again accepting the System Boot and Security Microconference and giving this community a place to meet, exchange ideas, and move challenging upstream work forward.
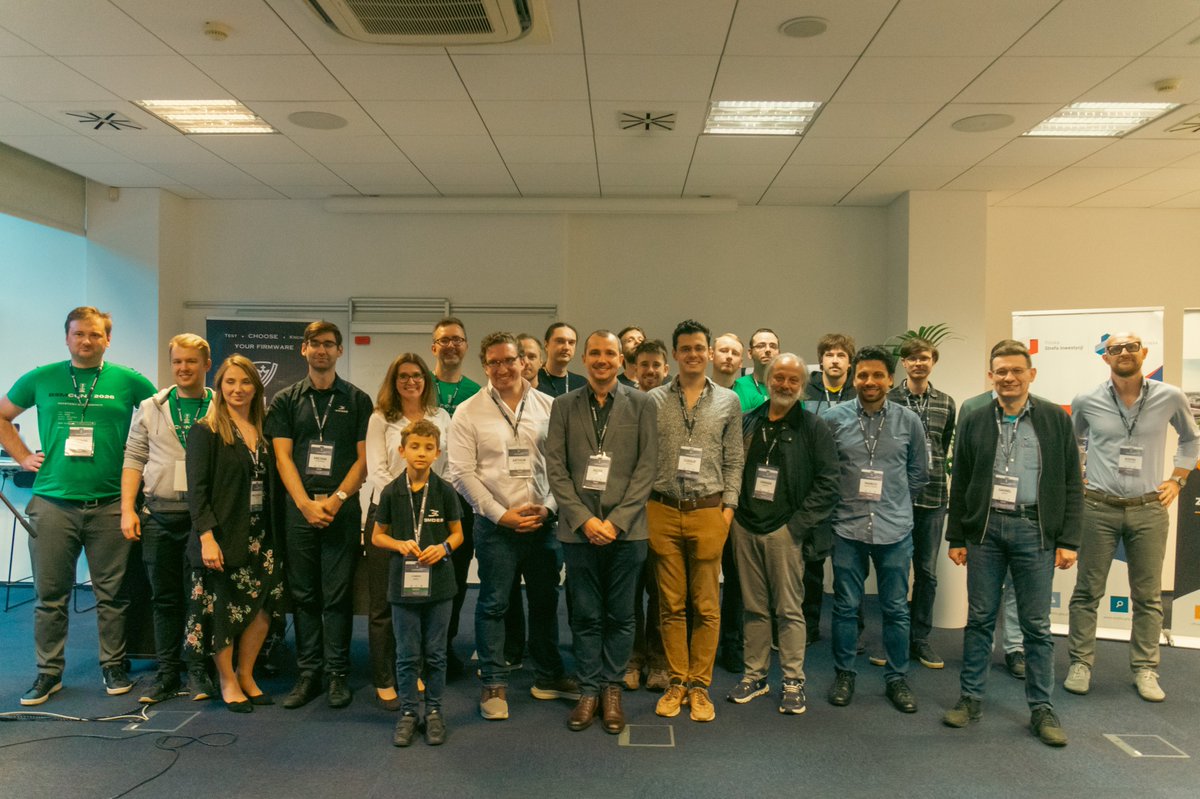
BSMConf 2026 is done. 21–25 September, GPN-T, Gdańsk.
Three days on the bench, two days of talks on the x86 boot chain. Thank you to every speaker, attendee, and the 3mdeb team who carried the week.
USB debugging without an expensive closed source analyzer. Our USB Sniffer, based on Alex Taradov's open-source Low cost USB Sniffer, captures LS, FS and HS traffic to PCAPNG for analysis in Wireshark.
Available now from 3mdeb:
https://t.co/wA3baBIZRB