Found a heap overflow vulnerability in Windows SMB that leads to RCE and reported it to MSRC in June.
The vulnerability has now been addressed with CVE-2026-62800 in the August Patch Tuesday updates.
https://t.co/MVDbXNccfw
CertiGhost (CVE-2026-54121) deserves much more attention than it is getting right now, from my point of view.
In a common/default AD CS setup, a low-privileged domain user can create a rogue machine account, trick the CA into issuing a certificate with the identity of a Domain Controller, authenticate as that DC via PKINIT, gain replication access and basically compromise the whole domain.
So if you run on-prem Active Directory with AD CS and your CA is still unpatched, an ordinary domain user may currently have a path to the highest privileges in your domain.
Patch it, obviously, or apply the temporary mitigation. But if you patched only recently, the harder and from my point of view more important question is: did someone already exploit it?
A patch closes the hole. It does not unfuck a domain that was already compromised.
I put a list of things I would check in the first reply.
Overview:
https://t.co/NHaJD5hlFi
Technical details:
https://t.co/ucGrc2SLbJ
PoC:
https://t.co/nvWARPtmso
Microsoft advisory:
https://t.co/kYoXWRKTyz
Temporary mitigation:
https://t.co/hVOHBYO5hD
If you want to hunt for signs of Certighost (CVE-2026-54121) by @h0j3n and @aniqfakhrul in your #XDR environment try this query.
1. Exclude DCs
2. Identify ADCS servers
3. Check for LDAP or SMB connectivity to any non DC from ADCS
BP for SMB possible!
https://t.co/BGOhTzsP40
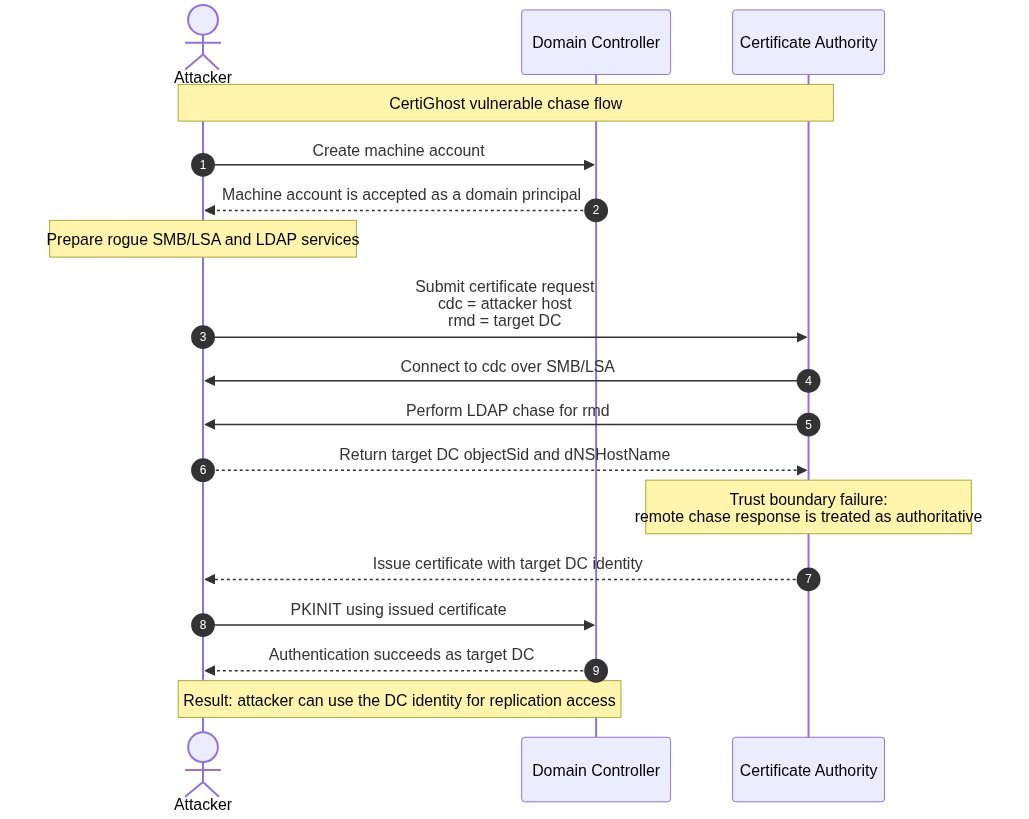
Yes, CVE-2026-54121 is bad with a public working exploit out now (CertiGhost)… although it’s still worth noting that proper network segmentation would mitigate this. Also, the attacker must have a way to run a fake LDAP server, which is not hard if you already have access to the victim machine. Here’s a flow chart to visualize how bad this is:
Attacker
(low-privileged user)
|
| 1. Creates a
| computer account
v
Starts fake LDAP server
|
| 2. Requests a
| certificate for
| Domain Controller
| DC01
v
Certificate Authority
|
| "I'll contact the
| LDAP server you
| told me about..."
v
Fake LDAP server
controlled by attacker
|
| "Yep, that's DC01"
v
❌!!! VULNERABILITY !!!❌
CA trusts the LDAP response
WITHOUT properly verifying
that it came from the real
Domain Controller.
|
v
CA issues a Domain Controller
certificate to the attacker
|
v
Attacker authenticates
AS the Domain Controller
|
v
Performs DCSync
|
v
Full Active Directory
compromise ✅
https://t.co/9e2bPwLlXv
Happy to share a technical analysis by @h0j3n on our recent CVE-2026-54121 a.k.a Certighost. glhf🔥
Technical analysis: https://t.co/jYrZDLPlJr
POC: https://t.co/yBeHg1vQHP
🚨 LATEST UPDATE: Perkeso’s SKBBK benefit is now voluntary.
You can choose to opt out. 👌
The decision was made after PM Anwar raised public feedback on the matter.
https://t.co/27E65JagP5
Today we're launching https://t.co/7C21vf5hmL
It gives any AI agent ready-to-use security context for thousands of open source projects, built from each project's commit history of security fixes and its disclosed CVEs.
Useful whether your agent is writing code or reviewing it for bugs. Free, no auth, over MCP and API.
Interesting read on using LLMs to find vulnerabilities. Core method:
1. Keep scaffolding minimal
2. Build a threat model first
3. Slice the codebase into small parts, prioritizing the most likely bug classes
4. Prompt injection
https://t.co/M32nNct2To
Mari kita ulangkaji rukun-rukun solat mengikut Mazhab Shafi’i. Kalau tinggal salah satu maka tak sah solat.
Rukun Qalb (Hati)
• Niat
Rukun Qauli (Baca dan didengari dengan telinga sendiri)
• Takbiratul Ihram
• Surah al-Fatihah
• Tasyahhud Akhir
• Selawat ke atas Nabi
• Salam Pertama
Rukun Fi’li (perbuatan)
• Berdiri dengan betul
• Ruku’
• I’tidal
• Sujud
• Duduk diantara 2 sujud
• Duduk Tasyahhud Akhir
Rukun Am
• Tertib
• Toma’ninah (berhenti seketika dengan tenang)
Maka tak baca Doa Iftitah masih sah solat.
Wallahua’lam.