@jarredsumner Fair. Engineers getting paid full-time to work on MIT code is a great deal for everyone using it. As long as the license stays MIT, that's what counts.
@dhh Agreed. The fastest way to make people hate a technology is to ship it as a button before it has a job. The Copilot key needed a use case before it needed a keycap.
Use your preferred coding agent directly in @AndroidStudio.
You can now choose from over 40 coding agents inside the IDE, giving your agents project context and access to Android Studio tools 🧵👇
@aileonardM Agreed. The new bottleneck is verification. If you can't quickly tell whether an agent's PR is right, the fastest agent just makes your review queue longer.
Rust devs, which crate do you add to almost every new project before writing any real logic?
serde, anyhow, tokio, clap, tracing, or something else?
Drop yours 👇
@aslambeg84 Postgres, but the real answer is whatever your team can debug at 3 AM. 10 million users will break your schema long before they break the database.
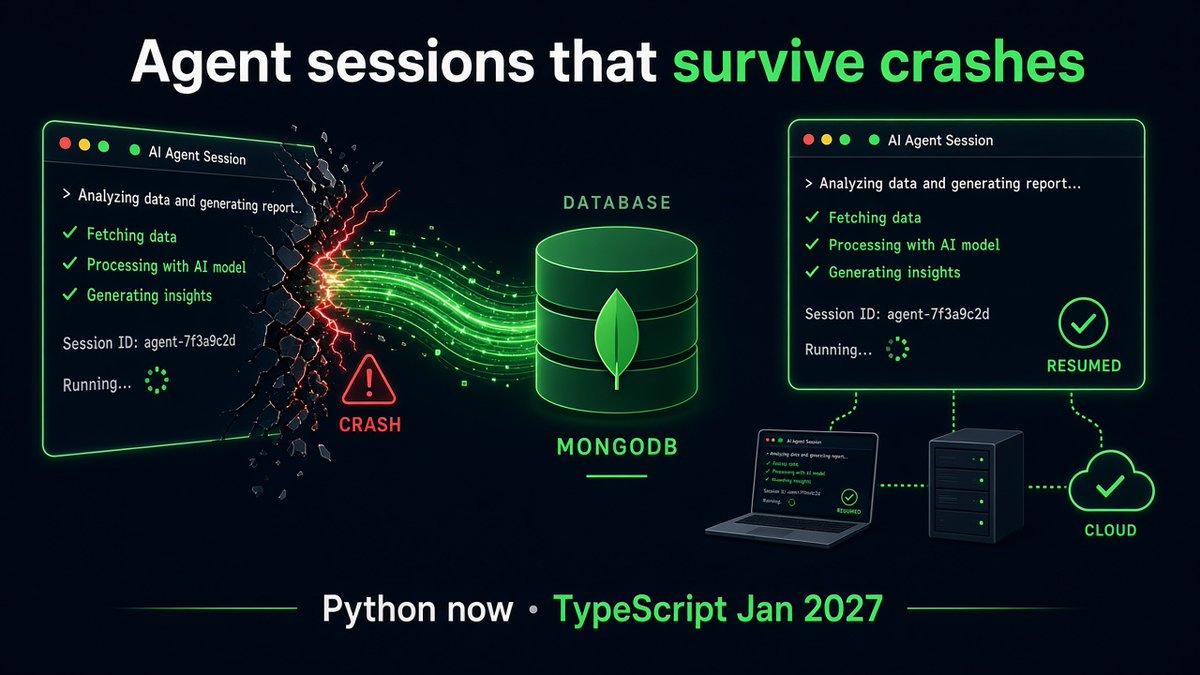
Your AI agent crashes mid-task. Now what?
MongoDB's Claude SDK Session Adapter saves agent sessions so they survive crashes and resume right where they left off, on any machine.
🐍 Python: available now
🟦 TypeScript: January 2027
‼️ Tailscale finally issued patches for SSH flaws that could turn one hacked device into root access on other servers.
The Tailworm research demonstrated rapid lateral movement across policy-permitted devices, without stolen passwords or user interaction.
⚠️ Headscale remains UNPATCHED.
Read - https://t.co/dY3SqdY30U
⚠️ EDK II CVE-2026-97631: a critical (CVSS v4 9.5) memory-corruption bug in PXE network boot in the UEFI firmware base most server vendors use.
It lets code run before Secure Boot. 🧵
https://t.co/7trw9HILAf
The advisory went out Oct 22 after AMI published the fix early in a public PR. It still says "Not patched currently".
Found by Alex Matrosov and Dan Holmes-Mitra.
⚠️ Tailscale: update to v1.104.4 (Oct 27).
After the "Tailworm" report, Tailscale patched privilege-escalation bugs (TS-2026-014 to -017): an authorized SSH user could exceed their local user's permissions. 🧵
https://t.co/1HLxH7uzRf