Call me paranoid, but be extra careful visiting ANY web site in the next few days, as some web admins are not always up-to-date with security patches.
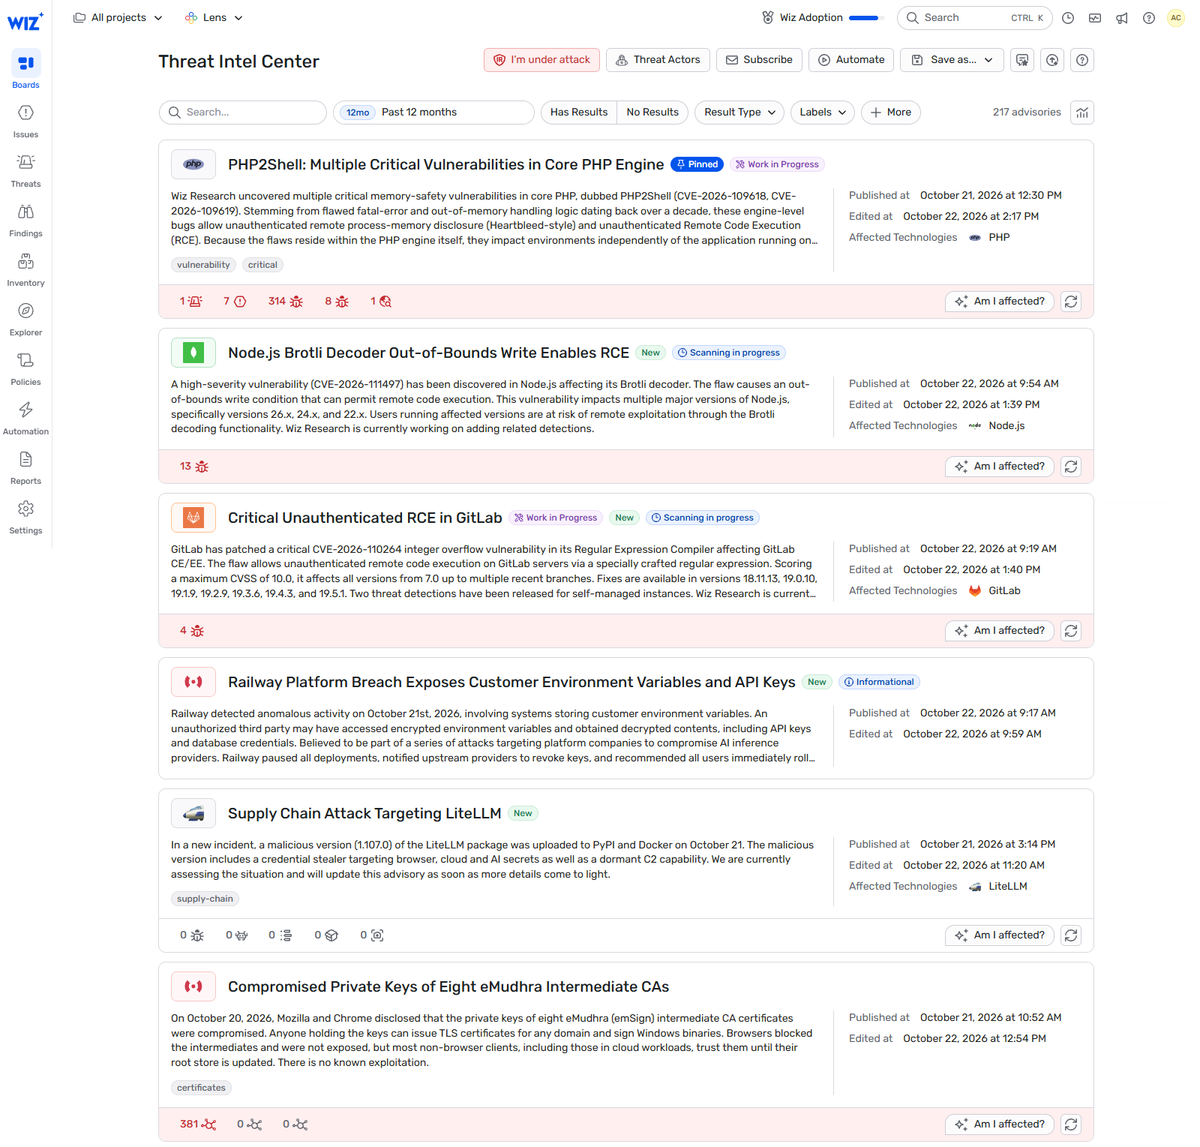
Two vulnerabilities (CVE-2026-109618 and CVE-2026-109619) reported for PHP, the web programming language, affecting servers running popular apps like WordPress and Magento, with patches released October 21, 2026 after details leaked early.
Exploitation was confirmed in the wild soon after disclosure, prompting quick WAF protections and patching by IT teams, as unauthenticated attacks could turn visited sites into vectors for credential theft or device exploits.
Stay SAFU!
Thrilled to share my latest research on AI-assisted cyberattacks and the ARTEX hacking framework!
What initially appeared to be AI-assisted attacks targeting South Korean banks turned out to be part of a much broader operation spanning multiple countries and industries.
My investigation revealed a financially motivated campaign leveraging ARTEX to pursue various monetization opportunities, including stealing customer data, reverse-engineering Android applications to identify vulnerabilities, and even attempting to acquire free NFT tokens.
AI is accelerating the speed and scale of cyberattacks, even when attackers rely on known vulnerabilities, enabling broader targeting and faster exploitation.
A closer look at the attacker's infrastructure, AI-assisted operations, and financial motives:
https://t.co/1HKtME3890
@k3r3n3 I'd love if someone could dumb this vulnerability down for a beginner. @grok Explain in two levels for a beginner and for a graduate student. Gives examples.
This is what I mean when I tell people everything got faster. Usually we talk about the gap between a CVE and a working exploit. Now with #php2shell the clock starts before the patch even exists. The fix lands today at 14pm UTC , stay tuned and get ready to patch your PHP!
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 https://t.co/W4kfzx5lxz
#NodeJS#Security
Understanding OS, kernel, and browser internals teaches you how things actually work under the hood. Exploit development is about identifying where assumptions break, how vulnerabilities arise, and how they can be exploited. The deeper your understanding, the better equipped you are to discover vulnerabilities, bypass mitigations, and develop reliable exploits. It also allows you to validate and work with AI VR findings, chain exploits, and save time not getting distracted by hallucinations and overstated severities.
What's the purpose of studying internals of an OS, or it's kernel say windows internals for example or doing research into browser internals ?. What benefit is there to it, for someone who wants to get into security research ?. @Steph3nSims
I'm off to Tokyo in the morning to teach SEC660: Advanced Penetration Testing and Exploit Writing. This course has existed for 15 years and it's amazing how different it is now to teach it in the AI era. It's fun to teach the low-level details first and then using AI to amplify.
Are some of these sites essentially watering holes for spyware ?. Take former soap2day for example, a popular pirate site where I understand some ppl can stream movies and tv shows.