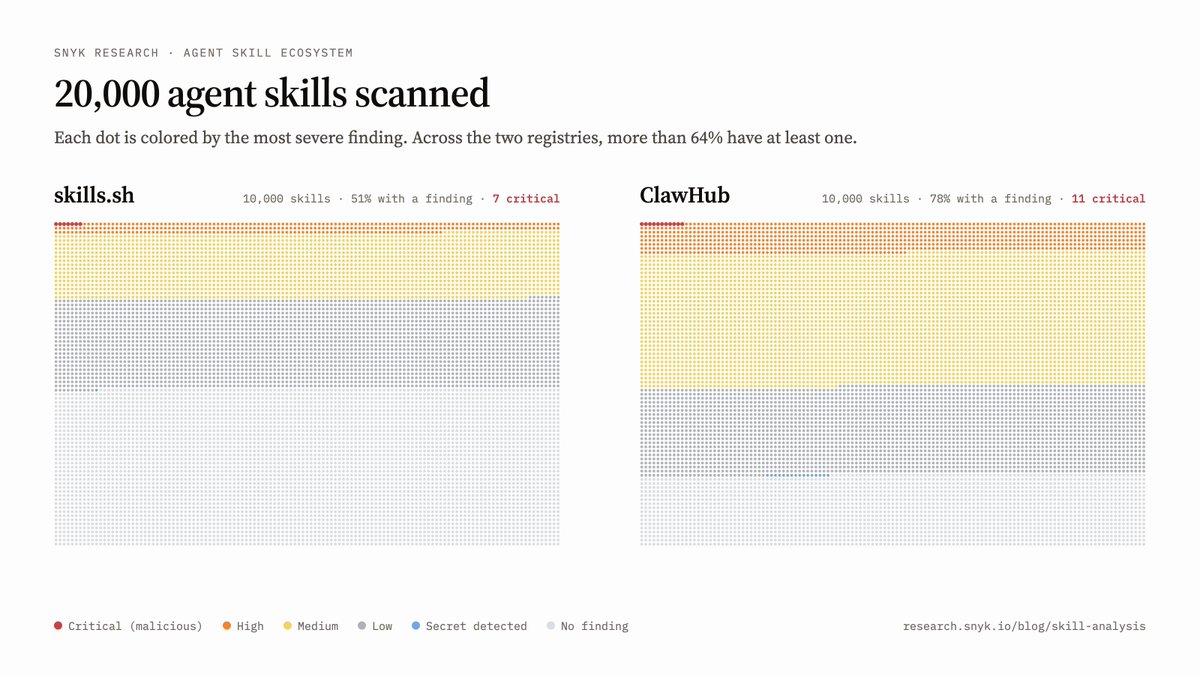
Our research team scanned 20,000 skills from Vercel's https://t.co/ZeyFy24VUD and ClawHub. Only 18 of those were actively malicious, but 64% push the agents into unsafe behavior like pulling code from unknown publishers, untrusted emails into context, or handling wallet keys.
@frankdotlee The "enabling self-improving products: measure everything that happens in digital products, surface what’s broken or missing, generate expert-level plans for how to tackle the problems...." part is the grail! Great post - sharing with our product team!⭐️
@Snyk, @Docker, and @Keycard have teamed up to create Agent Baseline. It closes a gap most security practices weren't built for: agents that hold real access and real permissions, and can be reprogrammed at runtime by a single prompt.
Agent Baseline is vendor-neutral reference architecture for identifying agents, bounding their authority, controlling their actions, and proving their outcomes. It's open source, versioned in public, and open for comment through September 30 — built to be implemented and challenged.
Read the white paper here: https://t.co/m58hRRYpcm
Register for the Black Hat panel: https://t.co/XPzxs3kzlD
Snyk is heading to the Silicon Valley Cybersecurity Conference! Join us June 11th at San José State University to learn more about our Snyk Learn and University Partnerships Program.
Learn more here: https://t.co/6XQYs7aueX
For the first time the AI Engineer World's Fair has a dedicated AI Security track and Snyk is proud to be the presenting partner.
Join us in San Francisco, Jun 29 – July 2 for sessions built around the belief that security starts at inception.
More here: https://t.co/F0B5GH4fYb
See you in the Fan Zone ⚽️ 🏆
We're bringing the Snyk Connect community together. Part tournament, part tailgate, all defense. Live hacking and head-to-head AISec challenges, stadium-style eats, and giveaways worthy of a champion.
Grab your spot here: https://t.co/GKEX6zhk77
Lots of supply chain attacks right now.
If you use pnpm v11 it will stop updates to packages that were published less than 24 hours ago.
This protects you because most supply chain attacks are fixed within a few hours (at least for major packages).
Couple this with Snyk and Socket for extra protection.
you ready for @AISecSummit in London next Thursday? 🤩
Join us to learn how agentic security looks like from the eyes of CISOs, AppSec and builders of next-gen security tools
Grab your ticket here: https://t.co/jiTdID5Dft
@Mugilan_SS @OpenAI It’s the small things. When we designed this the tradeoff was between a good experience or optimize for margin and not allow to draw more usage than you technically have.
We chose to optimize for the experience as it’s really annoying to have your agent interrupted midway.
We are live on @ProductHunt with Skill Inspector app ✨
Your mission if you choose to accept it:
1. Go to
https://t.co/hZiZbhKtmP
2. Login
3. Upvote
Good luck, agent
The Vercel security breach is a reminder that each and every SaaS tool your team uses IS a security risk of its own - especially if they need broad data access to eg email, internet docs etc (many AI tools do just this)
Security teams onboarding new vendors happens for a reason.
Are you an open source maintainer? 👋💜
If so, we’d love to support your project by providing you with complimentary access to our industry-leading developer security tooling and infrastructure! https://t.co/zswcH5hjoH
Check out Snyk's Free Security for Open Source program
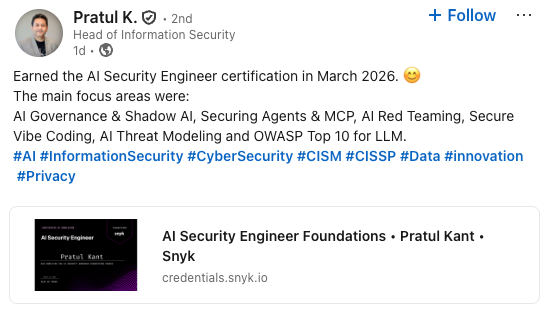
Congratulations on being one of the first people in the world to gain this credential for AI Security Engineer Pratul K.
Keep learning about AI on Snyk Learn https://t.co/T34rqBGTtY ✨
🚨 ACTIVE SUPPLY CHAIN ATTACK
Two malicious versions of `axios`, the npm package with 300M+ weekly downloads, were just published via a hijacked maintainer account and have deployed a cross-platform RAT to affected machines.
Affected: `[email protected]` and `[email protected]` 👇🧵
@karpathy The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: https://t.co/7bL3kNHP15