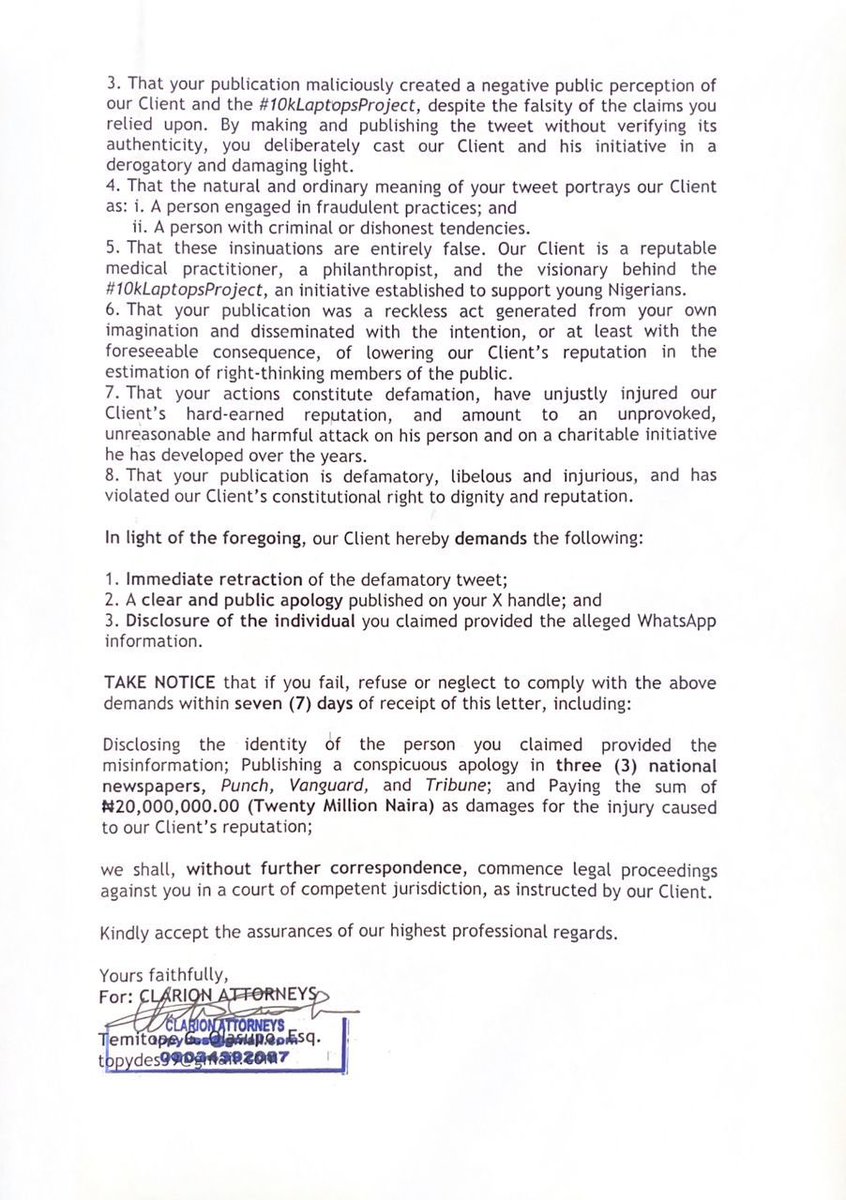
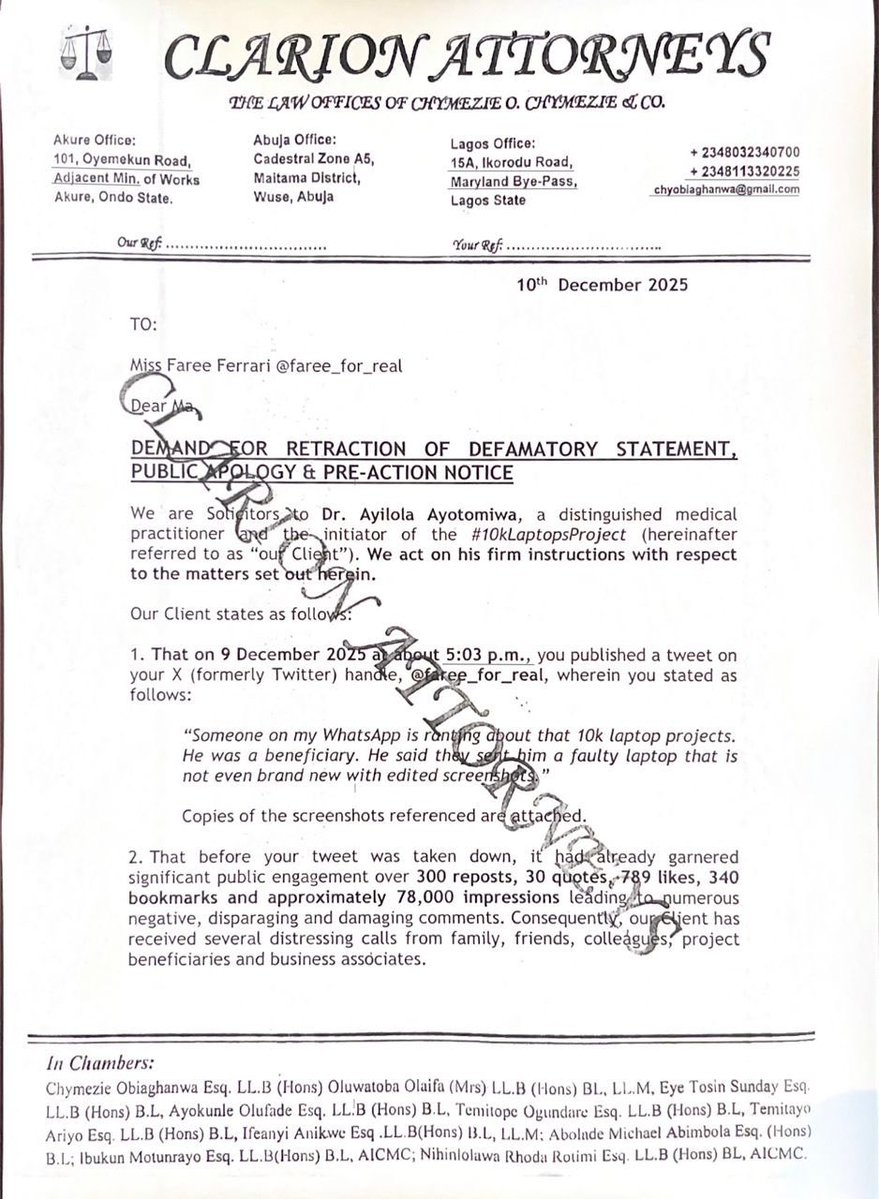
All I asked, @faree_for_real, was for you to provide evidence of the person who sent the WhatsApp post you shared in your Twitter Space, where it was indirectly implied that the organisers of the 10k laptops initiative were distributing faulty devices.
Even if you buy your Samsung 1M, na u go still use mouth explain say your mobile cost
But u see iphone, that 3 camera no need chochocho
U go just dey hear Pablo left front center
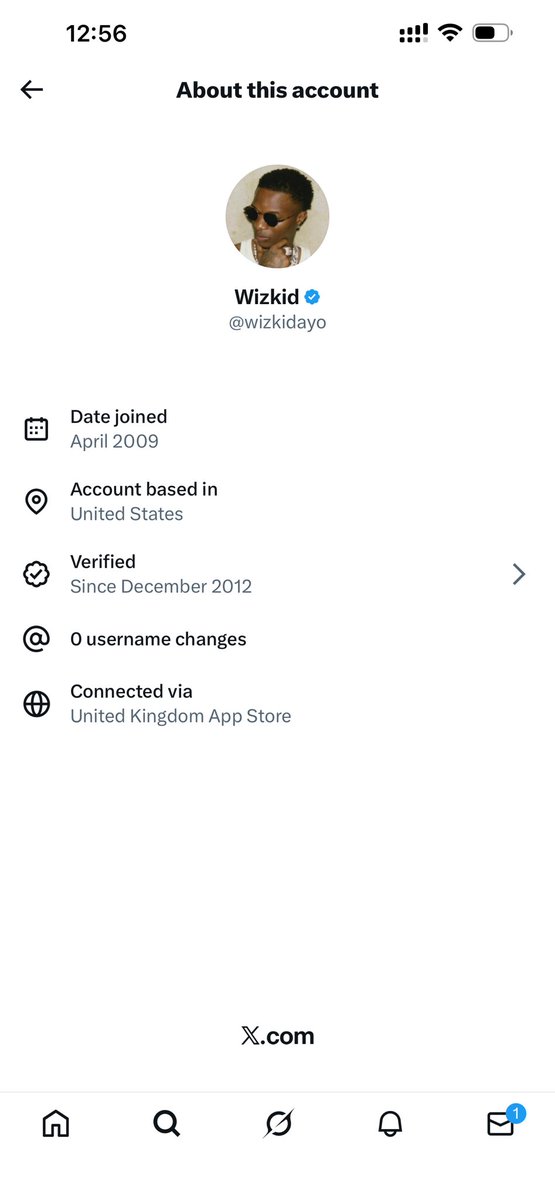
The new “Automatic Account Location” feature being rolled out by X has triggered important legal questions about the lawfulness of this form of data processing. X has stated that the objective of the feature is to promote transparency, combat misinformation and inauthentic behaviour, and address the rise of AI-generated spam.
Determining whether this processing is lawful requires answering three core questions:
1) Are the data shared through the feature “personal data”?
2) If yes, has X lawfully processed them?
3) If not personal data, does any privacy obligation still arise?
1. Are the data being shared by X “personal data”?
Article 4 of the GDPR defines personal data as information relating to an identified or identifiable natural person. Identification may be direct or indirect.
X is a platform with millions of users, many of whom operate under pseudonyms, parody identities, fictional names, or anonymous fan accounts. A large number of accounts do not reflect an identified natural person at all.
The question therefore arises: does the disclosure of a non-precise, non-real-time location (e.g., “Country of use”) amount to personal data?
Under the GDPR, the answer is “no” where the account is not tied to an identifiable natural person. For parody accounts, bot accounts, organizational accounts, burner accounts, or fictional identities, the disclosed information does not relate to a known or identifiable data subject. In such cases, the GDPR and similar legislation such as the NDPA do not apply, because their scope is limited strictly to personal data.
The information disclosed is neither an IP address nor a real-time geolocation. It is too coarse and too detached from a specific, identifiable human being to meet the definition of personal data for these categories of accounts.
However, for identified natural persons, the location information does qualify as personal data under the GDPR and NDPA. Therefore, the next question is whether X has lawfully processed such data.
2. If they are personal data, has X lawfully processed them?
Data protection laws provide specific grounds for lawful processing. One of these is compliance with a legal obligation imposed on the data controller. Article 6(1)(c) of the GDPR states that processing is lawful when:
“Processing is necessary for compliance with a legal obligation to which the controller is subject.”
To rely on this ground, two sub-questions naturally follow:
(1) Were users notified of this basis/processing before processing?
Transparency and accountability are non-negotiable principles under the GDPR and other legislations like the NDPA. X’s Privacy Policy (effective July 28, 2025) discloses under section 2.2 that user information may be used to foster safety and security of users and to defend against fraud.
Section 3.3 further states that X may share or disclose user information where reasonably necessary to comply with law, protect the safety or integrity of the platform, prevent spam, abuse, or malicious activity, and address fraud and security risks.
Therefore, the notification and transparency requirements are met.
(2) Is there a legal obligation that necessitates this processing?
X is subject to several regulations globally as a large online platform.
For the purpose of this analysis, the EU Digital Services Act (DSA) is instructive. The DSA, widely regarded as a gold-standard regime, requires platforms to implement technical and organisational measures that ensure:
- a high level of privacy and safety,
- protection for minors and vulnerable users,
- consumer protection in environments where the platform facilitates trade,
- mitigation of illegalities such as fraud, misinformation, impersonation, & deceptive content.
Given X’s stated purpose for the feature, promoting transparency, combating misinformation, addressing inauthentic behaviour, and fighting AI-generated spam, the measure is clearly aligned with its compliance obligations under...
1/2
Nothing beats trilogy. The villains are the best.
From Ra's al Ghul, Joker and bane. Christopher Nolan sealed his greatness with that masterpiece. Christian bale will always be the best.
CORRECTION: Gen. Uba, Brigade Commander of Damboa has been comfirmed killed by ISWAP terrorists.
Before his unfortunate capture, the Brigade Commander made this video we shared stating that he was okay. Unfortunately, after several hours, lost orientation within the forest.
The troops, both ground and air made several efforts to rescue the Commander who told them he was on his way to return to his base. He was unfortunately re-captured by the terrorists after viral report of his abduction went viral.
@DHQNigeria@HQNigerianArmy
Time for @thenff to take their job seriously. Missing yet another World Cup reflects deep structural failures that can no longer be ignored.
Same players refused to train recently because they were not paid thier bonuses. This is terrible!!
#NGADRC
Nigeria joked with most of their qualification matches and ended up paying the ultimate price. If only we had taken our 1st few matches more seriously.
#NGADRC
When I saw this form this morning, I knew it was going to be taken down.
You can't ask people to send in their data which includes NIN number, NIN picture and passport just like that. Scammers often use these forms to harvest personal information for fraudulent activities.