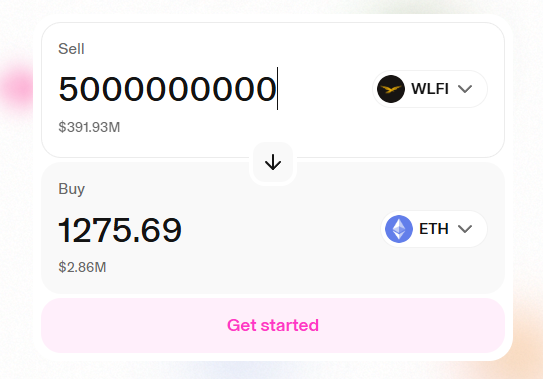
For people who do not understand how bad the situation is, their most liquid pool is on ETH which has $2.8M. When this gets liquidated, selling this stake on that pool today gets you $2.8M (basically the whole pool).
@Dolomite_io has no way to liquidate this and come out as whole from this situation. The stablecoins that were borrowed belonged to people who people who deposited on Dolomite for earning yield. When they go to withdraw it, they will not be able to do so.
@CoreyCaplan3 is the founder of @Dolomite_io and the CTO of @worldlibertyfi. He has not commented so far but he seems to be in the right position to suggest this Dolomite rug. It is at the expense of depositors on Dolomite.
🚨 $WLFI Team has now borrowed $150M worth of USDC against 5% of $WLFI supply. $WLFI has less than $10M in core assets all their DeFi pools on all chains combined.
@Dolomite_io is rugging. Their founder is the CTO of @worldlibertyfi so you know he's aware of this. Despite several alarms raise, he hasn't said anything on this topic.
@ArtemR@rodydavis@_mohansolo@antigravity I believe it is ridiculous if any issue with using their AI platform can cause real harm to the actual Google account. A lot of things are dependent on the Google account. It is just safer to not use them to ensure the safety of the main account.
Dear Mr. Hacker,
It is with the deepest admiration that we write regarding your recent undertaking on-chain.
With a single valid signature, you relieved the EP vault of 612,506 EP and converted the whole of it into approximately 1,050 USDT. We observed, moreover, that you paid the full 10% sell tax without complaint, a portion of which was burned in the project’s honour. Such civic-mindedness is rarely seen in your line of work.
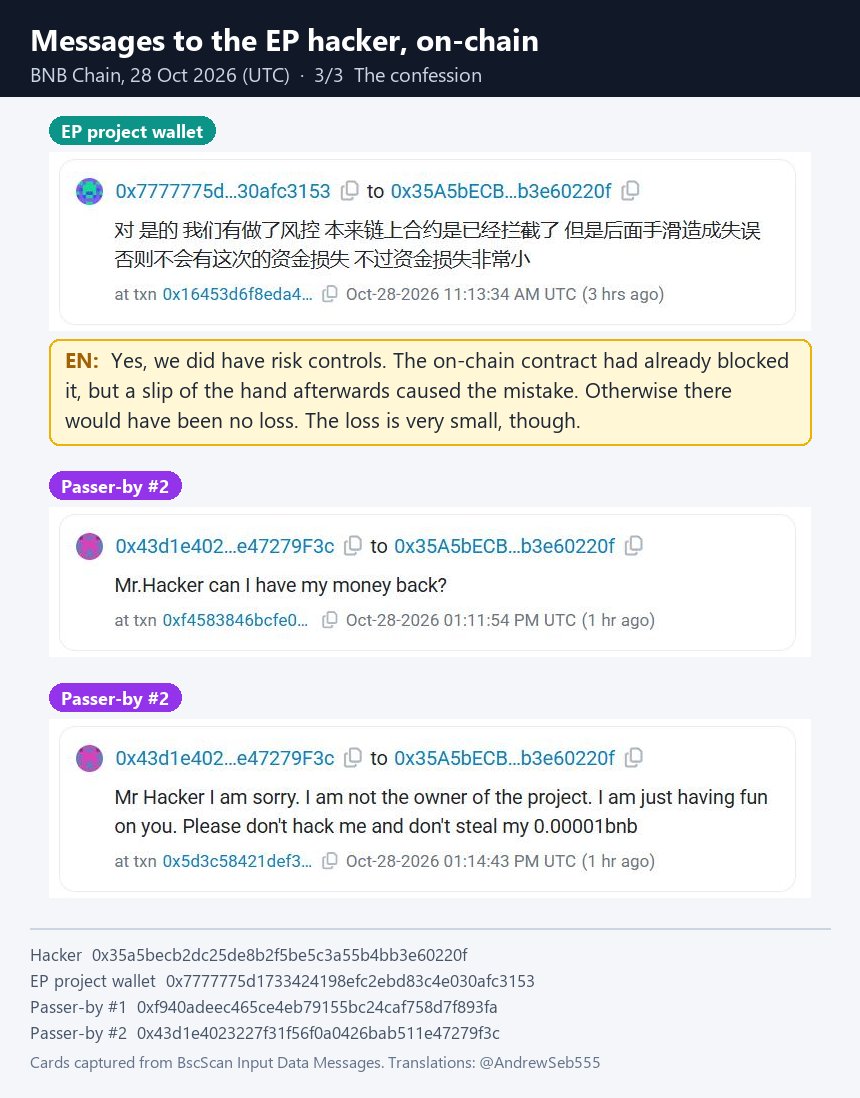
We must also apologise for the tone of certain correspondence sent to you on-chain. One party addressed you plainly and demanded the return of the funds. We were mortified. As a more refined correspondent has since reminded us, one should begin with “Mr. Hacker, can I have my money back?”
It is in that spirit that we most humbly ask whether you might see your way to returning some portion of the sum. We appreciate that it may already have departed for Monero, from which, we are told, few return.
Should you decline, please know that you remain in our most respectful thoughts.
We have the honour to be, Mr. Hacker, your most obedient and humble servants,
On-chain Participants
P.S. The gentleman who recommended the respectful tone has asked us to state, for the record, that he is not you.
An unusual on-chain negotiation:
"Return the funds."
"Please be respectful. You are asking someone who lacks any moral compass to return money."
"Keep some, return some—or I’ll organize the evidence."
Blockchain transparency makes for some very public conversations.
I think the number of accounts in the first batch was so low that it must have been dismissed as an outlier.
They mentioned that they would refund everyone but haven't mentioned what exactly went wrong. Also, if they only went after the big accounts, there's a chance that the hacker still has the keys for the smaller accounts and they're yet to be drained.
If it is a case of the hacker being selective, they're just being dishonest by not asking affected people to take measures.
🚨 @predictdotfun users got drained again today. It’s the second time in 5 days, and at least $390K is gone.
What happened:
• Today, 21 accounts lost their USDT. At least $265K. Most of it happened in 34 minutes, starting at 05:31 UTC.
• On Oct 22, the same setup hit 4 accounts for almost $125K.
• The money was moved to Ethereum and 115 ETH went into Tornado Cash, a mixer that hides where funds go.
I checked this on-chain. Every drained wallet is an account on the platform, and the attacker didn’t touch wallets from any other app, from my scan.
This wasn’t a hack of the platform’s smart contracts. It also wasn’t the usual “you signed a bad approval” scam.
Each withdrawal was signed with the victim’s own wallet key. It just wasn’t done through the app. Transactions from the app and from the attacker look completely different on-chain. Same keys, different door.
So someone was able to sign for these accounts. It could be leaked keys, a problem with how the keys are stored, or a hijacked login.
If you keep a large USDT balance sitting idle there, consider moving out what you’re not actively using until the team explains. So far only USDT balances have been taken, and open positions weren’t touched.
CC @dingalingts
The story of my last 4 month:
> I came up with a strategy for Predictfun
> Tested it on paper
> Tested it with small capital
> Fine tune it
> It was finally profitable
Got drained.
Update: @predictdotfun has confirmed the incident. They put the losses at about 400,000 USDT, which is in line with what I found on-chain across both waves (at least $390K).
They say all affected users will be fully reimbursed.
Their early finding is that their API documentation site, which a third party hosts, may have been compromised. The site is offline until the investigation is done, and they’ve promised a full post-mortem.
On-chain, every theft was signed with the account’s own key. So the open question is how those keys were exposed.
https://t.co/qNBuuGarFL
We are aware of a small number of users who have experienced unauthorized transfers of funds from their wallets, totaling approximately 400,000 USDT.
Our preliminary investigation suggests that our API documentation site, which is hosted by a third-party provider, may have been compromised, potentially affecting a small number of users over a short period of time. The API documentation site has been taken offline as a precaution and will remain offline until our investigation is complete.
At https://t.co/lu7UxgqTOy, we take the security of our users and their funds extremely seriously. As such, we will fully reimburse all affected users for any funds lost as a direct result of this incident.
Once our investigation is complete, we will publish a full post-mortem detailing what happened and the steps we're taking to prevent similar incidents in the future.
The details, for anyone who wants to check.
Where the money went today -
Each drained account sent its USDT to a brand-new wallet, and each of those wallets bridged it to Ethereum within seconds:
0x0299b21d5a285e3ee5505c12299b4e33d3bab102: 60,500 USDT (1 account)
0xcd34891c7fc9299f86da30e4797232ae6f4f685c: 53,700 USDT (1 account)
0xbe754caab768f114b1d610982dfe981e13fc83b8: 50,510 USDT (4 accounts)
0x002c755b902dfc0fff94bb5ba05789d8ead8a2e4: 41,000 USDT (1 account)
0x8b001d7378dbc19c1c62e39c0fc9ffad84182fba: 24,655 USDT (7 accounts)
0x435f8c80de1190a96adf625532faab76b24fb2d4: 23,815 USDT (3 accounts)
0x31383cec40efc929f293c4cf54e29219b70076e9: 7,415 USDT (2 accounts)
A 100 USDT drain at 5:10 UTC. One account was hit a second time at 06:18 UTC, for 3,538 USDT. A smaller ones followed (111 USDT). The last of those was at 08:49 UTC, after people had already started posting about it.
Into Tornado Cash -
On Ethereum, these 7 wallets put 115 ETH into Tornado Cash between 05:41 and 07:26 UTC. The first deposit landed 10 minutes after the first drain, while the drain was still going on:
0xd500a43442253a4b92a025f6604df2dd57d78e6f: 30 ETH
0x85cd3ee47307bcaf9e1ada4230cc7646e603d429: 22 ETH
0x5b51e000f08eeaf34484ea6b7e16f536773fe4ee: 20 ETH
0x93b94f8db5655064f35b2cbc5b8e37e34443747c: 20 ETH
0x3c9f6411cd1fbefaf33397145514ed2bf662eef9: 10 ETH
0x294dc89990f70ddb3067b0a8c917413a3e8d7c13: 10 ETH
0x44870558ef468eaf3caef7c802945a6697ec30a5: 3 ETH
The first wave, Oct 22 -
0xd14ca6d1173a710706149a222b7e20324003a660 lost 82,000 USDT to 0xeda13cffb9b1bb71b948c2b0132f04cf466de710, plus 27,000 USDT bridged to 0x177e67f11a0390edc735d220f4d553e1182ab5f3 on Ethereum.
0xa5162f5bb972a508dee6bb1092ceb22ebd1e4d40 lost 13,920 USDT to 0x420c85800903dc93424dde4ace10d0e229534a5b.
0x773b2b07f2c7fcb23ad72394e18bcb9eec618e4a lost 1,410 USDT and 0x8ae78a3d93cc30fc85dc2720f9ae5ee875c5c0d0 lost 535 USDT, both to 0xe5f3bcf5ae7818da8e0122352e1558b79c7fbff9.
How it worked -
For every drained account, the theft was the first transaction of this kind it had ever made. It took two steps. First, allow a gas service to charge the account in USDT and then send the whole balance out. Both steps were signed with the account’s own key, but in a format the app doesn’t use.
Of 9,568 normal https://t.co/IlFGvKwlhq transactions over two days, only 3 used a gas service like this. All 80 accounts I checked sign in the app’s standard format. All 70 of the attacker’s transactions used the gas service and the other format.
Relayer: 0x3cfdc212769c890907bce93d3d8c2c53de6a7a89
Gas service (owned by that relayer): 0x8b1f6cb5d062aa2ce8d581942bbb960420d875ba
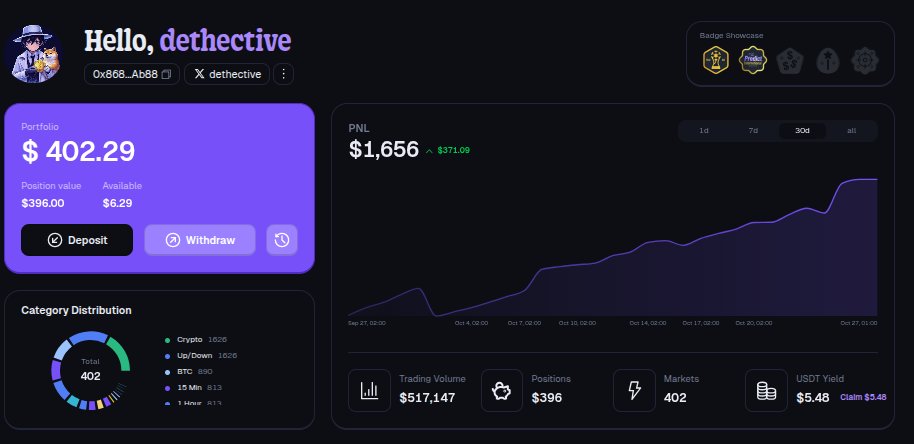
Example, @dethective’s account: https://t.co/2e9hgInCKF
How I know these are https://t.co/IlFGvKwlhq accounts
All 30 wallets the attacker touched run the wallet contract from https://t.co/IlFGvKwlhq’s own code (0xbac849bb641841b44e965fb01a4bf5f074f84b4d). They use the same signer module (0x845adb2c711129d4f3966735ed98a9f09fc4ce57), and they have permissions set on https://t.co/IlFGvKwlhq’s trading contracts, such as 0x8a289d458f5a134ba40015085a8f50ffb681b41d. Normal https://t.co/IlFGvKwlhq users look exactly the same.
On the other hand, when the contract sells on the chart to recover fees, it paints the chart red, because it sent funds to the chart which never belonged there. Surely, you get more volume, at the expense of causing panic when the contract nukes.
That being said, I don't think either approach can be strongly criticised.
Backpack is a great solution. The issue here is that people say that tokenized stocks have 24/7 liquidity as they are on-chain, but during the weekend they're unable to be arb'ed with real stocks, leaving them isolated and open to PA like a shitcoin.
If he would have waited till after the weekend, the MMs would have brought it up to par but then claiming that tokenized stocks are available 24/7 wouldn't be correct.
Farming on bundled tokens requires a conscious decision from the victim and they agree to participate in it. Draining wallets is taking funds from someone who is just holding funds on his wallet.
They do seem very similar things treated differently now because they are. 3 years ago, if someone would grift and farm, people would shun them out of Crypto. These days, they get an affiliate badge and the platforms push them towards new audience.
@Hikkimori That is the right thing to do, especially when he has people like you screenshotting DMs lol
"Pump employee bid this XXXX memecoin. Posted with proof"
If it has been fixed now, that's good news. This approach requires optimization because the taxes are sold into the chart at a different point than when it was acquired.
One of the systems I work with requires this to happen on buybacks. It requires keeping the amount in check to avoid impact on the chart and from searchers not profiting off it to extract from the project.