Four years ago, we built @MistTrack_io to make on-chain tracing and AML compliance analysis more accessible. Today, it’s trusted by 500+ institutions and 100,000+ users.
Whether you’re investigating fund flows, building tools, or managing compliance, we’ve got options for every budget 🔎
✅ Free tracing & wallet risk checks
✅ Premium from $229/month
✅ API from $20 for 100 calls across 19 chains
Explore what we’ve built → https://t.co/HcDNzjYTy7
Built by the @SlowMist_Team four years ago, MistTrack was purpose-built for on-chain tracing and AML compliance analysis. Today, it’s trusted by 500+ institutions and 100,000+ users.
On-chain intelligence for every budget 🔎
✅ Free tracing & wallet risk checks
✅ Premium from $229/month
✅ API from $20 for 100 calls across 19 chains
Investigators, developers & compliance teams: get started → https://t.co/ezJvCoNJ1s
🚨 MistTrack Fund Tracking 🚨
Drift Protocol Exploiter is moving funds.
💸 25,710 $ETH mixed via Tornado Cash
📌 Address: 0xAa843eD65C1f061F111B5289169731351c5e57C1
We’ll continue tracking the movement of these stolen funds.🕵️♂️
https://t.co/GmIkNvq40E
🚨 MistTrack Fund Tracking 🚨
CryptoBillis Ledger Drainer-related address is moving funds.
💸 ~463 $ETH transferred into Tornado Cash
📌 Address: 0x83aeaC166f6832aE3500000a24510a95a052A599
We’ll continue tracking the movement of these stolen funds.🕵️♂️
https://t.co/Ui4ONY5R5F
We’re seeing @tether freeze a significant number of $USDT across addresses linked to this incident.
Based on our current tracking, the reported losses are approaching $90 million. Some affected users have contacted us for assistance, and our team is actively following up on these cases.
bc1qjqgwejnp8dc0x2938x9n9954hj97t82unx49dl
bc1qqnkwurxs99xkx5t4yffqhq3u6qwy0qpjyujtm9
bc1qgqheemzla77pesl227hdtgf5ykz62d0zvld26n
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW
TSDWtuZ2pARUVz4v3PkL2hi3iXPjowAr5a
0x69c8f401cfc6cd40ac94691d6d7c48e3b7a47841
0x033636e45d519bebb7b5c2520ca6ce56fbdb4f7a
0x83aeac166f6832ae3500000a24510a95a052a599
🫡 cc @SpecterAnalyst
We’re seeing @tether freeze a significant number of $USDT across addresses linked to this incident.
Based on our current tracking, the reported losses are approaching $90 million. Some affected users have contacted us for assistance, and our team is actively following up on these cases.
bc1qjqgwejnp8dc0x2938x9n9954hj97t82unx49dl
bc1qqnkwurxs99xkx5t4yffqhq3u6qwy0qpjyujtm9
bc1qgqheemzla77pesl227hdtgf5ykz62d0zvld26n
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW
TSDWtuZ2pARUVz4v3PkL2hi3iXPjowAr5a
0x69c8f401cfc6cd40ac94691d6d7c48e3b7a47841
0x033636e45d519bebb7b5c2520ca6ce56fbdb4f7a
0x83aeac166f6832ae3500000a24510a95a052a599
�� cc @SpecterAnalyst
Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: https://t.co/4p918UH8yb
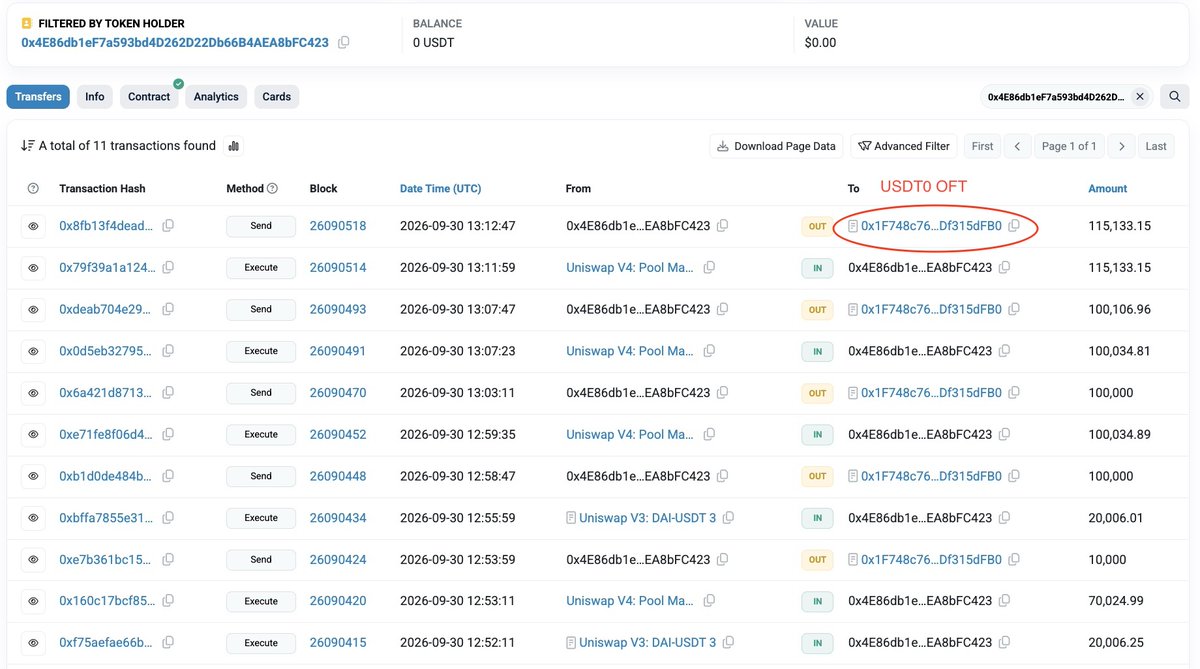
🔎 The @bitget exploiter is moving stolen DAI on Ethereum through a series of swaps and cross-chain transfers:
DAI → USDT on Ethereum → USDT0 → Tron
💱 One recent transaction:
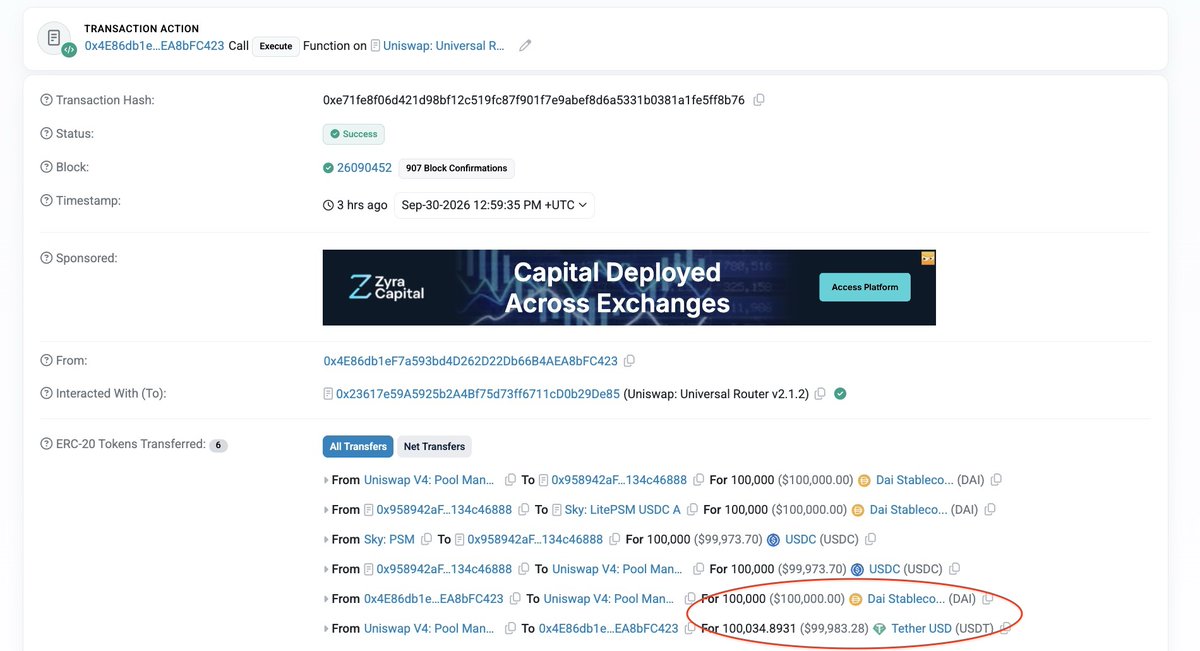
100,000 DAI → 100,034.89 USDT via #Uniswap.
https://t.co/txJ5DzvAkf
🌉 The USDT was then transferred from Ethereum to Tron via #USDT0 infrastructure.
https://t.co/xck9s5JmM2
USDT0 OFT:
0x1f748c76de468e9d11bd340fa9d5cbadf315dfb0
Tron-side USDT0 OFT:
0x3a08f76772e200653bb55c2a92998daca62e0e97
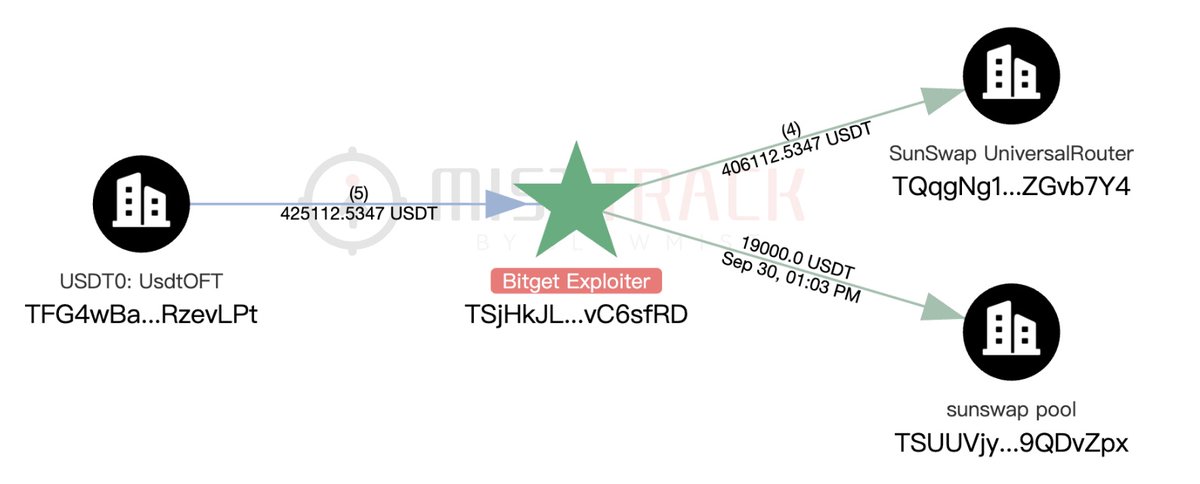
On Tron, the funds continued moving via #SunSwap:
• 90,967 USDT → $USDD
• 19,000 USDT → $TRX
This activity is part of an ongoing flow from an address linked to the Bitget exploiter. The same address has been repeatedly converting $DAI to $USDT and bridging the funds to #Tron.
We’ll continue tracking the movement of the stolen funds across chains and services. 👀
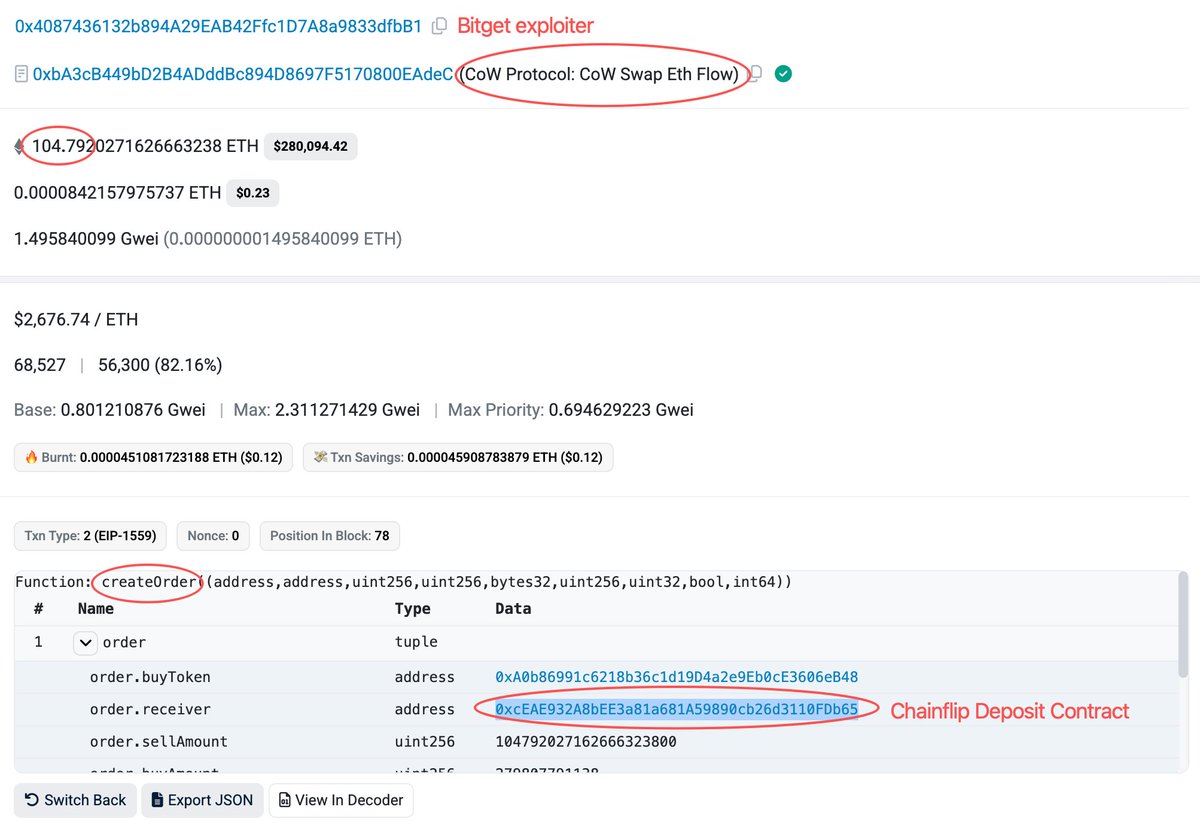
🔎 MistTrack TrackAgent spotted a notable cross-chain pattern in the movement of funds stolen from Bitget: Using a CoW Protocol + Chainflip combination to automate cross-chain transfers.
The flow:
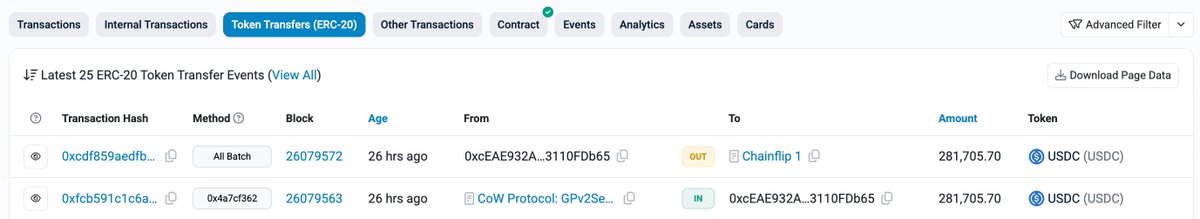
1) An automated script creates an order on #CoWProtocol.
2) The order’s recipient is set to a pre-prepared #Chainflip Deposit Contract address.
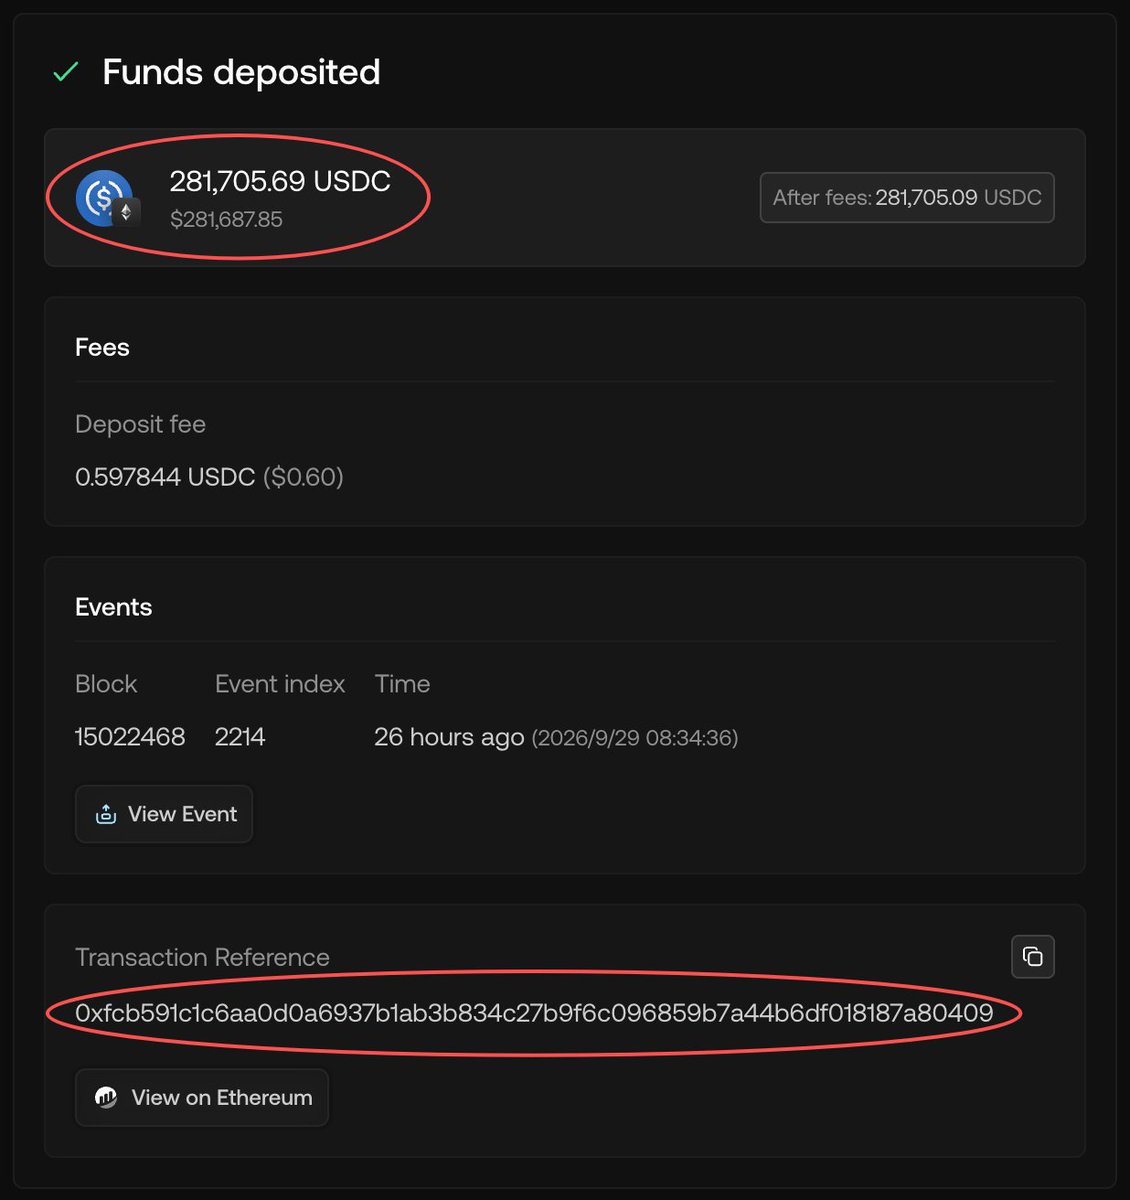
3) Once the order is executed, the assets enter Chainflip and are swapped across chains into BTC.
⤵️ One example:
Create Order on CoW Protocol:
https://t.co/uuFVTfiaaY
Order execution:
https://t.co/epOlkRgq9X
Chainflip Deposit Contract:
0xcEAE932A8bEE3a81a681A59890cb26d3110FDb65
Chainflip swap:
https://t.co/ZY4NObPLCa
Destination BTC address:
bc1qa0rjjhyu9pg3adgpel4v7dct6a8606az863jyh
The interesting part is the automation: rather than manually interacting with each bridge or swap, the attacker can prepare the destination and let the flow execute once the order is filled.
We’ll continue tracking how the stolen funds move across chains and services. 👀
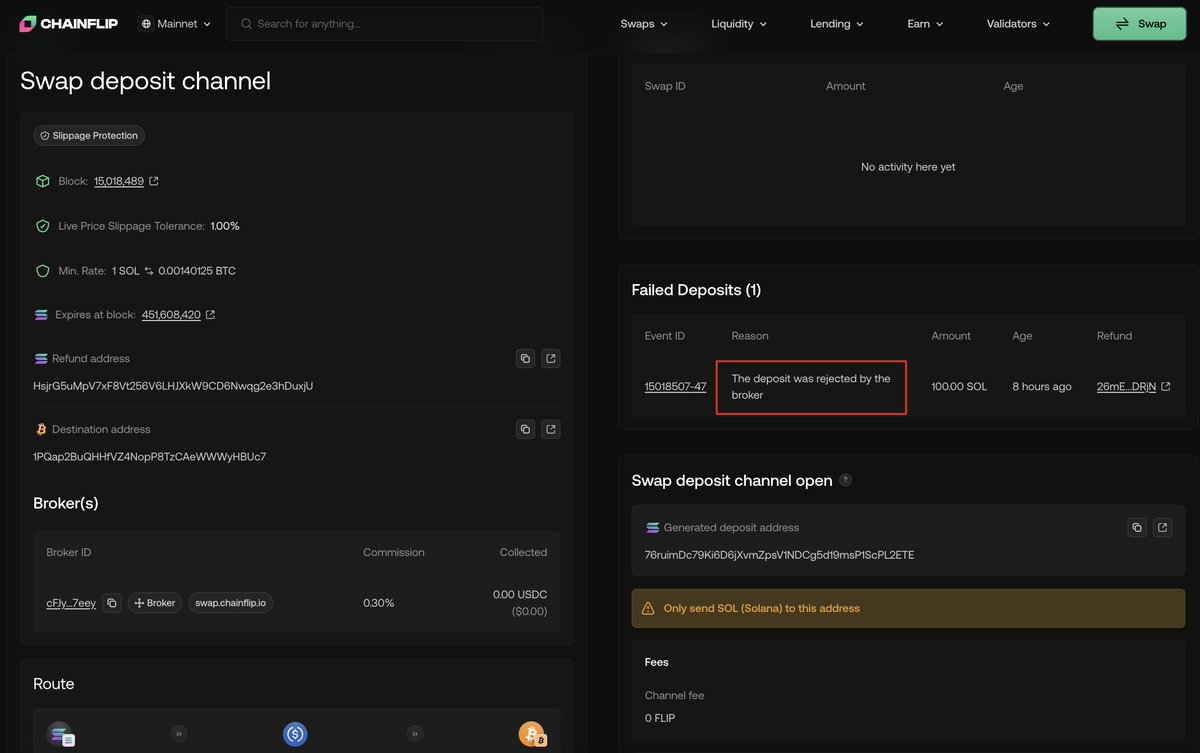
The @bitget exploiter tried to move the stolen funds through @Chainflip.
Chainflip’s response?
“Deposit rejected by the broker.” 👋
No freeze, but no luck either — the funds were refunded. 👍
Nice try. 😶
We’ll continue tracking the movement of the stolen funds.
🔗 https://t.co/bG3EaPa1PI
Because multiple Asgardex contributors explicitly refused to return the ~$900K in fees you profited from the Bybit hack by DPRK.
Multiple of those teams you mentioned decided to return fees.
Choosing to keep Thorchain as decentralized as possible and not censoring activity at the protocol level is one thing.
Profiting fees off the hack (knowingly) and then refusing to return those fees after is criminal.
I don’t think THORChain’s TSS + validator model represents true decentralization.
The selected validators set collectively controls the underlying assets in the TSS vaults. Once the signing threshold is reached, those validators can move the funds. So from a custody perspective, THORChain is not comparable to Bitcoin or Ethereum base-layer consensus — it effectively acts as an intermediary between users and the native chains.
TSS distributes control among multiple parties, but distributing an intermediary does not eliminate the intermediary.
Our attacker addresses are publicly listed and actively tracked. We are formally asking @THORChain to refuse service to these addresses. Decentralization is a design principle, not a shield for facilitating known stolen funds.
The industry is watching.
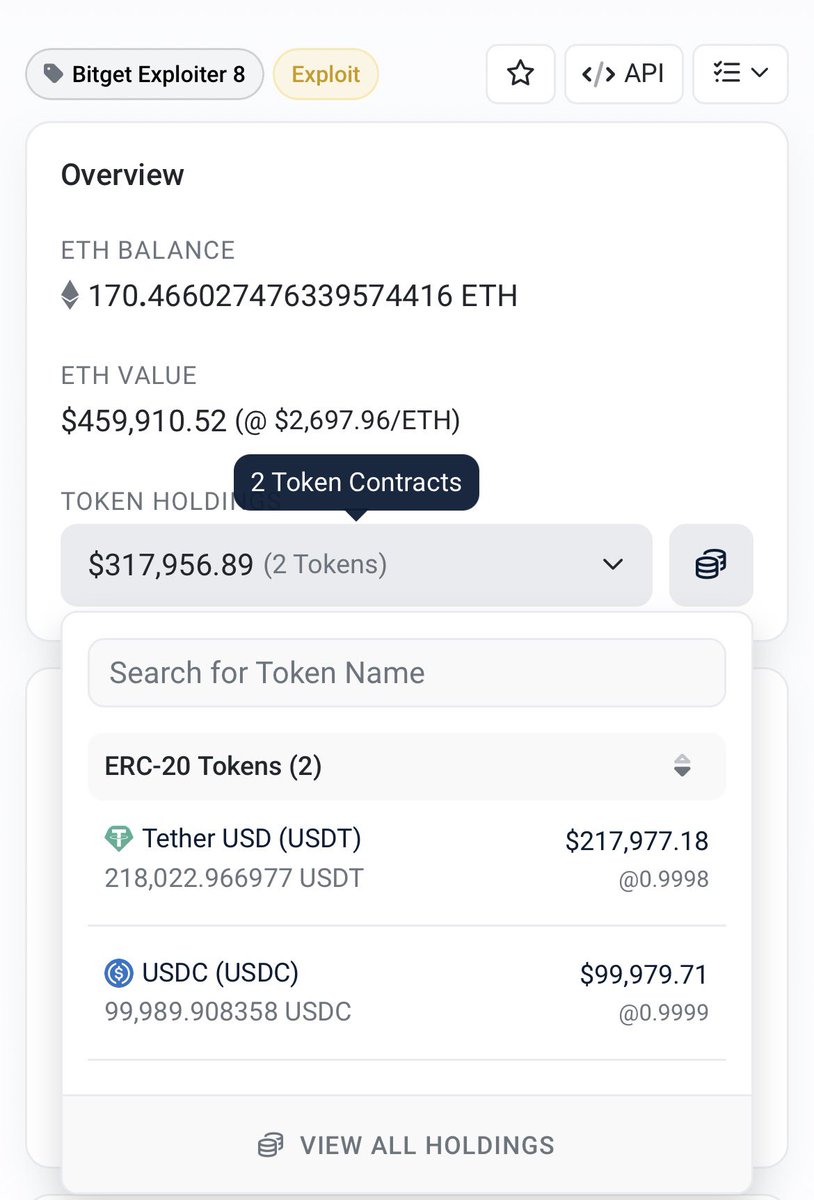
So far, we have identified the following addresses associated with the @bitget exploiter that still hold funds. We will continue to update this list. @GracyBitget@xiejiayinBitget@Bitget_zh https://t.co/bEpZSxzZhs
So far, we have identified the following addresses associated with the @bitget exploiter that still hold funds. We will continue to update this list. @GracyBitget@xiejiayinBitget@Bitget_zh https://t.co/bEpZSxzZhs
THORChain and Stolen Funds: The Industry Needs Answers
After the $1.46B @Bybit_Official hack last year, nearly $1.2B in stolen funds was reportedly traced through @THORChain as the attackers moved assets across chains.
Today, following another major security incident at @Bitget , we are once again observing Bitget Exploiter funds being sent into the THORChain for asset swaps and cross-chain transfers.
The question is no longer:
“Does THORChain know these funds are associated with hackers?”
The attacker addresses have already been publicly flagged and are being actively tracked by exchanges, blockchain security/aml firms, and the wider crypto industry.
The real question is:
When a protocol is aware that funds originate from a publicly identified major hack, yet continues to facilitate large-scale cross-chain swaps, how should the industry view this under the banner of “decentralization”?
Decentralization should not become a blanket excuse when dealing with known stolen funds.
If, after every major crypto hack, attackers can continue using THORChain as a route to move funds from ETH → BTC, BNB → BTC, and across other chains, the industry needs to seriously ask:
What responsibility should THORChain bear when handling known stolen funds?
@GracyBitget@xiejiayinBitget@benbybit