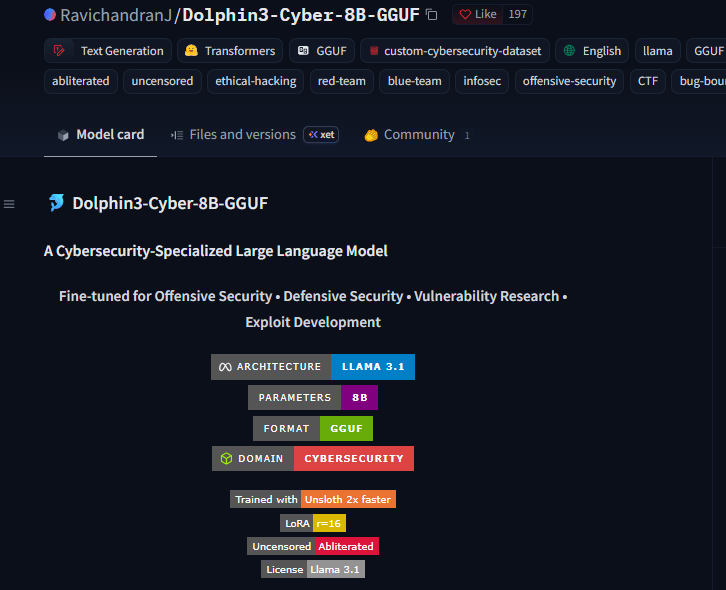
¿Imaginas correr un modelo de 8B especializado 100% en ciberseguridad, sin ningún tipo de censura ni bloqueos molestos, directamente en tu laptop con una GPU de 8GB?
Dolphin3-Cyber-8B (en su versión GGUF optimizada en Q2_K a solo 3.2 GB) acaba de salir y es una bestia para el día a día.
Lo que trae bajo el capó:
• Cero negativas absurdas en preguntas sobre pentesting autorizado.
• Entrenado con un dataset custom: OWASP Top 10, MITRE ATT&CK, CVEs, ExploitDB y metodologías reales de pruebas de intrusión.
• Ideal para code review rápido, resolver CTFs, armar notas de bug bounty y diseñar modelos de amenaza.
(Tip: mantén el contexto cerca de los 2k tokens que fue lo que vio su LoRA para que no alucine).
Herramienta brutal para llevar un asistente ofensivo local sin depender de la nube.
Te dejo el enlace al repositorio y los pesos directos abajo en los comentarios 🛠️👇
OSINT METHODS
39 step-by-step guides to the most common OSINT techniques. Beginner, intermediate and advanced levels.
https://t.co/e5WyEWbjMR
#osint#socmint
INSTEAD OF WATCHING NETFLIX TONIGHT. Spend 2 hours with this. Claude AI FULL COURSE that teaches you how to BUILD and AUTOMATE anything. The people who watch this tonight will wake up tomorrow with a new skill. Watch it and bookmark it now.
APRENDE A HACKEAR!!!
Hay un catálogo de máquinas vulnerables, montadas a propósito, donde puedes practicar intrusión sin cometer ningún delito.
Laboratorios gratis, entorno real.
Y cuando te atascas, existen las soluciones escritas paso a paso.
3 OSINT TOOLS I’M DONE GATEKEEPING
These are the kind of tools that make you realize how much information is already sitting on the public internet.
→ ROSINT can surface deleted Reddit content that has been archived.
→ Insecam lets you explore publicly accessible security —> camera feeds and see just how exposed some internet-connected devices can be.
→ MarineTraffic tracks cargo ships, oil tankers and superyachts in real time using public maritime data.
No hacking.
No exploits.
Just publicly available information being collected and visualized in ways most people never think about.
OSINT is getting ridiculous.
REPO BELOW
If you're new to exploit development, reverse engineering or vulnerability research, bookmark this before buying another course.
Blackstorm Security has published 1,600+ pages of research for FREE.
Windows kernel exploitation.
Driver reversing.
Patch diffing.
Chrome / V8 / WebAssembly.
Hyper-V.
macOS / iOS internals.
Modern mitigation bypasses.
Real CVEs taken from root cause to working exploitation.
Their CVE-2024-30085 series alone spans hundreds of pages and multiple exploitation strategies.
This is the kind of material that teaches you how vulnerability researchers actually think, not just how to run tools.
19 research papers. 1,657 pages. Free.
Start here:
https://t.co/wDftgmamHH
Author: @ale_sp_brazil
Focus on the techniques not the tools (X64DBG, GHIDRA/IDA, WINDBG, GDB GEF)
#ExploitDevelopment #ReverseEngineering #VulnerabilityResearch
Run local uncensored AI Model for cybersecurity : that's actually built for red teamers & pentesting
- Trained to handle offensive & defensive cyber like a pro.
- Exploit crafting, vuln analysis, remediation, the works.
- Long context for digging through massive logs.
- And small enough to run consumers hardware.
Runs on a single GPU, thinks like a seasoned pentester, and won't lecture you about ethics.
This thing doesn't refuse it delivers. No more jailbreaking generic models just to get useful output.
If you're in InfoSec, DevSecOps, or just love playing with powerful open tools this deserves a spot in your arsenal.
🧰 Petit aperçu de la toolbox :
Surveillance de canaux Telegram + RSS feed
Suivi des fuites de données (dataleaks)
Prise de notes avec visualisation en graphe (façon Obsidian)
Outils d'investigation SOCMINT
Archivage de pages web (en local)
Cartographie de plus de 700 liens vers des bases de données publiques internationales (ex. Pappers, Pages Jaunes)
Téléchargement de médias multi-plateformes (tous réseaux sociaux)
Recherche Whois
Plein de nouvelles fonctionnalités seront ajoutées. Le but est encore une fois de permettre à chacun de self-host facilement son propre workspace.
‼️🚨 Critical remote code execution in libssh2, the SSH client library embedded in countless tools: CVE-2026-55200, rated CVSS 9.2 by VulnCheck. Every version up to and including 1.11.1 is affected.
It's an out-of-bounds heap write in ssh2_transport_read(), which fails to bound-check the SSH packet_length field. A malicious or MITM'd SSH server can send oversized packets to corrupt memory and run code on the connecting client.
No known exploitation yet and it's not in CISA's KEV. Fix: move to a build that includes commit 7acf3df (PR #2052), and inventory anything that links libssh2 for SSH, SCP, or SFTP.
OptimizerDuck, open-source tool yang bikin lo uninstall CCleaner.
Ini bukan cuma "cleaner" biasa. Dia gabungin 30+ tweak Windows dalam satu app, dari matiin telemetry, block bloatware, sampai GPU registry tweaks yang biasanya lo harus edit manual.
Yang gue suka, dia kasih risk rating buat setiap tweak. Jadi lo tau sebelum apply, bukan asal pencet terus nyesel.
Fitur yang kerasa banget:
- Disable Windows telemetry, Cortana, Copilot, advertising ID
- Startup manager, lo bisa matiin semua app yang auto jalan pas boot
- Service host tuning based on RAM lo
- Custom high-performance power plan
- Keyboard latency reduction buat gaming
Dan semua reversible. Ga cocok? Balikin lagi.
Yang paling penting adalah, portable .exe. Download, langsung jalan. Ga install, ga registry sampah. Bisa di USB stick.
Dan dia open-source, bukan freemium yang nanti nagih. 2.3k stars, aktif dikembangin (commit terakhir 2 hari lalu). Support 8 bahasa termasuk Indonesia? Engga. Tapi EN, Vietnam, China, Korea, Prancis, Spanyol, Rusia ada.
Link: https://t.co/WjfhDLm30C
CCleaner Pro $40/tahun buat apa kalau ini ada.
🛠️ Deja de pagar suscripciones mensuales: 10 repositorios Open Source que reemplazan software premium
No gastes más dinero en licencias corporativas. Estos proyectos de código abierto son alternativas legítimas y gratuitas que puedes ejecutar localmente en tu propia máquina.
El arsenal definitivo:
📈 TradingAgents: Un equipo completo de analistas de IA (técnico, fundamental, sentimiento y gestor de riesgos) debatiendo y operando en tu computadora 24/7.
🔗https://t.co/jGZx3H3U59
🧠 LibreChat: Una interfaz única que unifica Claude, ChatGPT, Gemini y DeepSeek en tu propio servidor con soporte nativo de MCP.
🔗 https://t.co/qjZxGqiLeK
🎬 HyperFrames: El motor de video de código abierto de HeyGen. Genera MP4s de nivel de producción usando HTML, GSAP, Lottie y Three.js.
🔗 https://t.co/RrUVQtblgH
💼 Fincept Terminal: El clon de una terminal Bloomberg ejecutándose en tu laptop con agentes de inversión inspirados en traders legendarios.
🔗 https://t.co/Ie0QtAW2u1
📹 MoneyPrinterTurbo: Automatización de contenido. Introduces una palabra clave y genera guiones, imágenes, subtítulos, música y el video final editado.}
🔗 https://t.co/7ZjS0jJXWF
📬 Agentic Inbox: El cliente de correo inteligente de Cloudflare. Una IA lee tu bandeja de entrada y redacta respuestas sin que tus datos salgan de tu entorno.
🔗 https://t.co/HBircfkrBF
🗣️ VoxCPM: Clonación de voz avanzada. Duplica cualquier voz con solo segundos de audio o crea una desde cero con una descripción de texto.
🔗 https://t.co/ZyNbqzkOK1
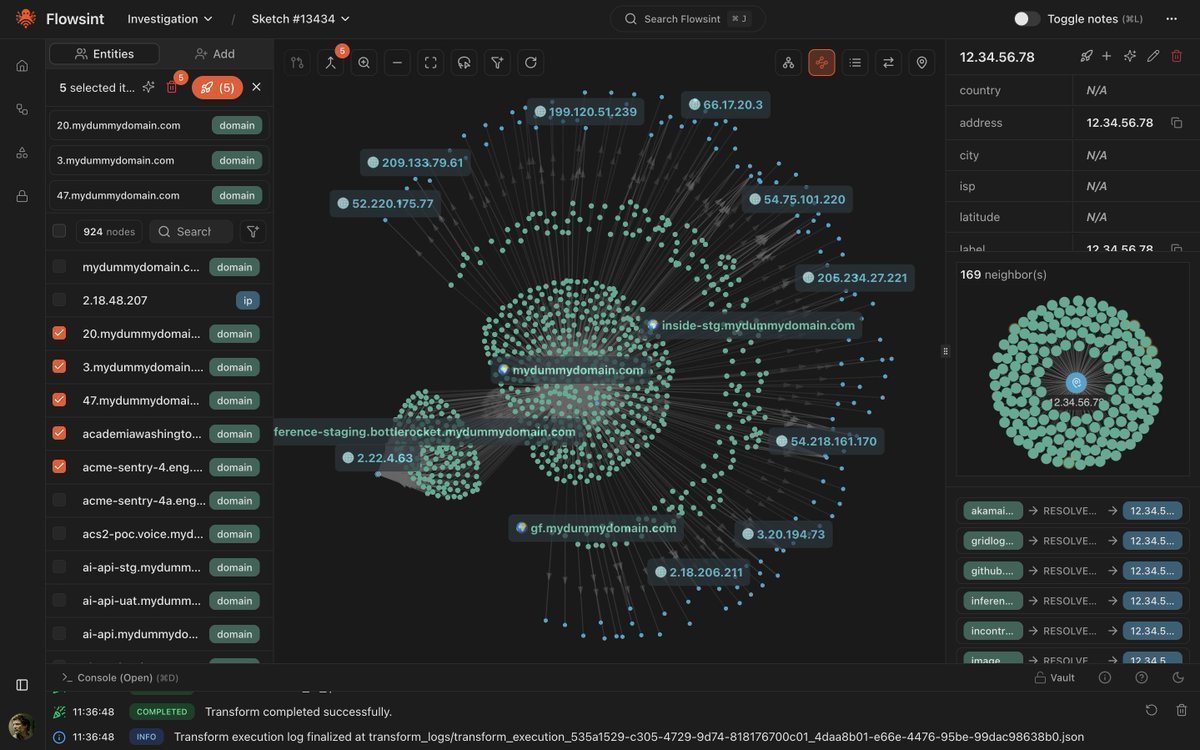
🛰️ Flowsint: Una bestia para investigaciones privadas y OSINT local. Introduces un dominio y mapea IPs, subdominios, correos y carteras cripto vinculadas.
🔗 https://t.co/ZyNbqzkOK1
💻 agent-skills: La librería de habilidades de producción para Claude Code liberada por ingenieros de Google. Cubre diseño de APIs, debugging y CI/CD.
🔗 https://t.co/SI8ZaPDcz8
🔌 Nango: La capa de integración por la que las empresas pagan miles de dólares. Cientos de APIs preconstruidas y gestión de OAuth integrada.
🔗 https://t.co/HVeU0cJ363
Entornos estables, 100% gratuitos y listos para integrarse en tu flujo de trabajo diario.
Enlaces a los repositorios en los comentarios. Guarda este post en marcadores para recortar tus gastos de software hoy mismo 🔖