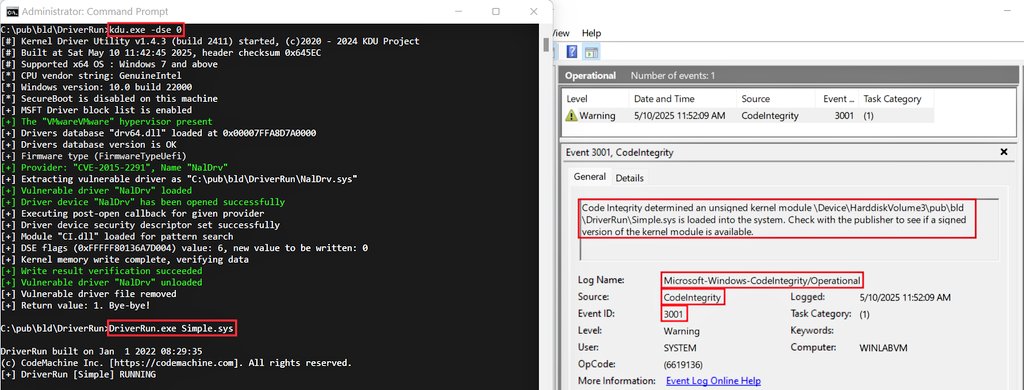
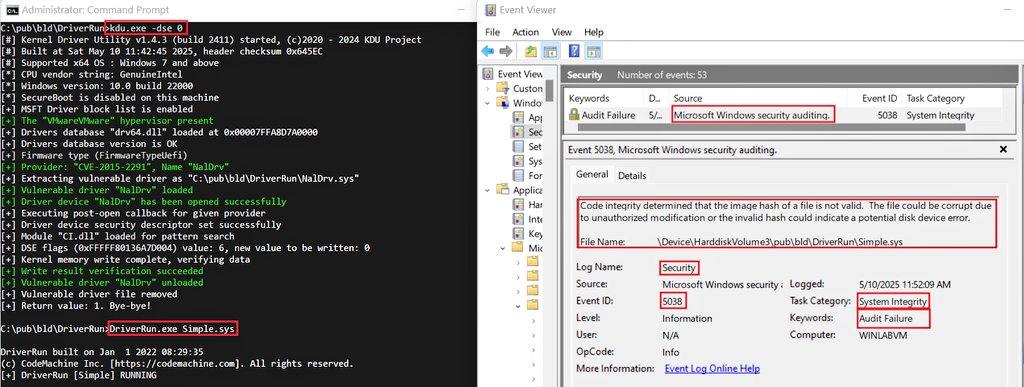
Looks like this post attracted the attention of MSRC - so just to confirm: this is not a vuln!
This is a teaser of my upcoming Secure Kernel research series, and while I did get unsigned drivers to load, it can only be done by breaking the root of trust. Not VTL 0.
That's right - an unsigned driver loaded and running with #HVCI enabled.
And the best part? The system still appears as locked down.
Article coming soon.
Wintel is coming for your SMEP bypasses!
No more flipping the U/S bit in a PTE to mark a user-mode page as supervisor-mode on Intel Arrow Lake CPUs :)
(note: this is meant for protection against speculative attacks, with the side effect of becoming SMEP 2.0)
@sixtyvividtails The threads actually aren't valid objects either! The !object command fails when given the address of an idle thread. Windows Internals also confirms this should be the case.
Getting code execution in a process that cannot be located using traditional kernel APIs and is untouchable from usermode? All while staying PatchGuard-friendly?
Sign me up: https://t.co/cbwQzuzrv9
@panchoszczcur@RiotVanguard Oh, great catch. I'll edit the article to properly list the authors. While the thread you posted is a great resource, I couldn't find any post discussing the actual hooked methods. I'm not part of any cheating circles, therefore if the info is shared on Discord, I wouldn't know.
Dug into @RiotVanguard's kernel driver's dispatch table hooks.
The article took an unexpected turn half way through, as I found some not yet documented stuff, such as the complete list of system calls hooked by the driver.
Article link:
https://t.co/LNDTAyZXz4
@panchoszczcur You make great points. Hooking ETW is certainly not a new technique, and there is multiple ways of hijacking CF via it. You sadly didn't save the rewrite in time, as I started looking Vanguard's hook right after publishing this article.
I'm sorry you didn't learn anything new.
ETW is an incredibly powerful tool in the wrong hands.
Just finished writing about how it allows drivers to hook context switches on Windows 11 24H2 while remaining PatchGuard and HVCI compatible: https://t.co/Qqq6ZLgM7t
Is it me or does it look like the crowdstrike driver is loading arbitrary binary files into kernel space and executing them?? Is csagent bypassing all security of the kernel?? The faulty file is all 00s!!
@wisdomicz@gf_256 System Informer can't do that because of Microsoft threatening to no longer sign their drivers. Look around and find the last build of Process Hacker (v3.0.4953), it doesn't yet have these restrictions.