🧊🚨 What happens when a cyberattack turns a supermarket freezer into a source of business disruption?
📦 Spoiled inventory
⏸️ Operational downtime
📉 Financial losses
The recent European retail cyberattacks show why cyber-physical security deserves attention well beyond the IT department. That’s why we’re unpacking these incidents in our upcoming webinar, examining what they reveal about unmanaged OT/IoT assets and how organizations can reduce their exposure.
📅 Thursday, November 12
🌍 10:00 AM ET | 3:00 PM GMT | 11:00 PM SGT
🔗 Save your spot: https://t.co/fG369kTTyL
#DefrostWave #CyberPhysicalSecurity #OperationalResilience
🏢⚠️ Your building’s HVAC could be the easiest way into your network.
New research from Armis Labs shows:
🔓 73% of organizations have a known exploited vulnerability in their building systems
📡 91% of systems use insecure protocols, including BACnet
🎯 Nearly three-quarters run the kind of system attackers already target
Attackers don’t need to steal data to cause damage. Shutting down elevators, badges, or climate control is enough to pressure an organization.
Learn more from @FacilitiesDive's coverage of our latest Armis Labs report: https://t.co/7i8hZCBofC
You can access the Armis Labs report directly at: https://t.co/YpWShoRjwy
#OTSecurity #BuildingSecurity
🏢🔓⚠️ Is your building automation system secure? Because 91% of them run on protocols that assume networks don't exist.
🏥 A recent ransomware attack forced a hospital to choose between patient care and their access control system.
▶️ Our new Armis Labs report breaks down the real risks—and how to get ahead of them. Read the full findings → https://t.co/YpWShoRjwy
#BuildingAutomation #Cybersecurity #AssetSecurity
🔍 Security data is only useful when it connects to the work your teams already do.
That is why Armis integrations enrich data – providing teams with a one-stop shop, overcoming the need to jump between solutions.
#ShiftZero starts with connected visibility.
#GartnerPeerInsights
🤖 AI agents already outnumber humans in most organizations by up to 100 to 1. Most security teams can't account for all of them.
🎙 Join @OmdiaHQ Principal Analyst Theresa Lanowitz and our team of security experts for a fireside chat on securing assets and identities in the AI agent era — closing visibility gaps, governing non-human identities, and stopping rogue agents before they cause damage.
🔗 Register now: https://t.co/okWNYVxmqV
#Armis #ServiceNow #CyberExposureManagement #AIAgents #NonHumanIdentity
🚨 Two critical PHP vulnerabilities have been disclosed, and affects a huge share of the web.
🔓 CVE-2026-109618 and CVE-2026-109619 are remote code execution flaws, each rated 9.2 on CVSS v4.0. Attackers could run commands on a server, steal data, or take over a site. The PHP security team released emergency updates on October 21 at 14:00 UTC.
🌐 PHP powers CMSs, shared hosting, control panels, and many apps that never mention it. The first challenge is visibility: knowing where PHP runs, including inside vendor software and appliances.
Patches are confirmed, focus on three things:
▶️ Find every PHP installation
▶️ Patch internet-facing systems first
▶️ Identify end-of-life PHP versions that may not get a fix
⏱️ Continuous visibility turns a days-long scramble into hours. Michael Freeman and Guy Broder’s full analysis and the steps to take now: https://t.co/L2nNxijBN6
#Cybersecurity #PHP #VulnerabilityManagement #Armis
🔍 One platform for the work security teams do every day.
Asset visibility, risk management, and daily cyber operations in one place.
#ShiftZero starts with knowing what you have.
#GartnerPeerInsights
73% of organizations have known exploited vulnerabilities in their Building Automation Systems (BAS). Even worse? 91% of BAS communicate over insecure protocols.
As facility networks converge with enterprise IT and cloud environments, smart HVAC, lighting, and access control systems are becoming prime entry points for lateral movement and ransomware.
Our research team analyzed real-world cyber-physical threat data to reveal:
⚡ Why 28% of vulnerabilities are exploited the exact same day they hit CISA’s KEV catalog
🔍 Over 4,200+ active CVEs that aren't captured in standard databases
🛡️ Practical ways to isolate and segment high-risk systems without causing operational downtime
Stop guessing your exposure. Read the new research from Armis Labs to protect your physical operations before attackers strike: https://t.co/YpWShoRjwy
#CyberPhysical #BAS #ThreatIntelligence #Armis
🤖⏰ Application security needs a new foundation—one that closes the window attackers depend on.
➡️ Discover why defense needs to move earlier—Shift Zero explained: https://t.co/JNgezWQ0l3
#ApplicationSecurity#ShiftZero#Armis
🤝 Asset intelligence. Identity security. Workflows that actually fix problems.
None of this works without the right partners. Hear from our alliance team and the incredible ecosystem of partners who we are building unified security outcomes with, together — @illumio and @Fortinet among them.
That's Partner First in action.
Our thanks to Christer Swartz, Illumio, and Michael Smiley, Fortinet.
📸 And to our Armis partner team:
Joel Churcher, Director Marketing, Strategic Alliances
Patrick McCue, VP Sales Executive, Alliances & Channel
Matthew Courchasne, Senior Director, Alliances and Channel Ecosystem
Lindsay Medeiros, Senior Director, Global Partner Marketing
#Armis #PartnerFirst #Partnership #BlackHat2026
🔍 Three organizations, three reviews, one common thread: asset discoverability is the foundation of modern cybersecurity.
From IT/OT/IoT environments to shadow hardware to governance roadmaps—Gartner Peer Insights reviewers are validating what we know: you can't secure what you can't see.
🔒Shift Zero starts here. Swipe through to see the full arc.
#GartnerPeerInsights
🤝 Partner-first isn't a tagline — it's how Armis operates.
When the security community comes together at major industry events, our partners are right there with us: on the floor, at every presentation, and in every conversation.
Thanks to our partners who joined us last month at Black Hat 2026. We are proud to show up with our ecosystem, not alongside it.
Demi Ben-Ari, @panorays
Evgeniy Kharam, @DiscernSecurity
Yiannis Vassiliades, @zscaler
Kobi Shetret, @sygnia_labs
Matt Wyckhouse, @FiniteStateInc
#Armis #PartnerFirst #Partnership #BlackHat2026
🏥 When patient safety is at risk, a patchwork approach to medical device security is indefensible.
🩺 That’s why healthcare organizations are closing their medical device visibility gap with Armis — unlocking end-to-end visibility and threat detection across their entire medical device infrastructure.
👉 See why CISOs and security leaders are making Armis their single point of truth.
Learn more: https://t.co/xZ3WvwEiXS
#Armis #MedicalDeviceSecurity #HealthcareCybersecurity #DeviceVisibility
⚡ Earlier this year, we were named a Leader for the second consecutive year in the 2026 Gartner® Magic Quadrant™ for CPS Protection Platforms.
Today, we feel that recognition carries even greater significance as CPS Security becomes a foundational pillar of @ServiceNow's Autonomous Security portfolio and our #ShiftZero vision.
We believe it reinforces the strength of our approach to securing complex operational environments: combining deep asset intelligence, cyber exposure management, AI-powered analysis and governed action to help organizations move beyond visibility toward proactive security.
Learn why we are a Leader and get the report: https://t.co/ZKijWpiTrp
#Armis #ServiceNow #Cybersecurity #OTSecurity #CPS #GartnerMagicQuadrant
⚙️ Operational technology demands security built for cyber-physical realities—not enterprise IT tools adapted for the plant floor. Here’s why: https://t.co/xgz1HeKziJ
@ServiceNow's full Autonomous Security portfolio, announced at Black Hat USA 2026, placed Cyber-Physical Systems (CPS) Security front and center. Nadir Izrael, ServiceNow’s GVP for Cybersecurity and Risk Products, explains how this delivers:
◾ 𝐀𝐮𝐭𝐨𝐧𝐨𝐦𝐲 𝐰𝐢𝐭𝐡 𝐂𝐞𝐫𝐭𝐚𝐢𝐧𝐭𝐲: Leveraging AI-driven exposure management without forfeiting operational control over critical physical assets.
◾ 𝐏𝐫𝐨𝐚𝐜𝐭𝐢𝐯𝐞 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐯𝐢𝐚 𝐒𝐡𝐢𝐟𝐭 𝐙𝐞𝐫𝐨: Moving beyond fragmented visibility tools toward continuous, governed risk prevention.
◾ 𝐏𝐫𝐨𝐯𝐞𝐧 𝐎𝐩𝐞𝐫𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐈𝐦𝐩𝐚𝐜𝐭: Connecting asset intelligence directly to operational workflows to deliver up to 90% faster incident resolution.
📖 Read Nadir’s blog via the link above to take a deeper look at the future of CPS security.
#OTSecurity #CPSSecurity #Cybersecurity #AutonomousSecurity #ServiceNow #Armis
😈 𝐀𝐭𝐭𝐚𝐜𝐤𝐞𝐫𝐬: AI-powered. Scalable. Moving in seconds.
🛡️ 𝐃𝐞𝐟𝐞𝐧𝐝𝐞𝐫𝐬: Reactive. Backlogged. Measuring response time in days.
This asymmetry isn't new—but the speed is.
Nadir Izrael, ServiceNow’s GVP for Cybersecurity and Risk Products, explains why hand-to-hand response does not work when your adversary operates at machine velocity. You need a different stance entirely. Not wait and detect. But instead:
Proactive. Preventative. Autonomous.
That's 𝐒𝐡𝐢𝐟𝐭 𝐙𝐞𝐫𝐨: the methodology of handling security threats like 'zero inbox'—as close to detection as possible, eliminating exposure before it creates risk.
Watch Nadir’s full conversation with Dave Gruber from Omdia, hosted by BrightTALK: https://t.co/fvbOofim3z
Access our latest research into the gaps created by traditional response times, and how we’re closing them with intelligence-driven detection: https://t.co/rkx7zO8z2j
#ShiftZero #VulnerabilityManagement #ThreatDetection #AICenterForCyberDefense
Vulnerability scans don't work anymore. Here's why:
🗓️ Scheduled scans = Every 4-6 weeks.
⏱️ AI-powered threats = Hours to minutes.
Traditional periodic scans leave you blind between cycles—and that's where attackers live.
🔗 Read our latest blog to discover how intelligence-driven detection replaces the vulnerability scan trap: https://t.co/rkx7zO8z2j
#VulnerabilityManagement #ThreatDetection #CTEM #Armis
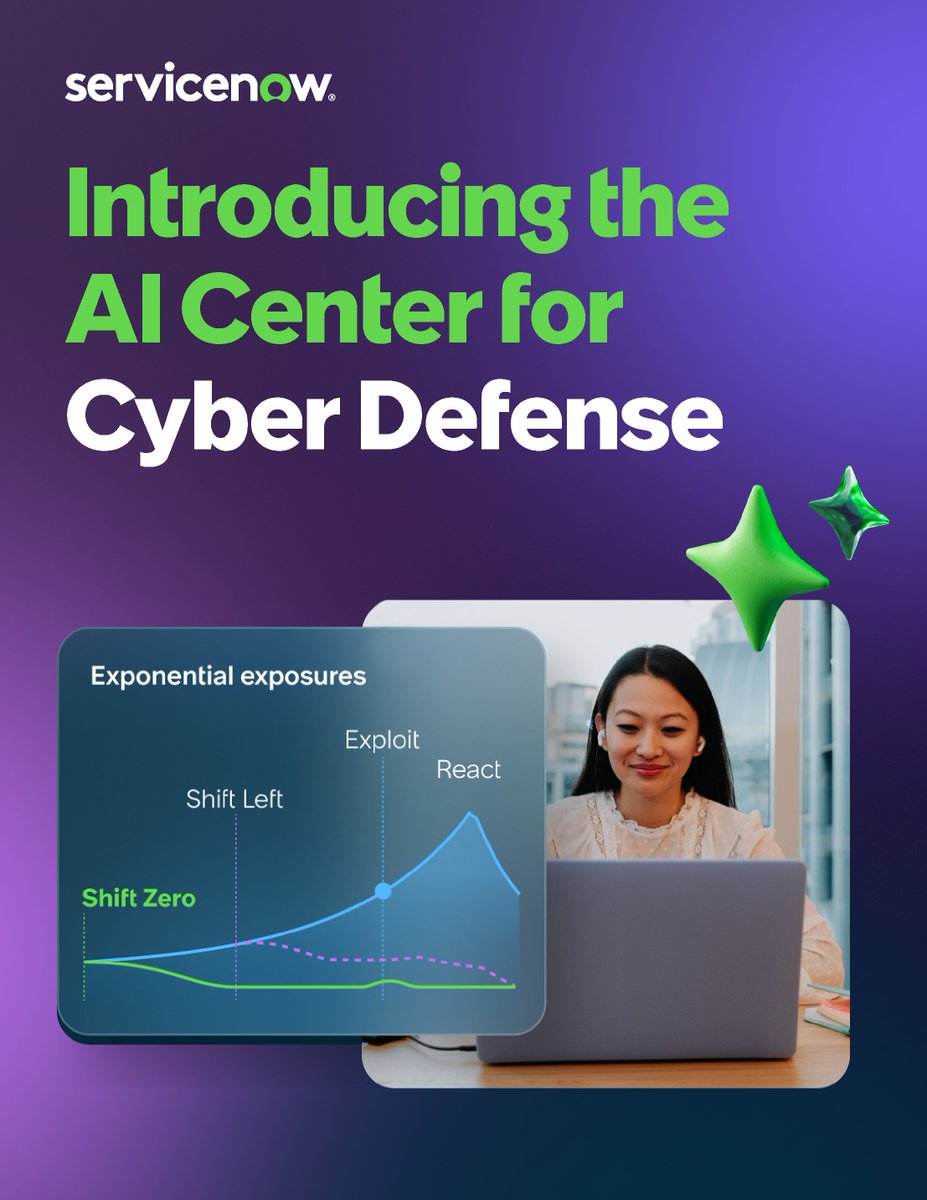
Introducing the AI Center for Cyber Defense, @ServiceNow's new global engine led by Nadir Izrael and built to pioneer the industry's shift to true autonomous, agentic defense.
Adversaries weaponizing AI move in seconds. Legacy controls — and legacy defense models — can't keep up. Enterprise defense requires a complete reset. That's what this center is built to pioneer.
Learn more: https://t.co/7fpV9OxrTq
#AICenterForCyberDefense #AgenticDefense #BlackHat2026
The legacy security model needs to evolve for the infinite threat landscape. Learn how your security peers are keeping up. Read the report. https://t.co/HHxUSneG1E
🏥🩺 When patient safety and regulatory compliance collide, asset visibility isn't optional - it's essential.
Fondazione IRCCS Policlinico San Matteo faced a critical challenge: align with NIS2 requirements while managing thousands of connected medical devices across their facility. The solution? Complete asset visibility.
With Armis Centrix™, San Matteo achieved:
✓ 100% visibility of all managed and unmanaged connected assets
✓ Real-time vulnerability prioritization that actually makes sense
✓ Reduced device downtime = more examinations completed for patients
In healthcare, better security doesn't just reduce risk - it improves care.
🔗 Read the full case study: https://t.co/45MrDWFl3J
#Armis #MedicalDeviceSecurity #NIS2Compliance #CyberExposureManagement