Day 30 -31 of learning cybersecurity
I learned the basics of how a SIEM works, including how logs are collected, indexed, and searched for analysis
#day31oflearningcybersecurity
NETWORKING KNOWLEDGE CHECKPOINT
During the TCP three-way handshake, which sequence is correct?
A. SYN → ACK → SYN-ACK
B. SYN → SYN-ACK → ACK
C. ACK → SYN → SYN-ACK
D. SYN-ACK → SYN → ACK
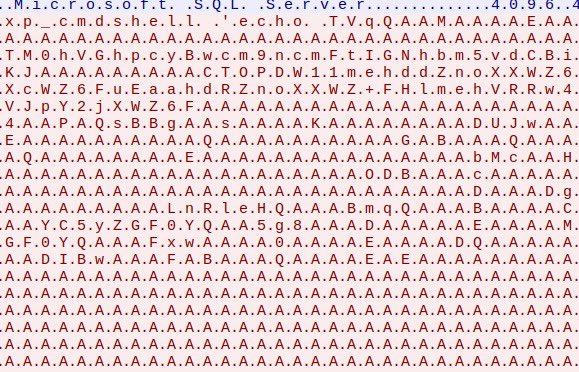
I identified the source IP responsible for potential port scanning activity and extracted the targeted username and password from the captured traffic.
#day29oflearningcybersecurity
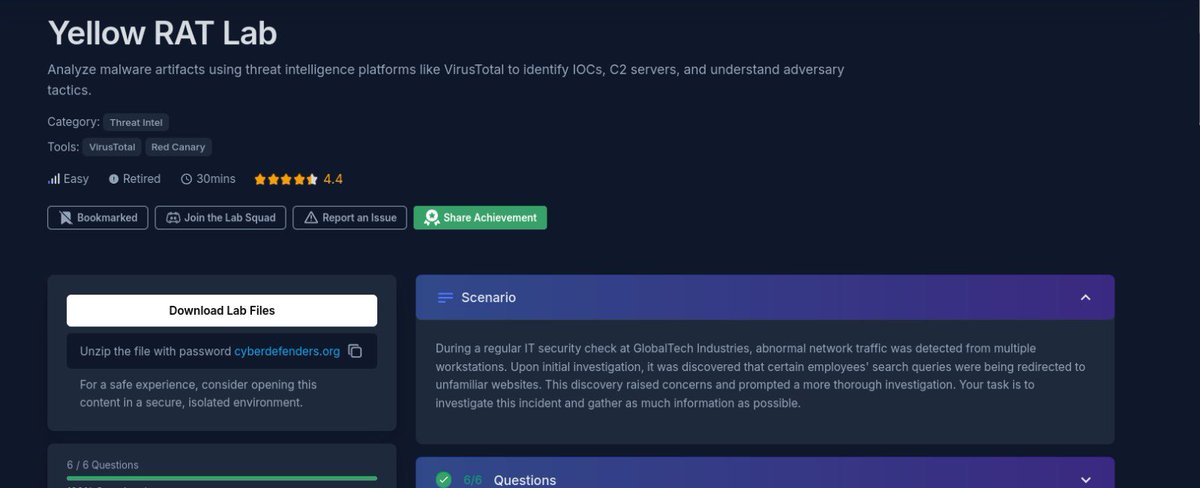
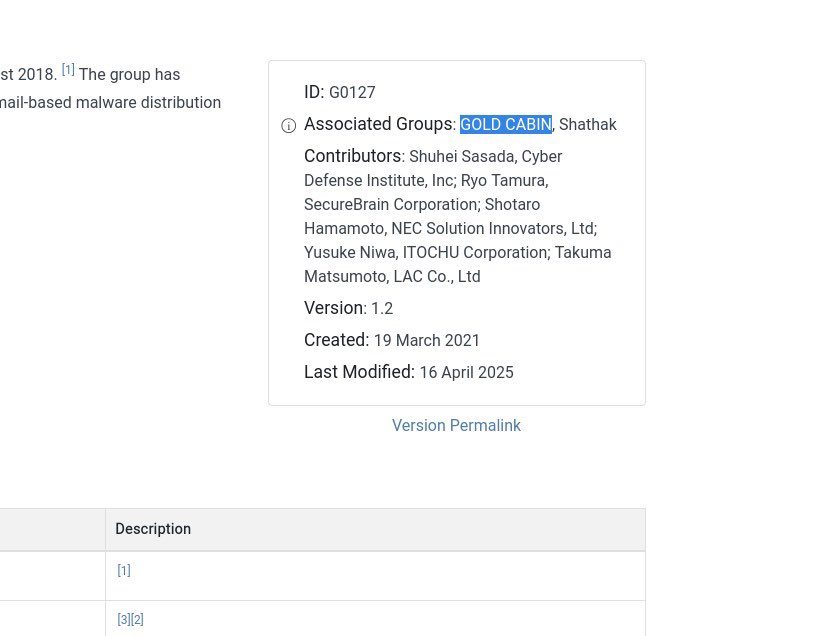
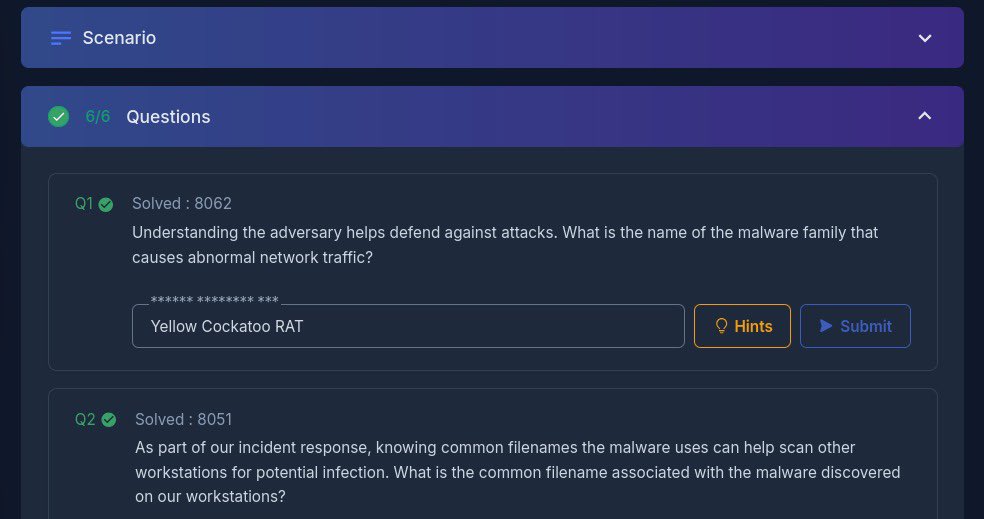
I investigated how the malware operates on a compromised system, including how it establishes remote access maintains persistence and communicates with its command and control server
#day28oflearningcybersecurity
Tomorrow is Thursday.
Fast if you are able to, if not earn reward by reminding others.
Remind, for indeed, the reminder benefits the believers (Q51:55).
Baarakallahu Feekum.
I explored how security analysts monitor systems, investigate alerts and respond to potential threats. The lab gave me practical aspect of how a SOC operates, including analyzing suspicious activities and making decisions based on available data.
#day27oflearningcybersecurity
If you’re a Muslim and this appears on your timeline, please retweet. It might be the reminder someone needs to complete their solat. May Allah accept it from us.
Day 27 of learning
I learned the key stages of handling a security incident from identification,containment to eradication and recovery.
#day27oflearningcybersecurity
Day 26 of my cybersecurity learning
I did introduction to logs on TryHackMe. I learned what logs are, why they are important, how they help in monitoring and investigating system activities.
#day26oflearningcybersecurity
Day 25 of my cybersecurity learning
I was did introduction to malware on TryHackMe. I learned the basics of what malware is, the different types, and how they behave on a system. The exercise also introduced how analysts begin examining suspicious files
#day25oflearningcyber
Day24oflearningcybersecurity
I worked through how phishing emails are crated and how attackers use them to trick users into clicking links.I also learned how to analyze these email by checking links and attachments that reveal they are malicious
#day24oflearnigcybersecuriy
Day23oflearning
I analyzed a malicious file used during an initial access scenario
I identified the IP address attacker used to gain access, the process and extracted the it’s sha256
#day23oflearningcybersecurity
I did Xworm lab on cyberdefender today and it is all about analyzing a malicious file from a phishing attack but unable to finish it
We go again tomorrow
#day22oflearningcybersecurity
I worked on a phishing investigation lab in cyberdefender
I analyzed the email headers to trace sender Ip, investigated malicious link and the hosting Ip,analyzed malware behavior and the requested URL and identified the C2 domain and telegram Bot
#day21oflearningcybersecurity
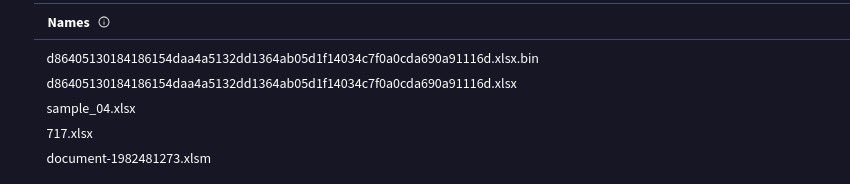
I was given a file hash and had to investigate the malware behavior and related activity using threat intelligence tools(virustotal)
I worked on identifying the file name associated with the given hash and found the name of a GIF files.
#day20oflearningcybersecurity