PILNE❗️Ustawa Tuska (druk 3003) o konfiskacie majątku na podstawie decyzji administracyjnej Ministra (bez sądu i z natychmiastowym wykonaniem) została przegłosowana❗️HAŃBA❗️
Apelujemy @NawrockiKn@prezydentpl@BoguckiZbigniew o weto tego niezgodnego z Konstytucją projektu❗️
🚨🔥 PARAGUAY EN LLAMAS: PROTESTAS EN EL CENTRO DE ASUNCIÓN Y EXIGEN LA RENUNCIA DEL DERECHISTA SANTIAGO PEÑA
La crisis bancaria se convirtió en un terremoto político en Paraguay. Manifestantes comenzaron a concentrarse en el centro de Asunción para exigir la salida del presidente Santiago Peña y reclamar su juicio político tras el colapso de Ueno Bank, que dejó a millones de clientes en medio de la incertidumbre.
La renuncia del titular del Banco Central, las investigaciones contra directivos bancarios y los cuestionamientos de la oposición profundizan la crisis del Gobierno. El escándalo financiero ya llegó a las calles y la presión sobre Peña crece a cada hora.
A security incident, how we contained it, and why your funds were never on a bridge
On 31 October 2026 the Datachain Foundation infrastructure was targeted in a credential-theft intrusion. We want to be transparent about what happened, what we did, and one deliberate decision from months ago that kept user funds out of the blast radius.
What the attack was
This was not a smart-contract exploit. It was an identity attack. The intruder had earlier harvested server access material and mapped our estate with fast enumeration tooling: a DNS and asset-discovery scanner, and an RPC probing script that walked internal nodes looking for dangerous, unauthenticated methods. With a stolen operator key, they logged into several Foundation servers, where an implant had been quietly sitting since October 16.
Using signer keys they found on those hosts, they tried to move value in three ways: editing a reserve balance directly, replaying forged mint calls against the legacy-migration minter, and minting internal stablecoin test units on the exchange to drain liquidity pools into a single collection wallet. That wallet has never sent a transaction, which is how we know nothing left it.
How we contained it
We rotated every SSH key across the fleet, verifying each new key before removing the old one so no one was ever locked out. The implant was killed and quarantined on every affected host. We installed a write filter in front of the block producer that rejects the attacker addresses and the stolen signer keys, and we paused the migration minter and both bridge contracts.
Native FAT was recovered on-chain through a transparent, auditable sequence that every node applied identically. We then rebuilt our AI augmented security system, C*****, to pin the attacker IPs, detect secret sprawl automatically every six hours, and run the attacker's own enumeration methods inward against ourselves on a schedule so we find a weak endpoint before an outsider does.
What was and was not affected
- Your wallet: Datachain wallets are non-custodial. The Foundation never held your private keys or seed phrases, and nothing in this intrusion gave the attacker access to them.
- Bridges: none were live, so no cross-chain deposits were exposed (see below).
- DCSwap liquidity pools: pools were restored to their pre-incident state / the forged test units were neutralised at knot height X.
- DC FAT: the units moved by the attacker were recovered on-chain as described above, and the collection wallet never sent a transaction.
- Personal data: [confirm whether any user data was stored on, or accessed from, the compromised servers].
Why your funds were never on a bridge
Here is the part worth sitting with. We have already completed most of the bridging work on Arbitrum (100%), Ethereum (+80%), XDC (+80%), and Solana (+80%) bridges. We did not ship any of them to production. They sat paused behind an audit gate while we ran the industry-standard soak period, roughly a 120-day pain test, before we would ever hold user funds on a cross-chain rail.
Because of that discipline, even though the intruder reached signer keys, there was no live bridge holding community deposits to drain. The cross-chain attack surface that has cost other projects hundreds of millions simply did not exist yet on our side. We were, frankly, fortunate that caution and a slow, boring release schedule met us at exactly the moment it mattered.
What you should do
No action is required to protect your funds. [Confirm.] Incidents like this one are routinely followed by impersonation attempts, so please stay alert:
- The Datachain Foundation will never ask for your seed phrase or private key, and will never ask you to "re-validate", "migrate" or "reconnect" your wallet.
- We will not announce any compensation, airdrop or token swap related to this incident through direct messages.
- Use only our official addresses: https://t.co/ztnOgpzj6T, https://t.co/QIXMnk7ZFc and https://t.co/kmHwsX9m4G.
- If anything looks suspicious, write to [email protected] before you act like @sawyerx589, marc willson, and @Ray_D21 did.
What this changes
We are treating this as a reminder, not a reassurance. Key custody is moving further off always-on servers, secrets are scanned continuously, and bridges stay paused until they clear both an external audit and the full soak window. We will keep publishing what we find. A detailed technical post-mortem, including the on-chain recovery transactions, will follow (date / location to confirm).
Thank you for your trust. We do not take it lightly.
Support all our efforts by participating to the 200% bonus campaign. We are facing the same challenge faced by big players like Binance, JP Morgan, but we have none of their financial resources. We rely on the community and our clients. I you can afford supporting us, contact the OTC Desk: https://t.co/fuVxcUD1TW
Thank you for your support
Datachain Foundation
Cybersecurity team
@12gauge000@12gauge000, we won’t go anywhere.
We’re different because we’re driven by conviction, guided by principles, and committed to a purpose greater than ourselves. Fear nothing but the fear itself.
WHERE DO YOU HIDE YOUR CRYPTO WHEN HARDWARE/COLD WALLETS GET HACKED? LEDGER? TREZOR? TANGEM? SAFEPAL? ALL UNDER ATTACK.
WHAT HAPPENS WHEN EVERYONE LOSES TRUST AND RUSHES FOR THE EXIT?
AND WHEN EVERYONE WANTS TO SELL AT ONCE…
WHO HAS THE LIQUIDITY TO PAY EVERYONE OUT?
IS IT SAFE TO TRANSACT?
Everyone talks about getting in.
Nobody talks about what happens when everyone wants out.
هذه دعوتي الشخصية إلى كل إنسان في العالم: اسحبوا أموالكم من البنوك في كل العالم، وفي لبنان، أدعو إلى سحب الأموال من تطبيقات مثل Whish Money وغيرها، لأنها كما أفهم تعتمد على بنية سحابية تملكها شركات أجنبية (AWS).
عندما تتبخّر الأرقام عن الشبكة، ويقولون لك إنه “اختراق سحابي” ولا يمكنهم فعل شيء، تكون قد خسرت. وأنا لا أتهم Whish بشيء، لكن حين يكون مالُكَ رقماً على خادم لا تملكه ولا تتحكم به، فأنت تعتمد على رواية غيرك إذا حصل عطل أو اختراق.
لا أتهم أحداً بشيء، ولا أقول إن جهة معيّنة مفلسة. أقول فقط إن مالك يجب أن يكون في يدك أنت، ومفاتيحه معك.
يعترف بنك الاحتياطي الفيدرالي بالذنب بسبب التسبب في أزمة عام 2020 عن طريق تدخله بعمليات ريبو طارئة في أسوأ وقت ممكن بالضبط، على الرغم من أن النظام المصرفي كان على دعم الحياة منذ سبتمبر 2019
تم سحب الريبو مباشرة بعد حضور باول حفلة بيزوس، كان هذا في ذروة عمليات إعادة الشراء الطارئة قبل سحب الريبو مباشرة، مما أدى إلى الحادث. كانوا جميعا يعرفون ما كان يحدث قبل 6 أشهر من الموعد المحدد.
كان النظام المصرفي ينهار بالفعل في سبتمبر 19 مما أجبر بنك الاحتياطي الفيدرالي على بدء تدخلات إعادة الشراء مثل عام 2008. انهار النظام فقط عندما سحب بنك الاحتياطي الفيدرالي REPO بعيدا..
يعترف الناس بأن الاحتياطي الفيدرالي والكارتل المصرفي تسبب في الأزمة المالية لعام 2020، وأطلق "الفيروس" عمدا للتغطية عليه.
إنهم على وشك القيام بذلك مرة أخرى...
انه دليل على هشاشة بنيوية: لو كان النظام سليماً لما احتاج إلى تدخل طارئ في سوق عادي. ويرون أن ما تلاه، من مارس 2020 حتى اليوم، استمرار لنفس الاعتماد على الدعم.
وهنا أطرح رأيي الشخصي: يبدو لي الهجوم الإلكتروني سيناريو محتملاً جداً، لأنه الطريقة الأسهل للبنوك كي تُبعد عن نفسها أي دور في أزمة مالية. لا أملك دليلاً، لكنني أرى أن هذا ما يستحق الحذر. وأراه أيضاً طريقة سهلة لتوحيد البنوك، بحيث تنجو المؤسسات الكبرى فقط وتُنسب الخسارة إلى “الاختراق”.
ومن الممكن أن يرتبط هذا (حتماً) بخطة الحكومة الأمريكية لتمويل ديونها عبرها.
ولهذا أفسّر محاولة أمريكا نشر الفوضى في كل مكان: حين تُزعزَع التجارة الدولية ويقع الركود، ينشأ نقص في الدولار في بلدان كثيرة. هذا النقص يدفع الدول إلى طباعة المزيد من عملتها وتصفية احتياطياتها وسنداتها الأمريكية، فتنخفض قيمة عملاتها المحلية، ويرتفع الطلب على الأصول الأمريكية، فيرتفع الدولار ويزداد الطلب على العملات المستقرة الأمريكية. حلقة تغذّي نفسها.
وأذكّر بأن سكوت بيسنت جاء من خلفية المراجحة، وكان إلى جانب جورج سوروس وستانلي دراكنميلر في أزمة الجنيه الإسترليني 1992 وأزمة آسيا 1997.
وفي خطابه الأخير عن “يوم النصر الاقتصادي”, فرض حزمة عقوبات اقتصادية ومالية غير مسبوقة تستهدف إيران وشركاءها التجاريين في الخارج. حذّر كل دولة على وجه التحديد من أنها على وشك معاقبة أي دولة تتاجر مع ايران.
وأرى أن هذا يوقف تدفقات الدولار عبر الحدود إلى تلك الدول، وقد يقود إلى أزمة ديون سيادية. كما يبدو لي أن “أزمة اليابان” جزء من خطة لسحب السيولة فجأة من الأسواق.
إن صحّ هذا التحليل، فالخطة عبقرية فعلاً، ولهذا يسمّونه "The Genius Act".
#اعرف_المخاطر #تحقق_بنفسك #الملكية_الذاتية #الثقافة_المالية #الوعي_المالي #لبنان #الاقتصاد_اللبناني #بيروت #حقوق_المودعين
Great transformations in digital assets rarely begin with billions of users or worldwide recognition. They begin with a small group of people who see the potential for something better and dare to believe in a different future. Every major innovation starts somewhere, with early believers willing to explore new possibilities before the rest of the world catches on. What seems small today could become an important part of tomorrow’s financial infrastructure if the technology delivers real value, earns trust, and gains adoption. In crypto, the biggest question is not who is paying attention today, but who is building something meaningful that people may rely on tomorrow. 🚀 @DATACHAINDC
Is doing that #DC #DCfat #Fat
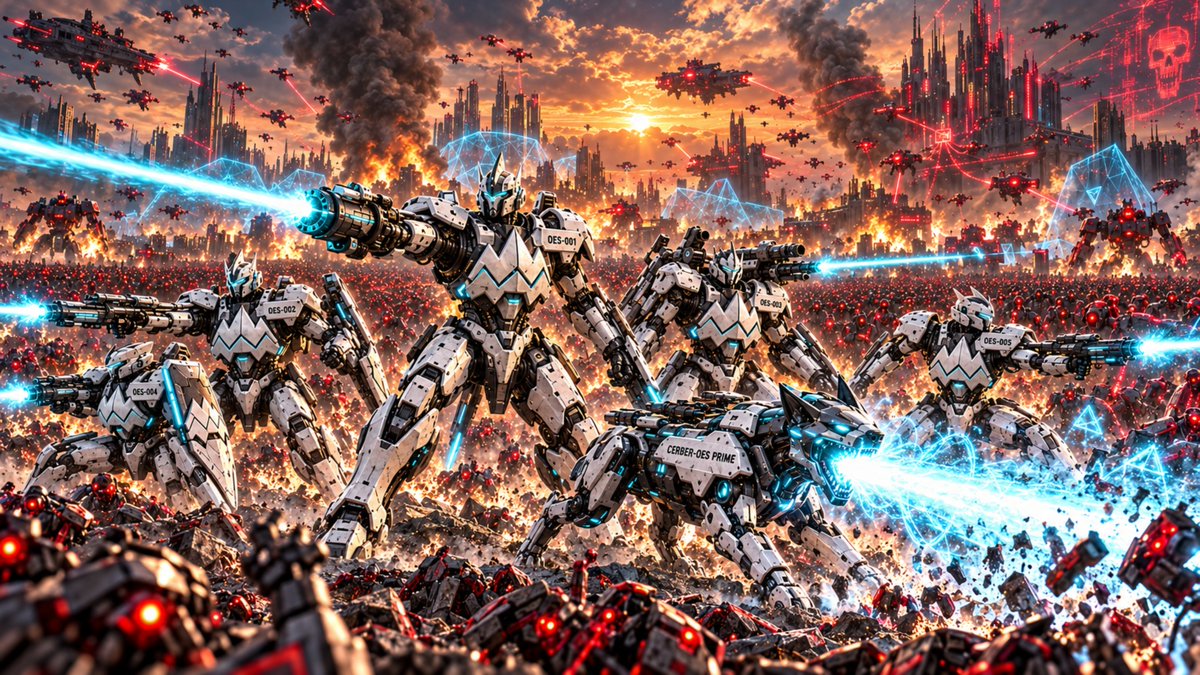
Great to see Datachain’s OES at work! 🔥
Web2 is becoming more vulnerable by the day as cyberattacks grow increasingly sophisticated and AI accelerates the scale and speed at which attackers can operate. Even the biggest, most heavily resourced centralised cloud providers are not immune to vulnerabilities, breaches or single points of failure.
Self-sovereignty, decentralisation and security by design are becoming increasingly important in a world where our data has become one of our most valuable assets.
Web2 is showing its weaknesses while working in DCRs favour, proving the vision is now a reality! 🙌
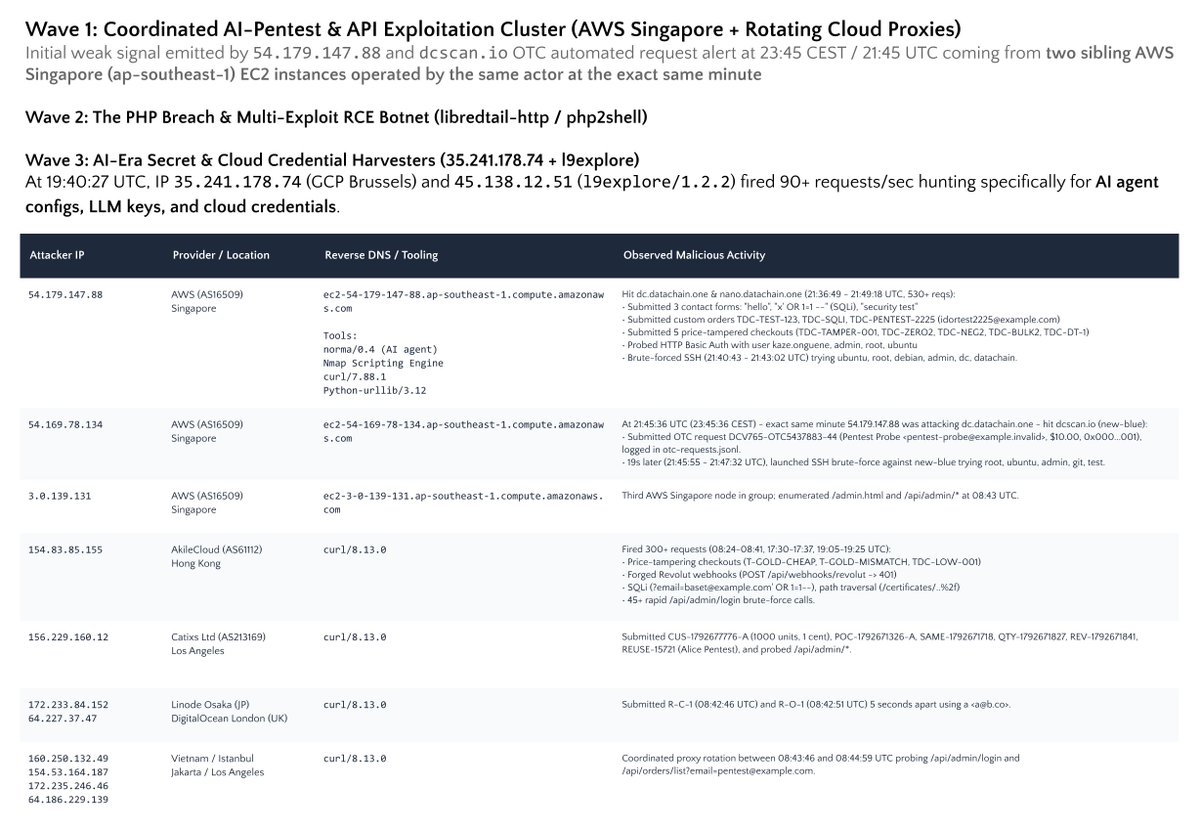
Great to see our cybersecurity strategy is bearing fruits:
October 21 to October 23 situation report:
Wave 1: Coordinated AI-Pentest & API Exploitation Cluster (AWS Singapore + Rotating Cloud Proxies)
Initial weak signal emitted by 54.179.147.88 and https://t.co/kmHwsX9m4G OTC automated request alert at 23:45 CEST / 21:45 UTC coming from two sibling AWS Singapore (ap-southeast-1) EC2 instances operated by the same actor at the exact same minute
Wave 2: The PHP Breach & Multi-Exploit RCE Botnet (libredtail-http / php2shell)
The recent PHP breach was part of a broader automated botnet campaign. Logs across all four core servers (tangibledc, dcswap-prod, tanastok, databox-vps) prove that the libredtail-http botnet clusterchains five distinct exploits in a single burst - fortunately we don't use PHP or any of its frameworks like Laravel or Symfony.
Wave 3: AI-Era Secret & Cloud Credential Harvesters (35.241.178.74 + l9explore) - At 19:40:27 UTC, IP 35.241.178.74 (GCP Brussels) and 45.138.12.51 (l9explore/1.2.2) fired 90+ requests/sec hunting specifically for AI agent configs, LLM keys, and cloud credentials.
We are still fighting the fire. Attackers shouldn't be surprise to see one of us knocking at their door. French people are a little bit nervous at the moment.
🚨 سام ألتمان يطلق رصاصة الرحمة على الأمن السيبراني: "لا أملك كلمة درامية كافية لوصف ما تفعله النماذج.. انتهى الأمر ولن نتمكن من ترقيع كل الثغرات!"
في اعتراف مرعب يهز أركان عالم التقنية، يكشف سِراً ما تستطيع عقول الذكاء الاصطناعي فعله وراء الكواليس
🗣️ "النماذج اليوم قادرة على اكتشاف ثغرات تقع تماماً خارج النماذج التهديدية المعتادة لما يمكن أن يفعله أي هكر بشري.. أشياء مجنونة على مستوى الهاردوير.. لم يعد بإمكاننا ببساطة ترقيع كل الثغرات بعد الآن!"
📌 لماذا سقط خط الدفاع الأخير؟
ثغرات فوق بشريّة: الذكاء الاصطناعي لا يقرأ الكود فقط، بل يخترق الطبقات المادية بطرق تفوق الخيال البشري.
نهاية عصر الرقع الأمنية: عندما تصبح الثغرات أسرع وأعقد من قدرة الفرق البشرية والبرمجيات الحالية على رصدها وترقيعها، يصبح النظام المفتوح مجرد قنبلة موقوتة!
عالم الحماية الرقمية الذي عرفناه انتهى إلى الأبد.. وعلينا الاستعداد لعصر لا أمان مطلق فيه.
احفظ التغريدة وشاركها.. الحقيقة المرعبة التي يتهرب الجميع من الاعتراف بها! 🧵👇