Google Mantis is a skills pack for security review with coding agents
Install:
npx skills add google/mantis
Key commands:
/mantis-threat-model: builds a threat model from your codebase
/mantis-researcher: scans for vulnerabilities
/mantis-review: filters false positives
/mantis-reproduce: writes a PoC and runs it in a sandbox
/mantis-patch: applies a fix and confirms it blocks the PoC
/mantis-report: generates the final security report
This is a good use case for running your agent in a sandbox, since the reproduce and patch steps execute generated code
https://t.co/OhmZDDNcWy
Introducing PageBreak, an agentic vulnerability discovery tool using deterministic validation to achieve a near-zero false positive rate.
How it works: https://t.co/n3k4vvNhoq
For real-world vulnerabilities PageBreak has discovered 👇
https://t.co/0pZ5rWoWw2
🤯 Someone has released a dataset with over 23,000 smart contract security audit findings, free to download
Severity, proof of concepts, recommended fixes, everything is inside - it's a GOLDEN MINE. Thank you @RightNowIn - amazing contribution🔥
https://t.co/ejmuCuCkRK
Codetective 0.9.3 released - added 'crack mode' to automatically try encodings, classical ciphers and chains of them and ranks the candidates by how much they look like real text or a CTF flag. https://t.co/H74SyQC3Ef
🚀 OSWatcher is finally out !
https://t.co/i41RlgPfH8
docker compose up -d
And open http://localhost
⚡️Web UI, GraphQL API and Neo4j, all running locally
👉2,4GB Windows/Ubuntu graph corpus included
Download requests for Windows binaries forwarded to Winbindex @m417z 👏
Containers are no longer a security boundary.
Over the past few months, we’ve seen a crazy amount of Linux kernel vulnerabilities and exploits. This has forced us to rethink the security of infrastructure that relies heavily on the underlying kernel, especially containers.
As models become more capable, the barrier to escaping a container has fallen so much that adversaries can now generate working kernel exploits in a single shot. CVE-2026-80521 is one such example. We discovered it using dfs-large1 from @depthfirstlabs and generated the exploit in one shot with GPT-5.6 Sol. The exploit still works on the latest Ubuntu 26.04 release because the fix has not yet been backported.
Read our full writeup: https://t.co/ZFSQCMCN73
Full devirtualization of VMProtect (Ultra mode + high complexity + multiple instances): jump tables (switch stmts), conditionals and loops. Plus working recompilation.
All updates in discord - https://t.co/r2kA7f56fS
Credits: mr. UJ, Ivan Permyakov, Gogi, unrustled.jimmies
Do you want to learn how to fuzz like a real expert, but don't know how to start ?
If so, this is the course for you!
10 real targets, 10 exercises. Created by github staff member.
Github:- https://t.co/wtW5l1QehQ
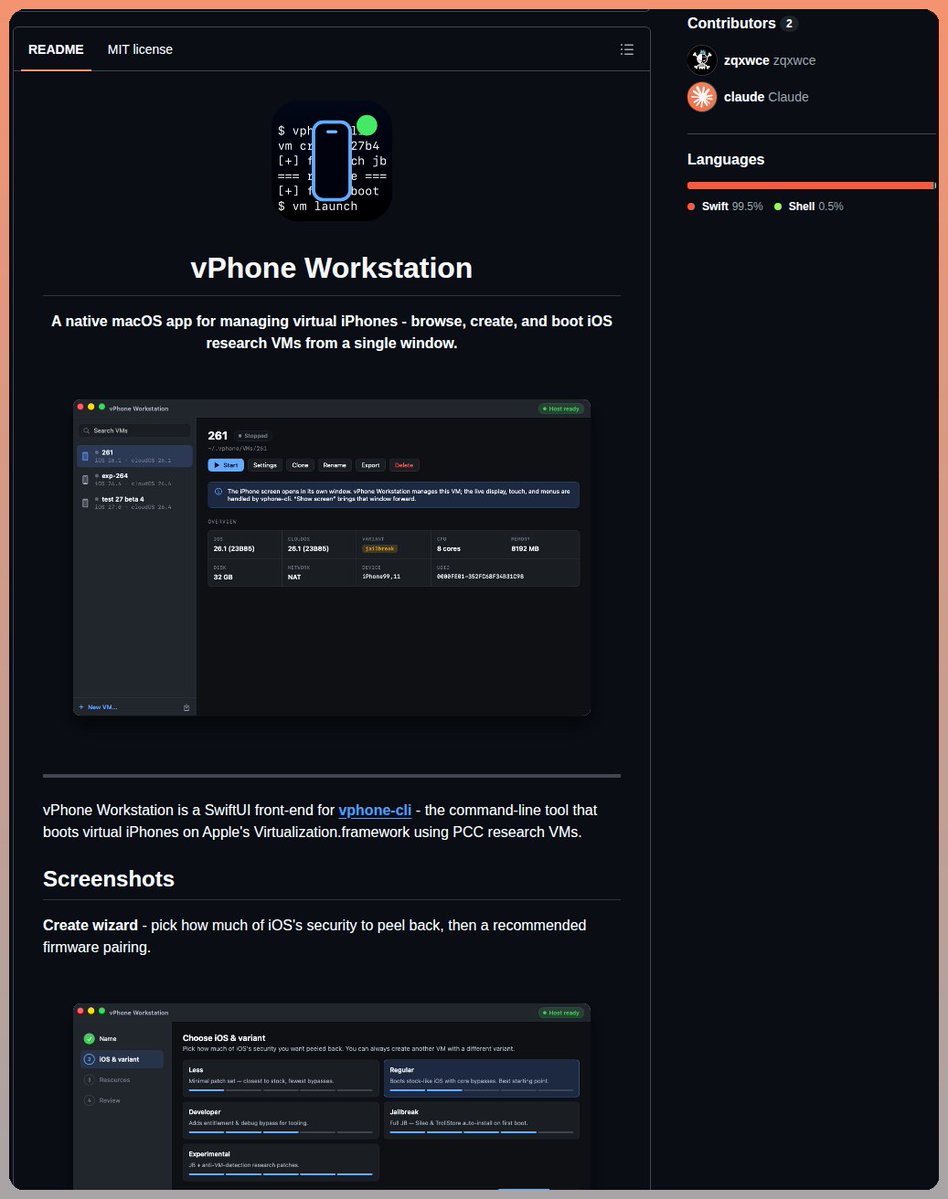
Manage virtual iPhones with vPhone Workstation. This macOS app boots iOS research VMs using the Virtualization framework and offers a wizard to configure security variants like Regular, Developer, and Jailbreak.
https://t.co/sXn2jAaMNb
"3 random dudes”
1. hacked apple, again and again.
https://t.co/5aZcB0RbjF
https://t.co/UdsKrmfFJW
https://t.co/hWDQaimW8c
2. your github enterprise is our github enterprise.
https://t.co/u3UjajnBKq
3. get a discord message from me, get pwned.
https://t.co/pX3RkjxNOX
https://t.co/noscPNmZm9
4. oh yeah, at one point we basically had shells across the electron ecosystem. check the DEF CON research.
https://t.co/1Th5fvpa21
5. your supabase database is my database.
https://t.co/nOIKthdDnM
6. we got the posthog prod database.
https://t.co/VIeGJz1hKq
7. react2shell? vercel paid us $170k for helping secure their waf.
https://t.co/Y2RgQSdl3g
8. your palo alto vpn is my vpn.
https://t.co/oVB068UhST
9. ai ides? we got shells for you, antigravity
https://t.co/tsvSXQuSS0
10. windsurf rce.
https://t.co/DpdGqmNRvu
11. turning cluely into malware.
https://t.co/8QcIYhXQfS
12. ai browsers? sure, uxss: your perplexity browser is my browser.
https://t.co/WVXlHzY0CB
13. openai atlas too. kinda uxss
https://t.co/jkQWnLD7rV
14. hey, it’s not even our first time hacking discourse.
https://t.co/viI1op7aMf
15. adobe coldfusion: pre-auth rce. because apparently we needed another one.
https://t.co/aFILo3suP2
there’s a lot more. go dig.
anyway, yes: “3 random dudes.”
and @HacktronAI is full of more random dudes like these.
The best defense is understanding the offense. Learn to spot and prevent the C/C++ implementation bugs that attackers love to exploit. Secure Development 1001 by @XenoKovah https://t.co/DJmRwObVZg
Let AI agents use your real, logged-in browser without interrupting your work. CLI + extension for browser automation across any shell-capable AI agent.
https://t.co/fVQdzsU4Rn