I wrote this late on Oct 22, mostly to sort out my own head. PHP2Shell is a serious bug, the fix has been out since Oct 21, and I couldn't find a confirmed break-in through it. Lots of attempts, though. What I'd do is in here. #BlackOctober#PHP2Shell
Maersk confirmed today that someone took data from an old system it got in an acquisition. WhiteArmor claims 100GB and wants $5M. Maersk says nothing sensitive leaked. The acquisition part sticks with me. Nobody loves patching the box that came with the deal.
#Maersk
If you run Xen Orchestra, update to 6.9.2 or 6.10.1 today. Vates says attackers are using a login bypass that gives them admin and can end with root on your XCP-ng hosts. They paired it with a second bug that has no fix yet, so rotate your creds too.
#XCPng#Virtualization
One number: 1,122. Apiiro checked 104,185 public GitHub copies of Claude Code's settings.local.json and found a real secret in 1,122. "Yes, and don't ask again" saves the command, password included.
Deleting the file won't erase git history. Rotate first.
#OneNumber#DevSecOps
Scam of the week: a caller claims to be FTC, reads off a badge number, and says a phone in your name is running scams overseas. He hands you to a fake cop. The FTC says real staff never threaten to shut off your phone or ask you to keep a call secret. Hang up.
#ScamAlert#FTC
Microsoft says one Outlook bug in yesterday's Patch Tuesday was already exploited. CVE-2026-124194: open a rigged message file and Outlook can connect out with no warning, leaking a hash that lets someone log in as you. Previewing it won't. Update Office.
#PatchTuesday#Outlook
CISA put the Barracuda email gateway bugs I posted about Nov 5 on its known-exploited list yesterday, and gave federal agencies until Nov 13 to fix them. Three days is a short leash. The Chrome zero-day Google patched Nov 9 went on the same list, due Nov 24.
#CISA#Barracuda
Up to 7.13 million. That's how many fake credit card company emails went out Oct 28 to 30 from the real sending address of Arara, a Japanese email service, after attackers got in. Real sender, fake email. Would your filter have flagged it?
#Phishing
Is it as bad as the headline? "2.2M Sega customers exposed" turns out to be email addresses from 11 newsletters, mostly Japanese arcade and prize-lottery promos. Sega says no names, passwords or cards. The real risk is phishing dressed up as Sega.
#DataBreach#Sega
N-able shipped N-central 2026.4 Hotfix 2 (build 2026.4.1.26) on Nov 10, fixing 7 Able2Shell CVEs. Hosted servers are done, but on-prem boxes should stay offline until upgraded, and everyone still updates Agents first, then Probes. Another hotfix is coming.
#MSP#NAble
@mweinbach On @Visible whenever I unfold the duo, I get much better service than when it’s closed. It’s very bizarre. I have a Starlink mini in my car so it’s not a big deal for me, but I did notice this the other day. I’m on Visible+ Pro.
CISA added the Alpine OpenSSH bug (CVE-2026-123158) to its exploited list today, with a federal deadline of Nov 12. If you run Alpine or another musl distro with sshd exposed, patch and restart today, then check authorized_keys for keys you didn't put there.
#OpenSSH#KEV
N-able pulled hosted N-central offline today after a researcher dumped 33 unpatched bugs and exploit code on GitHub. On-prem customers are told to unplug theirs too until a fix lands. No exploitation seen yet, it says. If an IT provider manages your PCs, ask what they run.
#MSP #ZeroDay
The federal patch deadline for WordPress CVE-2026-119977 was Nov 6. Updating to 7.1.4 fixes it, but researchers warn a full-package update can briefly expose it again. Restrict web access to /wp-content/upgrade/ before updating.
#WordPress#KEV
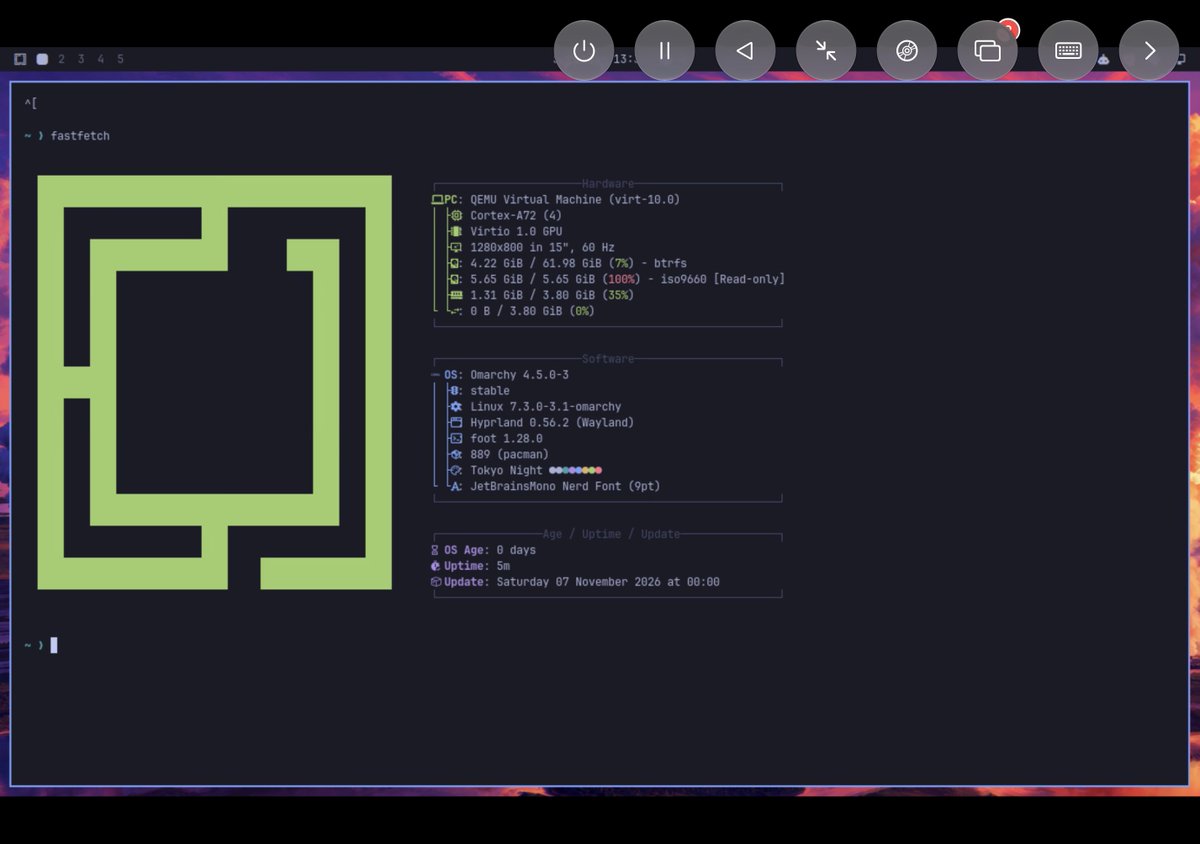
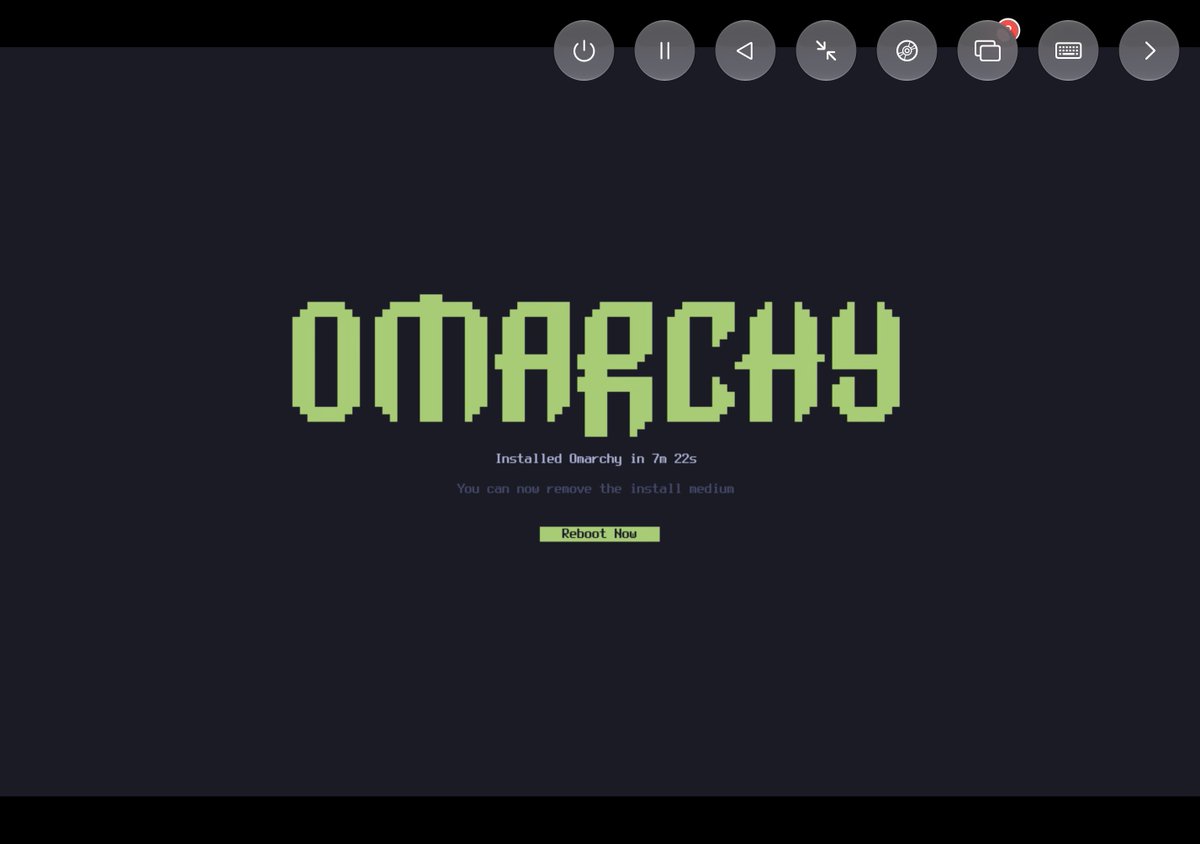
FOR SCIENCE: Omarchy is running on an iPhone Duo.
We custom-built UTM from source with StikJIT integrated into its signed iOS helper, enabling QEMU TCG JIT after a LocalDevVPN attach.
Omarchy 4.5 + Hyprland installed in 7m22s. Pocket Linux workstation. @dhh@UTMap#omarchy#UTM
Anthropic says Claude Code put signed-in emails into curl User-Agent headers when sites asked for a contact. Privacy mod landed in 2.1.317 (on by default). Removing email from context comes early next week. Stable is still on 2.1.311, so update.
#ClaudeCode#InfoSec
DreamHost says an intruder reached FTP/SFTP logins of anyone using its File Manager from about August until Oct 23, when it caught on. No evidence billing or the control panel were hit.
Host a site there? Change reused passwords, check forwarding rules.
#DreamHost#DataBreach
OpenSSH 10.6p2 (Nov 5) fixes a password bypass on musl libc Linux like Alpine with PAM off. A 257 to 1,024 character password logs in as any key-only account, if another account has a password.
On Alpine? Update, restart sshd, or set PasswordAuthentication no.
#OpenSSH#Linux