@stvemillertime I keep an eye on RR as there was an APT group that used null resource records for C2. Probably not as important as others referenced here but maybe a little interesting.
@_RyanBenson@jason_solomon Great work. Combining GRR and a tool such as osquery can be a very powerful pairing providing detection and response. For reference, the osquery approach was described a few years back: https://t.co/hE1mfIqcB4.
@timminchin Repeating my comments about #Upright for this thread:
Absolutely loved it. Brilliant dialogue. Moving. I loved the characters. A true gem that I hope many people get to watch and enjoy. Kudos to everyone that put it together.
Thank you @timminchin I finally managed to watch Upright. Absolutely loved it. Brilliant dialogue. Moving. I loved the characters. A true gem that I hope many people get to watch and enjoy. Kudos to everyone that put it together.
@stvemillertime Great advice. It’s not uncommon to see a reaction where staff work very long hours and are burned out early in an investigation. You’re fortunate if an investigation and response can be wrapped up quickly but usually this takes longer than expected.
@stvemillertime Searching for XOR strings is definitely helpful. I have also searched for values from User Agents too. Yara now supports the “xor” keyword which searches for strings with single byte XOR, which should make yours rules easier to write.
@n3mes1s@Oddvarmoe@Hexacorn Nice find. Take a look at Ghostery, Squish, and Skysea Client View as I think they may also offer some similar capabilities.
Thank you @CrowdStrike! “In response to the devastating fires burning across Australia, the CrowdStrike Foundation is working closely with the Red Cross. [...]The CrowdStrike Foundation will match donations of employees to the Red Cross.” #AustralianBushfireDisaster
Please review public RDP access to your environment and lock it down. I’ve observed many recent ransomware campaigns that are successful and started out with successful RDP brute force or password spray. #Ransomware#CyberHygiene
@CrowdStrike is looking for various #DFIR Experts! I am hunting for someone in #singapore to join our team. You can reach out to me for a chat or apply here https://t.co/QagntznDUH - Please share this post to those who may be interested. #securityjobs
New blog post is up starting a series of looking at just how Mimikatz achieves its magic, beginning with WDigest (and ending with a bit of lsass DLL loading fun). https://t.co/cAUAAsBpXd
New https://t.co/urL5tSHMGW post on my talks at #BlackHat2018 & #DEFCON26 this past week in Vegas. Slides are posted for both talks now.
https://t.co/Ejf0sdEGyQ
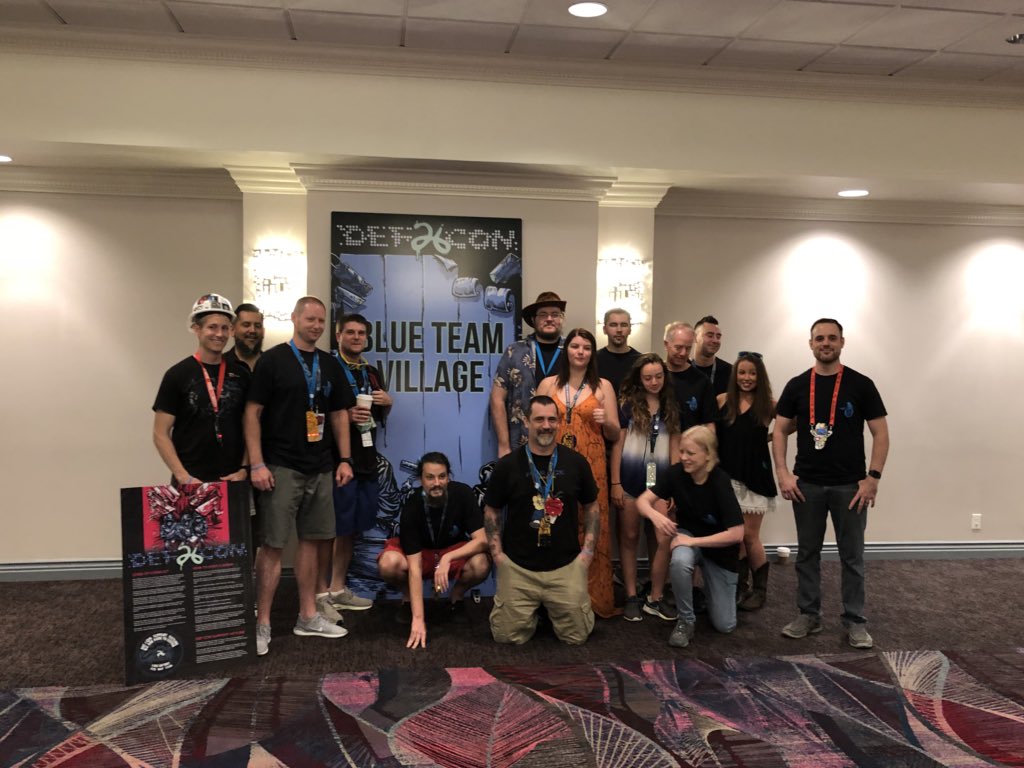
Thanks @BlueTeamVillage for running a fun CTF. Excellent job for the first time @defcon. Congrats too our team @moofusecurity, @Fryx0r, and @daniel_augustyn for a respectable 3rd. Kudos 604 for the win.
Cool talk at #BlackHatUSA about recovering deleted volume shadow copies by @unkn0wnbit and @herosi_t . Cool research, free tools and extension to libvshadow.