@9xJester@CrumbOSRS@shinji Do you know what his actual role in the hack was? Last thing I heard was Kirk was the scraper and caller and some other 16 year old kid in NA was the coder and researcher.
new scam just dropped and it almost got me
someone DMs you pretending to be from a major media outlet, asks if you want to do an interview.
then sends a real calendly, you click it, pick a time, hit submit, and the next screen is the X API asking you to authorize full access to your account
never seen Calendly redirects into the scam before
honestly genius. they’re getting too good
New: Chinese hackers broke into Staples. Staples has an internal customer support tool called Nexus, Chinese hackers got into that, issued millions of dollars of gift cards. Mules then went on a spending spree across the U.S. Gang made $100 million+ https://t.co/52Vt4sanGf
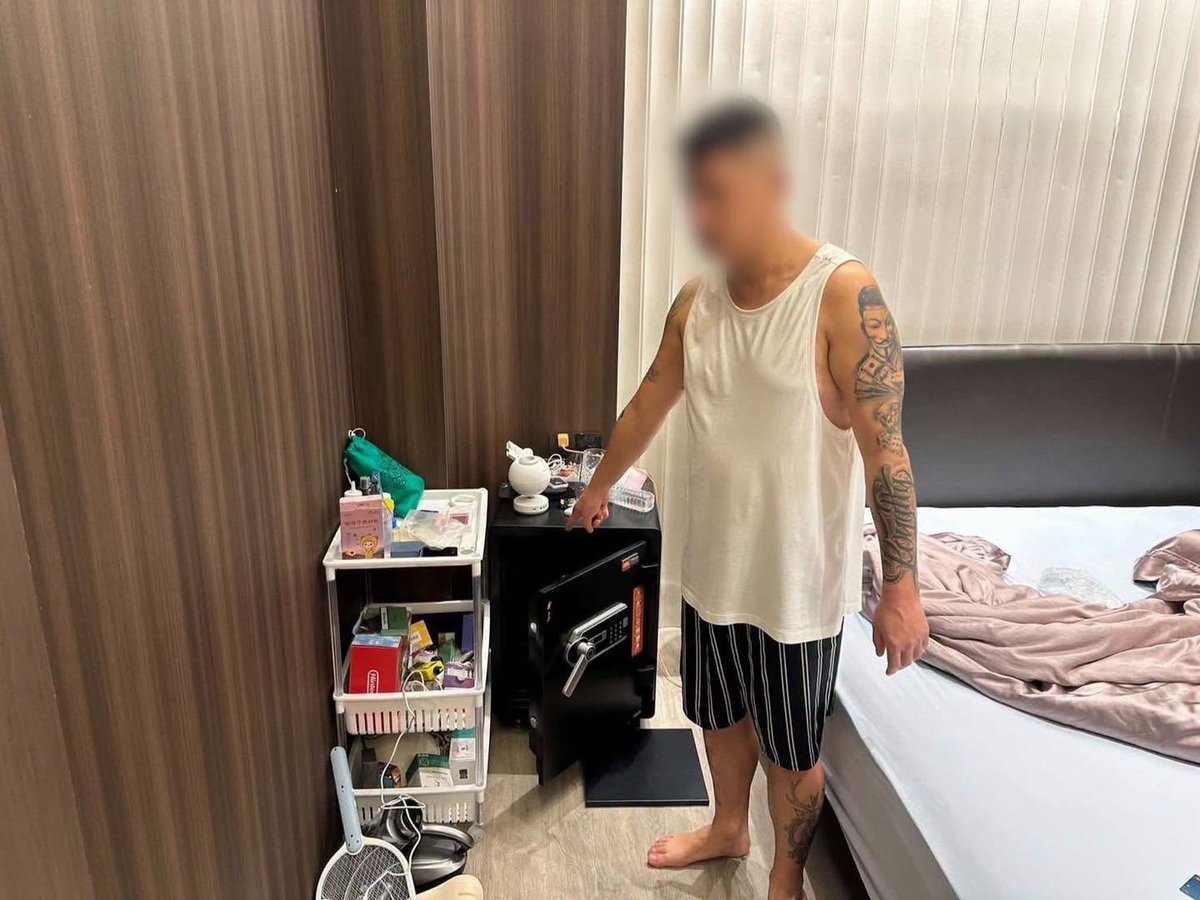
Three armed robbers stormed a luxury home in Nong Prue, Pattaya, Thailand early Tuesday morning, taking cash and Rolex watches before forcing a foreign victim to transfer cryptocurrency worth around US$820,000.
https://t.co/cTSmkAPq9H
An attacker moved ~$6.07M from @Duelbits hot wallets across five chains in a suspected private-key compromise, including the replacement wallet named after its $4.6M theft in 2024. It reopened days later, cause still undisclosed. What changed since 2024?
https://t.co/oqAmhuIHiS
If you have a Gmail account, you need to read this.
Google’s AI is now rifling through your inbox emails and attachments, bank statements, tax docs, medical letters, the whole stack. It was enabled by default, and that quiet rollout is now facing a class-action lawsuit.
Here are 5 steps to turn it off because the kill switch is buried in two different spots:
I got hacked at 3:59 AM without clicking anything. My voicemail handed the attacker my Telegram login code.
Here is exactly how it worked, so it doesn't happen to you.
3:54 AM. My phone rings about ten times in a row, No Caller ID. That was not harassment. It was the attack: keep my line busy.
Meanwhile, the attacker asks Telegram to log in with my number and picks "send the code by phone call". My line is busy, so Telegram's robot call lands on my voicemail and reads the code out loud to it.
Carrier voicemail can often be reached remotely, with a default PIN or a spoofed caller ID. He listens to the message. At 3:59 he is in.
Fortunately, the attack was noisy. The calls woke me up. At 4 AM I only wanted to go back to sleep, but I had the presence of mind to check my notifications. Telegram was showing a new login from a device I didn't know. That check is what saved me: I ended his session within minutes. If I had rolled over, the next day would have been a mess.
In those few minutes he had already typed /balance, then /start on every old wallet bot he could find in my chats. He was hunting for funds tied to my Telegram. The bots were long dead and nothing was lost. He still had time to set his own 2FA password on my account.
What would have stopped it:
Telegram two-step verification, with a recovery email. With a password on the account, the code alone is useless.
Your voicemail. Change the PIN, block remote access, or turn it off (##002# cancels call forwarding on most carriers).
Same for WhatsApp and any service that can send a code by voice call.
No seeds, keys or passwords in Saved Messages. Ever.
A burst of masked calls at night is a signal, not a nuisance. Check your notifications and your active sessions.
I have been building in crypto for more than ten years and I had never thought about my voicemail. Check yours today.