Just a few of the biggest security incidents in the past week... we're still accelerating:
* PHP2Shell: Two critical RCE bugs in PHP core
* eMudhra: Eight intermediate certificates had extremely weak private keys due to a key-generation script error that created keys with tiny values.
* GitLab: integer overflow RCE
* Plex Media Server: flaws compromised internet-facing servers used for cryptominers and proxy tools.
* Arista VeloCloud Orchestrator zero-day: Actively exploited authenticated SQL injection enabling privilege escalation.
* Node.js Brotli decoder RCE
* NGINX critical heap/use-after-free issues
* Railway breach: Attacker accessed systems storing customer environment variables and, for some, obtained decrypted contents (API keys, database credentials, private registry logins, etc.)
* Zeabur breach: ~321,810 accounts and over 3.2 million environment-variable records exposed. Company announced it is shutting down.
* LiteLLM supply-chain compromise: Malicious version 1.107.0 pushed to PyPI and Docker Hub containing a credential stealer and remote-access/backdoor capability.
* California public school data theft: 5.7M+ student records leaked, including names, dates of birth, addresses, demographics, and disability status.
* Capcom breach: Unauthorized access to ~11.77 million CAPCOM ID records
* Quest Diagnostics: Unauthorized access to Quanum Lab Services Manager system used by some clients; potential access to certain patient records.
* State Bank of India breach: customer records appearing on dark web
@matters_btc Multisig, or more broadly, architectures that are designed to eliminate every possible single point of failure, are what one should implement when you have more bitcoin than you can afford to lose.
Seeing reports of another round of snail mail social engineering letters from "Ledger" that try to trick you into scanning a QR code that takes you to software that steals your seed phrase.
If you rely on the volunteer maintained https://t.co/29fHgEGRei we urge you to move to distro packages or building from source now, so you can immediately apply updates. The repo will not have updates today.
@dubya_brian If you know how to calculate the traffic volume served by PHP enabled sites, I'm all ears.
Wikipedia, Wordpress, phpBB forums... there's certainly significant traffic served via PHP.
🚨DEFCON 1🚨
In a few hours, a critical vulnerability that affects ~70% of web sites will be disclosed. It allows an attacker to upload and execute arbitrary code.
It's probably best if you stop browsing the internet for the rest of the week.
https://t.co/LxgLOhP8qO
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
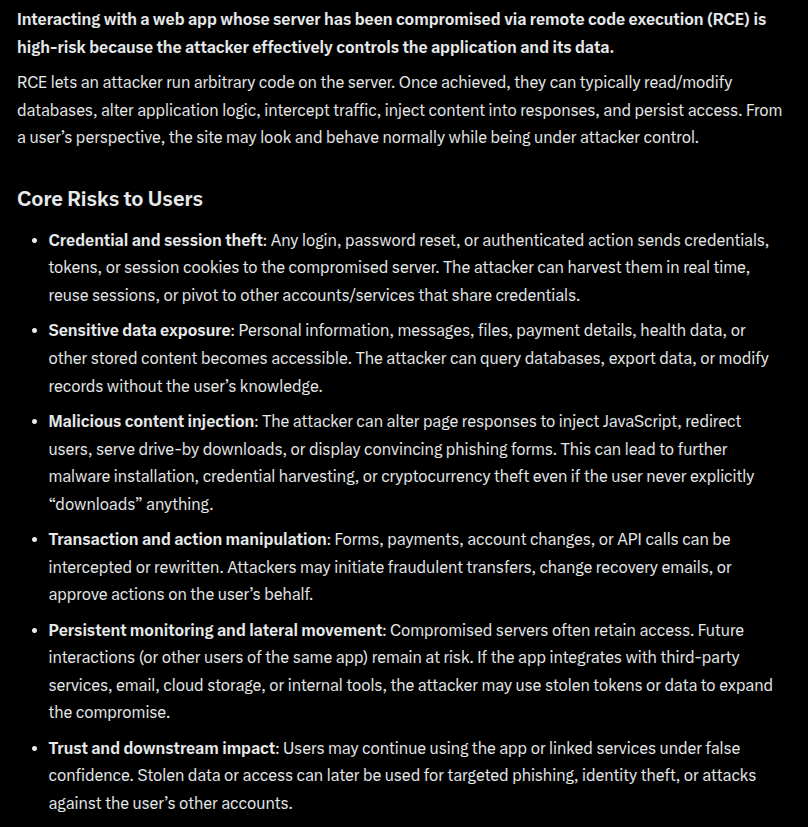
Since morons are noting my post, claiming that it's only a server side issue that doesn't affect clients, here's why interacting with compromised servers is A BAD IDEA:
@Undeference Loading a site that has been compromised could result in you being served with malware. Sending data to a site that has been compromised could result in that data being leaked to unintended actors.
@Dovid That's the entire point - browsing a compromised site could lead to you leaking data or downloading malware that has been injected into the site.