An open-source YARA rule from @SEKOIA_IO triggered on the sample – and it’s part of their public repo.
The attribution in the rule name is probably misleading though, given this kind of obfuscation comes from public tools.
The rule has been included in the YARA Forge set for a while already.
Use it with any YARA scanner.
(If yours also scans archives – like THOR Lite – you’ll catch this stuff inside packages too.)
Rule: https://t.co/l6rFDNscFG
YARA Forge intro: https://t.co/S1FocXF9Lk
Think turning off your phone protects you?
Your device carries two unique codes that follow you everywhere.
You can’t change them. You can’t hide them.
IMEI and IMSI.
Every time your phone connects to a mobile network, it leaves a trace.
No apps needed. No browsing. Just sitting in your pocket.
These IDs reveal:
- What phone you use
- Which tower you connect to
- Where you are
- Which line is yours
- When you swap SIMs
- Even who was nearby
This thread explains what IMEI and IMSI are, why they’re dangerous for your privacy, how they track you, and how to reduce that risk.
Let’s go 🧵👇
Windows SMB Client Elevation of Privilege Vulnerability
CVSS Score: 8.8
Attack Vector: Network
Attack Complexity: Low
Privileges Required: Low
User Interaction: None
Do I have to say more?
https://t.co/SbFqsTWTSN
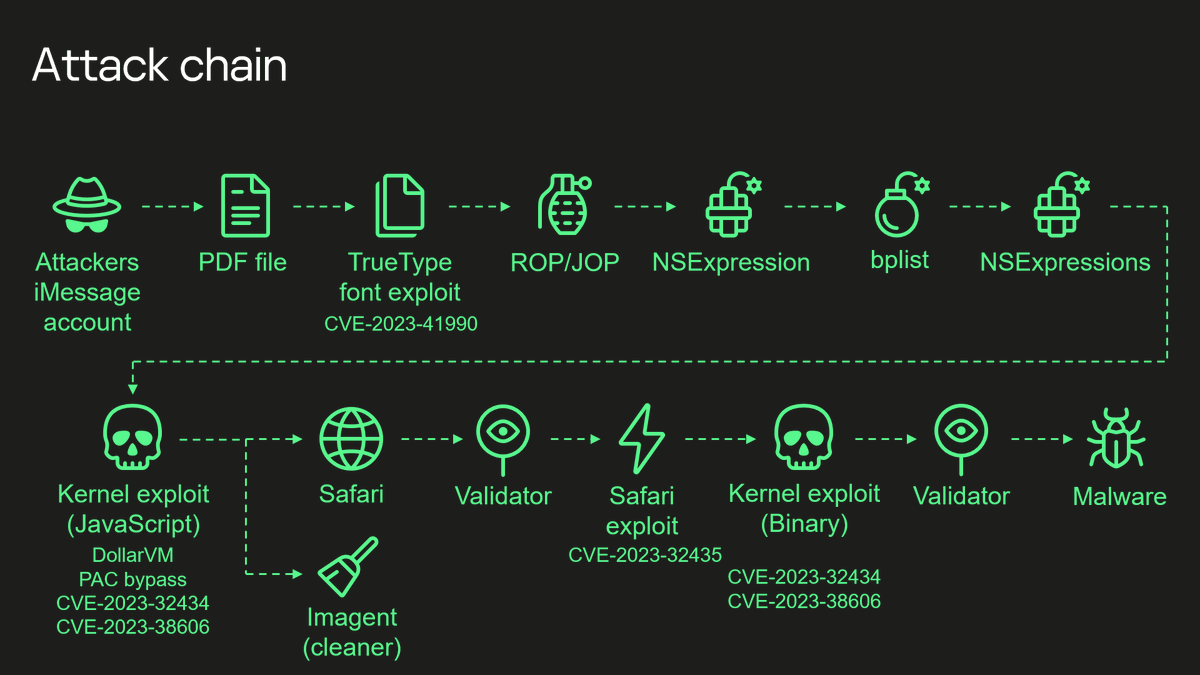
This iMessage exploit is crazy. TrueType vulnerability that has existed since the 90s, 2 kernel exploits, a browser exploit, and an undocumented hardware feature that was not used in shipped software:
https://t.co/YJdY6alLbV
#LOLBin in my favorite built-in tool ? I am seriously disappointed now. 😭
Requires Windows 11, as it's related to a new set of features related to "fsutil trace" command.
⚠️SANS released their new Memory Forensics class (FOR532).
As @SANSInstitute talk about #volatility 3 in this class and to comply with the vol3 license:
‼️SANS published all @volatility 3 related content for free!
Slides:https://t.co/0metSbLiaX
Labs:https://t.co/qebcp4m88Y
#DFIR
Drum roll please 🥁 Congratulations to the winners! It truly went right up to the last challenge.
That's a wrap on the Cybersecurity Awareness Month #HuntressCTF! What was your favorite challenge from the month?
OSINT TIP #227🔍
Open Source Surveillance - real-time intelligence gathering tool, free to register for everyone. It contains only three modules - Flickr, Surveillance Cameras and Road Traffic.
🔗https://t.co/OE6zmf1WEr
@the_wojciech 🔥
#OSINT#CyberSecurity
I have a new blog post up detailing per app registry hives for analysis in #DFIR investigations related to MSIX Registry Redirection. These hives can contain additional information that may not be found in other locations. @ZeroFox@sansforensics https://t.co/re9KDpz63g
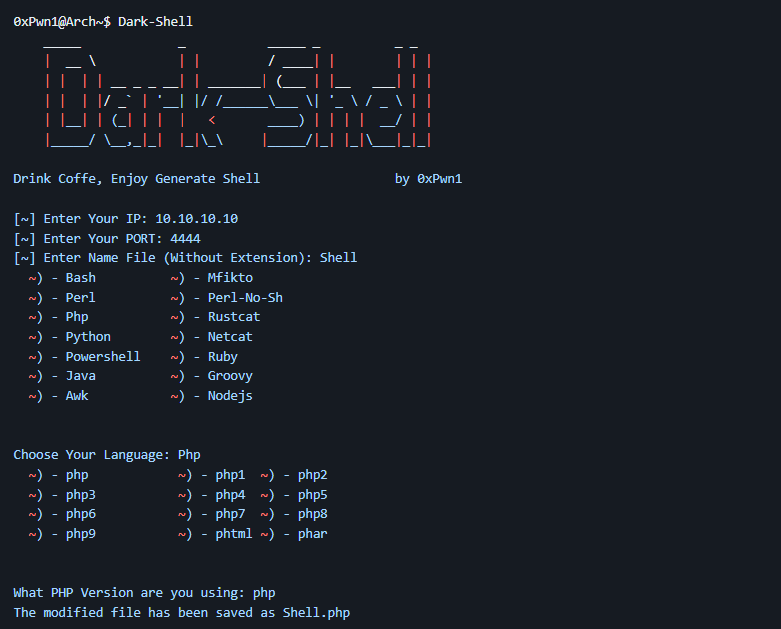
Dark-Shell
A versatile and user-friendly penetration testing tool designed to simplify the process of generating Reverse Shells for ethical hacking and security testing purposes. With "Dark-Shell," users can effortlessly create customized Reverse Shells by providing essential parameters such as IP address, port number, output file name, and preferred programming language.
https://t.co/IfxSsomV9z
#cybersecurity #infosec #pentesting #redteam