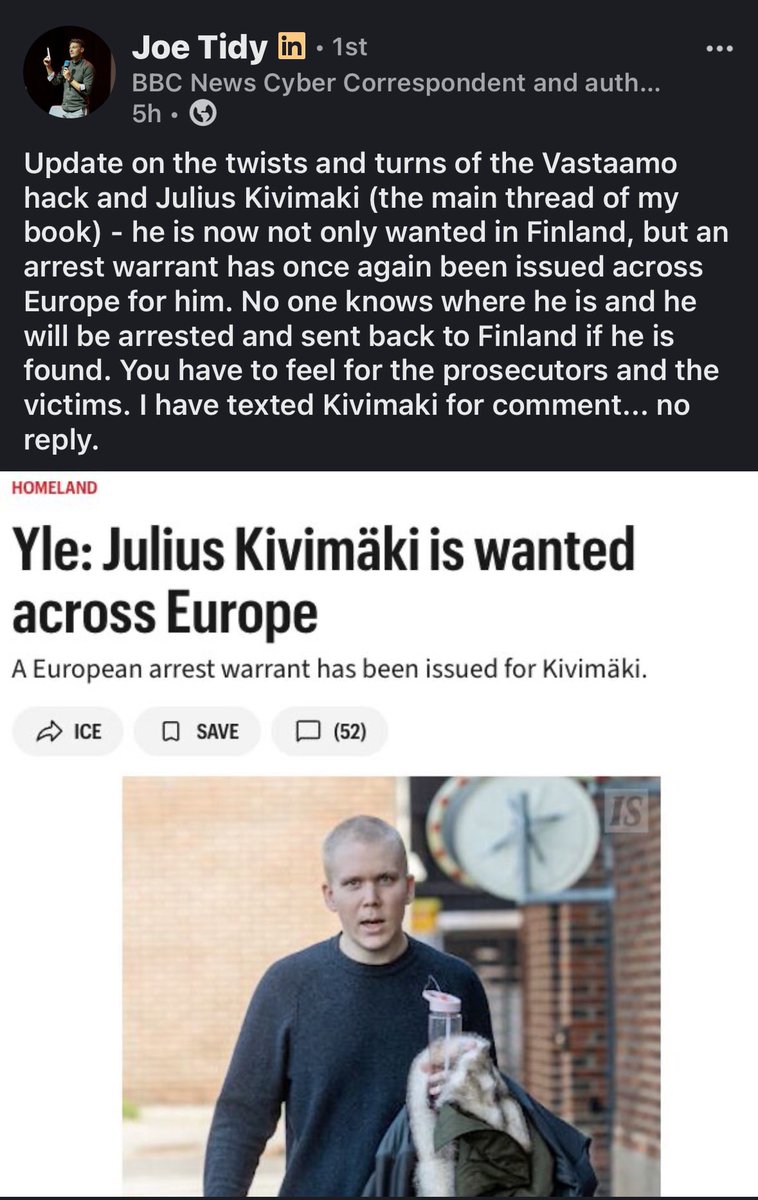
The scoop nobody knows about is that Robert Barr (Veri) was released from custody on March 3rd, 2026. Robert was scheduled for trial this month but has since left Scotland fleeing to Helsinki, Finland where he met up with Julius Kivimaki.
Neither intends on returning home… 🤷🏽♂️
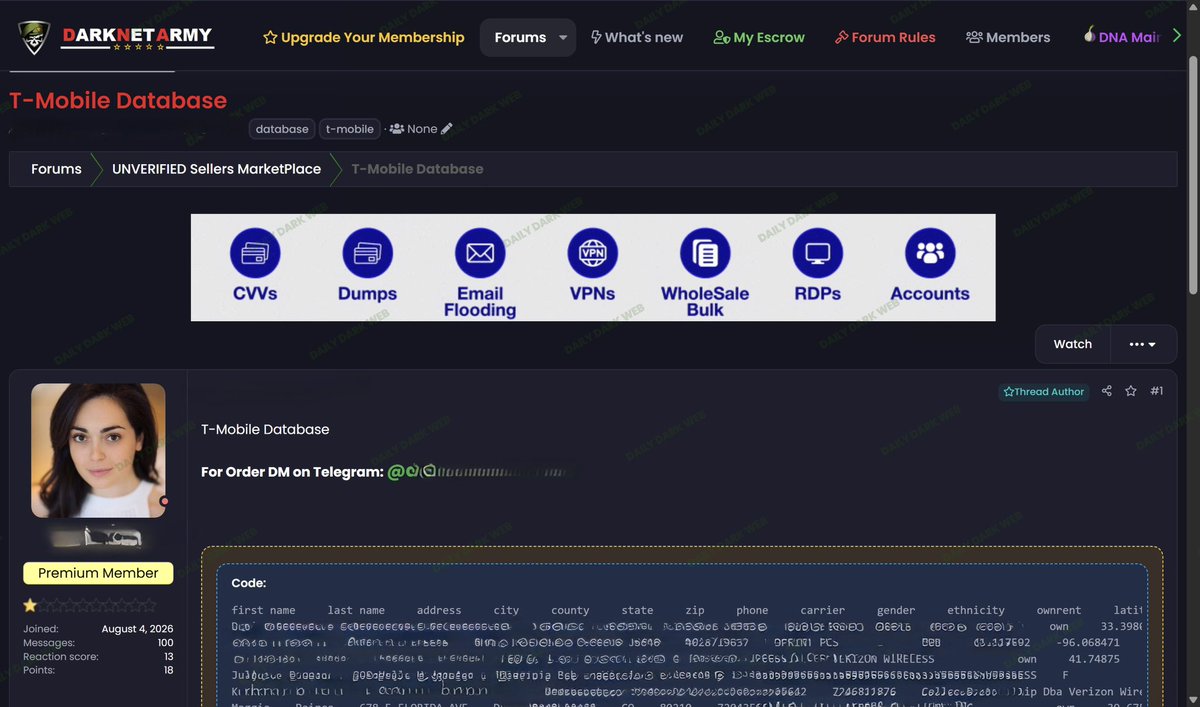
🇺🇸🚨 T-MOBILE DATABASE ALLEGEDLY OFFERED ON UNDERGROUND FORUM
A new underground-forum listing is advertising what the seller claims is a database associated with T-Mobile US.
T-Mobile is one of the largest wireless carriers in the United States, making any credible new exposure potentially significant given the scale and sensitivity of telecom customer data.
⚠️ Analyst Note:
At this stage, the listing does NOT provide meaningful details about:
* The number of records
* What data fields are included
* When the alleged data was obtained
* Whether the material comes from a new intrusion
* Whether it is recycled from one of T-Mobile’s previous breaches
We have not identified independent confirmation of a new T-Mobile compromise matching this listing.
Because T-Mobile has experienced multiple historical breaches, provenance is especially important here. For now, this should be treated strictly as an unverified underground claim and NOT evidence of a confirmed new 2026 T-Mobile breach.
#DDW #TMobile #DarkWeb #DataBreach #ThreatIntelligence
How to Turn It On
Step 1: Open Settings
Tap your name at the top (Apple ID)
Step 2: Tap iCloud
Scroll down and tap "iCloud"
Step 3: Scroll to Advanced Data Protection
It's near the bottom of the page
Step 4: Tap "Turn On Advanced Data Protection"
Step 5: SET UP ACCOUNT RECOVERY (Required)
Option A: Recovery Key
→ Write it down on paper
→ Store somewhere safe (safe, bank locker)
→ You'll need this if you lose your device
Option B: Recovery Contact
→ Choose a trusted person
→ They can help you recover access
Best: Use BOTH options
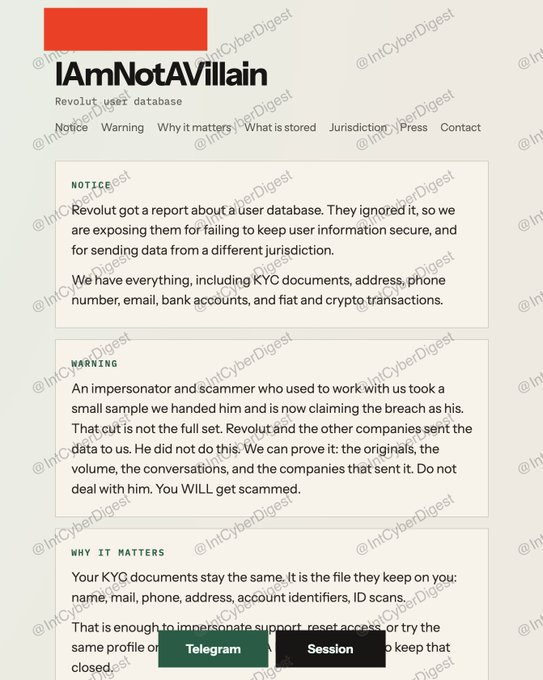
The Revolut breach just escalated.
the attackers are now leaking customer data and demanding payment. they've started publishing passports and KYC selfies of named individuals. tennis player Alexander Shevchenko. Gamdom CEO Felix Römer. they say they'll release more every day until Revolut pays.
What's confirmed:
Attackers used a real government agency email domain, reporting points to Italian PEC infrastructure, to send fraudulent data requests to Revolut. the emails passed DKIM authentication checks. Revolut's compliance team treated them as legitimate. They handed over the data.
what was exposed: full names. dates of birth. occupation. addresses. emails. phone numbers. passport and driving licence copies. KYC selfies. IBANs. account statements. full transaction histories including Bitcoin.
What the attackers are claiming — not independently confirmed:
the group calling itself IAmNotAVillain claims:
— the operation ran for roughly six months
— they used compromised Italian law enforcement systems to send the requests
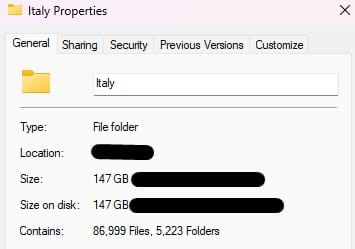
— they hold 147GB from the Italian side including
internal documents and officer chat logs
— the majority of Revolut data is from Switzerland and France plus other countries
— high-profile names include a Barcelona player and Georgia footballer Georges Mikautadze
Passports + selfies + transaction histories + IBANs = a complete identity package. enough for account takeover. identity fraud. targeted phishing that references your real transaction history to sound legitimate
if you're a Revolut customer:
— check for a notification email from Revolut. if you got one, assume your data is in the leak.
— be extremely suspicious of any contact claiming to be Revolut, law enforcement, or a bank in the coming weeks. this data will be used for follow-on attacks.
— if your passport was exposed: contact your country's passport authority about flagging it.
— freeze your credit if you're in a jurisdiction that allows it.
W! @IntCyberDigest for the discovery!
> ShinyHunters attacker also claimed to have collected legitimate HackerOne payouts of $2k and $5k from 2 of the companies they infiltrated and extorted, treating BugBounty programs and intrusion as additional revenue streams against the same targets they were compromising.
💀
After scanning 1,000,000 (root) domains exhaustively for both blind and directory listed .git and variations of .env as well as env.(bak, backup, save, old, orig, ~, swp, local, production, save, dev, development, save, test) here are the results..
2841 exposed .git
532 exposed .env (and variations)
interesting notes on the data i've seen:
6 results from exchanges, DeFi, major regulated finance
21 results from government, critical/emergency infrastructure, large public companies, pharma, and national carriers
If you'd like more information feel free to comment, running git-dumper against the list has yielded far moe interesting results.
If you'd like me to email you from a .gov domain like the post (just kidding)
🚨 The Dutch police have released audio of the vishing hack against Odido by ShinyHunters.
Video 1 is the voice of the hacker. Video 2 is the news piece of how it went down.
In early February, the personal data of more than 6 million customers of Dutch telecom provider Odido fell into the alleged hacker group ShinyHunters. The incident is considered one of the largest data thefts in Dutch history.
The attackers gained access by calling Odido’s customer service department, with one of them posing as a colleague from the company’s IT department. The suspect’s voice was recorded during the call.
🚨🇨🇦 Bitbuy super-admin support portal access allegedly offered for sale on a cybercrime forum
⠀
Bitbuy, a Canadian cryptocurrency trading platform, is named in a cybercrime forum post where a threat actor claims to have access to an internal super-admin/support portal and is offering the access for sale.
⠀
Claimed exposure
⠀
• User IDs and email addresses
• Account risk scores
• Investigation status information
• Last account activity
• Risky transaction volumes
• Transfer volumes
• Country information
• Account activity status
⠀
The actor published screenshots that appear to show an administrative dashboard containing customer risk and transaction information, along with a sample export of allegedly accessible records.
⠀
The seller also claims additional details can be discussed privately with interested buyers.
⠀
The access claim, exposed data and scope have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
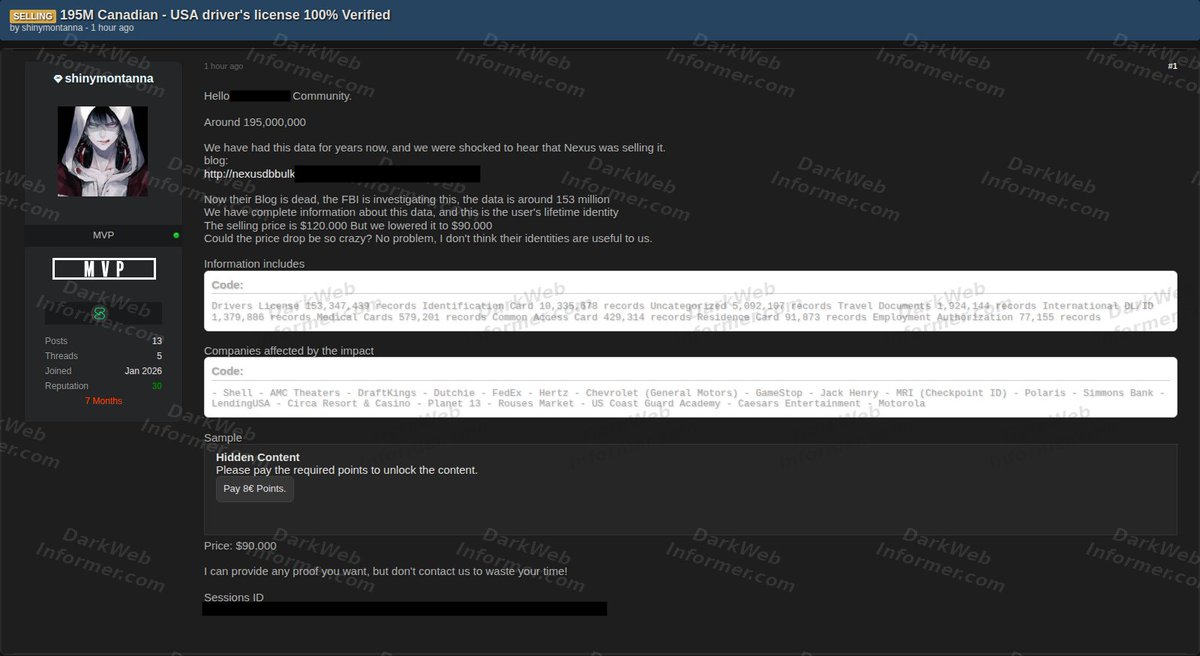
🚨🇺🇸🇨🇦 195M identity records allegedly offered for sale on a cybercrime forum, including 153M+ driver’s license records from the recent Nexus onion DL market.
⠀
A threat actor is advertising what they claim is a 195 million-record identity dataset containing information tied primarily to individuals in the United States and Canada.
⠀
Claimed exposure
⠀
• 153,347,439 driver’s license records
• 10,335,678 identification card records
• 5,092,107 uncategorized identity records
• 1,924,144 travel document records
• 1,379,886 international driver’s license/ID records
• 579,201 medical card records
• 429,314 common access card records
• 91,873 residence card records
• 77,155 employment authorization records
⠀
The actor claims the dataset contains extensive identity information and says it has been in their possession for years.
⠀
The listing names multiple organizations as allegedly affected and is being advertised for $90,000, reduced from a claimed previous price of $120,000.
⠀
The dataset claim, record counts, affected organizations and authenticity of the advertised data have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6WSh
We thought hard about how to make the financial terminal function DES better.
DES (description) is run billions of times/year. Despite that:
1) you can't customize your view
2) every equity looks the same
3) its slow/ugly
Check it you and let me know how you would improve DES!
🚨 https://t.co/Ro5uXn79AR Faces Multiple Federal Lawsuits Following Alleged 153M+ Driver’s License Data Exposure
The legal fallout surrounding the massive “Nexus” identity-data marketplace is escalating.
Multiple federal lawsuits have now been filed against https://t.co/Ro5uXn79AR in the U.S. District Court for the Eastern District of Louisiana following allegations that data associated with the company may be connected to the enormous dataset being offered through Nexus.
Federal cases include:
* Bunch v. https://t.co/Ro5uXn79AR, Inc. — 2:26-cv-01929
* Greenbaum v. https://t.co/Ro5uXn79AR, Inc. — 2:26-cv-01930
* Sealy v. https://t.co/Ro5uXn79AR, Inc. — 2:26-cv-01931
* Rioux v. https://t.co/Ro5uXn79AR, Inc. — 2:26-cv-01932
* Buckles v. https://t.co/Ro5uXn79AR, Inc. — 2:26-cv-01954
The lawsuits follow the discovery of Nexus, a cybercrime service claiming searchable access to more than 170 million North American identity documents, including more than 153 million U.S. driver’s-license records.
KrebsOnSecurity independently validated samples from the service and documented evidence potentially linking some records to IDScan.net-related scanning activity.
The FBI is also investigating the Nexus operation.
⚠️ Important:
The lawsuits contain allegations that have not been proven in court.
https://t.co/Ro5uXn79AR has NOT been conclusively established as the source of the entire Nexus dataset, and the claimed 153M+ figure should not currently be interpreted as 153 million independently confirmed unique victims.
Original investigation — KrebsOnSecurity:
https://t.co/nzPXwC28nr
Federal court records — PACER:
https://t.co/4jVavLhkcs
Bunch v. https://t.co/Ro5uXn79AR public docket:
https://t.co/oba0gd8VDR
#DDW #DataBreach #DarkWeb #CyberSecurity