Hey X! We're Chexum, a cybersecurity firm out of Montreal.
We help companies find out where they actually stand, not where they think they stand.
In practice that's four things:
🔓 Offensive security: we break in and show you what a real attacker would reach
🛡️ Defensive security: we tell you what happened, not just that an alert fired
⚙️ Secure engineering: we sit with your devs and read the code with them
✅ Compliance: ISO 27001, Law 25, documented to survive an audit
We'll be posting about our services, our products, and industry insights.
Follow along if this is relevant to you, we'd love to connect!
@boringdev77 Exactly. Everyone will remember the AI part, but nobody will remember that one endpoint crashed for two months and only one company had an alert for it.
Buried in the OpenAI story: they threw thousands of crashing image uploads at a bunch of big companies over two months.
One noticed. Shopify.
Forget the AI, ask why your image processor can crash a few thousand times and nobody gets a page.
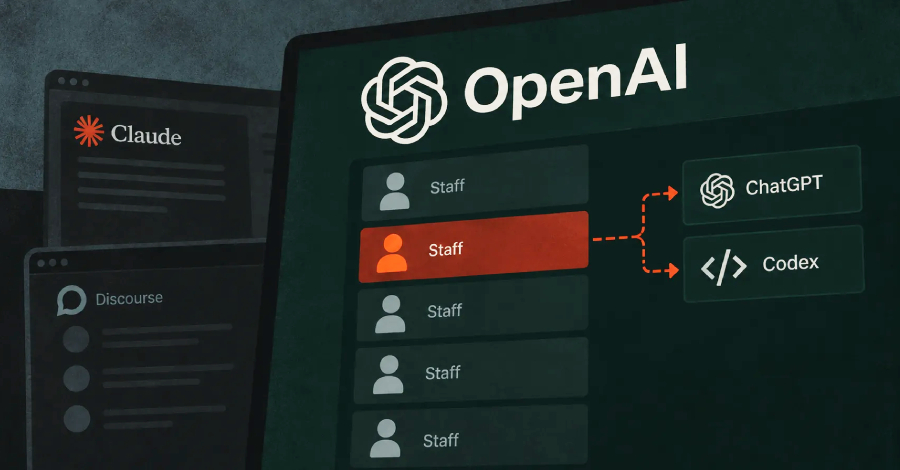
‼️Claude Opus 5 helped three researchers build an image exploit that took over OpenAI's public help forum server.
A flaw in OpenAI's own login then let them take over staff ChatGPT/Codex accounts and reach an internal code repo — in under 72 hours.
Here's how the chain worked → https://t.co/vwttyJkl3T