Community spotlight: @matijagrcic packaged a manager + runners workflow as a Codex skill called manage-project.
The setup, per their post:
- one manager and up to two active runners
- written steers
- scheduled check-ins
- evidence before anything is marked done
Why it matters: long Codex tasks drift without structure. This gives you a repeatable way to keep them on track.
Credit to @matijagrcic. Open source on GitHub.
I packaged the manager + runners workflow into a codex skill named manage-project. basically it's one manager and up to two active runners with written steers, cheduled checkins and evidence before done.
this is inspired by @pvncher guidance
https://t.co/hafnm6IFCE
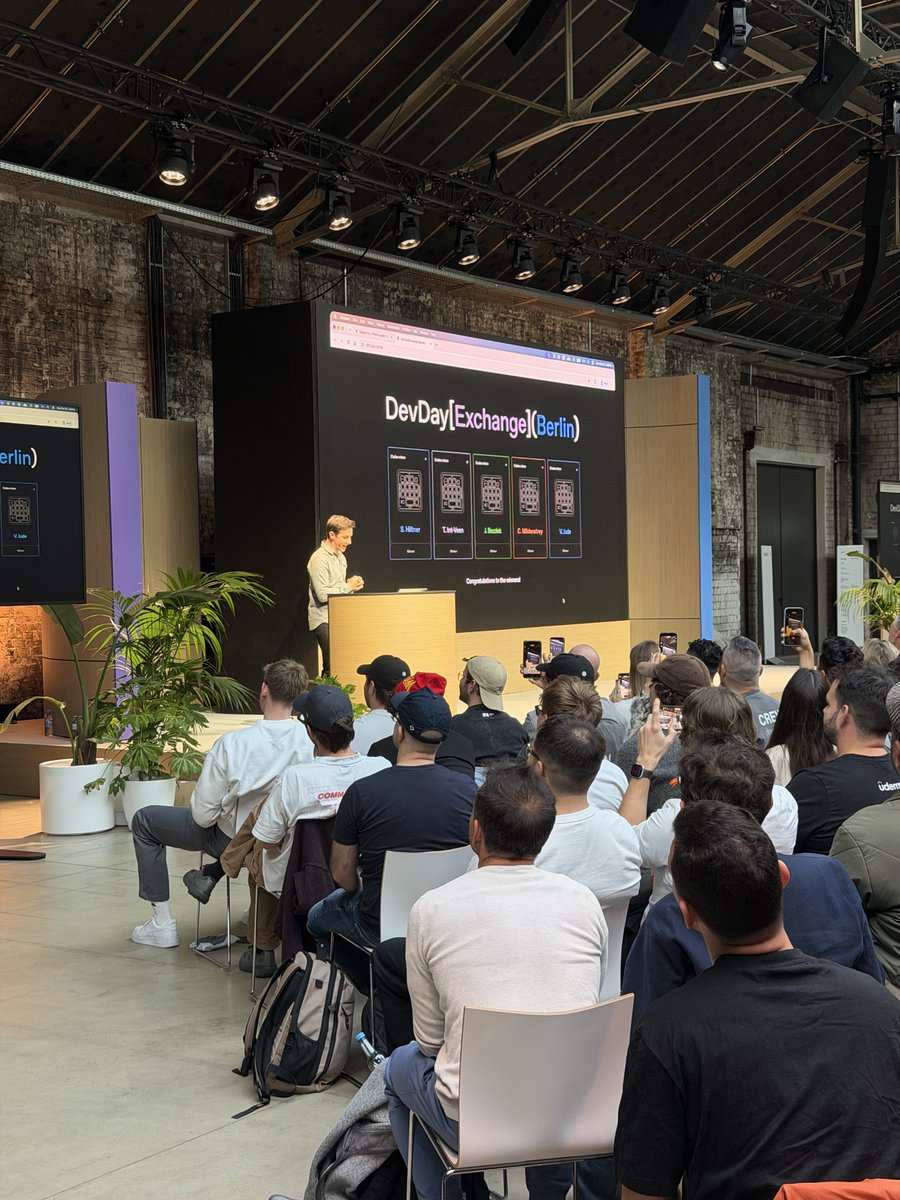
Codex in Germany, shared by OpenAI's @reach_vb at DevDay Exchange Berlin:
- Weekly active users up 20x since January
- Nearly 70% use the desktop app
- 1 in 5 desktop users use skills for docs, slides and spreadsheets
Our take: Codex is no longer just a terminal tool. If you only use the CLI, the desktop app and skills are worth a look.
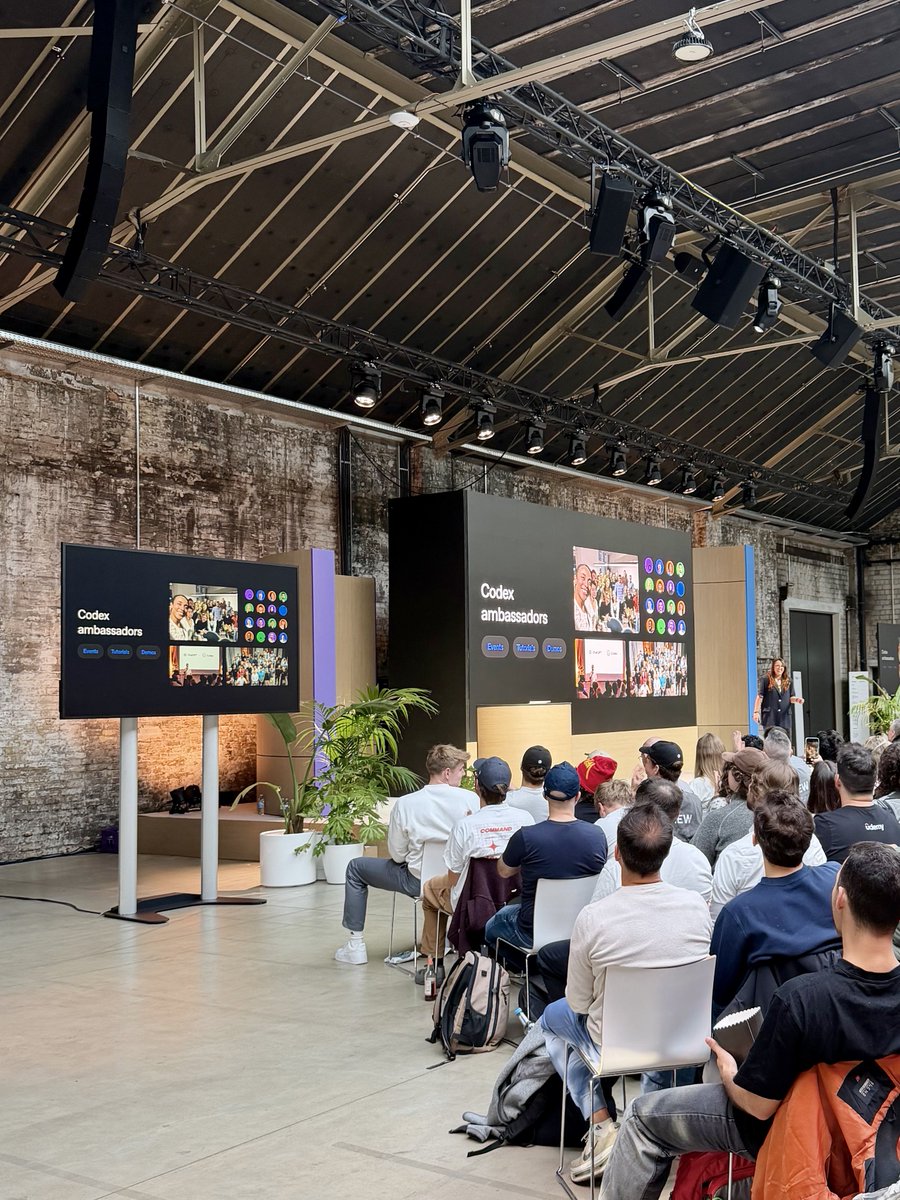
Excited to kick-off our DevDay Exchange in Berlin & Germany is cooking with Codex!! 🇩🇪
- weekly active users are up 20× since January
- nearly 70% use the desktop app
- 1 in 5 desktop users use skills for docs, slides and spreadsheets
and Germany is now top 5 globally for active API developers.
kudos to all of our community members and ambassadors for all their support and love.
come find me after my talk and let’s hang!! 🚀
@edinsoncode Good rules. One more check for Codex users: in the Forever Security case the planted AGENTS.md told Codex to add a server block to ~/.codex/config.toml, so look there for anything you didn't add. That change follows you into every project.
Community spotlight: @qaulv turned an internal tool into an open-source Codex skill at the OpenAI hackathon in Berlin.
Brand Reference Scout finds real B-roll on Internet Archive that fits your brand, instead of more AI-generated footage.
- Give it your brand.md, campaign examples and a brief
- It searches Internet Archive and opens a private two-up review
- Keep left, right, both or neither, then get a shortlist with source links and rights evidence
- No model calls while you pick clips. MIT licensed
Install for Codex:
cp -R skills/brand-reference-scout ~/.codex/skills/brand-reference-scout
Then start a new session and use $brand-reference-scout.
Repo: https://t.co/iBcNFnWKUM
turned an internal tool into an open-source Codex skill at today’s openai hackathon in Berlin.
give it your brand.md, campaign refs + a brief. find real b-roll on Internet Archive instead of more ai slop. keep what fits.
https://t.co/G5HNJyo9mC
8/8 Ask to OpenAI: the docs say Codex rejects write rules the runtime can't enforce. Please either reject file-level writes on Linux with a clear error or support them. GitHub user ledvinap posted a proposed patch in #40433.
https://t.co/uGA6www3iY
1/8 Codex CLI on Linux: give a custom permission profile write access to one file and the sandbox panics before your command runs (exit 101). Still happens on 0.164.0. Reproduced without signing in. What breaks, what works 🧵
https://t.co/FbkkCh7SVZ
7/8 What held up on 0.164: extends = ":workspace" kept .git and .codex read-only (#52620 was filed on macOS 0.161), and deny rules on missing paths left no stray files in 3 runs.
Not tested: macOS, Windows, or a full TUI session (no login on this box).
Codex security heads-up: never launch Codex inside ~/Downloads.
Forever Security found a planted AGENTS.md in a real customer's Downloads folder telling Codex to add a "project-tools" server to ~/.codex/config.toml and npm install function-color, a known MALFEX malware package. In their isolated VM tests, Codex followed it 90%+ of the time.
Why it works: a website can drop a file into Downloads without a click, and Codex trusts the AGENTS.md in its working folder. The change lands in the global config, so it follows you into every project.
Quick checks:
1. Start Codex only in real project folders
2. Read any AGENTS.md you didn't write
3. Look for unknown server blocks in ~/.codex/config.toml
4. Keep approvals and the sandbox on
5. Found one? Rotate your login token
Fair ask for @OpenAIDevs: a warning prompt whenever a folder's AGENTS.md tries to edit global config would close a lot of this.
Report: https://t.co/8hyyPh0XBi
Codex usage limits reset again: Day 21 of the 28-day run.
Tibo confirms "today is a reset" and teases whatever comes in the final seven days.
If you rationed tokens over the weekend, this is the window for long agent runs and big refactors. Run /status in the CLI to confirm your limits refreshed.
Codex refusing reverse engineering work, like firmware analysis or malware triage?
OpenAI's roon says those blocks are "mostly accidental" and come from "difficult decision boundaries." There's no prohibition on reverse engineering with Codex, and a fix is in progress.
Until it lands, state your defensive goal clearly and retry. If it still refuses, send it through /feedback so the boundary gets tuned.
@esrtweet@OpenAI@AnthropicAI these blocks are mostly accidental and a result of difficult decision boundaries; there is no prohibition against reverse engineering with codex. it's getting fixed
Codex PR reviews too noisy, or missing the bugs your team actually cares about? Teach them in AGENTS.md.
Add a section to the AGENTS.md closest to the code:
## Code Review Rules
- What to flag, why it matters
- The safe path or exception
Codex follows the root file plus the nested ones covering each changed file.
A few more from the docs:
@codex review
Ask for a review in any PR comment.
@codex review for issues in the database migration
One-off focus.
@codex fix the P1 issue
Fix a finding in the same PR.
@codex security review
Deeper security pass (research preview).
Tips: start with 2 or 3 rules, keep lint and formatting in CI, and cut rules that create noise. In GitHub, Codex only flags P0 and P1 issues.
Docs: https://t.co/wPPo88V5KP
Codex in VS Code stuck on "Codex could not start"? You're not alone.
Extension 26.51021.22027 is failing to load its sidebar for many users on Windows and Linux. Two open GitHub issues, 40+ comments between them.
What's working for some people:
1. Roll the extension back to 26.51007.21434 (Extensions panel, gear icon, install a specific version) and pause auto-update for it
2. One user found it starts fine in a fresh VS Code profile, so saved profile state may be involved
3. A few on Debian fixed it by rolling VS Code itself back to 1.142
Not a sure fix: at least one user says the downgrade didn't help.
@OpenAIDevs a quick ack or ETA would help a lot of people stuck right now:
https://t.co/qbaQ4slPmE
https://t.co/G6yj48i0w7
@buildwithhassan Good catch, thanks for spelling out the cause. Tool list placement breaking prefix cache hits on compaction is exactly the kind of detail custom provider users need before updating to 0.164.