Breaking. #ESETResearch discovered a new data wiper malware used in Ukraine today. ESET telemetry shows that it was installed on hundreds of machines in the country. This follows the DDoS attacks against several Ukrainian websites earlier today 1/n
With recent troop movements & #DDoS attack in Ukraine, many are looking to the 2014 invasion of #Crimea for insight into what may happen in the current #RussiaUkraine conflict. Check out this side-by-side comparison to see how current Russian activity overlaps with that of 2014.
On Monday, KrebsOnSecurity began following up on info provided by @holdsecurity that a ransomware group (Ryuk) is preparing to encrypt systems at possibly hundreds of medical centers/hospitals. FBI/CISA/HHS just had a call warning of "imminent, credible threat to US hospitals."
The threat of #cryptojacking is continuing to grow due to the deployment of techniques such as #malware stuffing and #mobilemalware. What organizations should be aware of when defending against these #cyberattacks: https://t.co/3jbWmLMU2H via @DarkReading
Scary since this #DDoS attack totaled only 150 Gbit/s. Yet, it caused a major outage and half-a-day downtime across the entire country. It's time to fight #cybercrime more effectively. In the digital age, 99% availability is just no longer good enough.
https://t.co/yhDEcrR9lp
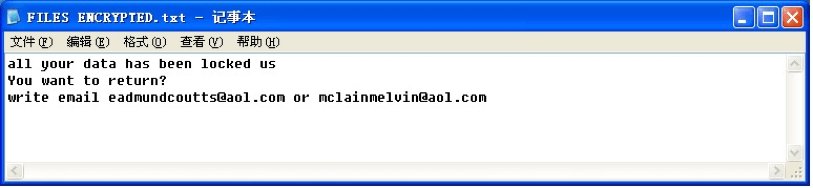
FortiGuard Labs has been monitoring the Dharma (#CrySiS) #malware family for years. Once authenticated, a Dharma attacker can map a hard drive remote share or use the clipboard to pass malicious content to the victim. More on Dharma: https://t.co/Bvsim97UyY
#Microsoft patched a zero day vulnerability impacting #Windows 7, Server 2008 and Server 2008 R2 systems.
Researchers @kaspersky who discovered the #vulnerability said it was found in use by a number of APTs. #PatchTuesday
https://t.co/GAVTCZoHa4