Your X account already knows which of your posts work. You just never read the data.
Download your archive: Settings → Your account → Download an archive of your data. It can take a day to arrive. Unzip it, open Claude Code in that folder, and paste:
"Read data/tweets.js. Spin up 5 subagents in parallel:
1. Topics: group my posts by subject and rank each group by average likes and reposts.
2. Hooks: compare the first lines of my top 20 posts with my bottom 20. What do the winners do that the losers don't?
3. Timing: which days and hours my posts do best.
4. Formats: threads vs single posts, lists vs stories, with links vs without, with media vs without.
5. Dead weight: the topics and formats I keep posting that never work.
Merge it into one page: what to post more, what to stop, my 5 best hook patterns, and 10 new post ideas written in my winning style."
You'll learn more in 10 minutes than in a year of guessing.
You can now check your own phone for Pegasus, for free.
Zero Breach Toolkit looks for traces of known government-grade spyware, including Pegasus, Predator, Graphite and Candiru, on Windows, Mac, Android phones and iPhone backups.
It's read-only, makes zero network requests during a scan, and never uploads anything. Every report says how strong the evidence is and what it couldn't check. A clean result is never sold to you as "you're safe."
No technical experience needed. The guide walks you through it in about 20 minutes.
https://t.co/uSjMLHV9pW
A BUG LET A HACKER PRINT $2.7M OUT OF THIN AIR. THE CHAIN SHUT ITSELF DOWN TO STOP HIM. 5 SECONDS LATER HE MOVED 1,135 ETH ANYWAY.
they literally turned off a blockchain and it still didn't matter
I went through the tracehound trace on the Initia hack. 85 seconds. this one broke my brain.
the "just halt the chain" crowd will hate this. the "L1s are safe" crowd will hate it more.
let me show you how bad it is
> HE PAID FOR GAS WITH TORNADO
08:26 UTC, oct 23.
0.1 ETH out of Tornado Cash lands in his wallet.
6.5 hours before the attack.
he wasn't improvising. he was clocking in.
> THE PRINTER
14:59 UTC.
a caching bug in the chain's VM.
one script, and Initia believes he holds WETH, USDC and AUSD that nobody ever backed.
~$2.7M. printed. backed by: nothing.
> 7 MINUTES 21 SECONDS
he doesn't wait to find out if it's real.
LayerZero. CCTP. bridges.
the fake money crosses to Ethereum and becomes real money.
999,999.89 USDC in one swap.
a million dollars, minus pocket change.
> THE CHAIN PULLS THE PLUG
15:41:30 UTC. 42 minutes after the mint.
Initia halts. every rollup on it stops.
no blocks. nothing moves.
on Initia.
> 5 SECONDS
15:41:35 UTC.
on Ethereum, 1,135.52 ETH moves to one fresh wallet. one transaction.
you can stop a blockchain.
you can't stop ethereum.
> AND THEN... NOTHING
no tornado. no bridge. no exchange.
1,135.52 ETH, parked in plain sight.
days later: still there.
so let's recap:
> gas from tornado, 6.5 hours early
> printed $2.7M out of a bug
> bridged it out in 7 minutes 21 seconds
> watched the chain halt
> moved 1,135 ETH five seconds later
> and now just... sits on it
he's not hiding. he's waiting.
now read this twice:
A HALT STOPS A CHAIN.
IT DOESN'T STOP THE MONEY THAT ALREADY LEFT IT.
if a whole L1 can't freeze a thief in 42 minutes...
what's your plan when it's your wallet?
tracehound traced it in 85 seconds and we're watching that wallet.
paste an address. watch them run.
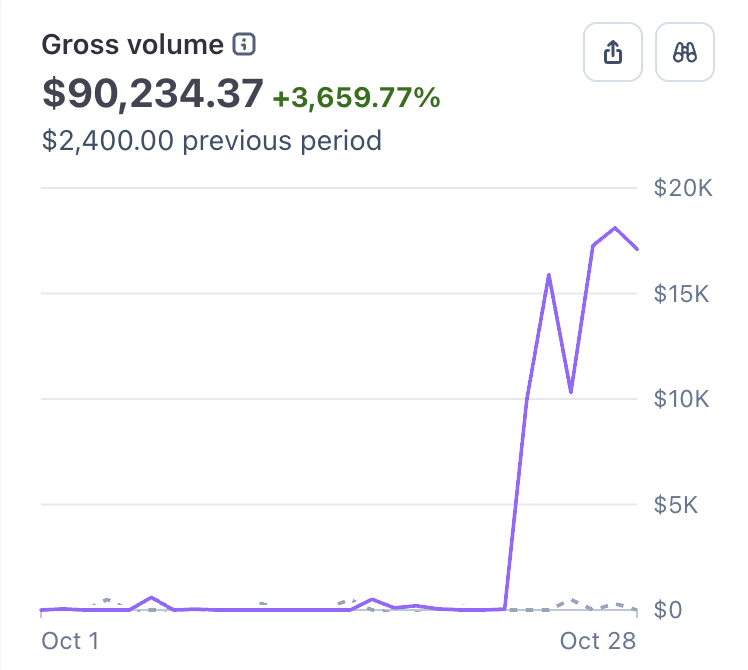
We just crossed $1M in annualized revenue run rate in just 6 days after launch.
And we're just a team of 2 people.
Our idea started out really simple: ai video platforms are doing billions, but they don't have a strong moat. why don't we just steal their users?
Seems like it worked.
--
I genuinely believe that the only moat in AI applications is acquiring users with velocity, then making them stay by getting deeply embedded in their daily workflows.
Our plan is simple. Keep stealing users from ai video platforms' $nB+ pie in every area with no moat, ship new features every week, and find the ones that get deeply rooted in marketers' everyday work.
Sure, you can ask how we're gonna make our users stay. But honestly, worst case we still hit $100M ARR, and if we're crushed by competitors, my cofounder and I will go back to a shitty couch, build again with no salary, and make millions again. Not worried about that either.
We just focus on growth & net revenue retention.
In an era of thin moats, we don't need fake storytelling like "Agentic creative OS". We should build something people want :
"A product that's cheaper than higgsfield, better than higgsfield"
Ouhhhh man I'm tired
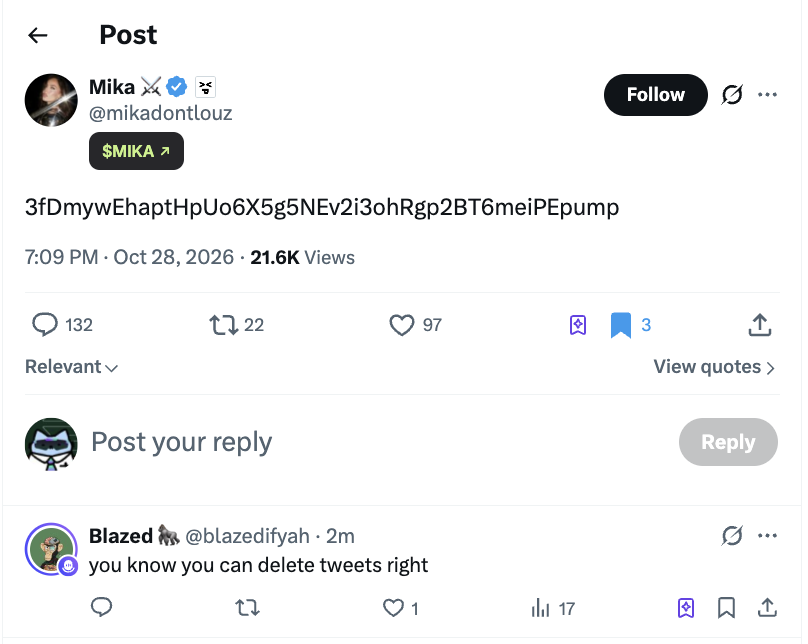
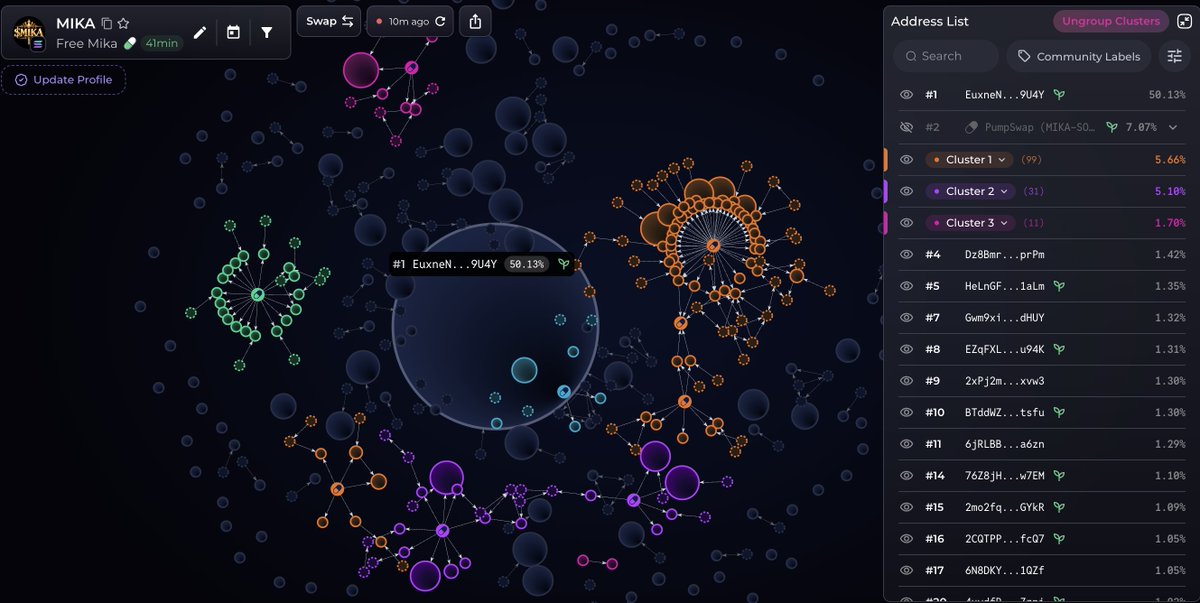
@mikadontlouz "accidentally" posted her private key and "lost $40K"
(was fake.. she put a nonce on the wallet before posting it)
She then posted a CA
- 400k spawner
- dev holds 50%
- awful bubblemaps
Introducing Reality-Aware Rendering in @Simulon, a completely new way to create with the real world.
Place neural assets with your phone and act out the scene. When you stop recording, Simulon renders the take, reading everything in it (what you do, what you say and the place around you), and your assets respond to all of it.
The final is regenerated from your recording: a new performance of the scene, not a copy of the footage.
Available now on iPhone. Coming to Android soon.
someone can hack your phone by sending you a telegram sticker and you don’t even have to open it
a security researcher just showed that telegram’s animated stickers have a zero-click vulnerability rated 9.8 out of 10, that’s almost as critical as it gets
you receive the sticker, telegram automatically processes it to show you a preview, and that’s it.
code runs on your phone, no tap needed, no link clicked, nothing
the worst part? telegram is saying the bug doesn’t exist. they claim their servers validate every sticker so this is “technically impossible.”
meanwhile the researcher presented proof at a security conference in tokyo and the flawed code is still live in the app
there’s no patch. the vulnerability was reported months ago and telegram hasn’t fixed it
go to Settings → Privacy and Security → Messages and restrict who can message you. right now that’s the only thing between you and a sticker that owns your phone
the app 300 million crypto users trust with their group chats doesn’t even acknowledge the door is open
how X ranks your posts (breakdown of the new algo update)
the X algo predicts how each person will react to your post, and that then decides if and where it shows up in their feed
here's how much each reaction counts, compared with a like:
> someone copies the link: 30x
> someone you follow back replies: 30x
> a reply, a quote or a DM share: 7.6x
> a follow from the post: 6x
> a repost: 1.5x
> a like: 1x
> a bookmark: 0
the negative actions weigh far more, a report is -355x a like, a mute -89x, "not interested" -79x and a block -47x
if X predicts someone is likely to mute or report your post, it ranks lower in their feed
reports get a big weight because they are rare, a report is over 1,000x less likely than a like
these rules decide how far a post can reach:
> if you have 50,000 followers or fewer, X can boost a new original post up to about 16th place in someone's feed
> the boost only works in the post's first 2 hours, and stops once the post has 200 views in the Home feed
> X boosts one post each time a feed loads, and it prefers posts that got the most likes per view from their first viewers
> after 48 hours, X stops putting your post in people's feeds
> your replies and reposts only show up in the feeds of people who follow you
> original posts can also reach people who don't follow you, X scores them 25% lower for those people
> when several of your posts compete for one person's feed, the 2nd keeps 62.5% of its score and the 3rd keeps 43.75%
> replies, quotes, DM shares and copied links only count when people find your post in their feed, so engagement from a group chat link adds nothing
> if X labels your post low quality, it shows a notice on it and people can't like, reply, repost, bookmark or share it, misinformation labels can limit it too
what I'd do with it (my read of the weights):
> post when you can reply in the first 2 hours
> write posts people want to quote, reply to or send in a DM
> reply back to accounts that follow you
> post originals when you want to reach new people
Last night, three of my wallets were drained. I still don’t know exactly how this happened or what the attack vector was.
Over the past week, we’ve seen multiple security incidents and vulnerabilities being discussed across the industry, including PHP-related security concerns and other potential exploits. I don’t know whether any of these incidents are connected to what happened to me.
The amount involved is significant, and honestly, I’m struggling to process what has happened. I’ve spent years in this space, and experiencing something like this is absolutely heartbreaking.
Right now, I’m trying to trace the transactions, investigate the affected wallets, and understand how my security was compromised.
If anyone has experience with wallet drainers, compromised devices, malicious browser extensions, or on-chain investigations, please reach out to me via DM. Any genuine help in identifying the source of this attack would mean a lot.
🚨BREAKING NEWS : Your "deleted" photos aren't deleted.
Claude Code found years of them sitting in a hidden cache on my iPhone.
I plugged my iPhone into my MacBook to run a backup. I had Claude Code doing a security check at the same time. It flagged something I wasn't looking for. A directory called PhotoData/Thumbnails.
Thousands of files. Photos, videos, screenshots. A lot of them were things I had deleted.
Photos from a couple of years ago. Screenshots I took and deleted a few seconds later. Stuff I went into Recently Deleted and cleared. Some of it was still sitting there.
What I found in that cache:
- old screenshots of banking apps
- photos I deleted right after taking them
- random pictures I didn't want on my phone anymore
- a few things I specifically remember deleting more than once
When you delete a photo on iPhone, iOS removes it from your camera roll and Recently Deleted folder. But it keeps a compressed copy in a Spotlight search cache so your phone can still find things when you search. That cache doesn't get fully cleared.
I checked which apps had Files and Folders access. There were more than I expected, including apps I downloaded a long time ago and forgot about. Any of them could potentially read files from that cache.
I went through the list and removed access from most of them.
The prompt I used is below. It doesn't take long if you already have a backup.
How many apps on your phone have Files access right now?
Claude Code found 214,856 photos and videos I permanently deleted from my Android.
Three years of deleted photos and videos still sitting in a hidden cache. Any app with storage access can read them.
After the iPhone post I plugged my Pixel into the MacBook and asked Claude Code to check for leftover deleted files. It immediately pointed at a folder I had never opened.
DCIM/.thumbnails. Over 215,000 files. Photos, videos, screenshots. Every single one was something I deleted. Claude Code said most of them were not listed in the gallery trash or in MediaStore.
Photos from 2022, 2023, 2024 and 2025. The ones I deleted the second after taking them. The ones I cleared from Trash. The ones I deleted three separate times because I wanted to be sure they were gone. All still there.
Passport photo I took for a visa application in 2024. Screenshots of my bank app with full account numbers visible. Private photos I sent someone and immediately deleted after a breakup. Screenshot of my crypto seed phrase I took temporarily in 2023. Photo of my ID and credit card I took to remember the numbers and deleted 5 seconds later. Screenshots of my ex’s private stories I saved and permanently deleted in 2024.
Most were compressed previews. A few dozen were close to full size. All organized by date going back to 2021.
When you delete a photo on Android, the gallery removes it from your camera roll and Trash holds it for 30 days. It keeps a compressed copy in the thumbnail cache and MediaStore so your phone can show previews when you search or scroll. The system almost never cleans this folder. Files from 2022 were still sitting there.
They told you it was permanently deleted. It wasn’t.
I checked which apps on my phone had storage access. 27 apps. Weather apps. QR code scanners. PDF readers. A flashlight app I downloaded in 2021 that I forgot I even had. A calculator. Two of them still asked for full file access every time I opened them. Any one of them could have been reading every photo I ever deleted this entire time.
Went from 27 apps to 5 in about two minutes.
On iPhone the cache was harder to reach. On Android any app with storage permission can open this folder directly.
Full step by step below. Takes 2 minutes. Save it so you don’t lose it and send it to anyone with an Android phone.