#Cybersecurity Tip of the Day: Don’t let hackers sneak into your digital life! Enable two-factor authentication (2FA) on your accounts for an extra layer of protection, because a strong password alone isn’t enough.
#Cybersecurity Tip of the Day: Keep your software updated to stay one step ahead of cyber crooks! Set your apps and devices to auto-update, so you’re always protected with the latest security patches.
#CyberSecurity Tip of the day: Kick back, but don’t let hackers crash your vibe! Before you binge that new series, double-check your streaming accounts have strong, unique passwords. No one wants a cyber creep hijacking their watch party!
#Cybersecurity Tip of the Day: Regularly review your app permissions on your phone and computer. Revoke access for apps that don’t need your location, camera, or contacts to reduce the risk of data leaks!
#Cybersecurity Tip of the Day: Always verify the sender before clicking links or downloading attachments in emails. Phishing scams often mimic trusted sources to steal your data; hover over links to check their true destination and stay safe!
On public wi-fi, the admins can see what banking websites users visit, such as Chase or Bank of America, but won't be able to see anything else. All the traffic is TLS encrypted.
@unusual_whales Anyone replying that they work long hours as well should know that this should not be a standard. Life comes before work. If more work is required, hire some more people. Overworking is not going to give good results and will burn out employees.
@Aarowaim@geerlingguy@EpicGames It's the developers or application expert responsibility fill out a Security Assessment questionnaire. The info sec guy is the individual who hands the questionairre to that team, and based on their answers, verifies if its compliant with their company's security policy.
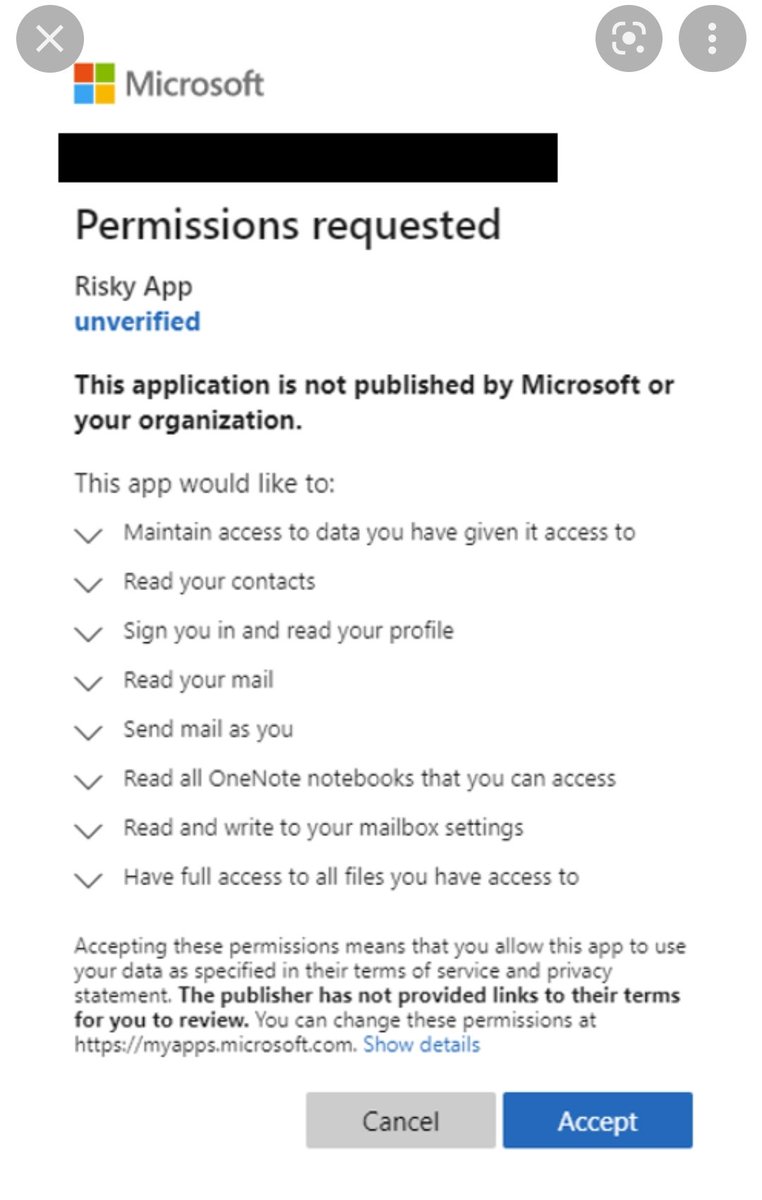
#Cybersecurity tip: Never grant permissions from apps you don't trust. You may get an email with a code asking you to insert it to the actual Microsoft website. If you insert it, this page will show up. And if you accept, your entire 0365 will be compromised.
@scrumdumpster69 I guess it really depends on where you get your masters. During my masters, we learned to use splunk, Metasploit, Wireshark, burpsuite... did plenty of projects on Linux terminal and other programming projects.
@NetworkChuck Let me add there is nothing wrong with a Helpdesk job. But if you have a CS or Engineering degree, you can apply directly to other positions. Unless you're trying to get into Google or something, maybe then it'd be smart to do Helpdesk and transition to another position.
@NetworkChuck Helpdesk is only for those individuals who didn't obtain a Bachelors or Masters in a Computer Science or Engineering degree, to get their foot in the door. My first job out of college was in Dev Ops.
#CyberSecurity tip: Learn to identify spam messages and never click on these types of links, without verifying from the sender. My little brother allowed an app access to his contacts, and they texted everyone this.